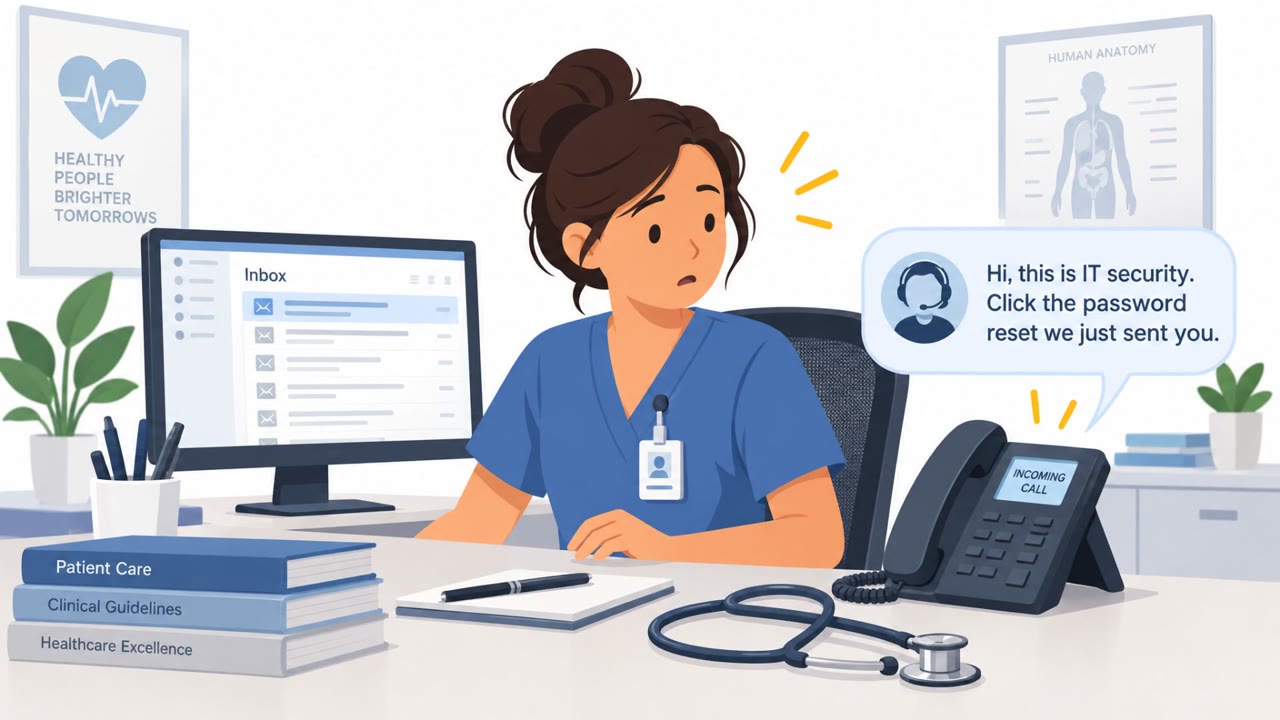
A hired security tester socially engineered a hospital nurse to unlock a restricted medical records room, despite having a non-working fake badge. He used a believable story, referenced a real doctor’s name, and built rapport by complaining about that doctor to convince the gatekeeper to let him in. The story highlights how friendly, “I belong here” behavior can bypass physical controls and lead to exposure of sensitive medical files.
How the attack worked
A hired security tester posed as a brand-new hospital employee. He wore scrubs and carried a fake security badge that could not possibly swipe in at the door. When the badge failed, he did not walk away. Instead, he leaned into a pretext: a named doctor on staff was allegedly failing to pull records needed for a trauma case, and he had been sent to retrieve them urgently.
The nurse gatekeeping the restricted records room responded to the story, and to the shared frustration about the doctor's behavior, by opening the door and letting him in. Once inside, he retrieved a targeted patient file. Rather than leaving immediately, he stayed and talked with the nurse for another ten minutes, complaining about security being incompetent, which further normalized his presence.
Why it succeeded
Several factors combined to make this pretext effective:
- The visual credibility of scrubs and a badge, even a non-functional one, created an initial impression of legitimacy.
- Referencing a real doctor's name gave the story specific, checkable-sounding detail.
- Framing the request around urgent patient care (a trauma case) applied pressure that discouraged the nurse from pausing to verify.
- Complaining about the doctor built rapport and shared grievance, which lowered the nurse's guard.
- Lingering afterward to chat reduced the chance the interaction would be remembered as suspicious.
What to watch for
Defenders in healthcare settings should treat these signals as warning signs:
- A badge that fails to work, followed by a request for manual override or door assistance.
- Urgency tied to patient care or safety used to discourage verification steps.
- Name-dropping specific staff members, especially paired with complaints or gossip about them.
- Visitors or new-seeming staff who linger and engage in extended small talk after gaining access.
Building resistance
Organizations can reduce the risk of this kind of physical social engineering by reinforcing that appearance and confidence are not proof of authorization. Staff should be trained to treat a non-working badge as a trigger for a documented verification process, such as contacting security or a supervisor, rather than manually opening restricted doors. Even in situations framed as urgent or life-or-death, access to sensitive areas like medical records rooms should require verified identity. Building this habit reduces the chance that a friendly, confident pretext alone can bypass physical access controls.
Key findings
- The tester wore scrubs and used a fake badge that “could not possibly swipe in,” then relied on conversation to get access.
- He exploited the nurse gatekeeper’s trust by name-dropping “an actual doctor on staff” and using a conflict-based pretext (“Dr Johnson's being an absolute asshole”).
- The nurse bypassed access controls and “opens the door, lets me in,” allowing retrieval of a targeted physical patient file.
- Extended small talk after entry helped normalize the access and reduce suspicion (“talked to the nurse for another 10 minutes”).
- Separately, the tester described a hospital where guest Wi‑Fi exposure enabled access to sensitive device traffic, with patient data “readily accessible and unencrypted.”
Who’s being targeted
- Commonly targeted roles: Nursing staff, Health Information Management / Medical Records, Reception / Front desk, Security / Facilities.
- Affected industries: Hospitals / Healthcare.
- Attack channels: physical.
- Impersonated: Hospital staff/security employee (new hire) with scrubs and badge.
Red flags to watch for
- Badge doesn’t work, but the person asks for access anyway (“non-working badge”).
- Emotional pressure and urgency tied to patient care (“trauma… We need these records”).
- Name-dropping a real doctor to sound legitimate (“picked out the name of an actual doctor on staff”).
Frequently asked questions
How did the tester get into the restricted records room?
He wore scrubs, carried a fake badge that could not actually swipe in, and used a story about an urgent trauma patient's records to convince a nurse to open the door for him.
Why did the nurse let him in despite the badge failing?
He built rapport by name-dropping a real doctor on staff and complaining about that doctor, which lowered the nurse's suspicion and made the request feel legitimate.
What should staff do if someone's badge doesn't work?
Treat a non-working badge as a red flag and follow a documented verification process, such as calling security or a manager, rather than manually opening a door.
What technique does this attack map to?
This case is associated with MITRE ATT&CK technique T1656, impersonation, used to gain physical access to a restricted area.
Read the video transcript
A guy in scrubs, fake badge that doesn’t even swipe… still walks into a restricted records room. He swipes, it fails, he sighs and says, “Look, I’m gonna save you the details. Dr Johnson’s being an absolute asshole, didn’t pull the trauma records. I’m brand new, they sent me to grab the file.” She says, “I got you,” badges the door for him, and he walks straight to a patient file. Then he hangs out, chatting another ten minutes so it feels normal. That’s social engineering, not teamwork. Here’s the move: if someone’s badge doesn’t work, you do not be the hero, call security or your manager and let them handle the door.