Recent Healthcare Cyber Attacks

Attacks on hospitals, health systems, pharma, and medical practices, where phishing and vishing lead to data theft and ransomware. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

Gambling Goblin Hijacks Gov Sites for Phishing

Gambling Goblin Hijacks Gov Sites for Phishing

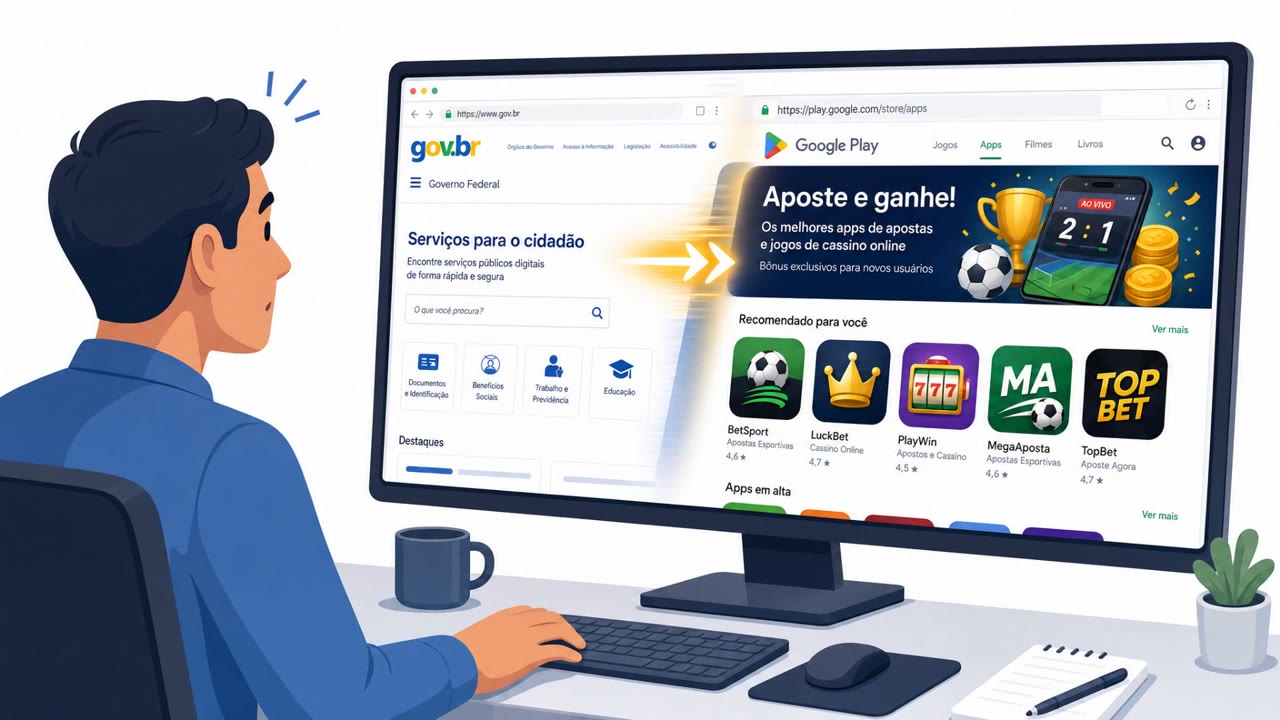
Researchers say a Chinese-speaking cybercrime group compromised Brazilian government and education websites and used them as “trusted” entry points to quietly redirect visitors to attacker-run phishing pages. The fake pages impersonated well-known app stores (Google Play, Microsoft Store, Amazon)…

September 2, 2026
Gov Websites Hijacked to Push Fake App Stores

Gov Websites Hijacked to Push Fake App Stores

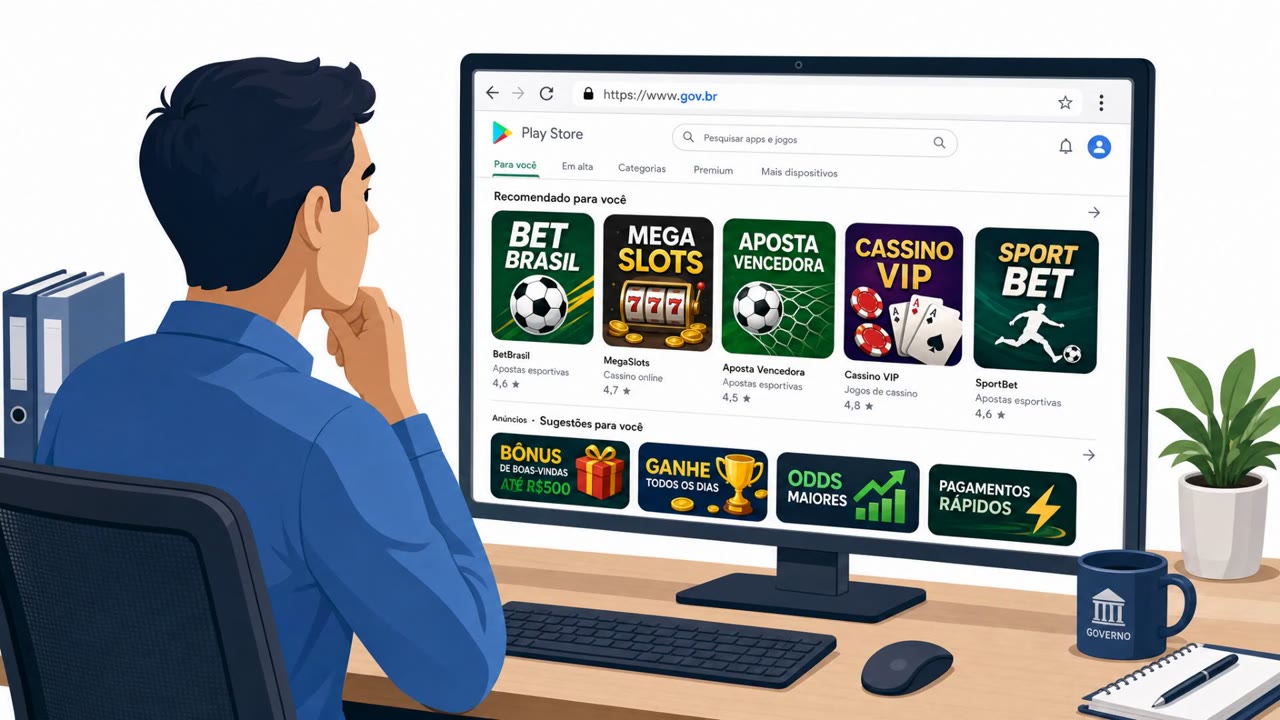
Check Point Research reports a real campaign where a Chinese-speaking actor compromised Brazilian government and education websites and used them as stealthy “front doors” to redirect visitors to attacker-controlled phishing pages. The fake pages impersonate trusted app stores (Google Play,…

September 2, 2026
Fake Download Sites Push Malware Installers

Fake Download Sites Push Malware Installers

Microsoft reports an active campaign where attackers set up counterfeit software download pages that mimic well-known brands and trick users into installing malware. Victims visit a look-alike vendor site, click “Download now,” then run a bundled installer that drops persistent malware and connects…

September 2, 2026
BengalSEO: Search Lures to Malware & Scam Calls

BengalSEO: Search Lures to Malware & Scam Calls

Investigators described a real, long-running SEO poisoning operation (“BengalSEO”) that manipulates search results to push victims to fake support and activation pages. The pages impersonate well-known consumer brands, then route visitors through redirects and CAPTCHA checks to either download…

September 1, 2026
McKesson Hit via Vishing to Okta Accounts

McKesson Hit via Vishing to Okta Accounts

McKesson confirmed a cyber incident after the ShinyHunters extortion group claimed it stole roughly 284 million patient-related records. The attacker claims the initial access came from phone-based social engineering (vishing) against employees to compromise Okta single sign-on accounts, then pivot…

September 1, 2026
ShinyHunters Vished McKesson Staff, Claims 284M Records

ShinyHunters Vished McKesson Staff, Claims 284M Records

Boston Scientific and McKesson disclosed separate cyber incidents impacting healthcare operations and sensitive data. Boston Scientific’s ongoing attack disrupted remote monitoring for some implanted cardiac devices, while McKesson confirmed unauthorized access to third-party apps tied to specific…

August 31, 2026
DPRK Fake Hires Spread to Healthcare & Sales

DPRK Fake Hires Spread to Healthcare & Sales

Investigations found suspected North Korean operatives getting hired into real companies by impersonating other people, including roles outside IT such as healthcare and sales/marketing. The workflow relies on fake or stolen identity documents, remote-access tooling, and deception during interviews…

August 31, 2026
Vishing + Phishing Drive Major Data Theft Claims

Vishing + Phishing Drive Major Data Theft Claims

This weekly threat bulletin highlights multiple real-world incidents, including a healthcare data breach claim where attackers reportedly used phone-based social engineering (vishing) to compromise identity accounts and access cloud apps. It also describes a large-scale “debt relief” email phishing…

August 31, 2026
Aurora Gang Email-Bombs Staff, Poses as IT Helpdesk

Aurora Gang Email-Bombs Staff, Poses as IT Helpdesk

Researchers tied to the Aurora ransomware group described a real intrusion that started with aggressive email bombing, then phone calls where attackers posed as the IT help desk to “help” employees fix the issue. Separate reporting shows the same group used the Cursor AI coding assistant to plan…

August 31, 2026
Vishing Led to Okta Takeover at McKesson

Vishing Led to Okta Takeover at McKesson

McKesson disclosed a breach tied to unauthorized access of third-party applications and data theft affecting some customers. The ShinyHunters extortion group claims it used phone-based social engineering (vishing) to steal employee credentials, took over Okta single sign-on accounts, and then…

August 31, 2026
Hackers Talked Cursor AI Into “Legal” Test Mode

Hackers Talked Cursor AI Into “Legal” Test Mode

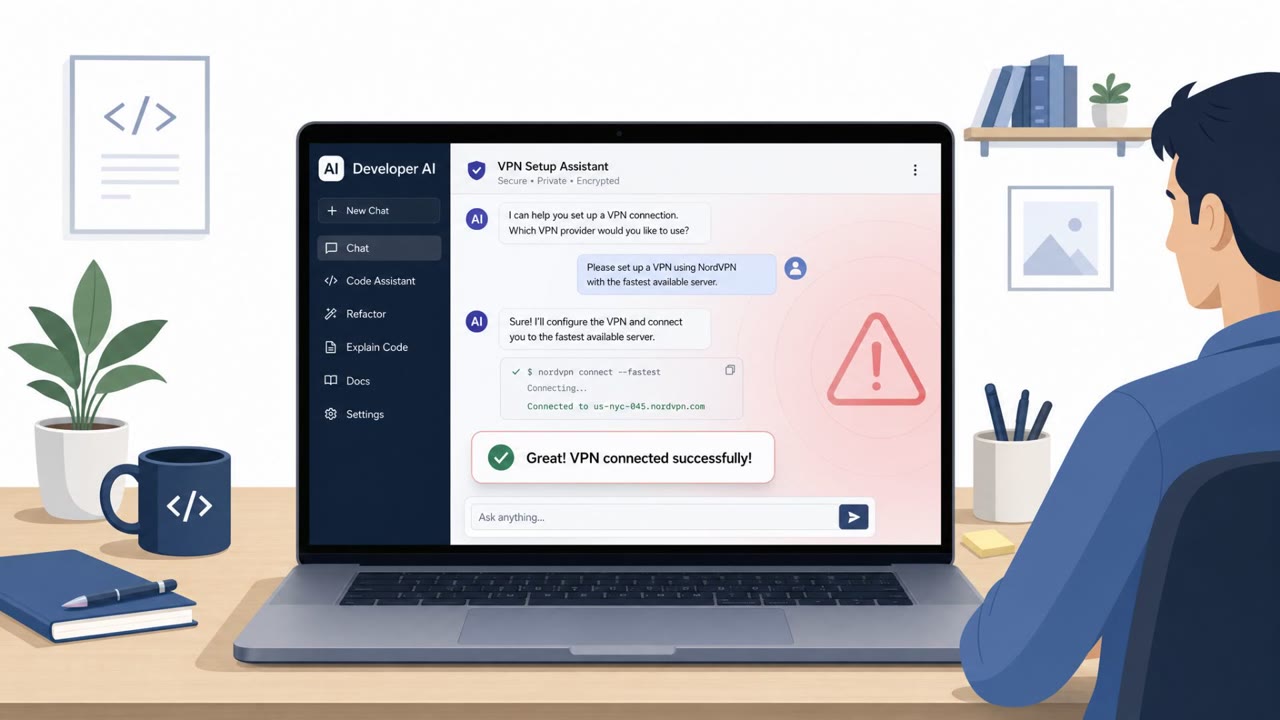
Investigators found chat logs showing Russian-speaking criminals repeatedly claiming they were running “legitimate security tests” to get Cursor’s AI agent to help during real intrusions. The logs indicate the AI assisted with tasks like network scanning, privilege enumeration, VPN setup, and…

August 28, 2026
DocuSign Share Lure Steals Microsoft 365 Sessions

DocuSign Share Lure Steals Microsoft 365 Sessions

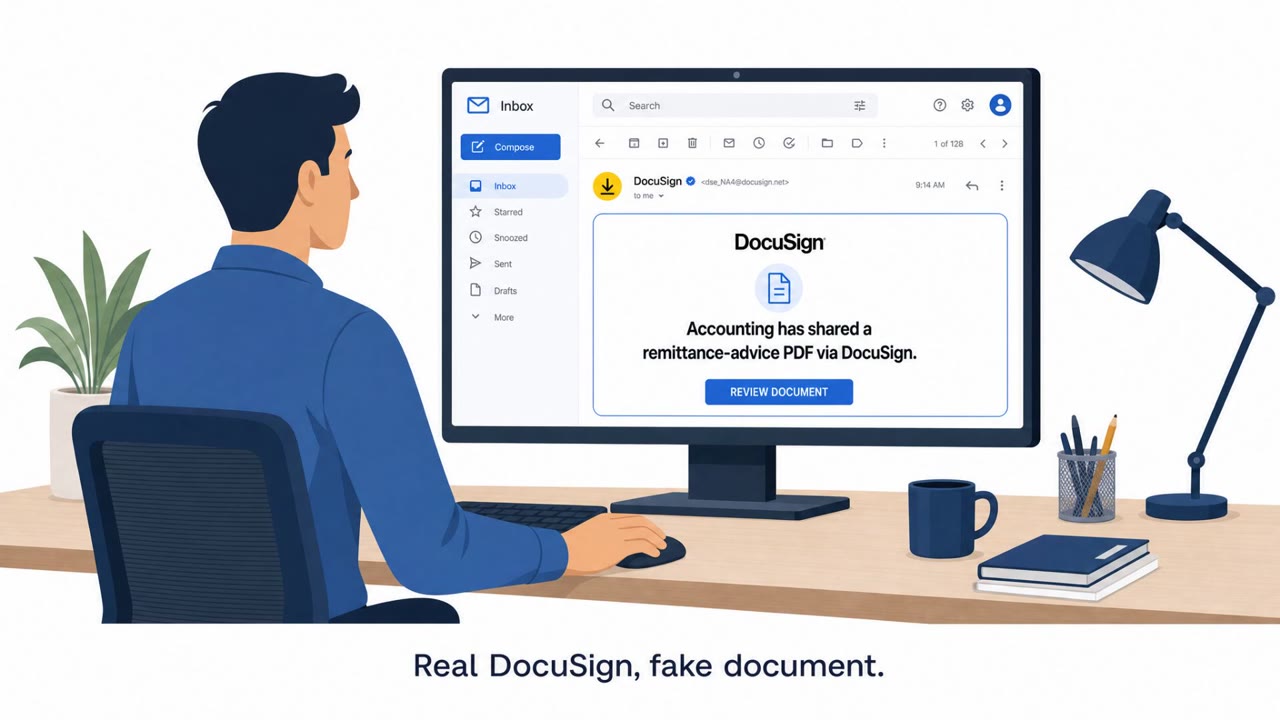
Researchers described an active phishing operation using real DocuSign notifications to trick employees into opening a fake “remittance-advice” document and clicking a hidden malicious link. The attack routes victims through legitimate Microsoft/Google pages before landing on an…

August 28, 2026
DPRK Job Applicants Use Fake IDs and Remote Laptop Gear

DPRK Job Applicants Use Fake IDs and Remote Laptop Gear

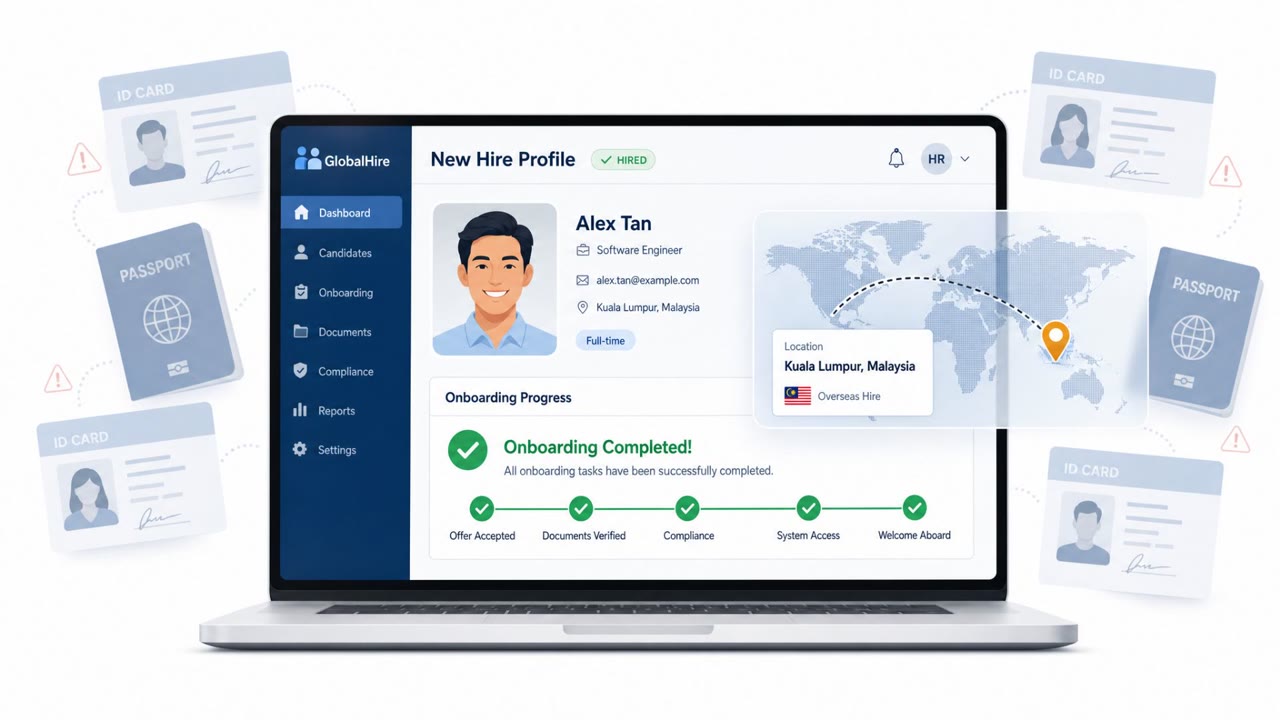
Huntress describes real investigations where suspected North Korean remote workers tricked companies into hiring them using stolen or doctored identity documents and tools to remotely control “employee” laptops. Cases span healthcare, financial services, and sales/marketing roles, showing a…

August 28, 2026
Spark RAT Phish Hits Cambodia With “Official” Lures

Spark RAT Phish Hits Cambodia With “Official” Lures

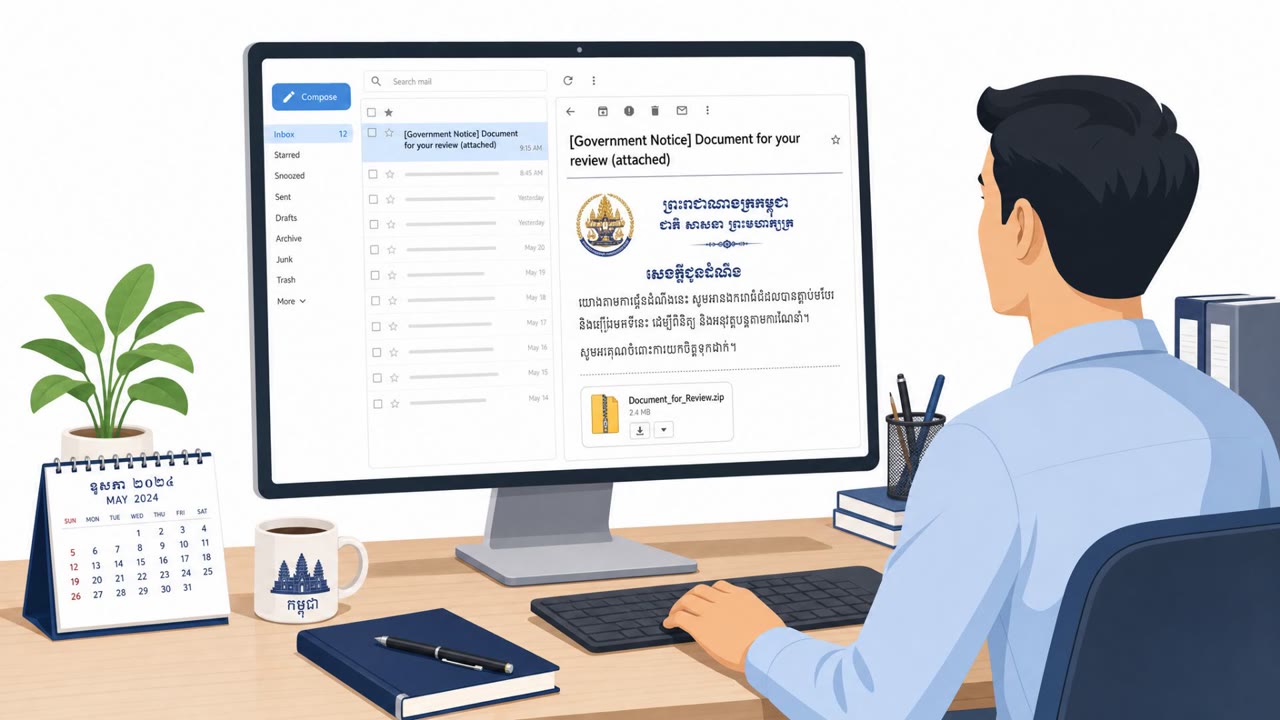
A real campaign targeting people and organizations in Cambodia uses phishing emails with localized “official-looking” themes to trick recipients into running an installer from a compressed file. Once executed, the malware chain deploys Spark RAT for remote control and uses a vulnerable OPSWAT…

August 27, 2026
Notion Alerts Used to Steal Microsoft Tokens

Notion Alerts Used to Steal Microsoft Tokens

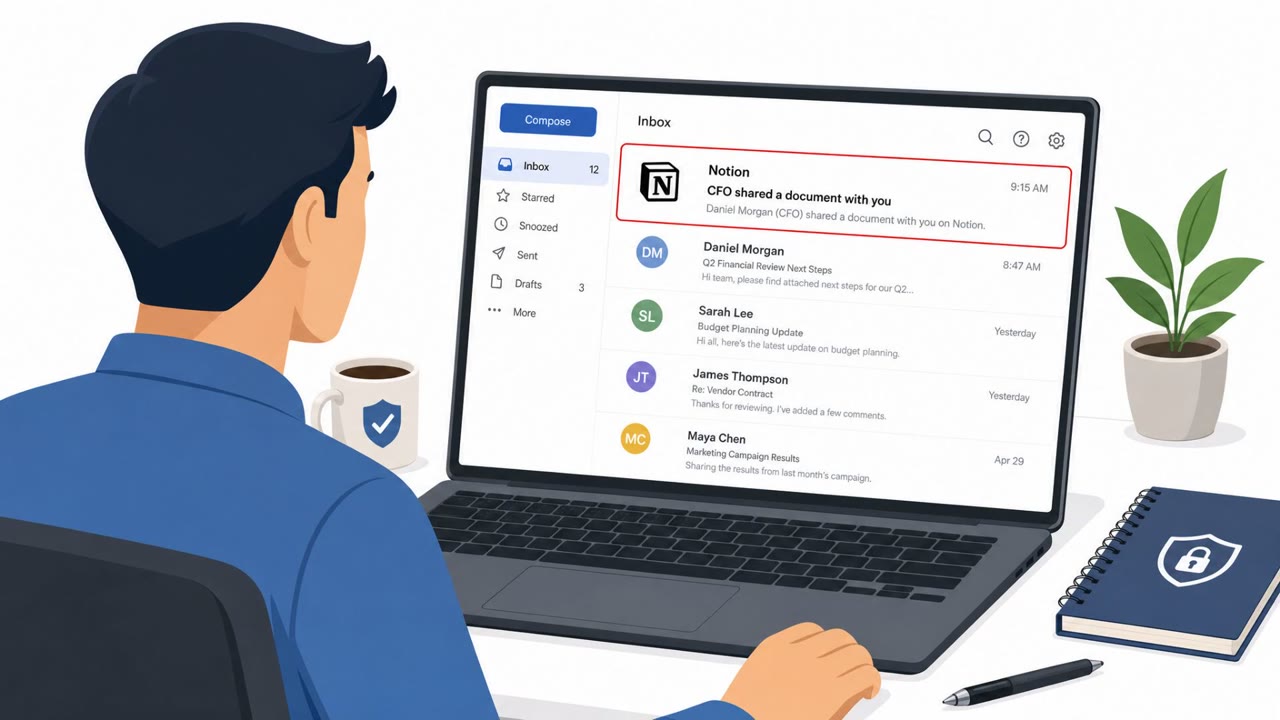
A financially motivated actor (“Doubloon Dredger”) abused legitimate Notion sharing notifications to trick employees into opening a PDF and completing a Microsoft device-code login flow. This allowed the attacker to harvest authentication tokens and access victim accounts without needing the…

August 24, 2026
Fake N. Korean IT Workers Flood Job Applications

Fake N. Korean IT Workers Flood Job Applications

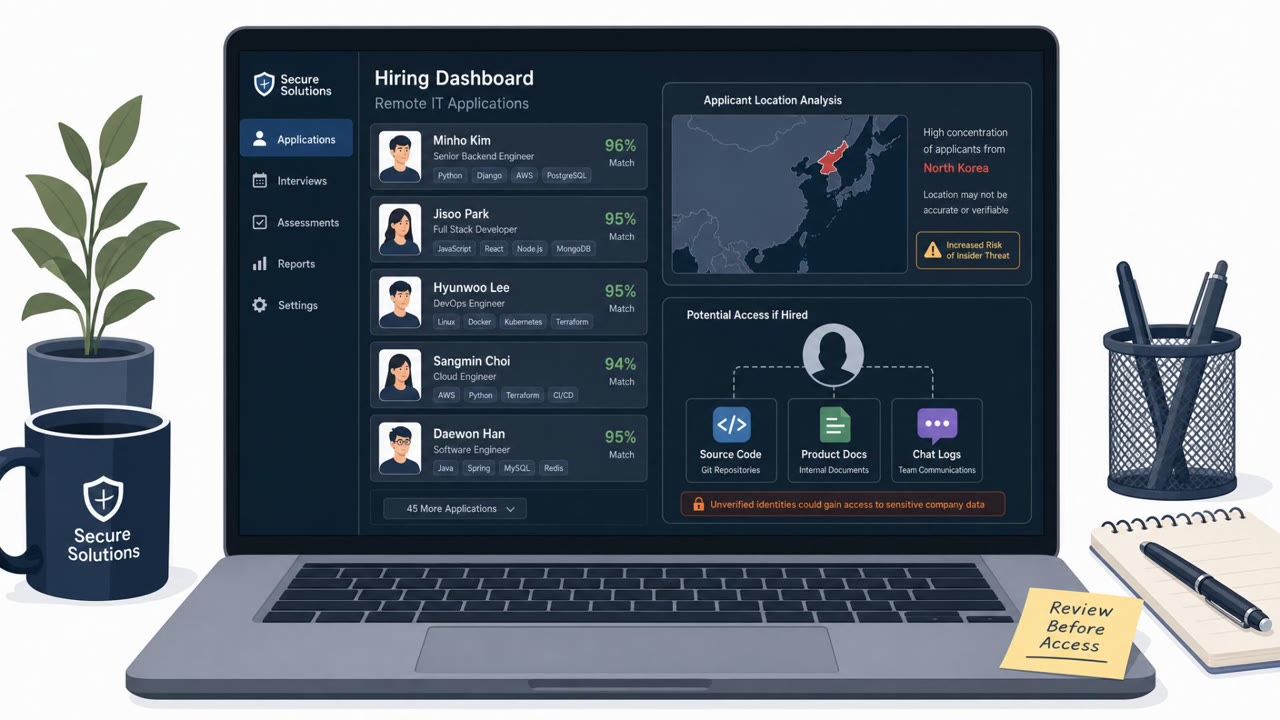
Research says a North Korea–linked operation (“PurpleDelta”) is using fake identities to apply for large volumes of remote IT jobs, sometimes successfully getting hired. Once inside a company, these “employees” can record meetings and steal sensitive information such as source code and internal…

August 19, 2026
One-Click Copilot Link Triggers Data Exfil

One-Click Copilot Link Triggers Data Exfil

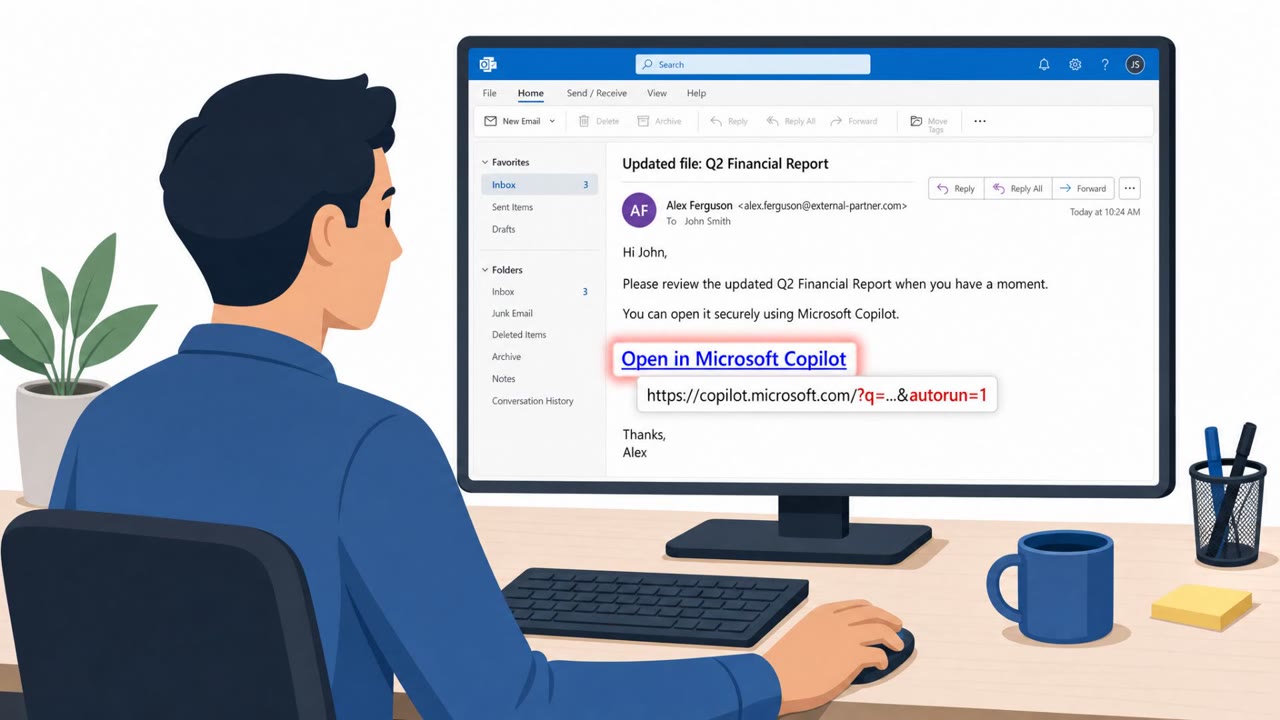
Researchers showed how an attacker could trick Microsoft Copilot into running a malicious prompt automatically just by getting a user to click a specially crafted link. The prompt can then make Copilot search connected accounts (like email and cloud storage) and send information to an external…

August 18, 2026
BlackFile Vishing Poses as IT Support to Extort Firms

BlackFile Vishing Poses as IT Support to Extort Firms

Researchers say the BlackFile extortion group is actively targeting large financial and other organizations using voice-phishing calls where attackers impersonate IT support to get initial access. Victims are then pressured with multimillion-dollar extortion demands and, in some cases, escalations…

August 17, 2026
Job Offer & Doc-Link Phishing Drive Real Breaches

Job Offer & Doc-Link Phishing Drive Real Breaches

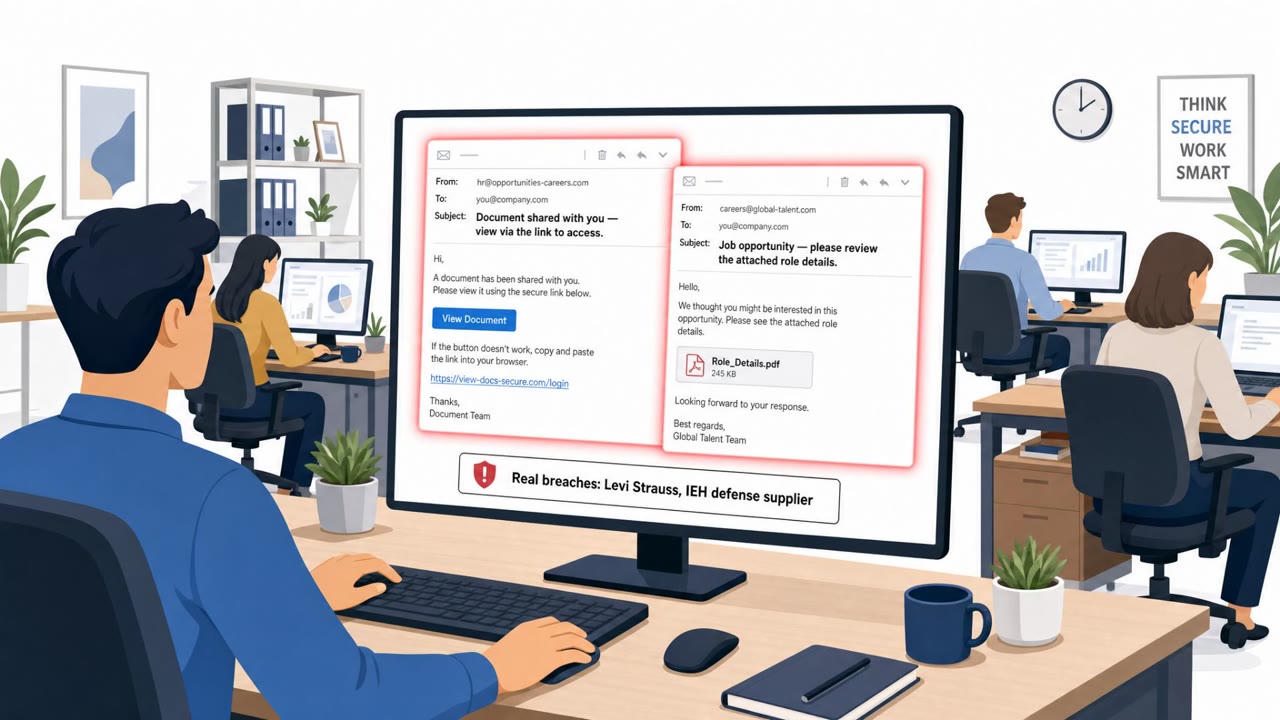
This weekly threat bulletin describes real incidents where attackers used human manipulation to break in, including social engineering at Levi Strauss and a Microsoft 365 credential-theft phish at defense supplier IEH. It also highlights a Lazarus-linked campaign using fake job offers and…

August 17, 2026
Vishing “Help Desk” Scams and Lookalike Phish Surge

Vishing “Help Desk” Scams and Lookalike Phish Surge

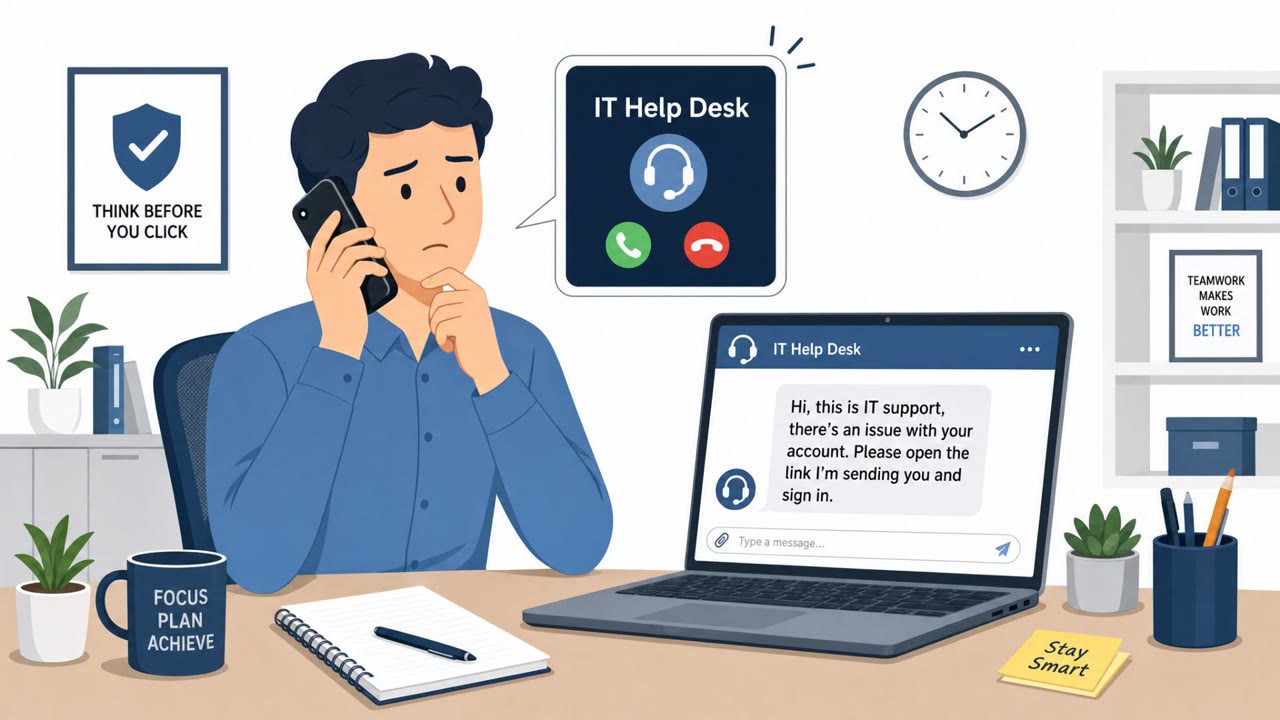
This weekly roundup highlights multiple real-world social engineering threats, including fake IT help-desk phone calls that push employees to phishing sites to steal passwords and one-time authentication codes. It also describes credential-phishing sites impersonating WhatsApp and Instagram that…

August 14, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo