Researchers reported a real phishing campaign targeting Call of Duty Mobile players with a fake “free Call of Duty Points” giveaway site. Victims are tricked into entering their email/password and then a one-time 2FA code, allowing attackers to take over accounts and potentially access linked gaming profiles and stored payment methods.
How the attack worked
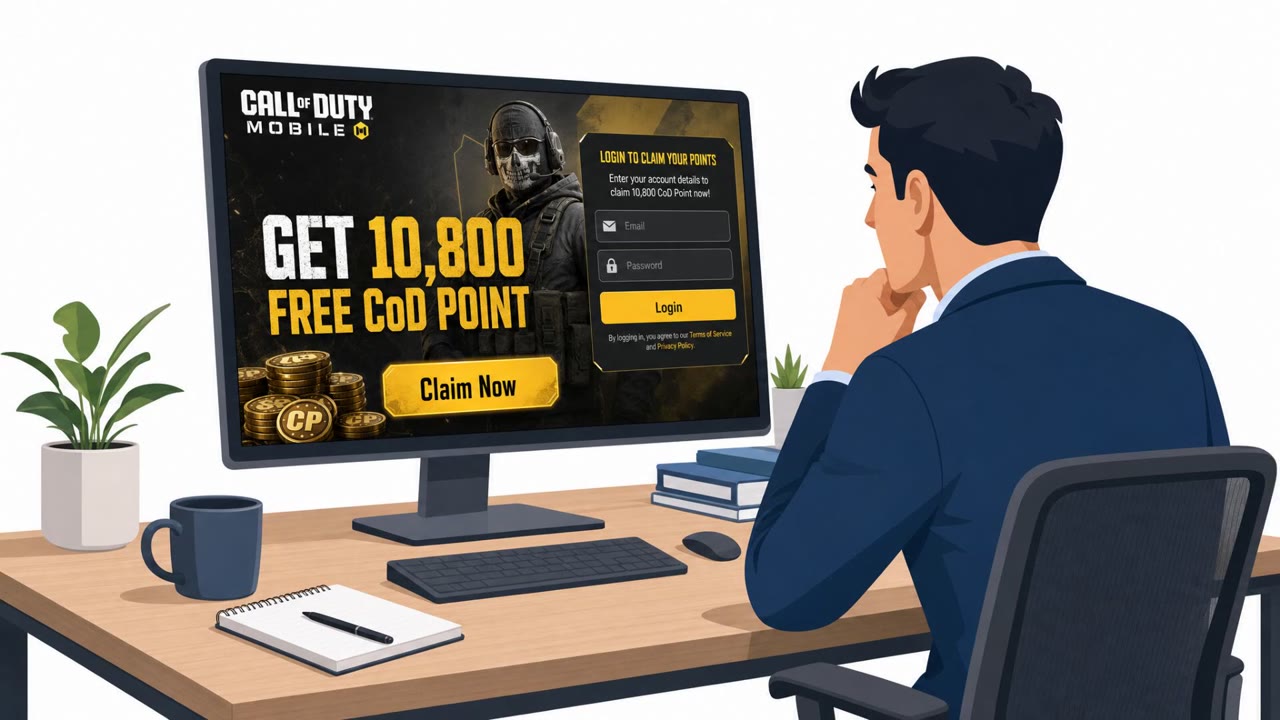
This campaign impersonates the official Call of Duty Mobile site with a promise of 10,800 free Call of Duty Points, the game's premium currency. Instead of a legitimate redemption code, the page asks victims to log in with their email address and password. After submitting those credentials, victims are redirected to a second page that requests their one-time 2FA code. Behind the scenes, the attack uses a real-time credential relay that forwards the stolen credentials to the real Activision login, which triggers a genuine 2FA challenge. When the victim enters that code on the fake page, it is relayed too, giving attackers everything needed to take over the real account.
Why it succeeded
The lure works because it plays on a common desire among mobile gamers, free in-game currency, and mimics the structure of a legitimate login flow closely enough to feel routine. Asking for a 2FA code immediately after login can feel normal to users who are used to two-step verification prompts on many sites, especially when the credential relay produces a real, valid 2FA request from the actual game publisher. This blurs the line between a fake prompt and a real one, making the scam harder to spot in the moment.
What to watch for
- Wording errors and awkward phrasing, such as "GET FREE POINT" instead of "GET FREE POINTS"
- A request to enter your password to claim a promotion, rather than a redemption code
- A second page asking for a one-time 2FA code right after login
- Extra elements like a live chat widget that seem present mainly to make the site look more legitimate
Impact of account takeover
Because many gaming accounts are linked to other services, a successful takeover can expose connected Xbox, PlayStation, or Battle.net profiles, along with stored payment methods and purchase history. This makes the scam relevant not just to individual gamers but also to teams supporting customer or community accounts, and to anyone whose gaming account may share credentials with other services.
How to build resistance
- Treat any "free points" or "free rewards" login page as suspicious; legitimate promotions should not require entering a password on an unfamiliar site
- Never share a one-time 2FA code with a website or person; codes exist specifically to stop this kind of takeover
- Go directly to the official app or type the publisher's website address into a browser rather than following links in messages, social posts, or ads
- If credentials were entered on a suspicious page, change the password immediately, treat the account as compromised if a 2FA code was also entered, review recent activity, sign out all sessions, and check linked payment methods for unauthorized charges
Key findings
- A phishing campaign impersonates the official Call of Duty Mobile site with a “free Call of Duty Points (CP)” offer.
- Victims are prompted to enter email and password, then redirected to a second page that asks for the 2FA code.
- The attack uses a “real-time credential relay” to forward credentials to the real Activision login immediately, triggering a real 2FA challenge.
- Account takeover can expose linked Xbox/PlayStation/Battle.net profiles and potentially stored payment methods and purchase history.
- The fake site contains noticeable quality issues (e.g., “GET FREE POINT” wording) and legitimacy cues like a chat widget.
Who’s being targeted
- Commonly targeted roles: All employees, Helpdesk/IT support, Finance (payment-method fraud awareness), Customer/community support teams.
- Affected industries: Gaming, Consumer online services, Digital entertainment.
- Attack channels: website.
- Impersonated: Call of Duty Mobile / Activision (impersonated official site).
Red flags to watch for
- Unprofessional/incorrect wording such as “GET FREE POINT” and awkward instructions
- Asks for email/password instead of a legitimate redemption code
- Requests a one-time 2FA code immediately after login on a separate page
Frequently asked questions
How does the fake Call of Duty Points giveaway scam work?
A fake site impersonating the official Call of Duty Mobile page offers 10,800 free Call of Duty Points and asks victims to log in with their email and password, then requests the one-time 2FA code on a second page.
What happens if I enter my 2FA code on this fake site?
The credentials and code are relayed in real time to the real Activision login, letting attackers complete account takeover and potentially access linked Xbox, PlayStation, or Battle.net profiles and payment information.
What are the warning signs of this phishing page?
Look for awkward wording like GET FREE POINT, a request for password instead of a redemption code, and a chat widget that seems included only to appear more legitimate.
What should I do if I already entered my credentials?
Change the Activision password immediately, treat the account as compromised if a 2FA code was entered, review recent account activity, sign out of all sessions, and check linked payment methods for unauthorized charges.
Read the video transcript
See a website yelling “GET FREE POINT” and promising 10,800 free Call of Duty Points? That’s the trap. The fake site looks like Call of Duty Mobile, even has a chat widget, but it asks for your email and password, then a second page demands your 2FA code. The moment you type that code, they can log in to your real Activision account, plus linked Xbox, PlayStation, or Battle.net profiles and stored payment methods. If a promo wants your password or 2FA code, back out and only claim rewards by opening the official app or typing the publisher’s site in yourself.