Recent Media and Entertainment Cyber Attacks

Attacks on media, entertainment, and gaming companies, from newsroom impersonation to takeovers of high-profile accounts. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

ClickFix Lures Spread ChainScript RAT

ClickFix Lures Spread ChainScript RAT

Researchers describe real-world “ClickFix” social-engineering lures that trick people into installing malware by downloading fake apps (like Spotify/Zoom/Teams) or copying commands into Terminal. One campaign abused a compromised, verified HBO Max Reddit account to run malicious ads, while another…

September 21, 2026
Revolut Fooled by Govt Impersonation Email

Revolut Fooled by Govt Impersonation Email

A person posing as a government agency used an email address on that agency’s real domain to obtain sensitive customer records from Revolut. The same weekly roundup also describes a fake antivirus renewal web page impersonating Avast, telling victims their subscription renewed for €129.99 and…

September 20, 2026
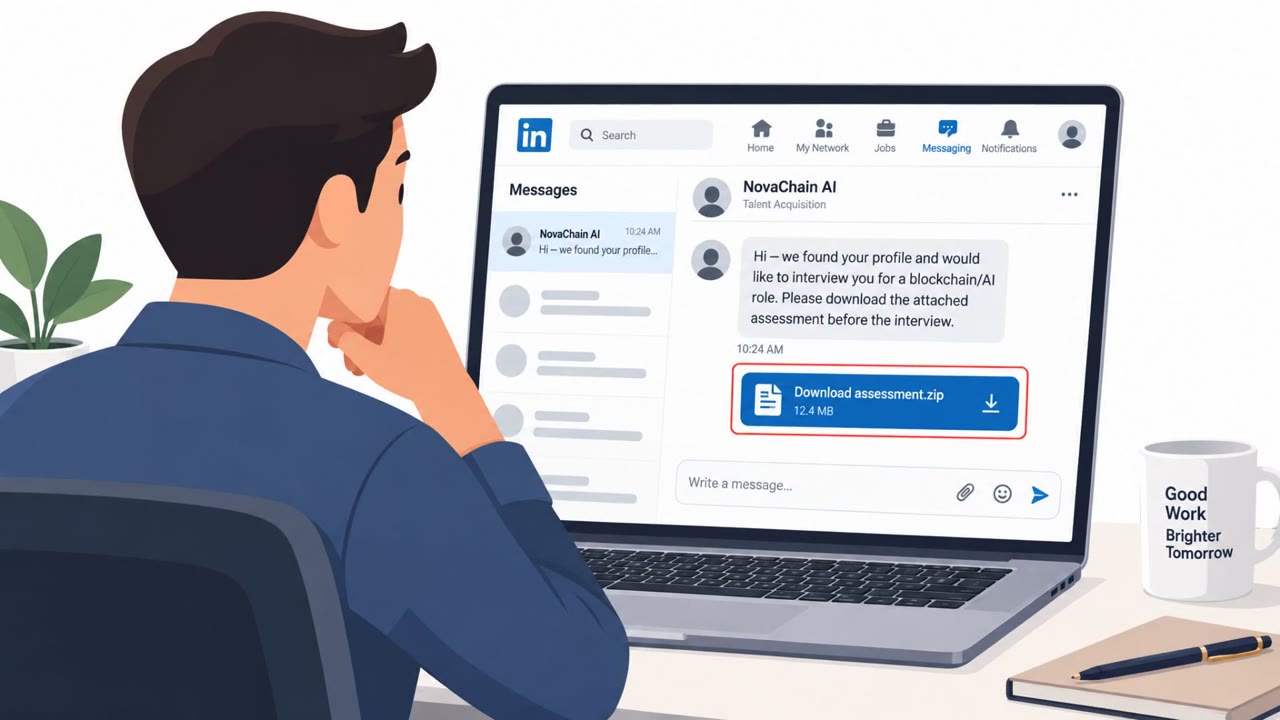
Fake Recruiters Hit Job Seekers With Malware Files

Fake Recruiters Hit Job Seekers With Malware Files

An alleged North Korean operation called “WaterPlum” targeted job seekers by posing as AI and blockchain companies and using the interview process to trick applicants into downloading malicious files. Authorities say the campaign infected tens of thousands of devices worldwide and led to theft from…

September 18, 2026
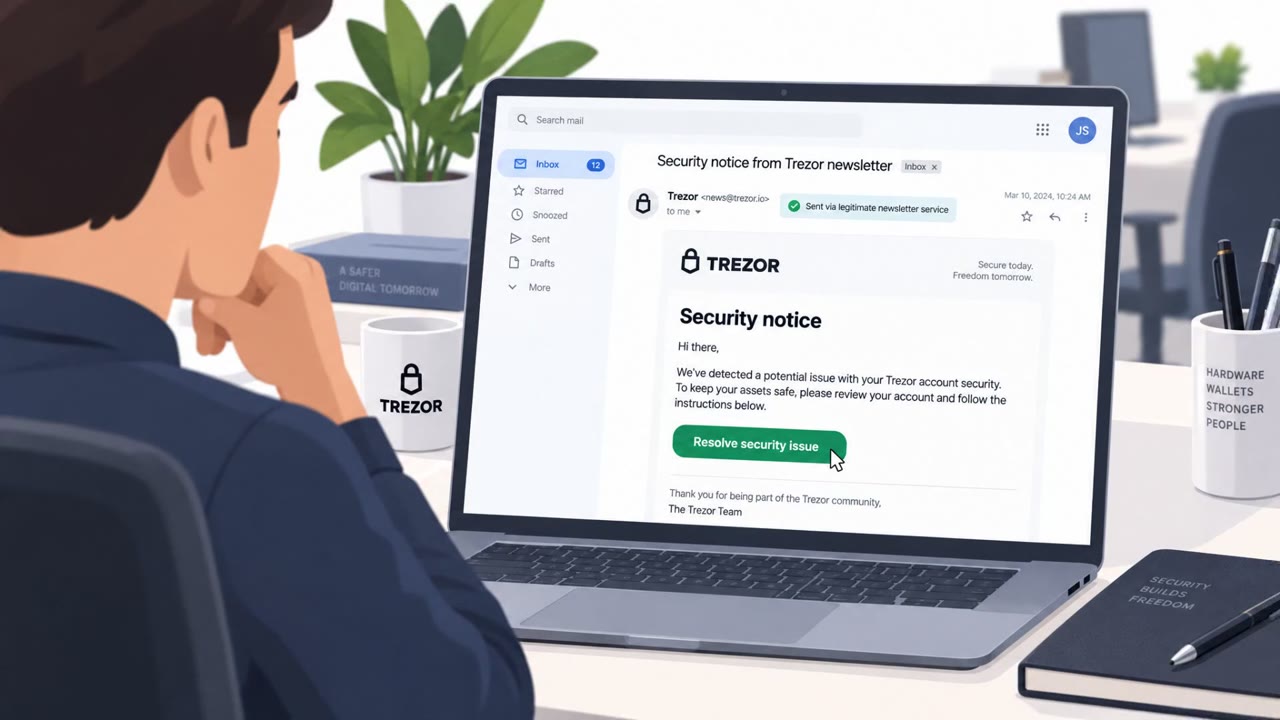
Trusted Channels Hijacked for Phishing and Malware

Trusted Channels Hijacked for Phishing and Malware

The article describes multiple real-world social engineering operations this week, including phishing sent from a legitimate Trezor newsletter channel and malware pushed through a verified HBO Max Reddit ad account. It also highlights a large-scale network of fake online stores impersonating real…

September 18, 2026
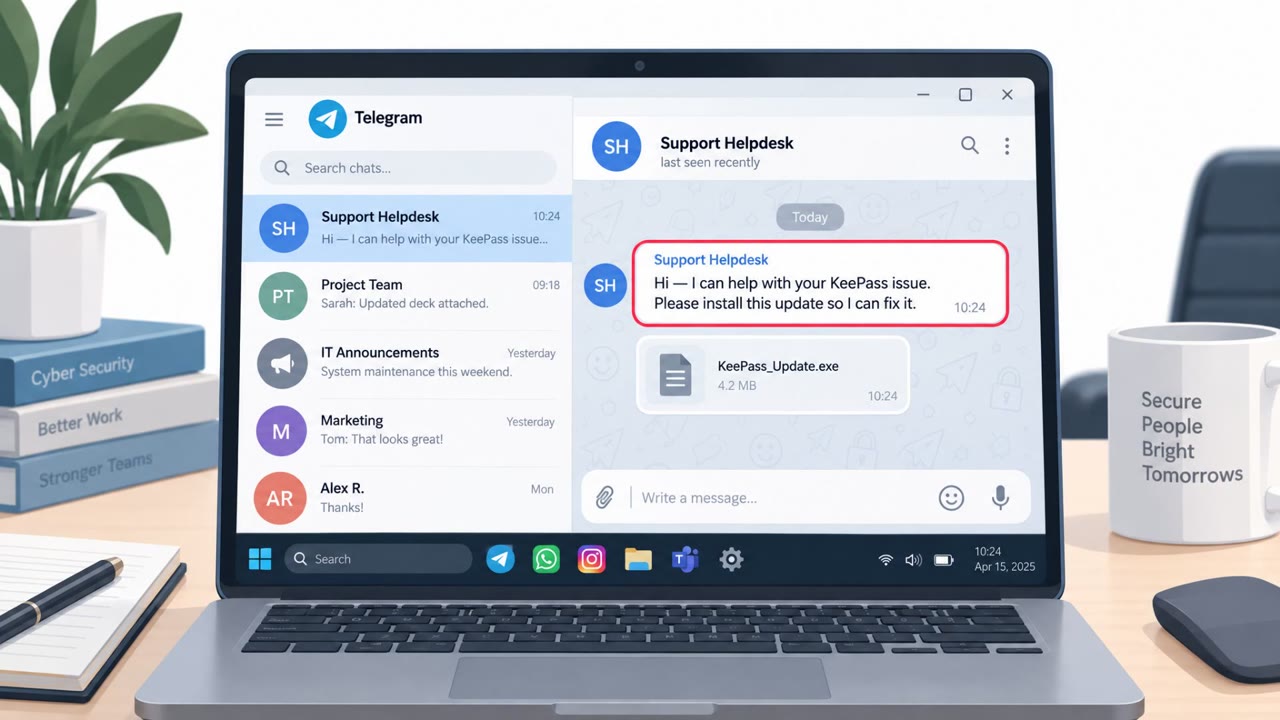
Handala Uses Fake “Support” Chats to Drop Malware

Handala Uses Fake “Support” Chats to Drop Malware

Researchers linked the Iran-aligned Handala Hack persona to a Telegram-controlled backdoor (HEAVYGRAM) that can steal passwords and exfiltrate chat data. The campaign reportedly starts with social engineering on messaging apps (Telegram, WhatsApp, Instagram), where the attacker pretends to offer…

September 18, 2026
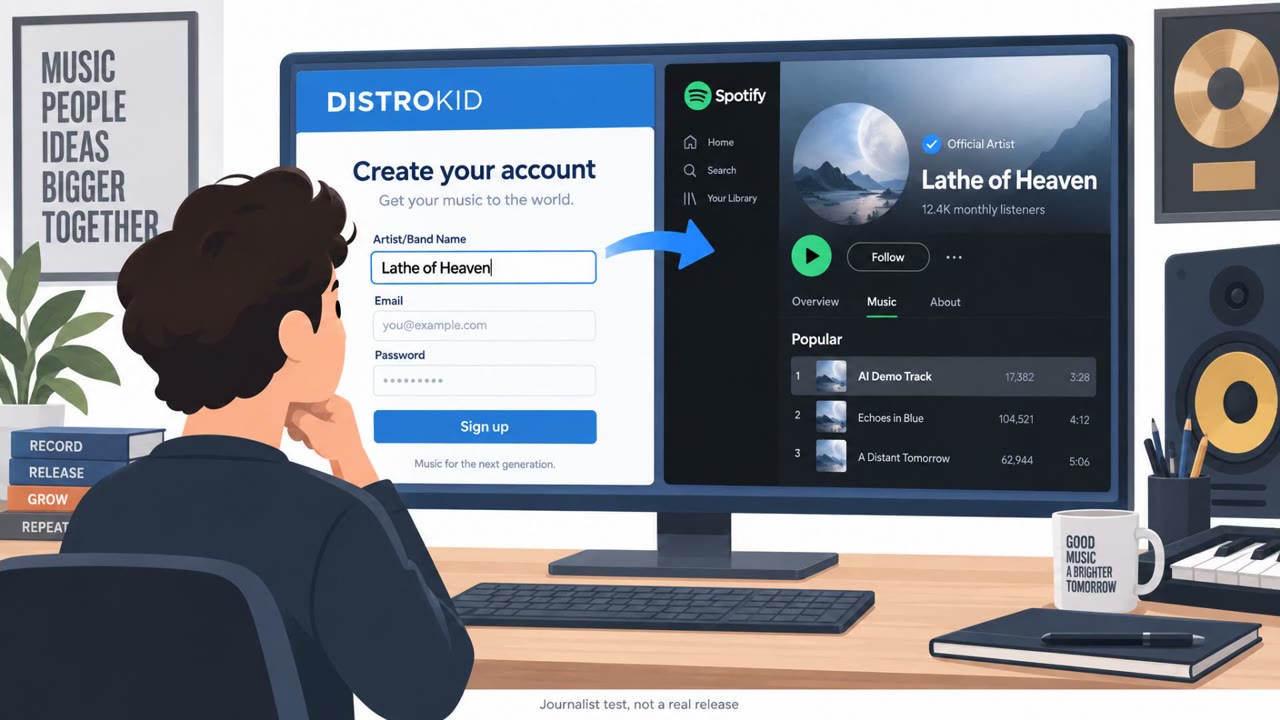
AI Scammer Hijacks Band’s Spotify via Distributor

AI Scammer Hijacks Band’s Spotify via Distributor

A journalist showed how easy it is to upload AI-generated songs onto a real artist’s official Spotify page by abusing weak identity checks in digital music distribution. By claiming to be the band during a distributor signup/upload process, the uploader can publish fake tracks to major streaming…

September 17, 2026
Iranian “Chosen Brick” Lures Sent via Telegram

Iranian “Chosen Brick” Lures Sent via Telegram

UK, US, and Dutch agencies warned that Iranian state-linked actors used social messaging apps to build trust with dissidents, journalists, and activists before sending disguised files that install Windows malware. The attackers often impersonated someone the target already knows or “technical…

September 17, 2026
HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

Attackers compromised HBO Max’s verified Reddit advertising account and used it to run 108 malicious ads in about 48 hours. The ads sent people to attacker-controlled websites that used “ClickFix” instructions to trick users into running commands that installed malware on Windows and macOS.

September 16, 2026
Iranian Spies Lure Targets via WhatsApp to Drop Malware

Iranian Spies Lure Targets via WhatsApp to Drop Malware

A joint UK-US-Dutch advisory warns Iranian state-backed cyber actors are targeting dissidents, activists, and journalists by first contacting them on WhatsApp or Telegram and building trust. The attackers then persuade victims to open a malicious file disguised as legitimate software (or even MRI…

September 16, 2026
Iran-Backed Spyware Uses Fake Support Chats

Iran-Backed Spyware Uses Fake Support Chats

UK and allied agencies warn that a Tehran-backed operation is targeting dissidents, activists, and journalists using social engineering to trick them into installing spyware called “Chosen Brick.” Attackers build trust on social media by impersonating known contacts or “technical support,” then…

September 16, 2026
Iran Uses WhatsApp Lures to Drop Chosen Brick Malware

Iran Uses WhatsApp Lures to Drop Chosen Brick Malware

Western government agencies warn that Iranian state-backed actors are using WhatsApp and Telegram messages to trick targeted individuals into installing a Windows surveillance and data-stealing tool called “Chosen Brick.” The attackers build trust by impersonating known people or organizations,…

September 15, 2026
Iran Spyware Poses as Apps, Delivered by Message

Iran Spyware Poses as Apps, Delivered by Message

Government agencies say Iranian intelligence-linked attackers are targeting dissidents, journalists, and activists with Windows malware controlled through Telegram. The attack starts with a trust-building message impersonating someone the victim knows or app support, then delivers a file disguised…

September 15, 2026
Iran-Linked Spyware Posed as Apps on WhatsApp

Iran-Linked Spyware Posed as Apps on WhatsApp

UK, US and Dutch authorities warned that Iran-linked attackers are targeting dissidents, activists, and journalists with Windows spyware. The group builds trust over messaging apps, then tricks victims into downloading malware disguised as legitimate software (or even medical files). The spyware…

September 15, 2026
Fake MRI File Used to Deliver Iran Spyware

Fake MRI File Used to Deliver Iran Spyware

UK, US, and Dutch agencies warned that Iran-linked operators used long-running social engineering to build trust with targets (including dissidents, activists, and journalists), then sent malicious files disguised as legitimate documents or software installers. One lure included a fake MRI scan…

September 15, 2026
Iranian Actors Lure Targets via Telegram/WhatsApp

Iranian Actors Lure Targets via Telegram/WhatsApp

UK, US, and Dutch authorities reported Iranian state-linked cyber actors using social messaging apps like Telegram and WhatsApp to build trust with dissidents, activists, and journalists. The actors then convince targets to open “legitimate-looking” files (fake apps or documents like MRI results)…

September 15, 2026
Iran-Linked Spyware Lures Targets via WhatsApp

Iran-Linked Spyware Lures Targets via WhatsApp

UK cyber authorities and international partners warned that Iranian state cyber actors have been tricking dissidents, activists, and journalists into installing spyware called CHOSEN BRICK. The campaign uses impersonation over messaging apps (such as WhatsApp and Telegram), rapport-building, and…

September 15, 2026
AI “Agents” Flood Inboxes With Spam Pitches

AI “Agents” Flood Inboxes With Spam Pitches

The article describes real-world examples of unsolicited emails that claim to be sent by “AI agents,” pitching services, interviews, coverage, and paid work. It includes specific subject lines and message excerpts that show a repeatable workflow: automated outreach that tries to prompt recipients…

September 15, 2026
Twitch Extension Exposed OAuth Tokens to Developer

Twitch Extension Exposed OAuth Tokens to Developer

Researchers reported that a popular Twitch browser extension sent users’ Twitch OAuth login tokens to proxy servers controlled by the extension’s developer. If a token was exposed, someone receiving it could potentially act as the account holder without needing the user’s password. The key user…

September 15, 2026
HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
Hijacked HBO Max Reddit Ads Push ClickFix Malware

Hijacked HBO Max Reddit Ads Push ClickFix Malware

Researchers reported that criminals hijacked HBO Max’s verified Reddit account and used it to run malicious ads that led people to fake download sites. The sites didn’t provide real installers, instead they tricked users into pasting and running commands in Terminal/PowerShell, causing them to…

September 15, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo