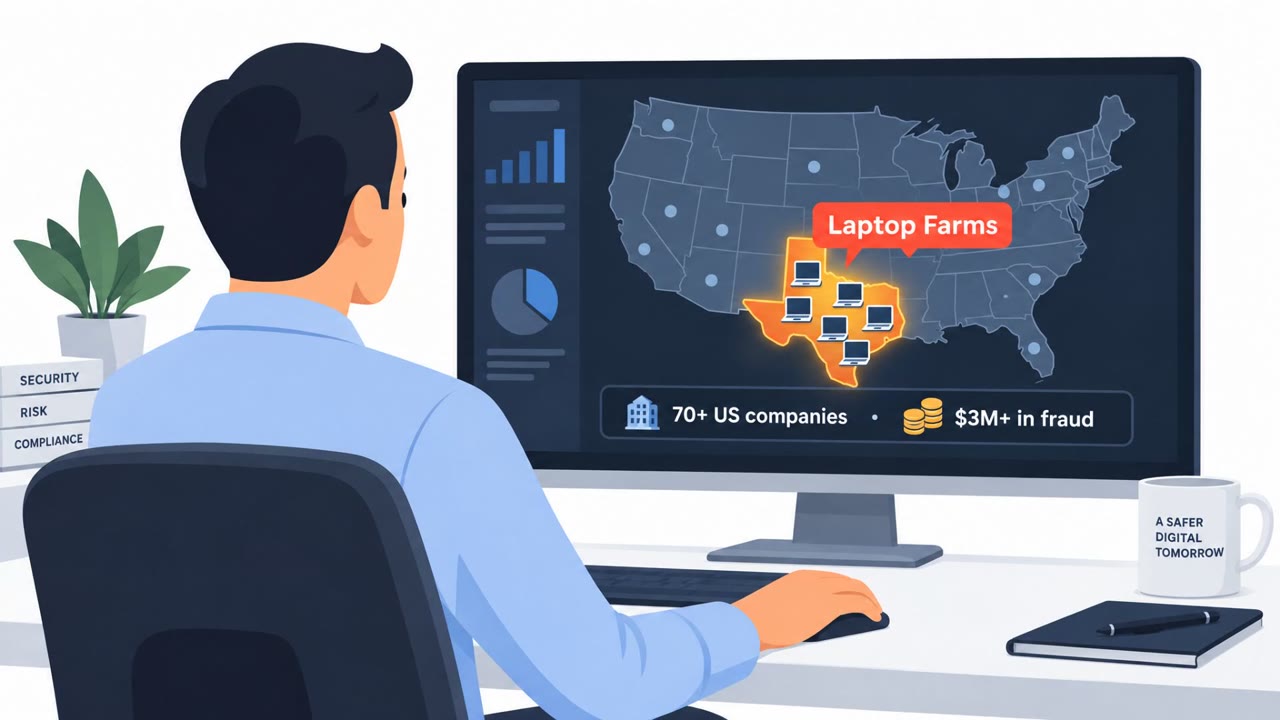
Researchers created a fake crypto startup and successfully hired three suspected North Korean IT workers by letting them pass normal remote hiring and onboarding checks. The suspected operatives used inconsistent identity documents and remote-access tooling to obtain legitimate employee accounts and access to a work virtual machine. The case highlights how “authorized” access gained through hiring can become an insider-risk and espionage pathway.
Key findings
- Researchers created a fake DeFi employer (“Ballena Azul”), posted developer roles, and hired three suspected North Korean operatives via standard remote hiring.
- Identity artifacts were inconsistent or likely altered (licenses from different states, mismatched locations/bank accounts, metadata suggesting AI editing and Google SynthID watermark).
- Once hired, the worker received legitimate access (“a real employee account and real access to source code and internal systems”), making the risk harder to detect as it appears authorized.
- On day one, the workers profiled the issued systems and checked apparent geolocation; one installed Chrome Remote Desktop and synced a personal Google account.
- Researchers observed tooling and infrastructure including 2fa.cn for sharing MFA codes, Outlook.com usage, AI interview/job-application browser extensions, and VPN/infrastructure providers (AstrillVPN, Vultr, Gorilla Servers).
- Defensive recommendations included periodic identity checks, in-person verification for remote-first companies, recruiter training, and blocking AstrillVPN; the July 31 advisory also flags many IPs per account and machine-translated profile text.
Who’s being targeted
- Commonly targeted roles: HR, Recruiting, Hiring managers, Engineering leadership, IT / Endpoint management, Security / IAM, Payroll.
- Affected industries: Software/IT services, Remote-first companies, Cryptocurrency/DeFi startups, Any organization hiring remote developers/contractors.
- Attack channels: github, email, website.
- Impersonated: Recruiter / hiring intermediary, Job candidate / new remote developer, Legitimate employee (new hire) performing ‘normal setup’.
Awareness takeaways
- Treat hiring and onboarding as a security control: validate identity beyond a single document check.
- Watch for identity mismatches (address, ID state, bank location) and possible AI-altered documents during onboarding.
- Limit and monitor remote-access tools and personal account syncing on company devices/VMs, especially for new hires.
- Flag unusual access patterns (many IPs/addresses in a short time window) and “machine translation” profile text as potential indicators.
Red flags to watch for
- Candidate pipeline is driven by a third-party recruiter plus chained referrals (“vouched for a friend, who vouched for a third”)
- Remote-only process with no in-person verification
- Pressure to rapidly provision access because the candidate ‘already passed’
- Location, ID state, and bank account geography don’t match
- ID appears altered/AI-processed (metadata/watermark signals)
- Identity documents belong to someone else or have stripped/odd metadata
- Remote desktop tool installation on day one
- Personal account sync on a corporate environment (risk of credential leakage)
- Use of external services for MFA handling
Read the video transcript
Imagine this: you hire a remote dev, and on day one, you’ve basically onboarded North Korea. Researchers built a fake DeFi startup, Ballena Azul, and a recruiter trawling GitHub delivered a developer, who vouched for a friend, who vouched for a third. All three passed normal remote interviews and got real employee accounts and a work VM. Here’s the tell: one "hire" claimed Pasadena, Texas, but sent a California driver’s license and a New York bank account. The ID image metadata even showed Google Gemini and a SynthID watermark. On day one, another installed Chrome Remote Desktop and synced a personal Google account. If a remote hire’s location, ID state, and bank don’t line up, or they push to rush access, stop. Your move: pause the hire and escalate to security for a deeper identity check before any accounts go live.