Recent Cryptocurrency Cyber Attacks

Attacks on crypto exchanges, wallet providers, and web3 projects, where phishing pages and fake airdrops drain funds in minutes. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

ClickFix Lures Spread ChainScript RAT

ClickFix Lures Spread ChainScript RAT

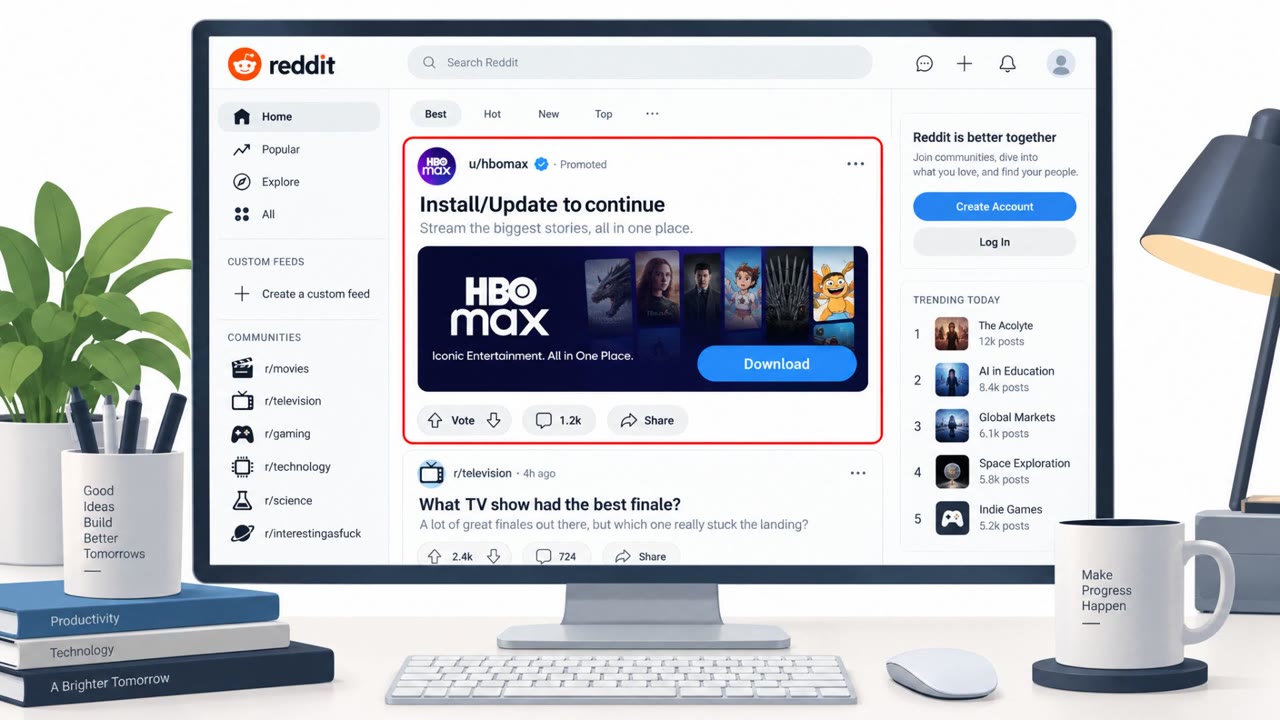
Researchers describe real-world “ClickFix” social-engineering lures that trick people into installing malware by downloading fake apps (like Spotify/Zoom/Teams) or copying commands into Terminal. One campaign abused a compromised, verified HBO Max Reddit account to run malicious ads, while another…

September 21, 2026
Revolut Smishing Uses Fake Identity Check

Revolut Smishing Uses Fake Identity Check

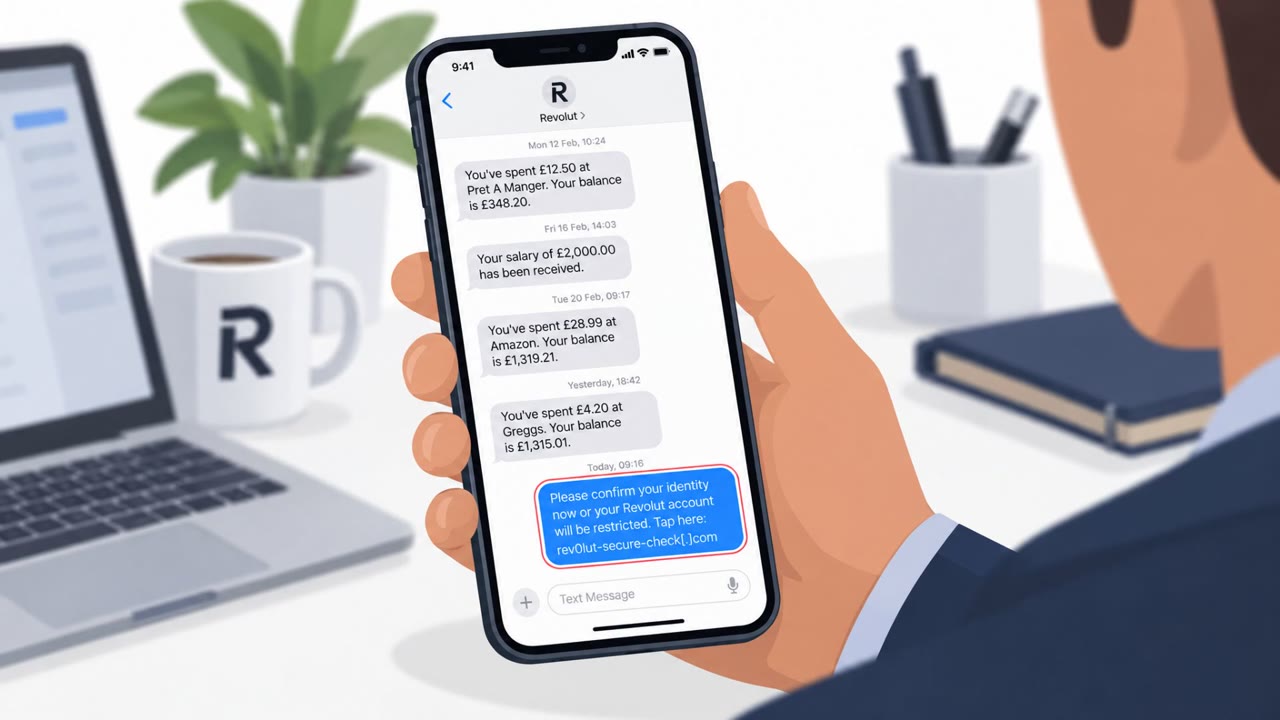
Following a Revolut data breach, scammers sent text messages that appeared to come from the same message thread as legitimate Revolut texts. The texts pushed victims to click a link for a fake identity “liveness check,” request camera access, and then capture passwords, information that could be…

September 21, 2026
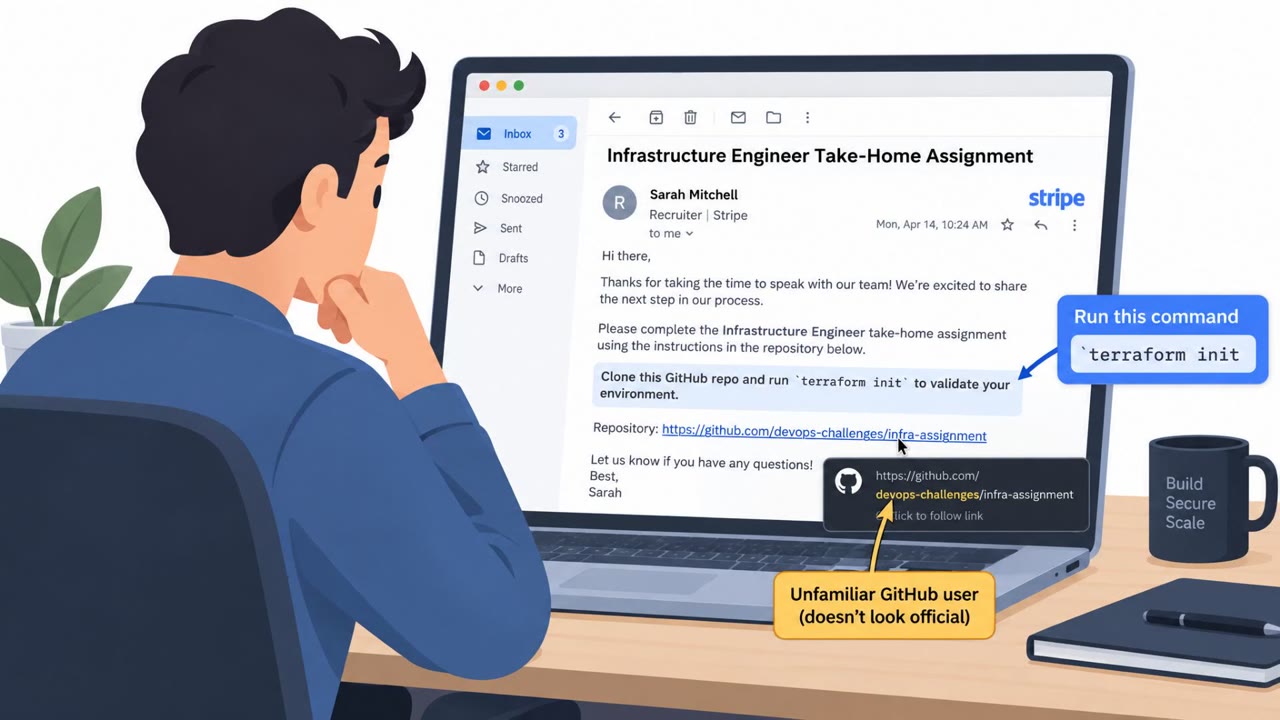
Fake Job Interview Repo Tricks DevOps Into Malware

Fake Job Interview Repo Tricks DevOps Into Malware

North Korea–linked "Jade Sleet" used job interview-style coding projects to trick developers into running malicious infrastructure code. The lure involved GitHub repositories that contained a weaponized Terraform file, leading to downloads from attacker-controlled domains and installation of macOS…

September 21, 2026
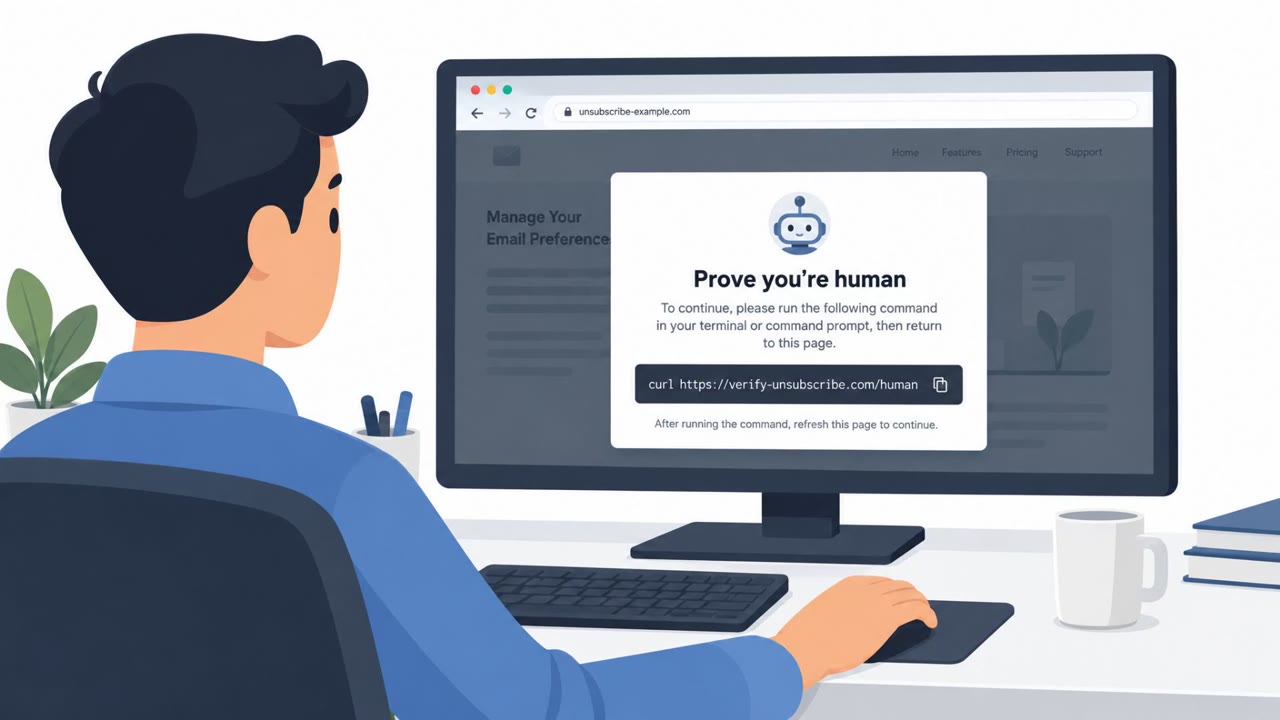
Brevo Breach Spread Malware via ‘Prove You’re Human’

Brevo Breach Spread Malware via ‘Prove You’re Human’

Attackers breached Brevo and used a stolen Cloudflare API key to inject malicious code into Brevo-hosted scripts that thousands of customer websites load. Visitors saw a fake “prove you’re human” prompt meant to trick them into running a command, and logged-in WordPress admins risked having a…

September 18, 2026
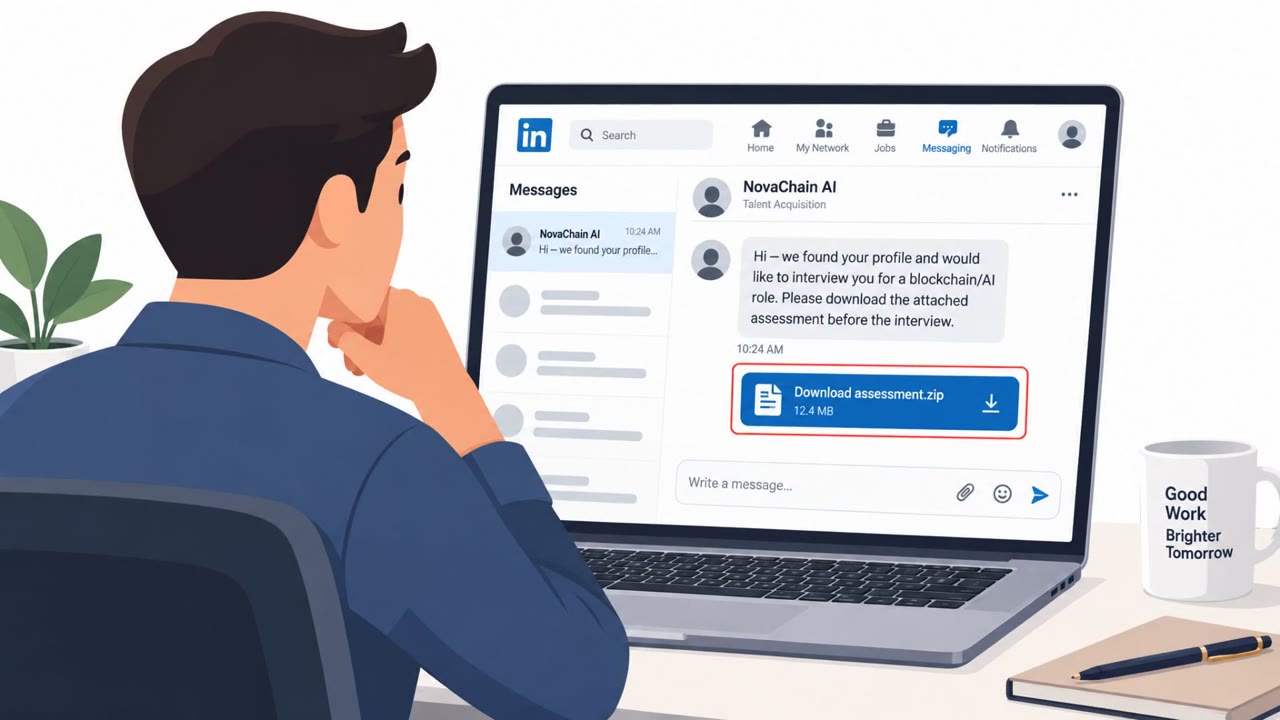
Fake Recruiters Hit Job Seekers With Malware Files

Fake Recruiters Hit Job Seekers With Malware Files

An alleged North Korean operation called “WaterPlum” targeted job seekers by posing as AI and blockchain companies and using the interview process to trick applicants into downloading malicious files. Authorities say the campaign infected tens of thousands of devices worldwide and led to theft from…

September 18, 2026
Trusted Channels Hijacked for Phishing and Malware

Trusted Channels Hijacked for Phishing and Malware

The article describes multiple real-world social engineering operations this week, including phishing sent from a legitimate Trezor newsletter channel and malware pushed through a verified HBO Max Reddit ad account. It also highlights a large-scale network of fake online stores impersonating real…

September 18, 2026
Fake Job Interviews Backdoor 30,000 Devices

Fake Job Interviews Backdoor 30,000 Devices

An international advisory says North Korea–linked actors posing as recruiters tricked jobseekers into downloading “coding assignments” during fake interview processes. Opening the files installed backdoors and malware, enabling theft from over 7,000 crypto wallets and supporting at least $10.71M in…

September 18, 2026
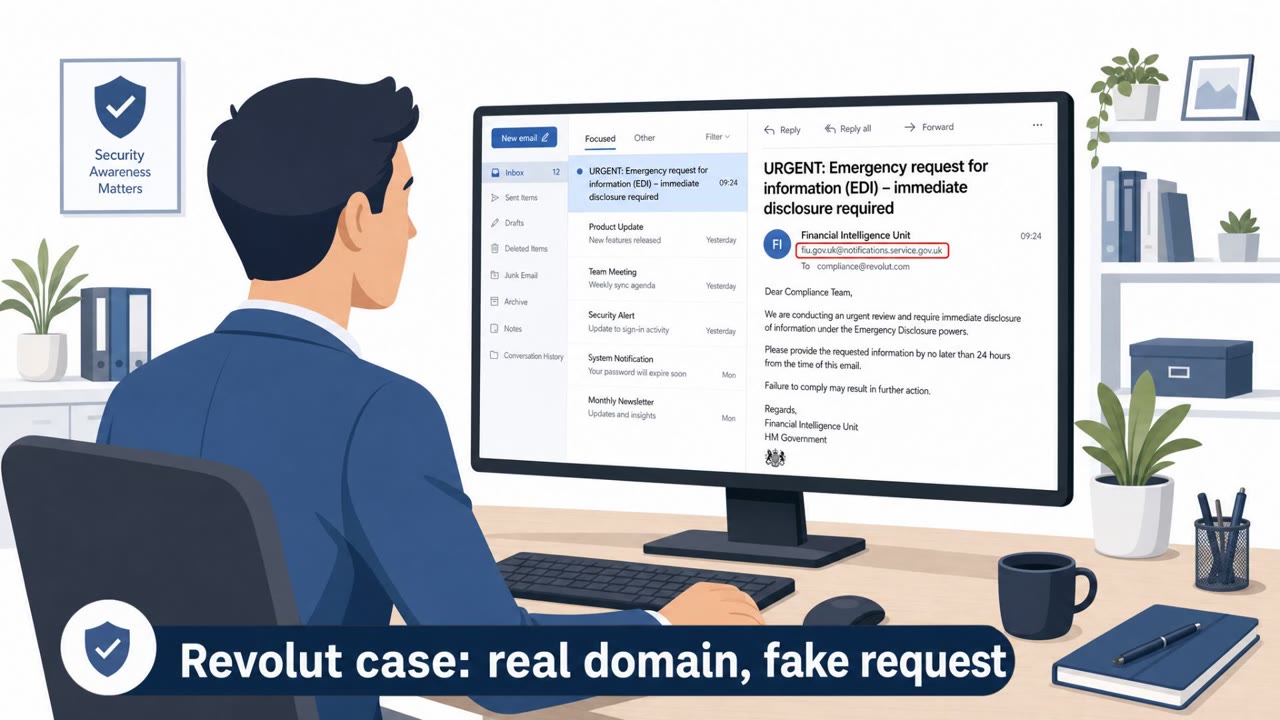
Revolut Tricked by Spoofed Government Email

Revolut Tricked by Spoofed Government Email

Revolut confirmed a customer data breach after attackers used a compromised government agency domain to submit fake “official” requests for customer information. Revolut provided sensitive details (including IDs like passports and driver’s licenses) based on those email requests, raising questions…

September 18, 2026
Brevo Hack Served ClickFix Malware to 100K Sites

Brevo Hack Served ClickFix Malware to 100K Sites

Brevo suffered a supply-chain compromise where attackers injected malicious JavaScript into Brevo-hosted pages and customer-embedded website scripts, affecting over 100,000 sites. Visitors were shown a fake “Cloudflare, verify you are human” prompt designed to trick them into running a command on…

September 18, 2026
Fake AI Trading Bot Steals Crypto Wallet Passwords

Fake AI Trading Bot Steals Crypto Wallet Passwords

Researchers observed real campaigns where a fake “AI crypto trading agent” website tricked victims into downloading malware that silently replaces browser wallet extensions and steals the wallet password when it’s typed. The same reporting also describes invoice emails using QR codes to push…

September 17, 2026
HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

Attackers compromised HBO Max’s verified Reddit advertising account and used it to run 108 malicious ads in about 48 hours. The ads sent people to attacker-controlled websites that used “ClickFix” instructions to trick users into running commands that installed malware on Windows and macOS.

September 16, 2026
HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
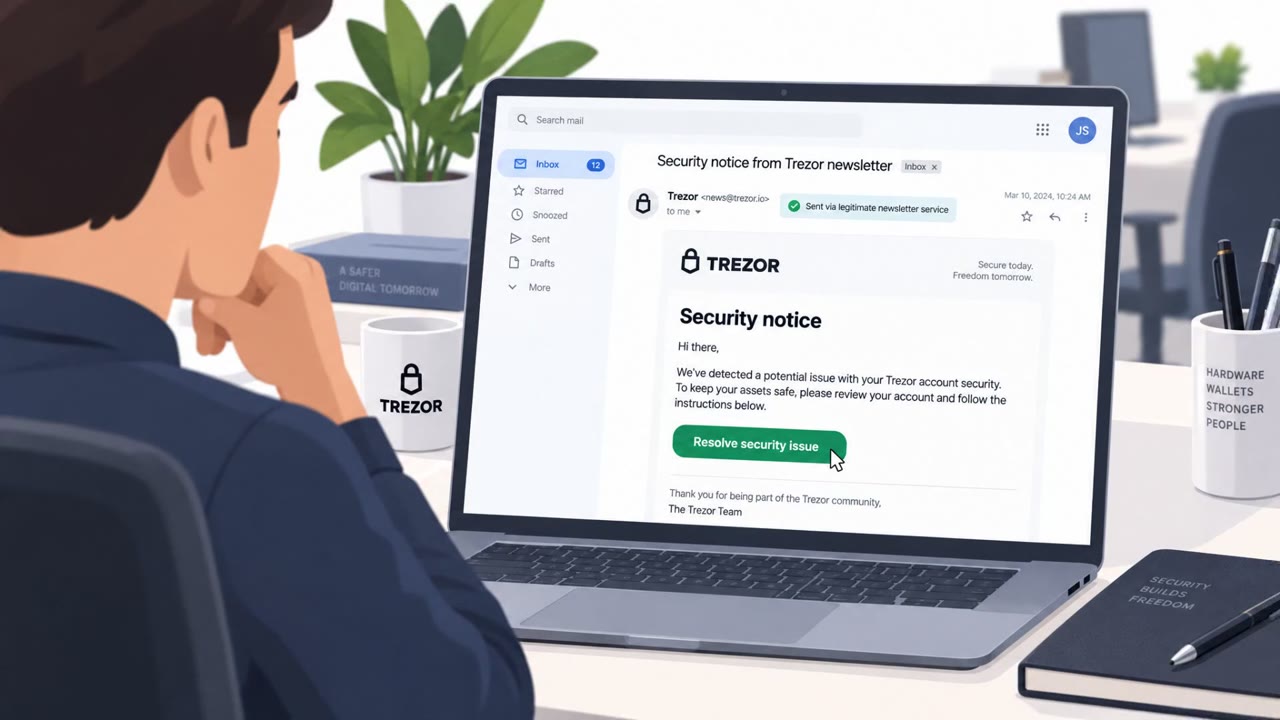
Trezor Users Hit by Phish via Brevo Breach

Trezor Users Hit by Phish via Brevo Breach

Attackers broke into Brevo, the email platform Trezor uses for newsletters, and sent a phishing “security warning” from Trezor’s real mailing system. The email claimed a serious hardware issue could expose wallet recovery seeds and pushed people to a malicious site/app that asked for a wallet…

September 14, 2026
Revolut Tricked by Fake “Emergency” Data Requests

Revolut Tricked by Fake “Emergency” Data Requests

Revolut confirmed it disclosed sensitive customer information after fraudsters sent “emergency” information requests from a legitimate government email domain. The attackers appear to have targeted high-net-worth customers, including people involved in crypto, and attempted to extort Revolut to…

September 14, 2026
Revolut Tricked by Fake Government Email

Revolut Tricked by Fake Government Email

Revolut disclosed it was deceived into sharing highly sensitive customer data after receiving fraudulent information requests that appeared to come from a legitimate government email domain. The attacker’s email passed domain authentication, making it harder to detect, and the shared data may…

September 14, 2026
Fake Govt Email Tricked Revolut Into Sharing KYC

Fake Govt Email Tricked Revolut Into Sharing KYC

Revolut says it handed over sensitive customer identity and financial data after receiving what looked like a legitimate government information request. The email came from inside a real government agency’s email domain and passed authentication checks, so staff processed it before later…

September 12, 2026
Brevo Breach Fuels Crypto Newsletter Phishing

Brevo Breach Fuels Crypto Newsletter Phishing

Attackers abused access to Brevo (an email marketing platform) to send highly convincing phishing emails from legitimate cryptocurrency company domains to newsletter subscribers. The lures claimed urgent security issues (hardware vulnerability or data breach) and pushed victims to click links,…

September 11, 2026
Trezor Users Hit by “Critical Security Alert” Phish

Trezor Users Hit by “Critical Security Alert” Phish

Trezor reported that about 347,000 customers received phishing emails after attackers abused a breach at its third‑party email marketing provider, Brevo. The phishing message used a “Critical Security Alert” theme and linked to a malicious site that attempted to trick users into entering their…

September 11, 2026
Pig Butchering Scams Drive $12.7B Crypto Losses

Pig Butchering Scams Drive $12.7B Crypto Losses

FinCEN reports that overseas scam centers stole about $12.7B from U.S. victims since 2023, largely through “pig butchering” style cryptocurrency investment scams. Scammers build trust using fake personas (often romance or “financial adviser” roles), then pressure victims to buy crypto and send it…

September 10, 2026
Fake M&A Wire Fraud and Trezor Phishing Alert

Fake M&A Wire Fraud and Trezor Phishing Alert

This bulletin describes multiple real-world scams where attackers manipulate trust to steal money or sensitive data. Notably, attackers impersonated executives to pressure legal teams into moving M&A discussions to WhatsApp/personal email to trigger international wire transfers, and Trezor users…

September 10, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo