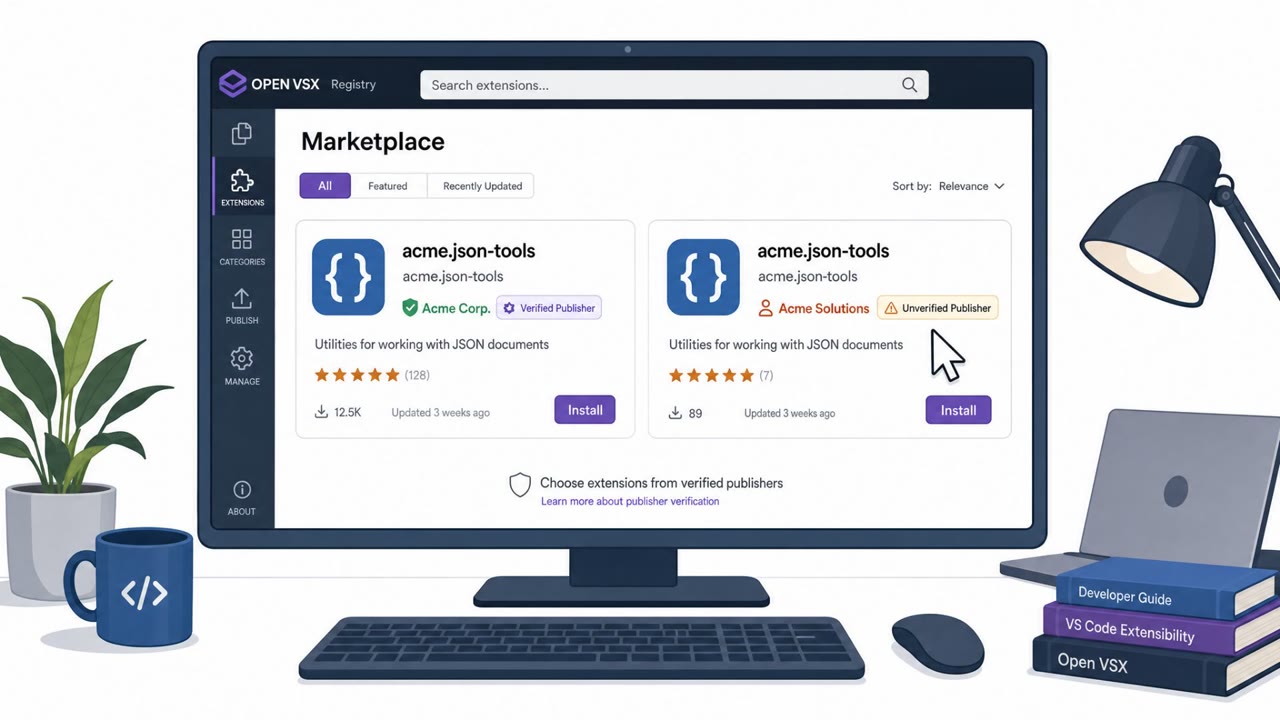
Researchers found a short burst of counterfeit extensions on the Open VSX marketplace that copied the names and descriptions of legitimate Visual Studio Code extensions. Some of these “evil twin” extensions quietly sent developer and CI/CD environment details to a newly registered domain, creating supply-chain risk for organizations that auto-provision developer tools.
How the attack worked
Over a one week window, 77 counterfeit extensions appeared on the Open VSX marketplace. Each one reused the name and listing copy of a legitimate Visual Studio Code Marketplace extension, but was published from an account unaffiliated with the original developer. Most used version 0.0.1, an inconsistency with the real extensions they impersonated. All 77 communicated with infrastructure under a single newly registered domain, and 19 of them went further, collecting OS usernames, workspace paths, Git organization and branch information, installed extension IDs, and CI identifiers from developer machines and CI/CD environments.
Why it succeeded
The technique relied on the gap between how VS Code Marketplace and Open VSX handle publisher identity. Because the two marketplaces maintain separate publisher-ownership systems, a lookalike extension can appear on Open VSX under the same name as a trusted tool without any relationship to the real publisher. That made it easy for the counterfeit listings to blend in during normal developer setup or automated image provisioning, where installs often happen with limited manual review.
What to watch for
- A publisher account that does not match the original tool's known owner
- Unusual version numbers, such as 0.0.1, on an extension that should have a longer history
- Unexpected network traffic from the editor to an unfamiliar or newly registered domain
- Extension listings that claim certain values, like CI identifiers, stay on the machine when the underlying behavior sends them elsewhere
Building resistance
Teams can reduce exposure from this kind of supply-chain impersonation with a few concrete steps:
- Treat extensions like any other dependency: install only from verified publishers and known-good versions
- Maintain an inventory of installed extensions, including what is baked into build images, since a marketplace takedown does not remove already-installed copies
- Monitor developer tooling for unusual outbound connections, particularly to newly registered domains
- Apply allowlisting controls, such as Microsoft's extensions.allowed policy, to restrict which publishers, extensions, versions, and platforms are permitted in managed fleets
This case is a reminder that developer tooling and CI/CD pipelines are part of the software supply chain, and that identity verification gaps between marketplaces can be exploited even when no credentials or source code are confirmed stolen.
Key findings
- 77 counterfeit Open VSX extensions appeared in a one-week window and impersonated legitimate VS Code Marketplace tools.
- All 77 communicated with infrastructure under a newly registered domain: mangorbit[.]com.
- 19 extensions collected detailed information about developer machines, Git repositories, and CI/CD environments (e.g., usernames, paths, org/branch, CI identifiers).
- The extensions were removed from the marketplace, but already-installed copies can persist in developer workstations and build images.
- Researchers did not find theft of source code, credentials, tokens, SSH keys, or browser data in the analyzed packages.
Who’s being targeted
- Commonly targeted roles: Developers, DevOps/Platform Engineering, CI/CD Owners, IT/Endpoint Management, Application Security.
- Affected industries: Software development, Technology, Any organization running CI/CD pipelines.
- Attack channels: website.
- Impersonated: Legitimate Visual Studio Code Marketplace extension publisher, Trusted VS Code extension (same name/listing as legitimate tool).
Red flags to watch for
- Publisher account is not the original publisher (ownership differs across marketplaces)
- Suspiciously new/odd versioning (e.g., 0.0.1) compared to the real extension
- Unexpected outbound traffic from the editor to an unfamiliar newly registered domain (mangorbit[.]com)
- Extension requests/uses data unrelated to its stated purpose (e.g., CI identifiers, workspace paths)
- Network egress from the editor to a non-business domain
- Extension listing claims certain data “stayed on the machine” but behavior contradicts that
Frequently asked questions
What happened with the fake Open VSX extensions?
Researchers found 77 counterfeit extensions on the Open VSX marketplace that copied the names and listing copy of legitimate VS Code Marketplace tools, all communicating with infrastructure under a newly registered domain.
What data did the malicious extensions collect?
19 of the 77 extensions gathered OS usernames, workspace paths, Git organization and branch information, installed extension IDs, and CI identifiers from developer machines and CI/CD environments.
Were credentials or source code stolen?
Researchers did not find theft of source code, credentials, tokens, SSH keys, or browser data in the packages they analyzed.
Is the risk over now that the extensions were removed?
No. The extensions were taken down from Open VSX, but copies already installed on developer machines or baked into build images can still persist and run.
Read the video transcript
You trust your VS Code extensions, right? Seventy‑seven fake ones just showed up on Open VSX in a single week. They copied real VS Code Marketplace listings word‑for‑word, but were published by random Open VSX accounts and most were version 0.0.1, all quietly pinging a new domain: mangorbit dot com. Once installed, nineteen of them ran inside editors and build runners, quietly grabbing OS usernames, workspace paths, Git org and branch, even CI identifiers, perfect recon on your repos and pipelines. Here’s the move: before you install or auto‑provision an extension, match the publisher and version to the real VS Code Marketplace listing, if they don’t line up, don’t let it into your image.