Hijacked Town Email Sends Payment Phish

Security Incidents DE · Medium sophistication
Last updated October 29, 2026

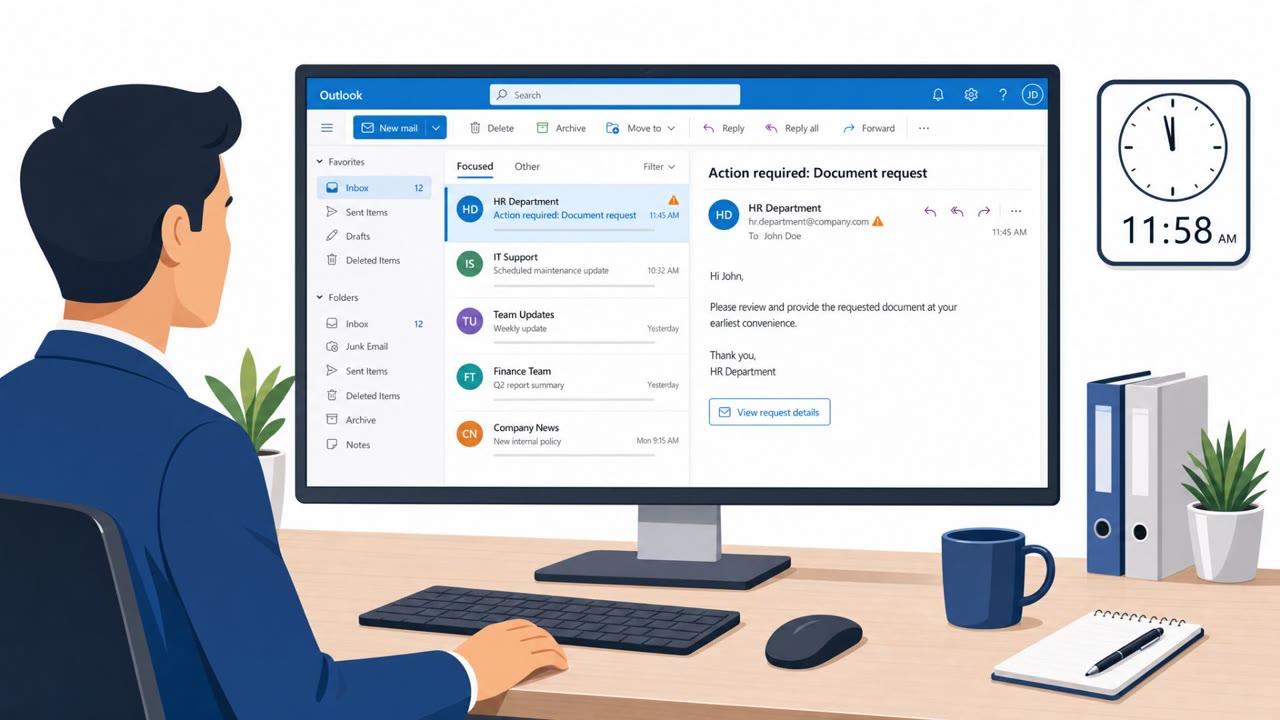
The Town of Whitsett, North Carolina, found unauthorized access to its Microsoft 365 account on October 22, 2026. An unknown party used an official town email account to send a phishing email titled "Ref: Approved Payment Report from Whitsett, NC" and included attachments recipients were told not to open.

Key findings

  • The Town of Whitsett discovered unauthorized access to its Microsoft 365 account on October 22, 2026.
  • Unknown attackers sent phishing messages from an official town email account.
  • The phishing email used the subject line "Ref: Approved Payment Report from Whitsett, NC".
  • Recipients were warned not to open the attachments or respond to the email.

Who’s being targeted

  • Commonly targeted roles: Accounts Payable, Finance, Procurement, Government employees, Vendors and external partners.
  • Affected industries: Local government, Public administration.
  • Attack channels: email.
  • Impersonated: Town of Whitsett, North Carolina.

Awareness takeaways

  • Treat unexpected attachments as suspicious, even if the email appears to come from a known organization or official account.
  • Do not reply to unexpected payment-report messages; verify the request through a trusted, separate contact method.
  • Finance and vendor-facing teams should independently verify payment-related emails because compromised trusted accounts can be used to make fraudulent messages look legitimate.

Red flags to watch for

  • An unexpected payment-related attachment, even when it comes from a legitimate-looking government address.
  • A payment report was not expected or does not relate to an active transaction.
  • The sender requests a reply or attachment opening without an established business context.
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

A real town email address can still send a phish. On October twenty-second, someone accessed the Town of Whitsett’s Microsoft 365 account. They sent an email titled, ‘Ref: Approved Payment Report from Whitsett, NC,’ with attachments. That’s the trick: the account was genuine, but the message wasn’t. If you weren’t expecting a payment report, the attachment and request to reply are red flags. Don’t open it or reply. Call your known Whitsett contact to check.

Categories

Similar attacks

M365 Direct Send Spoofs Internal HR & Finance

M365 Direct Send Spoofs Internal HR & Finance

Researchers observed a real phishing campaign that abused Microsoft 365’s “Direct Send” feature to deliver messages that looked like they came from trusted internal addresses (HR, accounting, admin). The emails commonly used familiar business lures like invoices, payment approvals, voicemail…

September 11, 2026
Silent Lynx Used Gov Emails to Lure Targets

Silent Lynx Used Gov Emails to Lure Targets

Researchers say the Kazakhstan-linked group “Silent Lynx” has run real espionage campaigns across Central Asia, targeting government bodies and energy organizations. The reported entry method relied heavily on spear‑phishing sent from compromised government email accounts, sometimes using trusted…

October 15, 2026
China-Linked Phish Uses Fake Gmail Preview

China-Linked Phish Uses Fake Gmail Preview

A China-linked espionage group (UAT-11587) targeted Asian government and policy organizations using highly tailored phishing emails and realistic decoy documents. After a click, malware ultimately installed the “Antino” backdoor, which then hid its command-and-control traffic inside normal…

October 3, 2026
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

Microsoft reports that the Russia-linked group Star Blizzard expanded from highly targeted spear-phishing to larger email campaigns aimed at Ukraine supporters globally. Lures included tax-audit/unpaid-fine notices and fake conference invitations, followed by a password-protected archive that…

September 30, 2026
Star Blizzard’s RedFlick Phish Uses VHDX Trap

Star Blizzard’s RedFlick Phish Uses VHDX Trap

Microsoft reports real-world Star Blizzard phishing campaigns where victims who engage with an initial email receive a follow-up message containing a password-protected ZIP/RAR attachment. The attachment chain hides a malicious shortcut disguised as a PDF, opening a decoy file while quietly…

September 30, 2026
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

Microsoft reports that the Russian state-linked actor Star Blizzard ran large-scale phishing campaigns in 2026 that use convincing lures like tax notices, fines, and “closed-door” event invitations. After a victim replies, the attacker sends a password-protected ZIP/RAR attachment that triggers a…

September 29, 2026