Recent Transportation and Logistics Cyber Attacks

Page 3 of 5
Fake Recruiters & Cloud Email Fuel New Phishing

Fake Recruiters & Cloud Email Fuel New Phishing

This roundup describes real-world social engineering where attackers impersonate recruiters on LinkedIn and lure developers into running “coding tests” that install malware. It also outlines active phishing campaigns that abuse trusted cloud services (Google, AWS, Azure, Cloudflare) to send…

September 2, 2026
Fake LinkedIn Coding Tests Deliver Mirage Kitten Malware

Fake LinkedIn Coding Tests Deliver Mirage Kitten Malware

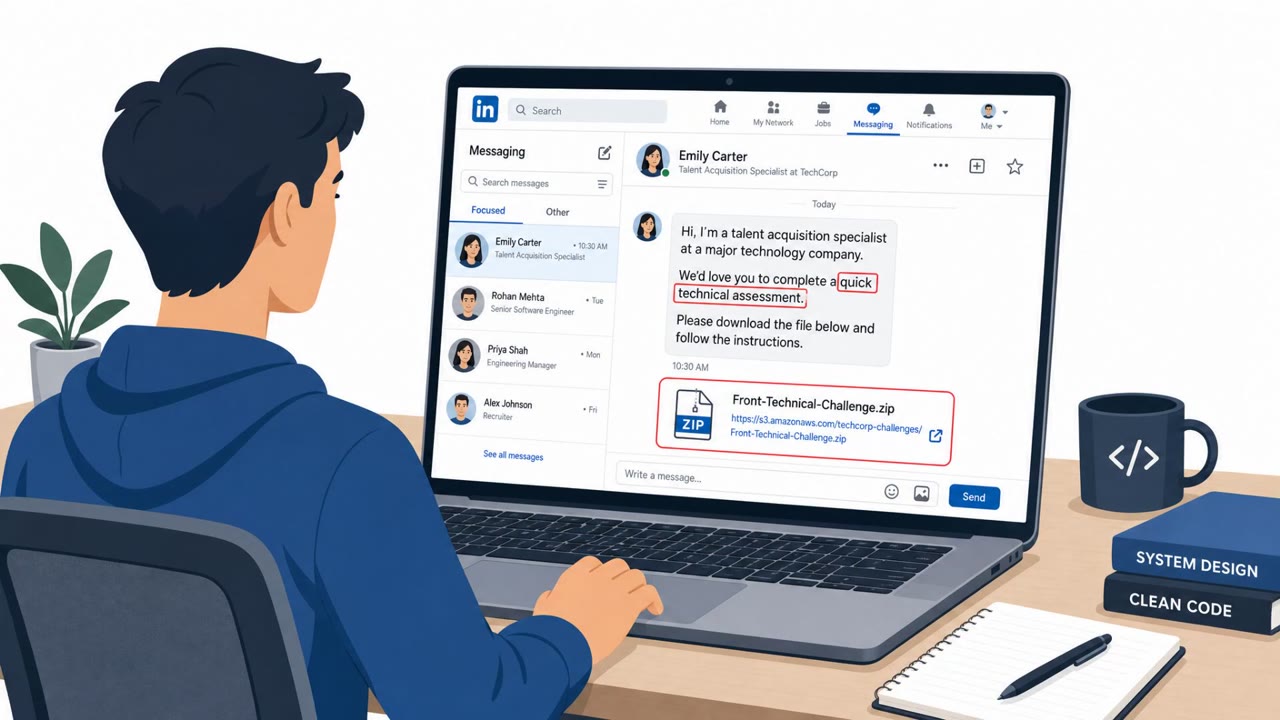
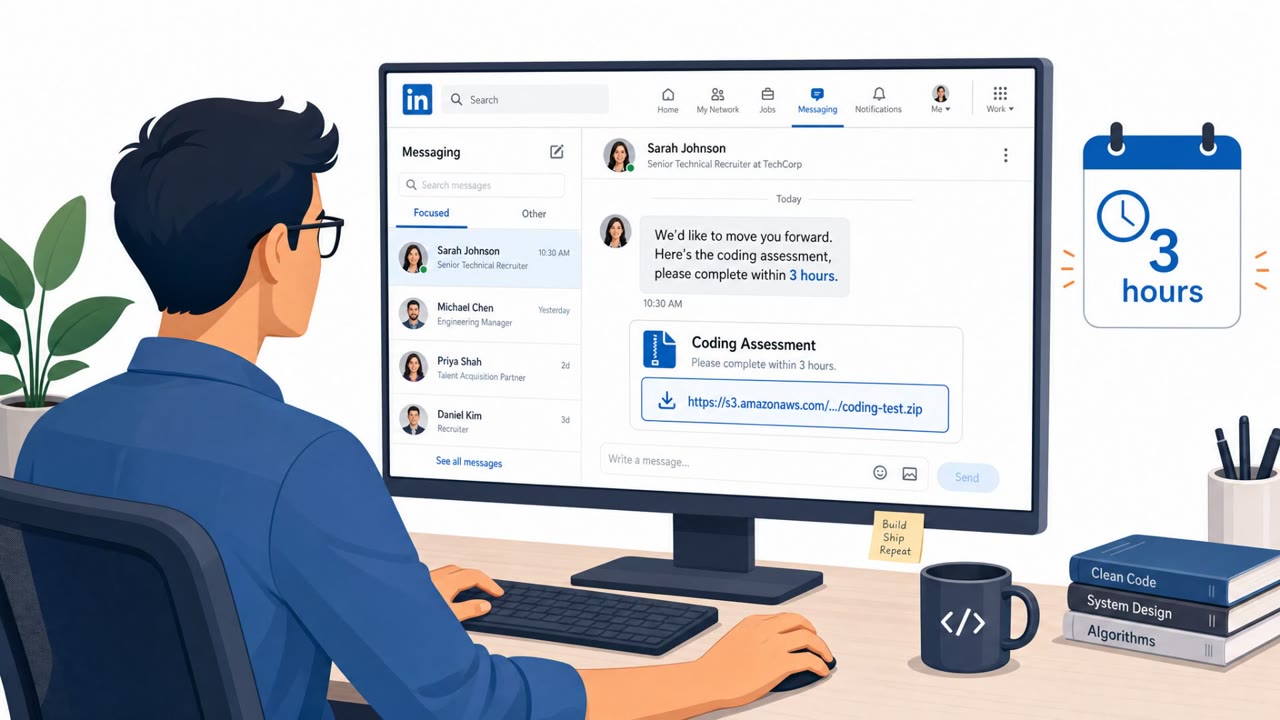
Kaspersky reported that Iran-linked APT Mirage Kitten approached software engineers on LinkedIn using fake recruiter personas and sent “coding challenges” that were actually trojanized projects. The lure used legitimate-looking cloud hosting (Amazon S3) and even instructed victims not to use AI…

September 2, 2026
Fake Download Sites Push Malware Installers

Fake Download Sites Push Malware Installers

Microsoft reports an active campaign where attackers set up counterfeit software download pages that mimic well-known brands and trick users into installing malware. Victims visit a look-alike vendor site, click “Download now,” then run a bundled installer that drops persistent malware and connects…

September 2, 2026
Fake Recruiters Lure Devs Into Malware “Coding Tests”

Fake Recruiters Lure Devs Into Malware “Coding Tests”

An Iran-linked espionage group contacted developers and other tech specialists with fake job offers on LinkedIn and similar platforms. Victims were pushed to quickly download and run “coding challenges” that secretly installed new malware, giving attackers remote access and long-term persistence.…

September 1, 2026
Fake Recruiter Lure Drops NodeRabbit RAT

Fake Recruiter Lure Drops NodeRabbit RAT

Researchers tied Mirage Kitten to a job-recruiting scam that targets developers via LinkedIn and job platforms. Victims are sent a “technical assessment” ZIP file hosted on legitimate cloud storage; running the project silently installs a remote-access trojan (NodeRabbit) that lets attackers…

September 1, 2026
Vishing + Phishing Drive Major Data Theft Claims

Vishing + Phishing Drive Major Data Theft Claims

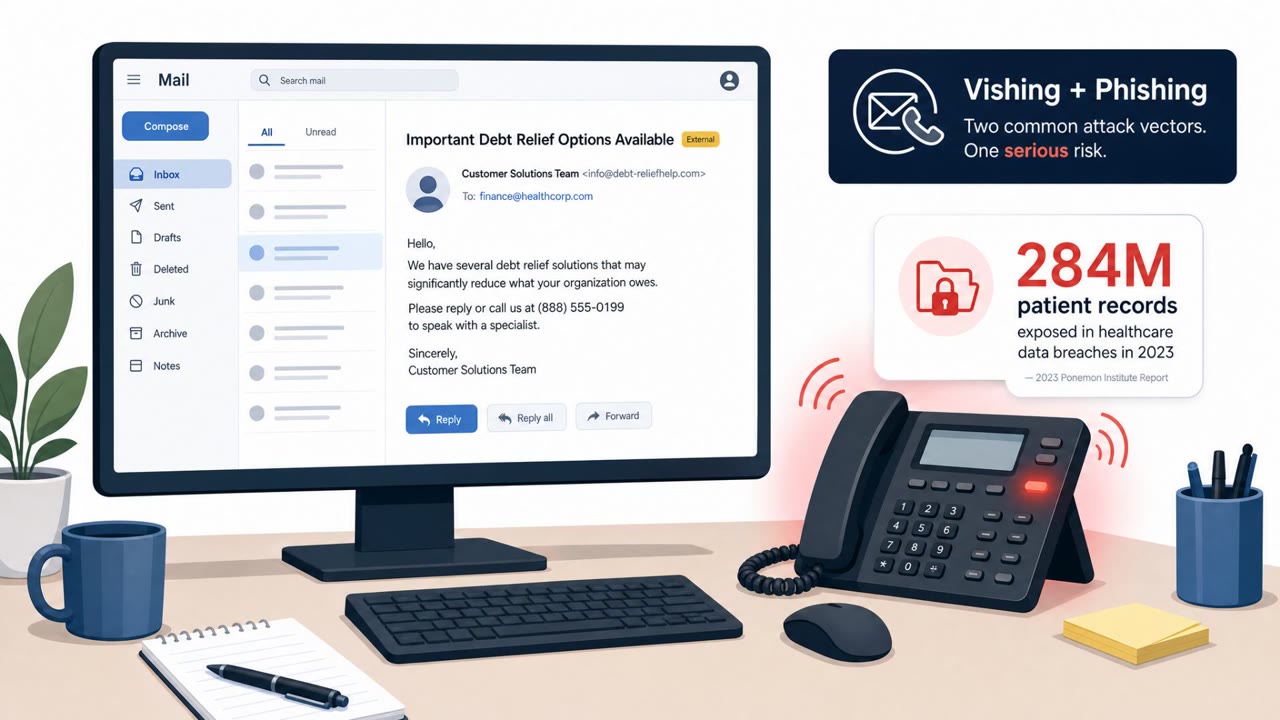
This weekly threat bulletin highlights multiple real-world incidents, including a healthcare data breach claim where attackers reportedly used phone-based social engineering (vishing) to compromise identity accounts and access cloud apps. It also describes a large-scale “debt relief” email phishing…

August 31, 2026
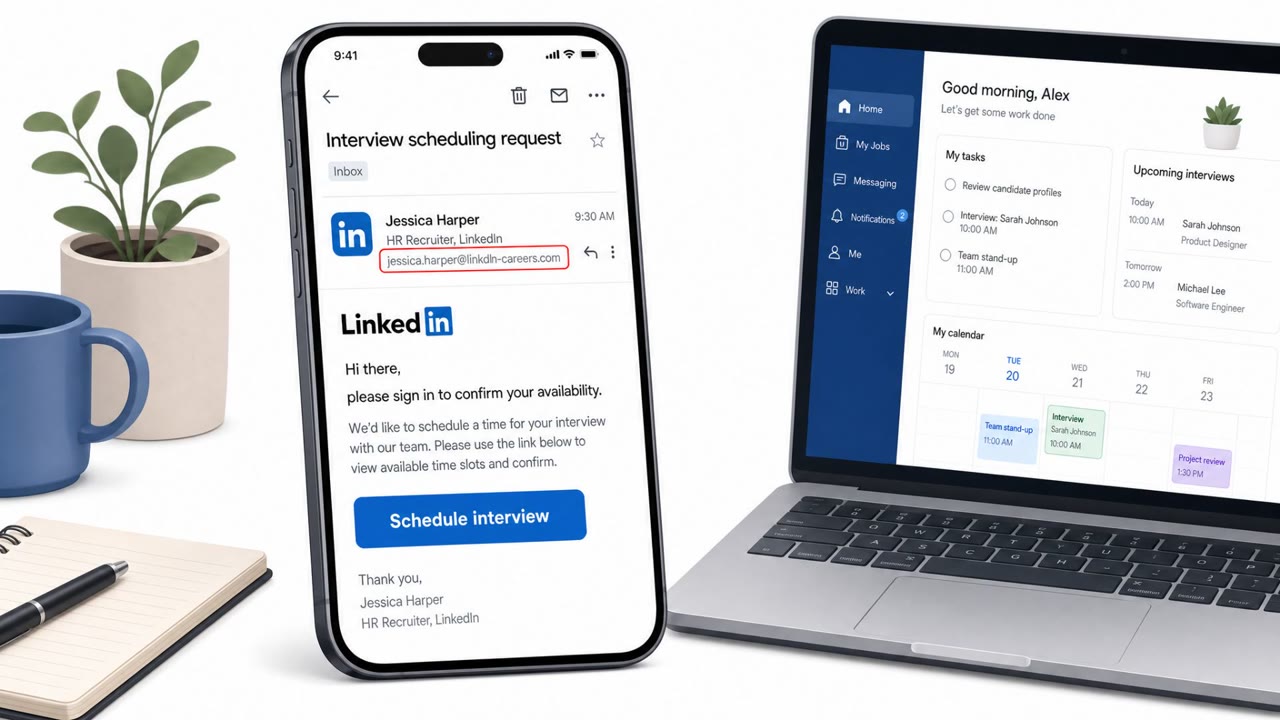
Fake Recruiters Steal Corporate Logins on Mobile

Fake Recruiters Steal Corporate Logins on Mobile

Scammers posing as HR staff at major brands are luring targets into an interview “scheduling” flow that ultimately steals corporate passwords on mobile devices. The campaign uses a browser-in-the-browser style approach (or a full-screen fake login on phones) and even blocks personal email logins to…

August 26, 2026
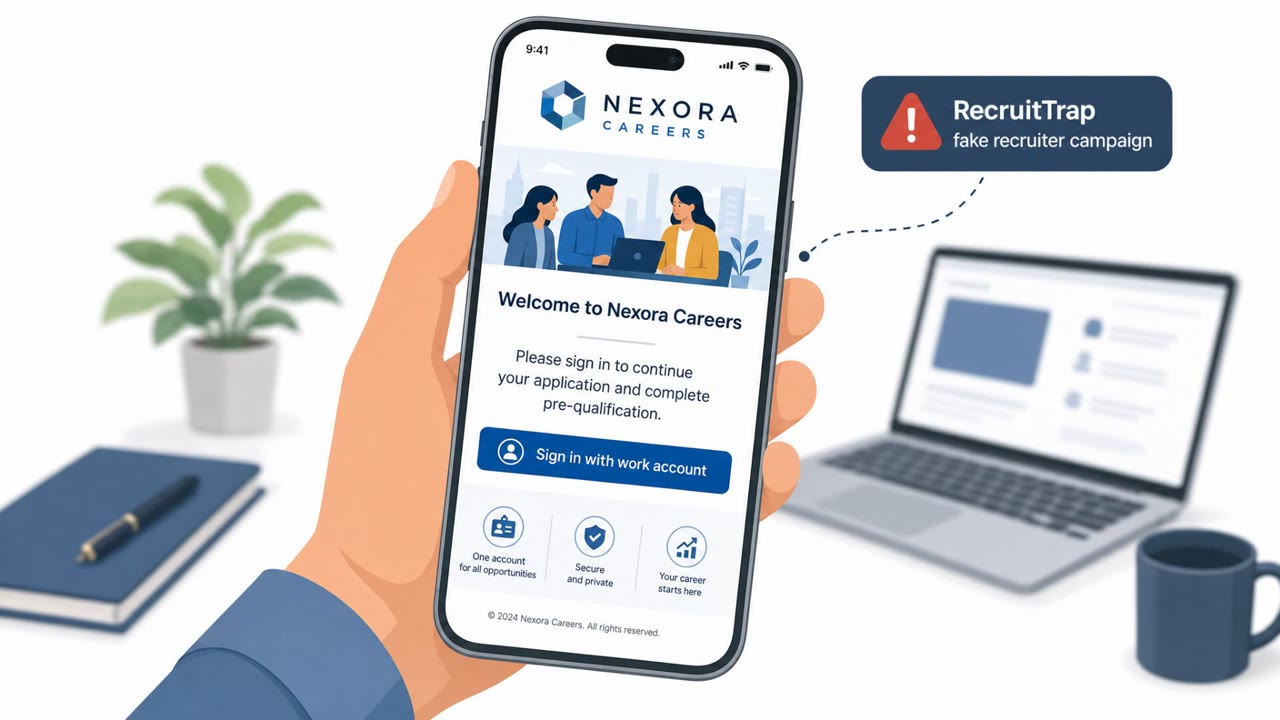
Fake Recruiters Steal Enterprise Logins on Mobile

Fake Recruiters Steal Enterprise Logins on Mobile

A real “fake recruiter” phishing campaign (tracked as RecruitTrap) is targeting employees’ corporate credentials, especially on mobile devices. The scam uses lookalike recruitment domains and full-screen fake login pages that hide browser cues, and it rejects personal email addresses to focus on…

August 25, 2026
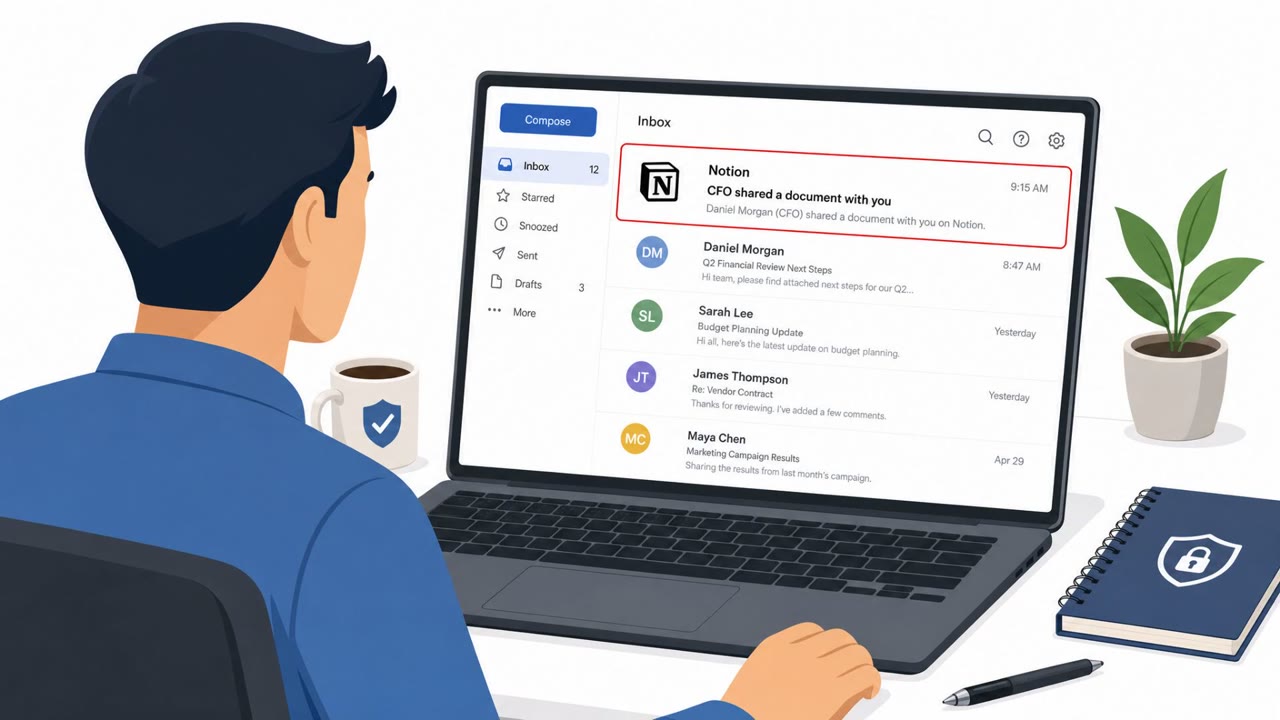
Notion Alerts Used to Steal Microsoft Tokens

Notion Alerts Used to Steal Microsoft Tokens

A financially motivated actor (“Doubloon Dredger”) abused legitimate Notion sharing notifications to trick employees into opening a PDF and completing a Microsoft device-code login flow. This allowed the attacker to harvest authentication tokens and access victim accounts without needing the…

August 24, 2026
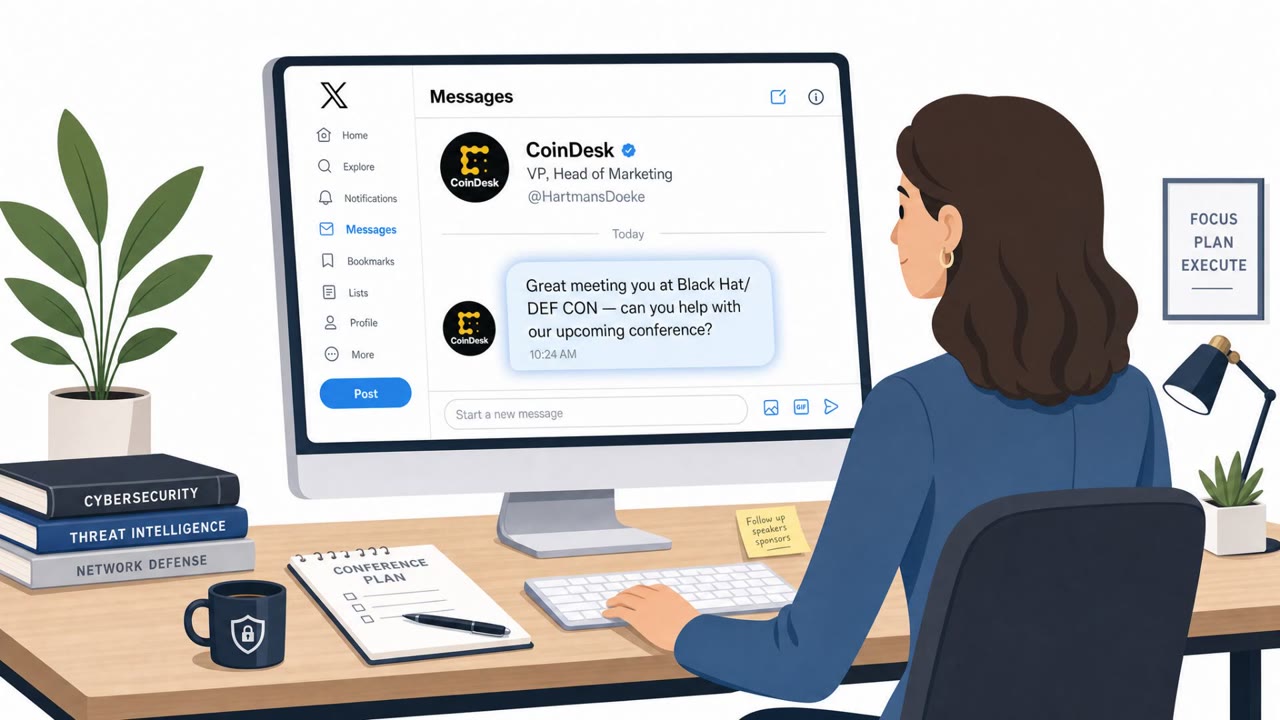
DEF CON Attendees Hit With Fake CoinDesk DMs

DEF CON Attendees Hit With Fake CoinDesk DMs

After Black Hat/DEF CON, cybercriminals allegedly targeted conference attendees by impersonating a CoinDesk executive over X direct messages. Victims were pushed into a realistic workflow using Google Docs and a fake Dropbox DocSend installer to trick them into running malware on macOS or Windows.

August 21, 2026
Fake Airline Apps Push Android Banking Fraud

Fake Airline Apps Push Android Banking Fraud

Researchers report two Android banking malware families (ToxicPanda 2.0 and GoldDigger) that rely on tricking people into installing malicious apps and granting powerful permissions. GoldDigger campaigns impersonate airlines and shopping retailers and then abuse Android Accessibility to take over…

August 20, 2026
BlackFile Vishing Poses as IT Support to Extort Firms

BlackFile Vishing Poses as IT Support to Extort Firms

Researchers say the BlackFile extortion group is actively targeting large financial and other organizations using voice-phishing calls where attackers impersonate IT support to get initial access. Victims are then pressured with multimillion-dollar extortion demands and, in some cases, escalations…

August 17, 2026
Vishing “Help Desk” Scams and Lookalike Phish Surge

Vishing “Help Desk” Scams and Lookalike Phish Surge

This weekly roundup highlights multiple real-world social engineering threats, including fake IT help-desk phone calls that push employees to phishing sites to steal passwords and one-time authentication codes. It also describes credential-phishing sites impersonating WhatsApp and Instagram that…

August 14, 2026
Fake “Delta WiFi FAST” Tricked Flyers

Fake “Delta WiFi FAST” Tricked Flyers

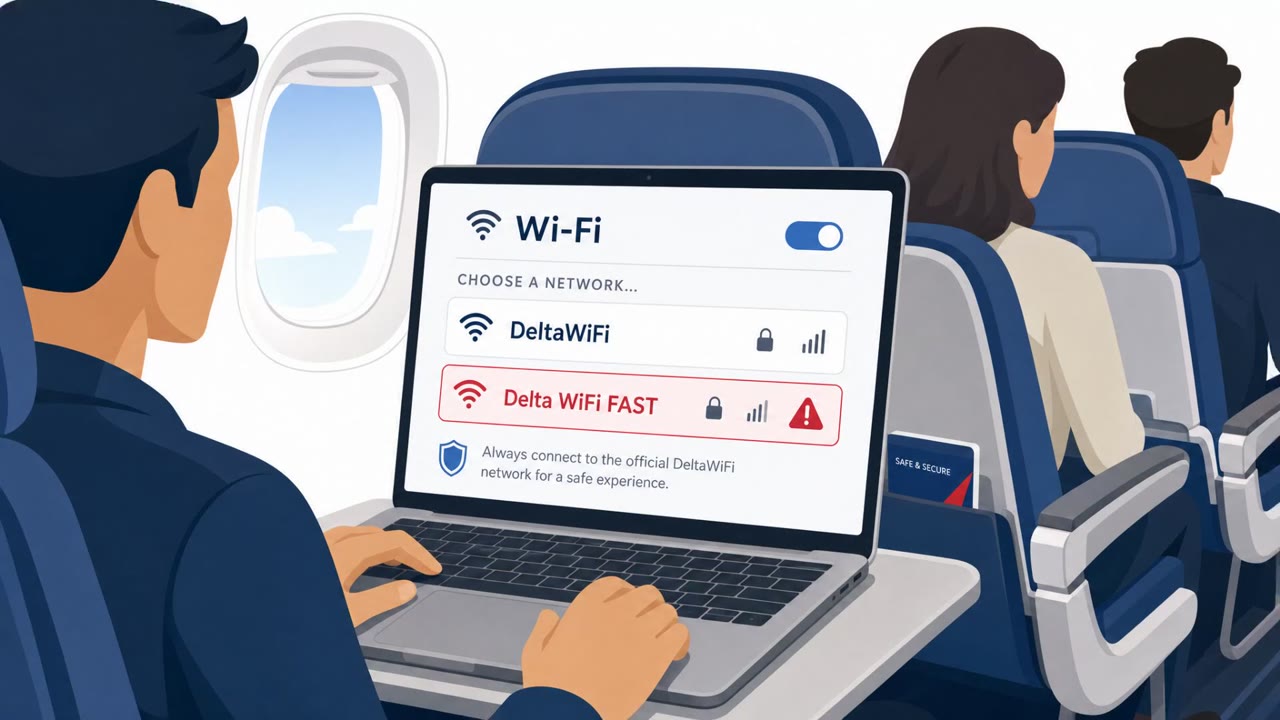
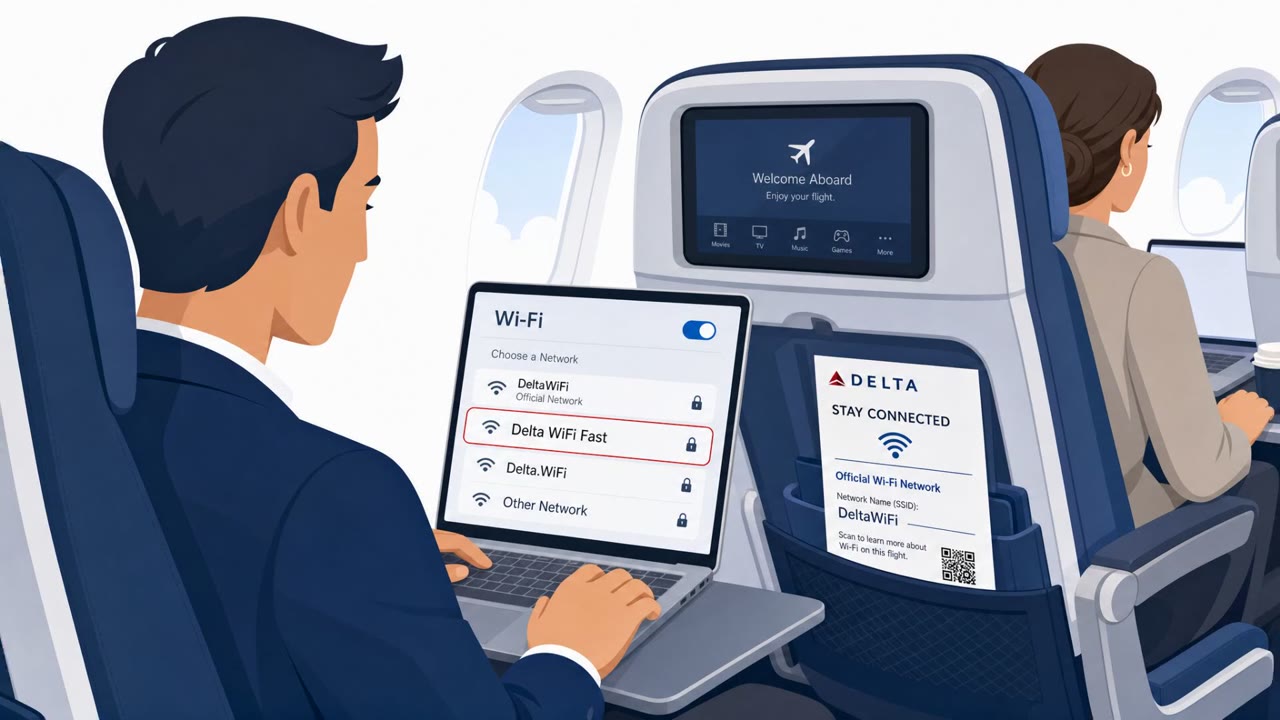
A passenger on a Delta flight allegedly set up a look‑alike Wi‑Fi network (“Delta WiFi FAST”) and tried to disrupt the real onboard Wi‑Fi so other passengers would join the fake hotspot. The goal was likely to push users to a login page and capture credentials (e.g., Google or Facebook). This is a…

August 14, 2026
Real-Time ‘JWR’ Smishing Steals Cards and OTPs

Real-Time ‘JWR’ Smishing Steals Cards and OTPs

Cisco Talos reported a real-world SMS phishing campaign using a framework called “JWR” that impersonates toll agencies and postal/courier services to lure victims to fake payment and login pages. Unlike basic phishing pages, the operator can actively steer the victim through fake checkout/login…

August 13, 2026
Helix Extortion Hit Uber Freight via Helpdesk Vishing

Helix Extortion Hit Uber Freight via Helpdesk Vishing

Uber Freight is investigating unauthorized access after the Helix extortion group claimed it stole nearly one million files from company cloud and email repositories. Google-linked research says the broader cluster (UNC6671) commonly gets in by calling employees and posing as IT helpdesk staff…

August 12, 2026
Fake “Delta WiFi Fast” Hit Passengers After DEF CON

Fake “Delta WiFi Fast” Hit Passengers After DEF CON

A passenger on a Delta flight allegedly set up a look‑alike in‑flight Wi‑Fi network (“Delta WiFi Fast”) to trick other passengers into connecting. Reports say the fake hotspot led to a phishing page intended to steal personal credentials, including Google login data. Delta confirmed the incident…

August 12, 2026
Freight Scammers Hijack Trucking Identities for AI Gear

Freight Scammers Hijack Trucking Identities for AI Gear

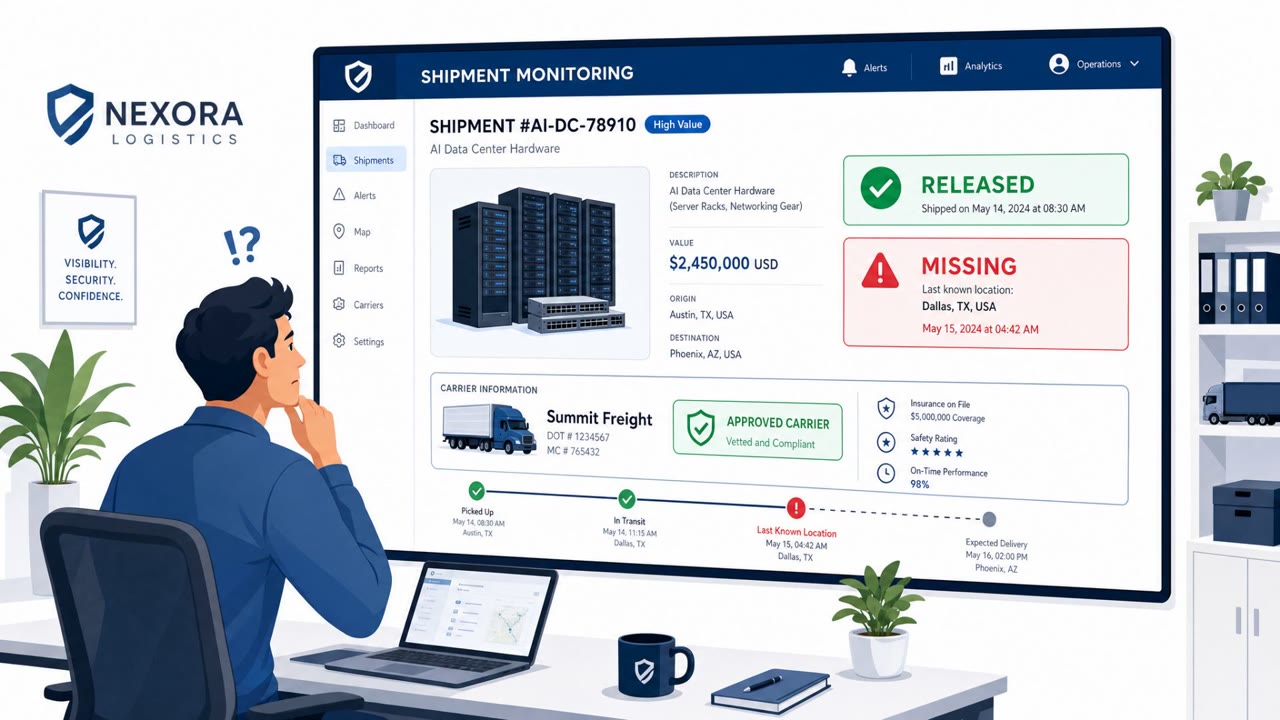
The article describes real cargo theft operations targeting high-value AI data center equipment, including cases where escort vehicles were deliberately disabled so shipments could disappear. It also explains a repeatable fraud workflow where criminals use phishing/social engineering to take over a…

August 12, 2026
Rogue “Delta WiFi Fast” Network Disrupts Flight

Rogue “Delta WiFi Fast” Network Disrupts Flight

Delta is investigating an onboard incident where an unauthorized Wi‑Fi network appeared on a flight and the crew shut off Wi‑Fi for about 30 minutes. Reports say a rogue network named “Delta WiFi Fast” may have been used to trick passengers into connecting and potentially entering credentials into…

August 11, 2026
Fake Job Offers Spread Lazarus Zero-Day Attack

Fake Job Offers Spread Lazarus Zero-Day Attack

Researchers describe a real, ongoing Lazarus-linked campaign where targets are lured with attractive job offers and tricked into downloading a PDF viewer and “job description” documents. Opening the files installs backdoors and, in at least one wave, attackers used a Windows zero-day to gain deep…

August 11, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo