Threat Watcher

Page 33 of 33
ClickFix Lures Push Trojanized Apps, Starland RAT

ClickFix Lures Push Trojanized Apps, Starland RAT

Cisco Talos reports a real, financially motivated campaign where victims are tricked via a “ClickFix” style lure into running a command that downloads a weaponized HTA file. That HTA then installs trojanized versions of legitimate software (e.g., WebEx/Zoom/MobaXterm) that deploy Starland RAT and…

July 16, 2026
TfL Help Desk Tricked, Hackers Got “Keys”

TfL Help Desk Tricked, Hackers Got “Keys”

Two teen hackers linked to the Scattered Spider collective gained deep access to Transport for London (TfL) by tricking the TfL help desk into resetting remote-access authentication onto a device the attackers controlled. TfL said the intrusion could have caused catastrophic disruption, forced…

July 16, 2026
LinkedIn Exec Impersonation Beat MGM Help Desk

LinkedIn Exec Impersonation Beat MGM Help Desk

The article highlights how attackers can quickly build convincing executive “profiles” from public information and use them to manipulate employees. It cites the 2023 MGM Resorts incident where attackers allegedly used an executive’s LinkedIn details to impersonate them in a help desk phone call…

July 16, 2026
700-Agent Call Center Scam Stole €100M/Month

700-Agent Call Center Scam Stole €100M/Month

Police say an organized crime group ran around 20 fraudulent call centers with over 700 staff who posed as “financial advisers” to trick people into fake investments. Victims were contacted by phone and online for weeks or months, shown fake profits on fraudulent trading platforms, then pressured…

July 16, 2026
Fake “Qantas IT Help” Vishing Led to Data Theft

Fake “Qantas IT Help” Vishing Led to Data Theft

Qantas avoided a formal Australian privacy regulator investigation after a June 2025 breach that impacted about 5.12 million people. The breach started with a phone-based social engineering call where an attacker posed as “Qantas IT help” and convinced a call-centre agent to connect a customized…

July 16, 2026
Fake “Qantas IT Help” Call Led to 5.7M Leak

Fake “Qantas IT Help” Call Led to 5.7M Leak

Australia’s Privacy Commissioner said Qantas’ 2025 breach was triggered by a tech-support phone scam targeting a contact center agent. The caller posed as “Qantas IT help” and coached the agent to take steps in the CRM that actually connected it to a data-extraction tool, enabling theft of customer…

July 16, 2026
Finance Phishing That Looks Like Routine Work

Finance Phishing That Looks Like Routine Work

Cofense reports that attackers target finance teams with phishing emails designed to look like normal invoices, contracts, and payment notices, not urgent “act now” scams. These “boringly normal” messages blend into everyday finance workflows, which can lead staff to click links or open attachments…

July 16, 2026
AsyncAPI npm Packages Poisoned via Malicious PR

AsyncAPI npm Packages Poisoned via Malicious PR

Attackers compromised the @asyncapi npm organization by abusing a misconfigured GitHub Actions workflow, then republished multiple AsyncAPI-related packages with a hidden loader. The malware ran automatically when the poisoned packages were imported (not during install), pulled a second-stage…

July 16, 2026
Fake Mac Crash Reporter Steals Passwords

Fake Mac Crash Reporter Steals Passwords

Researchers warn about a new macOS infostealer called “CrashStealer” that pretends to be Apple’s Crash Reporter. It uses a legitimate-looking installer and a fake macOS-style password prompt to trick users into unlocking Keychain, then steals credentials and crypto wallet data.

July 15, 2026
OkoBot Fakes Wallet App Screens to Steal Seed Phrases

OkoBot Fakes Wallet App Screens to Steal Seed Phrases

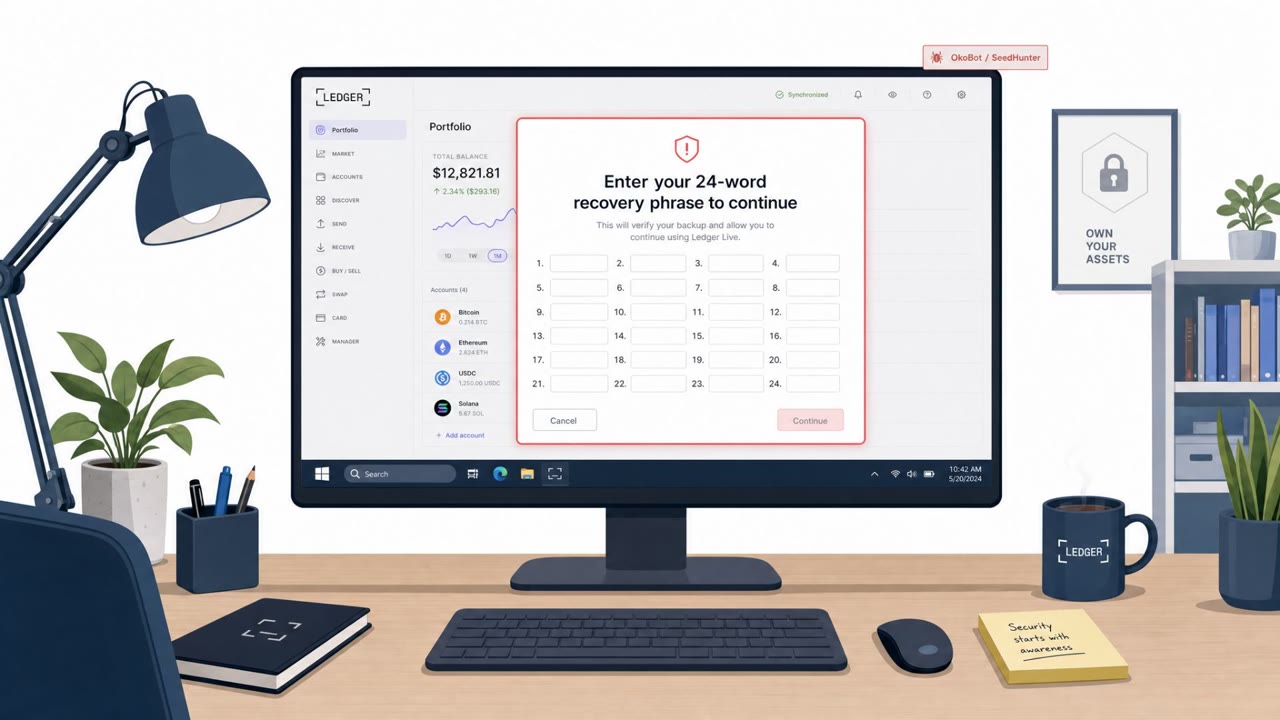
A real malware campaign called OkoBot is infecting Windows PCs and then showing a fake “recovery phrase” prompt inside legitimate Ledger and Trezor desktop apps. Victims are tricked into typing their wallet seed phrase into a malicious page that looks like it came from the trusted app, allowing…

July 15, 2026
Fake Céline Dion Tickets Trap Fans on Facebook

Fake Céline Dion Tickets Trap Fans on Facebook

Scammers are approaching Céline Dion fans on Facebook and steering them into paying for “tickets” outside official resale channels. Victims may even receive a real-looking Ticketmaster transfer link, but scammers send the same ticket to multiple buyers so only the first person scanned at the venue…

July 15, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo