Amazon captured records showing attackers using AI agents in a campaign that attempted to bypass identity checks at two cryptocurrency exchanges. The agents created deepfake video and forged identity-document photos to impersonate legitimate users during verification, although the reported video attempts were rejected by one verification provider.
How the attack worked
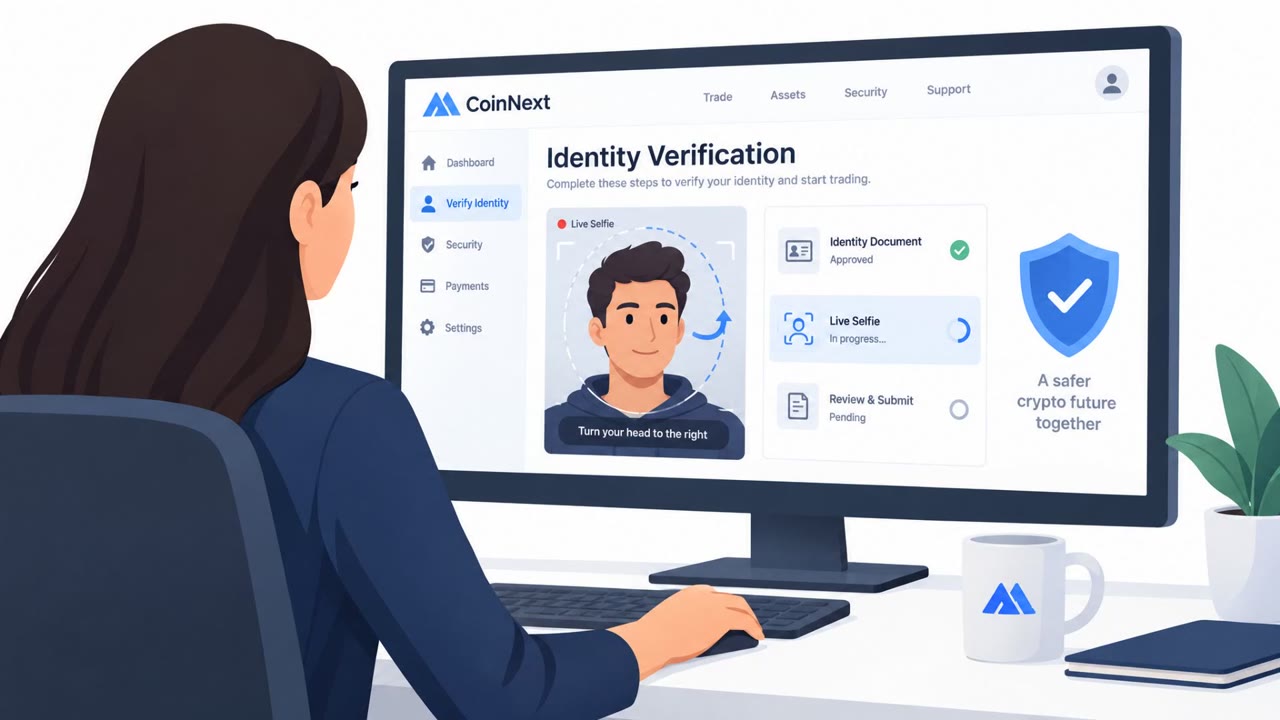
Amazon's decoy-server records describe a campaign where AI agents attempted to bypass identity verification at two cryptocurrency exchanges. The agents combined two tactics: generating live deepfake video of a fake applicant and fabricating identity-document photos to pair with that video. Together, these were used to try to pass through the onboarding checks that exchanges rely on to confirm a real person is behind an account.
In the recorded attempts, the live deepfake video was rejected every time by one verification vendor. It is not known whether the forged identity-document images passed separate document checks, since that detail was not disclosed in the captured records.
Why it succeeded, or didn't
The live-video channel held up against repeated automated attempts, which suggests that vendor had controls capable of detecting synthetic video characteristics. But the uncertainty around whether the forged document photos were caught highlights a gap: verification systems that check video and documents separately, rather than cross-referencing them together with other signals, may leave an opening even when one channel is resistant to spoofing.
The broader context also matters. The same captured records showed AI agents being used at scale to hunt for exposed AI applications and harvest provider keys, which points to attackers treating identity fraud and credential theft as parallel, automatable workflows rather than one-off manual efforts.
What to watch for
- Repeated video-verification attempts from the same applicant profile after an initial rejection
- Unnatural movement, lighting inconsistencies, or lip-sync mismatches in submitted verification video
- Identity-document images that do not clearly match the live applicant or show signs of digital alteration
- Account applications where document and video verification results seem inconsistent with each other
Building resistance
Identity verification and fraud teams should treat repeated failed video-verification attempts as a signal worth escalating rather than a routine retry. Repeated attempts can indicate an attacker tuning a deepfake or synthetic-identity attempt until it passes.
Layered verification is a stronger defense than any single check. Comparing live video, document images, account behavior, and other signals together makes it harder for a forged document or synthetic video to pass unnoticed, especially since it is unclear whether fabricated documents alone can clear some checks.
Finally, since the broader campaign involved stealing AI-provider keys from exposed applications, AI application administrators and cloud teams should ensure unique credentials, avoid hard-coded keys, and patch exposed interfaces promptly, closing off the kind of basic security gaps the agents were able to exploit elsewhere in the same operation.
Key findings
- Amazon's decoy-server records describe a second campaign in which AI agents attempted to bypass identity checks at two cryptocurrency exchanges.
- The agents used both live deepfake video and fabricated identity-document photos as part of the identity-verification attempts.
- One verification vendor rejected the live deepfake video on every recorded attempt.
- Amazon assessed with moderate confidence that separate China-linked groups operated the agents, based in part on Simplified Chinese prompts and China time-zone settings.
- The same captured records also documented large-scale technical efforts to steal AI-provider keys from exposed AI applications.
Who’s being targeted
- Commonly targeted roles: Identity verification teams, Fraud analysts, Cryptocurrency exchange operations, Customer onboarding teams, AI application administrators, Cloud and CI/CD administrators.
- Affected industries: Cryptocurrency exchanges, Financial services, Identity verification services, AI application providers, Cloud services.
- Attack channels: website.
- Impersonated: A legitimate cryptocurrency-exchange customer.
Red flags to watch for
- The applicant's live video may show unnatural movement, lighting, lip synchronization, or other signs of manipulation.
- Identity-document photos may be fabricated or may not match the live applicant.
- Repeated verification attempts after rejection can indicate an effort to tune or retry a synthetic identity.
Frequently asked questions
What did Amazon find about AI agents and deepfakes?
Amazon's decoy-server records describe a campaign in which AI agents attempted to bypass identity checks at two cryptocurrency exchanges using live deepfake video and fabricated identity-document photos.
Did the deepfake video attempts succeed?
No. One verification vendor rejected the live deepfake video on every recorded attempt, though it was not disclosed whether the fabricated ID document photos passed document checks.
Who was behind the campaign?
Amazon assessed with moderate confidence that separate China-linked groups operated the agents, based partly on Simplified Chinese prompts and China time-zone settings.
What else did the captured records reveal?
The same records documented a separate, large-scale effort to steal AI-provider keys from internet-exposed AI applications, verify the stolen keys, and pool them for reuse.
Read the video transcript
That failed crypto-exchange selfie check? It may be a test. Amazon's decoy records show AI agents tried identity checks at two exchanges, submitting forged ID photos and live deepfake video while posing as customers. Here's the tell: one vendor rejected every recorded deepfake-video attempt. Repeated failures may mean someone is tuning the fake. Check video movement, lighting, lip sync, and whether the ID matches. If you review identity checks, escalate repeated video failures for fraud review, don't approve based on the ID photo alone.