Recent Financial Services Cyber Attacks

Phishing, vishing, and social engineering attacks on banks, insurers, fintechs, and payment providers, and the customers they serve. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

One-Click Sogou Link Trick Dropped GRAYRABBIT

One-Click Sogou Link Trick Dropped GRAYRABBIT

Researchers reported a real intrusion where a China-linked group used a crafted link to exploit Sogou Input Method on Windows and install the GRAYRABBIT backdoor. Victims were lured into opening a special link (potentially via email or chat), which redirected Sogou’s built-in browser to an…

September 11, 2026
China-Linked Hackers Push “Gemini” Phish With Zero-Days

China-Linked Hackers Push “Gemini” Phish With Zero-Days

Proofpoint reports multiple China-aligned espionage groups used a chained set of browser/Windows zero-days (“BlueMoon”) and delivered it through phishing emails. Victims who clicked a phishing link could end up with a malicious browser extension disguised as Google Gemini, letting attackers watch…

September 11, 2026
Pig Butchering Scams Drive $12.7B Crypto Losses

Pig Butchering Scams Drive $12.7B Crypto Losses

FinCEN reports that overseas scam centers stole about $12.7B from U.S. victims since 2023, largely through “pig butchering” style cryptocurrency investment scams. Scammers build trust using fake personas (often romance or “financial adviser” roles), then pressure victims to buy crypto and send it…

September 10, 2026
Spy Groups Phish Victims Into Chrome Exploit Kit

Spy Groups Phish Victims Into Chrome Exploit Kit

Researchers reported four separate espionage groups using the same “BlueMoon” exploit kit within days, targeting organizations in the US and Southeast Asia. The attacks began with phishing emails that lured recipients to attacker-controlled websites, where Chrome and Windows vulnerabilities were…

September 10, 2026
Crypto Newsletter Breach Triggers Fake Security Emails

Crypto Newsletter Breach Triggers Fake Security Emails

Attackers abused access to a third-party email newsletter provider to send convincing “security alert” emails from legitimate-looking crypto company domains. The emails pushed users to click links that led to phishing sites designed to look nearly identical to real platforms. Trezor, CoinTracking,…

September 10, 2026
Fake M&A Wire Fraud and Trezor Phishing Alert

Fake M&A Wire Fraud and Trezor Phishing Alert

This bulletin describes multiple real-world scams where attackers manipulate trust to steal money or sensitive data. Notably, attackers impersonated executives to pressure legal teams into moving M&A discussions to WhatsApp/personal email to trigger international wire transfers, and Trezor users…

September 10, 2026
AI Brands Used as Bait in Phishing Waves

AI Brands Used as Bait in Phishing Waves

Microsoft Threat Intelligence reports real campaigns where attackers impersonate popular AI tools (like ChatGPT, Copilot, DeepSeek, and Claude) to trick people into clicking links, installing fake software, or entering payment and login details. One campaign sent up to 100,000 emails in a day to…

September 10, 2026
Fake Google Support Bait Led to $245M Crypto Theft

Fake Google Support Bait Led to $245M Crypto Theft

A Singaporean man, Malone Lam (aliases including “Anne Hathaway”), pleaded guilty to leading a group that stole over $245 million in cryptocurrency from U.S. victims. The group used social engineering, such as posing as Google Support and using spoofed phone numbers, to trick victims into handing…

September 10, 2026
Gigabud Hides Fake Bank App in Android Work Profile

Gigabud Hides Fake Bank App in Android Work Profile

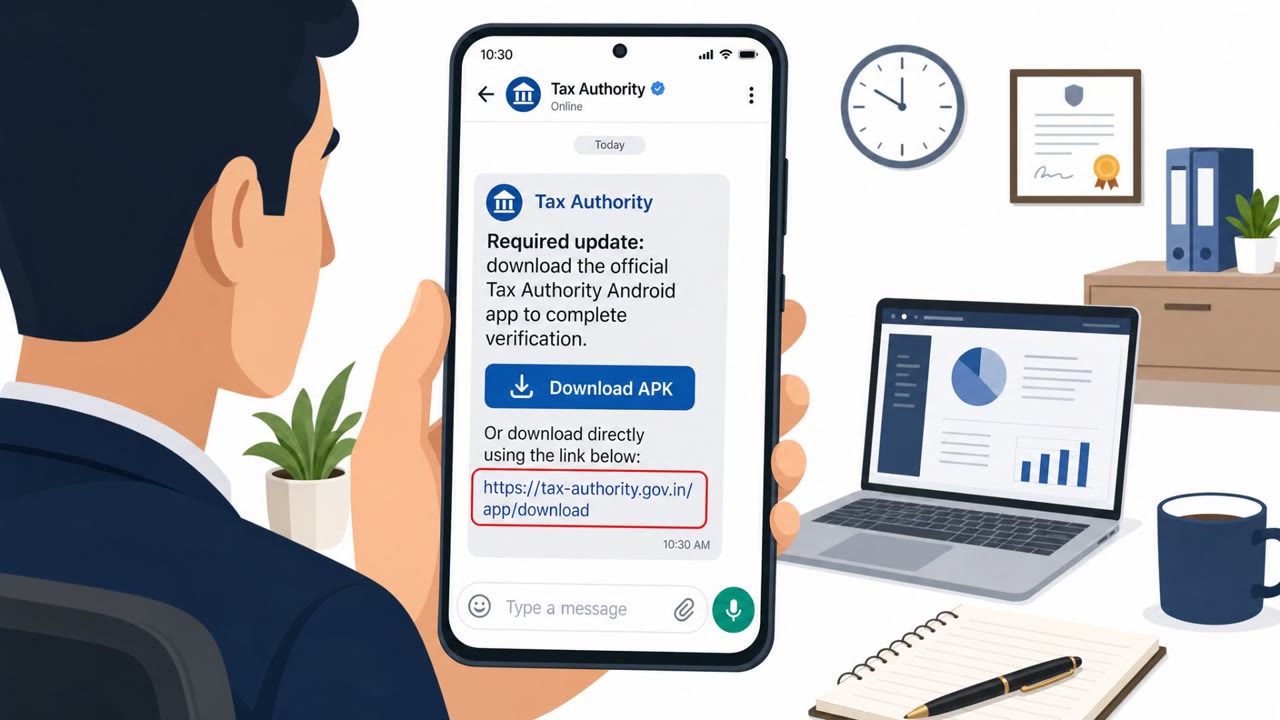
Researchers say the Gigabud banking trojan is being installed via fake apps (e.g., pretending to be an airline, tax office, or government portal) and then uses an Android “work profile” to hide a tampered banking app. Victims are tricked into granting powerful permissions, after which attackers can…

September 10, 2026
Brevo Breach Sparks Trezor Phishing Wave

Brevo Breach Sparks Trezor Phishing Wave

Trezor said attackers breached its third-party email provider (Brevo) and gained access to Trezor’s email domain, triggering phishing emails to subscribers. The scam emails used a fake “critical security alert” about a supposed microcontroller vulnerability and attempted to trick users into handing…

September 10, 2026
BlueMoon Phishing Lures Drop Chrome Zero-Day Chain

BlueMoon Phishing Lures Drop Chrome Zero-Day Chain

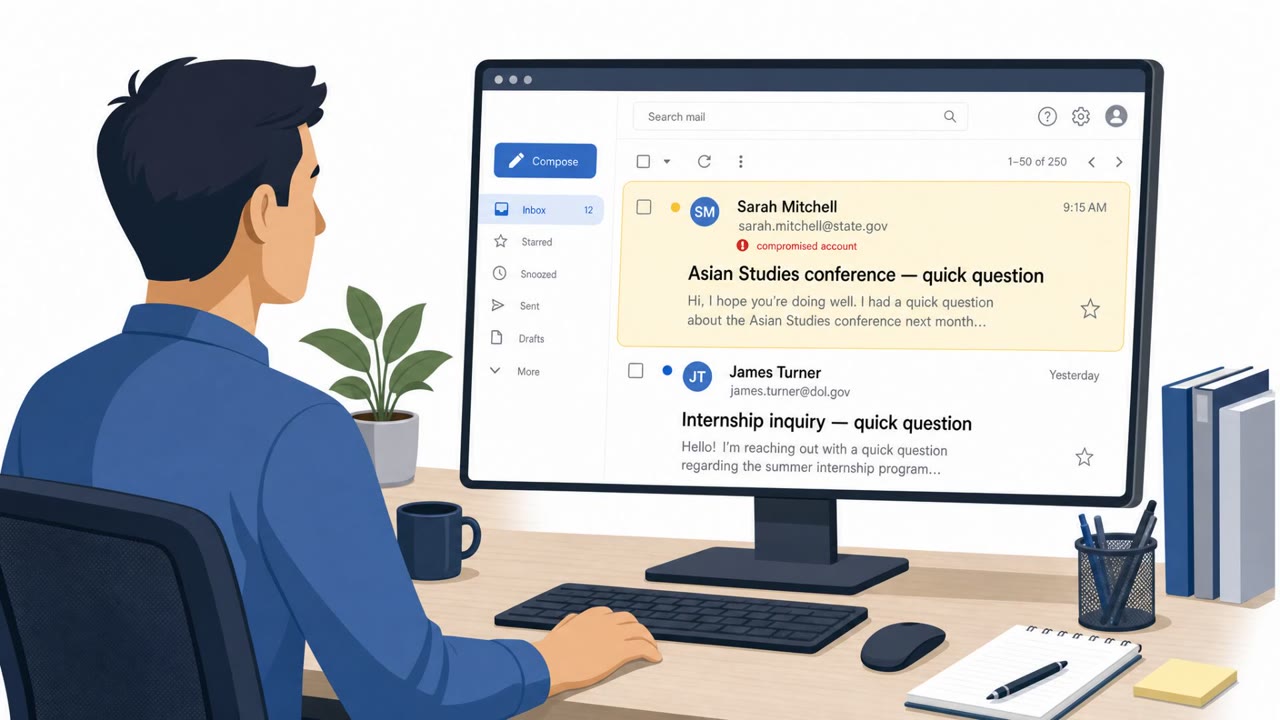
Researchers found multiple espionage groups using the same Chrome+Windows exploit kit (“BlueMoon”) within days of each other. The groups sent realistic phishing emails (internship requests, conference outreach, procurement inquiries, and vaccination appointments) that pushed victims to click links…

September 10, 2026
BlueMoon Phishing Uses Browser Zero-Days to Spy

BlueMoon Phishing Uses Browser Zero-Days to Spy

Multiple suspected China-linked espionage groups used a new exploit kit (“BlueMoon”) that starts with phishing emails and a malicious link to break into organizations in the US and Southeast Asia. Clicking the link can trigger browser and Windows vulnerabilities to install surveillance tools,…

September 9, 2026
APT31 Phish Drops Fake “Gemini” Extension

APT31 Phish Drops Fake “Gemini” Extension

Multiple China-aligned espionage groups used phishing emails to deliver a “BlueMoon” exploit chain that abused three zero-day flaws in Chrome/Chromium and Windows. In observed campaigns, victims who clicked the phishing link ended up with a malicious browser extension disguised as Google Gemini,…

September 9, 2026
Hidden Prompts Hijack ChatGPT Connected Apps

Hidden Prompts Hijack ChatGPT Connected Apps

Check Point demonstrated a prompt-injection technique where a hidden instruction inside ChatGPT can make a user’s session quietly run extra tasks using the session’s existing permissions. In the proof of concept, the victim’s ChatGPT (with Gmail connected) pulled email data and relayed it to an…

September 9, 2026
Phishing Uses Google Links to Steal Microsoft Logins

Phishing Uses Google Links to Steal Microsoft Logins

Researchers reported an active, large-scale phishing campaign that starts with links hosted on legitimate Google services, then redirects victims to attacker-controlled sites. The final pages mimic Microsoft sign-in or “identity verification” flows to steal credentials/MFA codes or trick targets…

September 9, 2026
Spy Groups Lured Victims to BlueMoon Exploit Links

Spy Groups Lured Victims to BlueMoon Exploit Links

Proofpoint reports multiple espionage-focused threat groups used a shared exploit kit (“BlueMoon”) after tricking targets with spear-phishing emails to click malicious links. Visiting the attacker-controlled web pages triggered Chrome and Windows exploits to install malware (including a fake…

September 9, 2026
China-Linked Hackers Share Chrome Exploit Lures

China-Linked Hackers Share Chrome Exploit Lures

Proofpoint reported at least four espionage groups (mostly linked to Chinese state intelligence) using the same Chrome zero-day exploit kit (“BlueMoon”) to compromise victims and deliver malware. The operations used believable business and event-themed lures (internship inquiries, procurement…

September 9, 2026
Gigabud Clones Banking Apps to Dodge Fraud Alerts

Gigabud Clones Banking Apps to Dodge Fraud Alerts

Researchers say the Gigabud Android banking trojan now clones a victim’s real banking app into a hidden Android Work Profile, so fraud can happen in a separate space that may not trigger the same malware and fraud signals. Victims are tricked into installing what looks like legitimate apps…

September 9, 2026
Ukraine Probe Links Officials to Scam Call Centers

Ukraine Probe Links Officials to Scam Call Centers

Ukraine’s prosecutor general resigned after investigators alleged officials took bribes to protect fraudulent call centers from police action. The article describes how these scam centers use phone-based impersonation (bank staff, police, financial advisers) and direct victims to fake investment…

September 9, 2026
Crypto Scammers Posed as Apple/Google Support

Crypto Scammers Posed as Apple/Google Support

U.S. prosecutors say a group led by Malone Lam ran social engineering scams that stole over $245 million in cryptocurrency. The scammers allegedly called crypto holders while pretending to be customer support from Apple or Google, talked victims into handing over key account details, and in at…

September 8, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo