FBI: Fake “Account Locked” Alerts Steal Intimate Media

Malwarebytes · Medium sophistication
Last updated August 11, 2026

The FBI warned that criminals are breaking into personal and social media accounts to steal and share intimate images and videos without consent. The campaign uses social engineering like fake customer-service texts and phishing “new login” emails to trick victims into handing over verification codes or passwords, enabling account takeover and further harassment or sextortion.

Key findings

  • Attackers are stealing and distributing non-consensual intimate images (NCII) after breaking into personal and social media accounts.
  • A common workflow is to trigger a real password reset and then trick the victim into sharing the verification code via fake “customer service” texts.
  • Phishing emails use lookalike support domains and “new login” warnings to send victims to fake password-change pages that steal credentials.
  • Stolen media may be posted or sold with personal identifiers (name, phone, email, handles), increasing risk of harassment, stalking, and sextortion.

Who’s being targeted

  • Commonly targeted roles: All employees, Executives, Anyone managing social media accounts, Security awareness / IT helpdesk (for user guidance).
  • Affected industries: General public / consumers, Any organization with employees using personal or social media accounts.
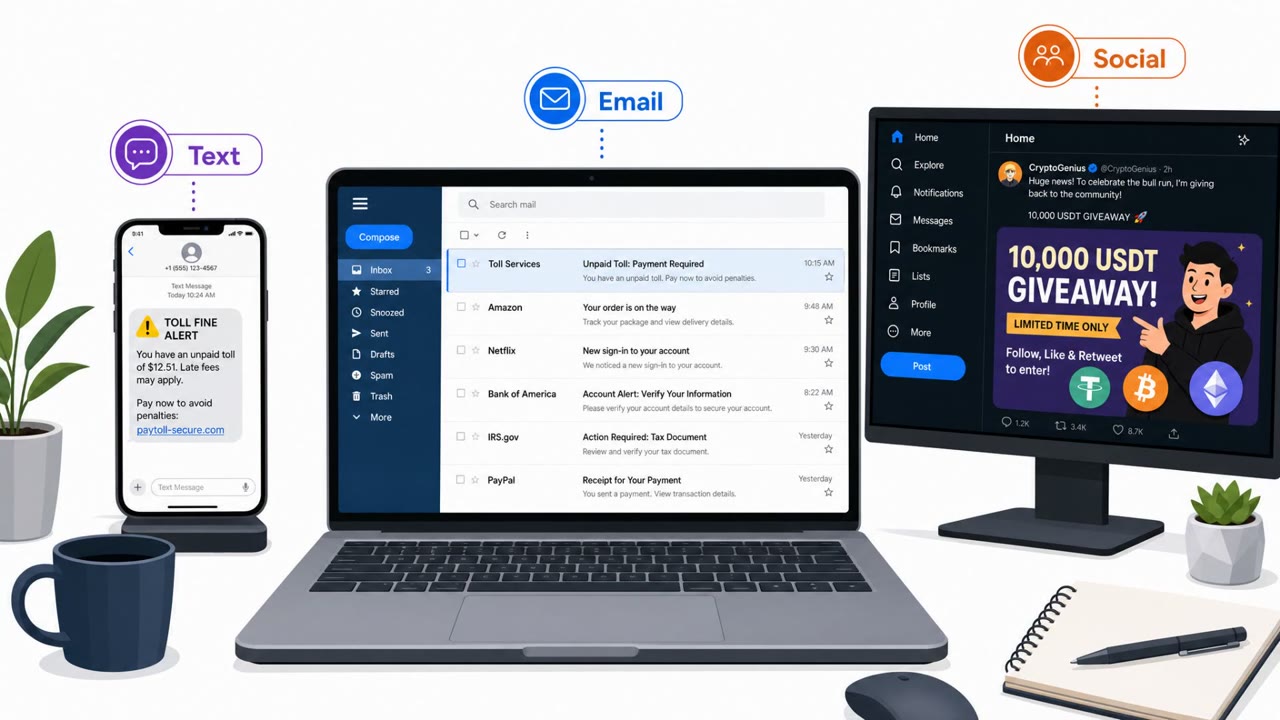
  • Attack channels: sms, email, website.
  • Impersonated: Social media platform customer support, Account/security support team (lookalike support domain).

Awareness takeaways

  • Never share verification codes (even if the request seems tied to a real password reset).
  • Treat unexpected account-warning texts/emails as suspicious and navigate using the official app or a known URL you type yourself.
  • Use unique, long passwords (and avoid predictable PINs based on public personal details) to reduce account-takeover risk.
  • Enable MFA, but don’t approve unexpected prompts or share one-time codes.

Red flags to watch for

  • Unsolicited account-lock warning sent by text
  • Pressure/urgency to act immediately
  • Request to share a verification code (codes should never be shared)
  • Lookalike support domain/email address
  • Link leads to a password change page that isn’t the real service
  • Unexpected “new login” alert prompting immediate action
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

You get a text: “Your social media account will be locked or disabled. Reply with the verification code we just sent.” Here’s the trick: they trigger a real password reset on your account, then pretend to be customer support so you hand over that real verification code. Once they’re in, they can steal and share intimate photos and videos from your personal and social media accounts, tied to your name, phone, and email. Your move: if any text or email asks for a verification code, stop. Don’t share it, open the real app or site yourself and check there.

Similar attacks

How Attackers Bypass MFA in the Real World

How Attackers Bypass MFA in the Real World

The article describes real-world ways attackers get around multifactor authentication (MFA), including “push bombing” (MFA fatigue), phishing pages that relay codes in real time, SIM swapping, and stealing session cookies so MFA isn’t needed again. It also cites known incidents (e.g., Uber 2022 MFA…

July 29, 2026
Fake IT Helpdesk Tricks Users Into Remote Access

Fake IT Helpdesk Tricks Users Into Remote Access

This bulletin describes multiple real-world social engineering campaigns where attackers impersonate IT support or use trusted-looking sharing and “Allow” prompts to gain access. Several campaigns abuse Microsoft Teams and document-sharing lures to trick employees into installing remote tools or…

September 3, 2026
Scammers Shift Lures to Email, Text, and Social

Scammers Shift Lures to Email, Text, and Social

Malwarebytes reports that scammers are increasingly tailoring different scams to the platforms where they work best, like unpaid-toll lures via email/SMS, romance scams via social media, and IRS scams via phone calls. The report highlights heavy brand and celebrity impersonation (including MrBeast)…

September 2, 2026
Quishing Emails Use QR Codes to Bypass Filters

Quishing Emails Use QR Codes to Bypass Filters

The article describes how attackers use QR codes in emails (“quishing”) to hide malicious links, push victims onto less-protected mobile phones, and steal credentials or MFA tokens. It also cites an FBI notice describing North Korea’s Kimsuky using QR codes in spearphishing emails targeting think…

August 18, 2026
Fake IT Calls Steal Microsoft 365 Access

Fake IT Calls Steal Microsoft 365 Access

Microsoft reports a real-world campaign where attackers call or text employees’ personal phones while posing as internal IT. Victims are pushed to “update” passkeys/MFA/SSO and click a link to a fake Microsoft sign-in page, letting attackers get into Microsoft 365 and quietly pull email and files…

September 10, 2026
Passkey Helpdesk Scam Hijacks Microsoft 365

Passkey Helpdesk Scam Hijacks Microsoft 365

Microsoft reports active intrusions where attackers trick employees with “passkey/SSO update” helpdesk pretexts delivered by phone, SMS, or even Microsoft Teams. Victims are sent to lookalike Microsoft sign-in pages or guided through device-code sign-in, letting attackers capture session access and…

September 9, 2026