Attackers took over the verified HBO Max Reddit account and ran over 100 malicious ads that sent people to fake download pages. The pages used a ClickFix-style trick: users were told to copy/paste a command into macOS Terminal (and similar OS-targeted lures) to install information-stealing malware.
How the attack worked
Attackers allegedly gained access to the verified u/hbomax Reddit account and used it to distribute more than 100 malicious ads. The ads impersonated a legitimate HBO Max offer, specifically an app for macOS, even though the streaming service does not actually offer a native Mac client. Anyone who clicked the ad was taken to a landing page such as hbomaxx[.]us that looked convincing enough to include a join or download button.
Clicking that button did not deliver a real app. Instead it produced instructions telling the user to copy and paste a command into Terminal on macOS, a technique known as ClickFix. This method relies on victims doing the actual work of infecting their own machine by running attacker-supplied commands themselves, which can bypass some traditional malware download protections.
Why it succeeded
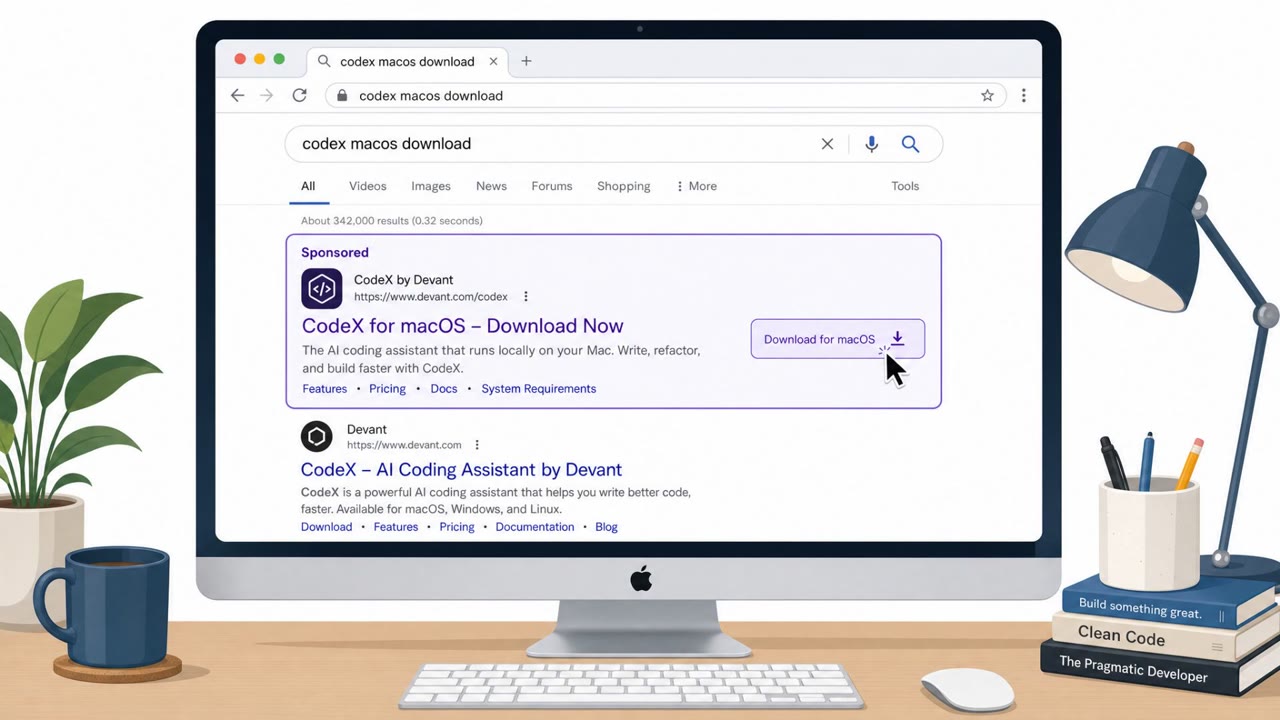
The use of a verified, trusted Reddit account gave the ads an air of legitimacy that a random or new account would not have. Combined with a landing page designed to look somewhat legitimate, and a lure for a product people might plausibly want, the campaign exploited both platform trust and the appeal of a well-known brand. Researchers connected this HBO Max lure to a wider operation called PasteSwitch, which ran for about 48 hours and used other themes as well, including an OpenAI Codex branded landing page.
What to watch for
- Ads or posts from otherwise trusted or verified accounts promoting software downloads
- Landing pages with domains that are close to, but not exactly, the real vendor's domain
- Any prompt asking a user to copy and paste a command into Terminal or a similar system tool to "install" or "fix" something
- Offers for products that do not actually exist, such as a native macOS app for a service that has never provided one
The PasteSwitch operation delivered different payloads depending on the victim's operating system, including infostealers, malware loaders, cryptocurrency clippers, and fake cryptocurrency wallet applications.
How to build resistance
- Treat ads and posts from verified or trusted accounts as still requiring verification before acting on them
- Only download software through official vendor sites or approved company channels, never through ad clicks
- Train staff to never copy and paste Terminal or PowerShell commands from a website, and to escalate such prompts to IT or security instead
- Reinforce awareness of lookalike domains and landing pages that appear almost legitimate but contain small spelling or naming differences
Key findings
- Verified u/hbomax Reddit account was allegedly compromised and used to post/serve malicious ads.
- Ads impersonated legitimate software offers (e.g., “HBO Max for macOS”) even though no native Mac client exists.
- Clicking ads led to landing pages that looked legitimate and prompted users to download/join.
- ClickFix workflow instructed users to copy/paste a command into macOS Terminal, a common method to trick users into self-installing malware.
- Researchers linked this to a broader 48-hour ‘PasteSwitch’ malvertising operation using multiple lures (HBO Max, OpenAI Codex, disk utilities, developer tools).
- Campaign delivered OS-targeted payloads including infostealers, loaders, crypto clippers, and fake wallet apps.
Who’s being targeted
- Commonly targeted roles: All employees (Windows/macOS users), Executives, IT helpdesk, Developers/Engineering, Finance (due to infostealer risk).
- Affected industries: Media & streaming, Social media platforms, Software & developer tools users, General consumers (Windows and macOS).
- Attack channels: website.
- Impersonated: HBO Max (verified Reddit account), OpenAI Codex.
Red flags to watch for
- Promotes a product that doesn’t exist (HBO Max native Mac app)
- Instructions to copy/paste commands into Terminal to install software
- Lookalike domains (e.g., hbomaxx)
- Unexpected ads for developer tools from non-official domains
- Domain does not match vendor’s real website
- Software install prompts that bypass standard app stores/package managers
Frequently asked questions
What happened with the HBO Max Reddit account?
The verified u/hbomax Reddit account was allegedly compromised and used to push more than 100 malicious ads serving ClickFix attacks targeting both Windows and macOS devices with information stealing malware.
What is the ClickFix technique used in this attack?
Victims who clicked the ads were taken to a landing page with a join or download button, and clicking that button produced instructions telling them to copy and paste a command into Terminal on macOS to install malware disguised as an app.
Was this limited to HBO Max branding?
No, researchers linked it to a broader campaign called PasteSwitch that used multiple lures including an OpenAI Codex theme, disk utilities, and developer tools, delivering OS-targeted payloads over roughly 48 hours.
What kind of malware did victims risk installing?
The payloads include infostealers, malware loaders, cryptocurrency clippers, and fake cryptocurrency wallet applications.
Read the video transcript
Imagine this: you’re on Reddit, you see an ad from the verified u/hbomax account for “HBO Max for macOS.” Looks totally legit, right? But in this real attack, someone hijacked that verified account and pushed over 100 fake ads. Click one, you land on hbomaxx.us, hit Join, and it tells you: copy‑paste this command into macOS Terminal to install. That’s a ClickFix, part of a PasteSwitch campaign also spoofing things like OpenAI Codex on codex-craft.com. The whole point is to get you to install infostealers and fake wallet apps yourself. Here’s the move: if any site tells you to copy and paste a Terminal or PowerShell command to install or fix something, stop, close it, and report it to IT or Security.