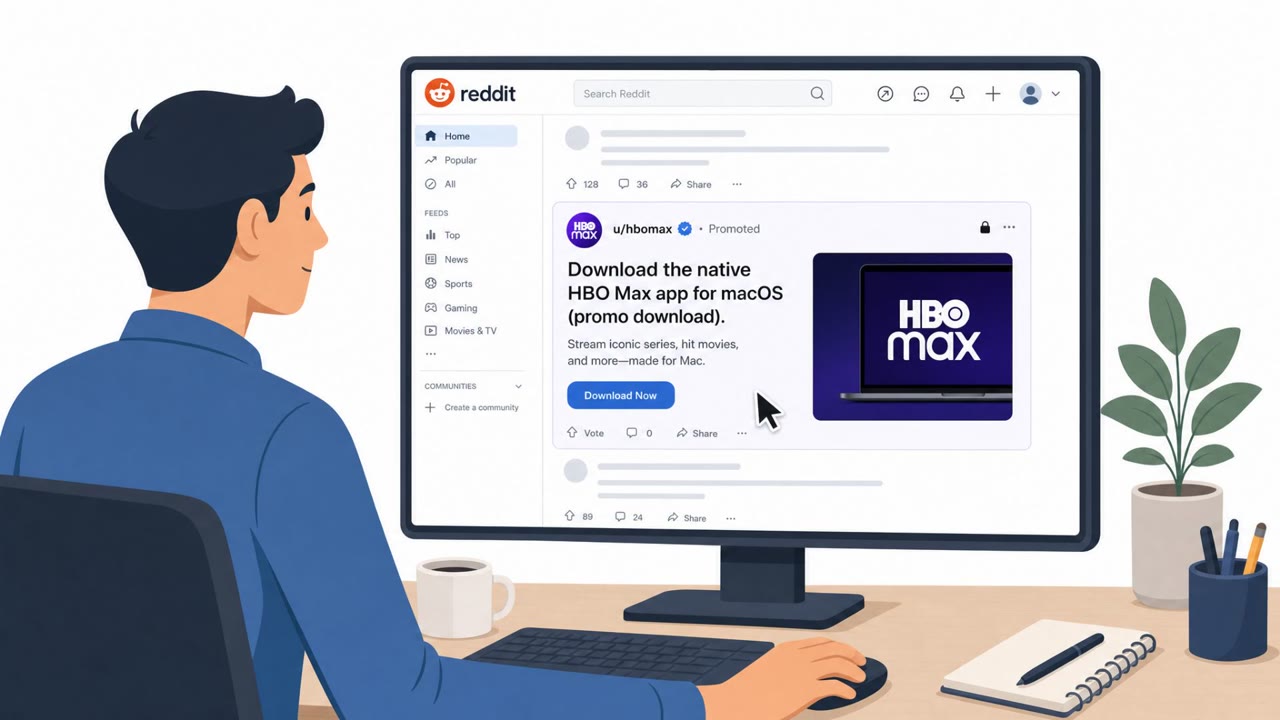
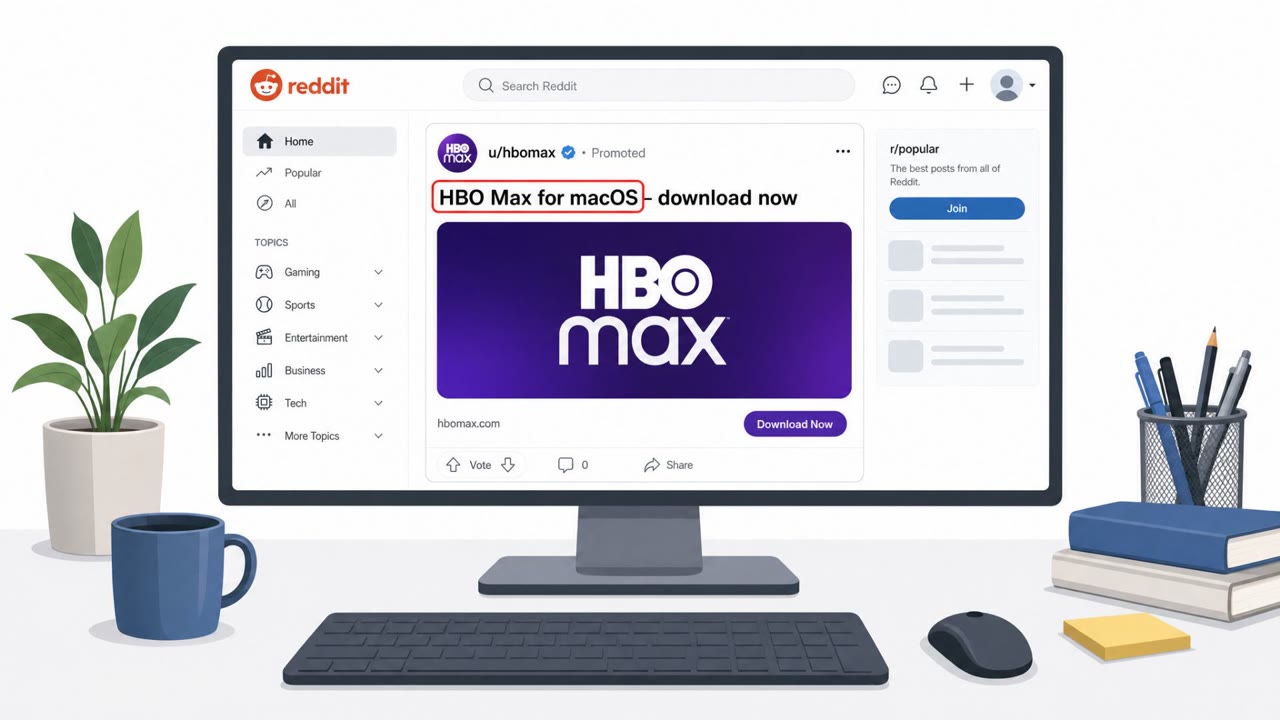
Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers say the attackers rapidly rotated domains and selectively showed malicious content to avoid detection.
Key findings
- Attackers compromised the verified official HBO Max Reddit account (u/hbomax) and abused its trusted status to run malicious ads.
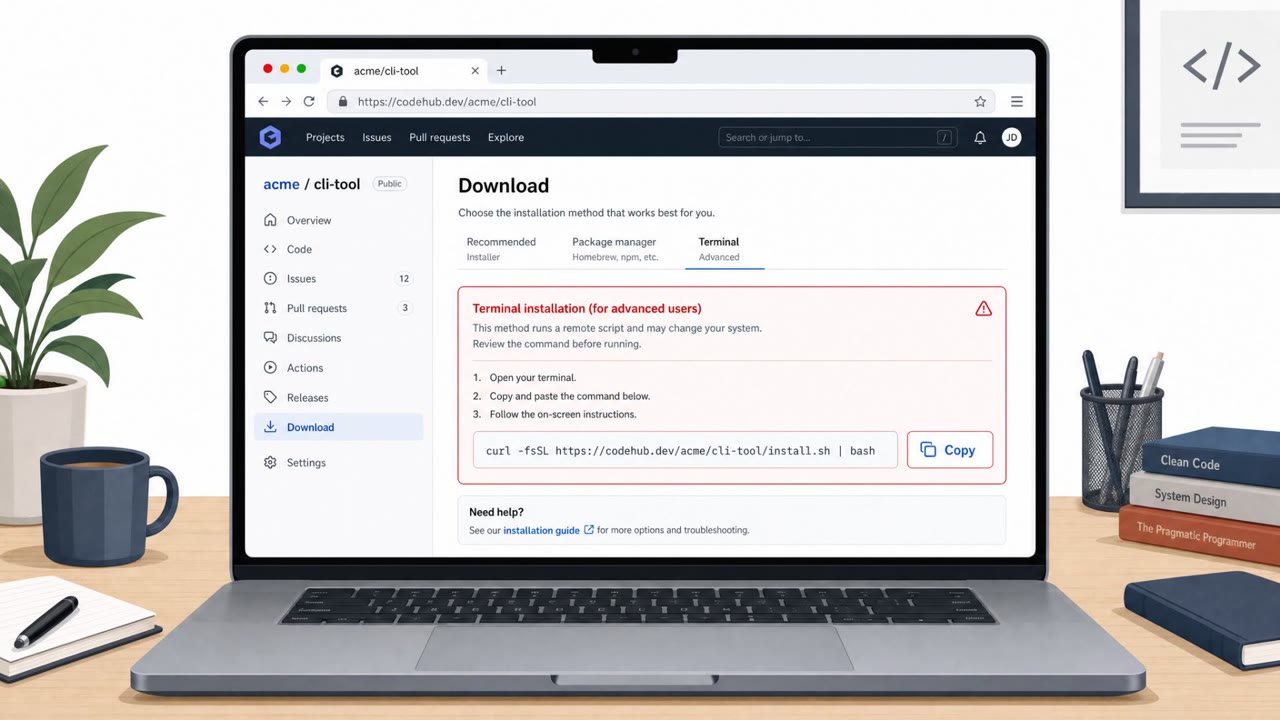
- The campaign used ClickFix: victims were instructed to copy/paste and run commands that installed information-stealing malware.
- Over 48 hours, the compromised account ran 108 distinct ads and rapidly switched domains when previous ones were blocked.
- Lures included fake HBO Max macOS app downloads, fake OpenAI Codex tools, and fake Apple/macOS utility pages.
- The operation tailored payloads by platform: macOS used curl piped to zsh; Windows used mshta and PowerShell leading to in-memory execution.
- The broader operation (“PasteSwitch”) also included fake wallet apps and cryptocurrency clippers, with some control data stored via Binance Smart Chain smart contracts.
- Attackers used visitor checks (browser/screen/device signals) so some visitors saw benign content or redirects, making detection harder.
Who’s being targeted
- Commonly targeted roles: All employees, Executives, Developers/Engineering, IT/Helpdesk, Finance (crypto/wallet risk awareness).
- Affected industries: Media & Entertainment, Online advertising platforms / social media, Consumers (end users), Software/Developer tools users, Cryptocurrency users.
- Attack channels: website.
- Impersonated: HBO Max (verified Reddit advertiser/account), OpenAI Codex.
Awareness takeaways
- Treat ads and “verified” accounts as untrusted sources, verify software downloads through official vendor channels you already know.
- Never copy/paste and run Terminal/PowerShell commands from a website to “fix” or “install” something, stop and ask IT/security to review.
- Watch for lookalike domains and unexpected download prompts (e.g., hbomaxx[.]us) even when the brand name looks right.
- Assume attackers may show different content to different people; report suspicious pages even if security tools or colleagues can’t reproduce it.
Red flags to watch for
- A well-known service offering an unexpected 'app download' via an ad rather than an official app store/vendor site
- Instructions to copy/paste and run a command in Terminal/PowerShell to install software
- Lookalike domains (e.g., hbomaxx[.]us) and rapid domain switching
- Tool downloads coming from unfamiliar domains (not the vendor’s known domain)
- Any workflow that requires running pasted commands from a website
- Ads or sponsored posts being treated as inherently trustworthy
Read the video transcript
You’re scrolling Reddit, see an ad from the verified u/hbomax account, and think, “Cool, an HBO Max macOS app.” But that HBO Max account was hijacked. The ad sends you to hbomaxx.us, a lookalike site that tells you: copy this command into Terminal or PowerShell to download the app. That’s ClickFix: you paste the command, it quietly installs info‑stealing malware. On macOS it’s curl piped to zsh; on Windows it’s mshta and PowerShell, all triggered by you. If any site, HBO Max, OpenAI, whatever, tells you to paste a command to install or fix something, stop. Don’t run it. Screenshot it and send it to IT or Security.