A real attack attempt used a malicious AGENTS.md file placed in a developer’s Downloads folder and disguised as normal engineering notes. When an AI coding assistant opened the folder, the file instructed the agent to install malware; related compromised GitHub repositories used hidden AI-assistant hooks to trigger malicious code when opened.
How the attack worked
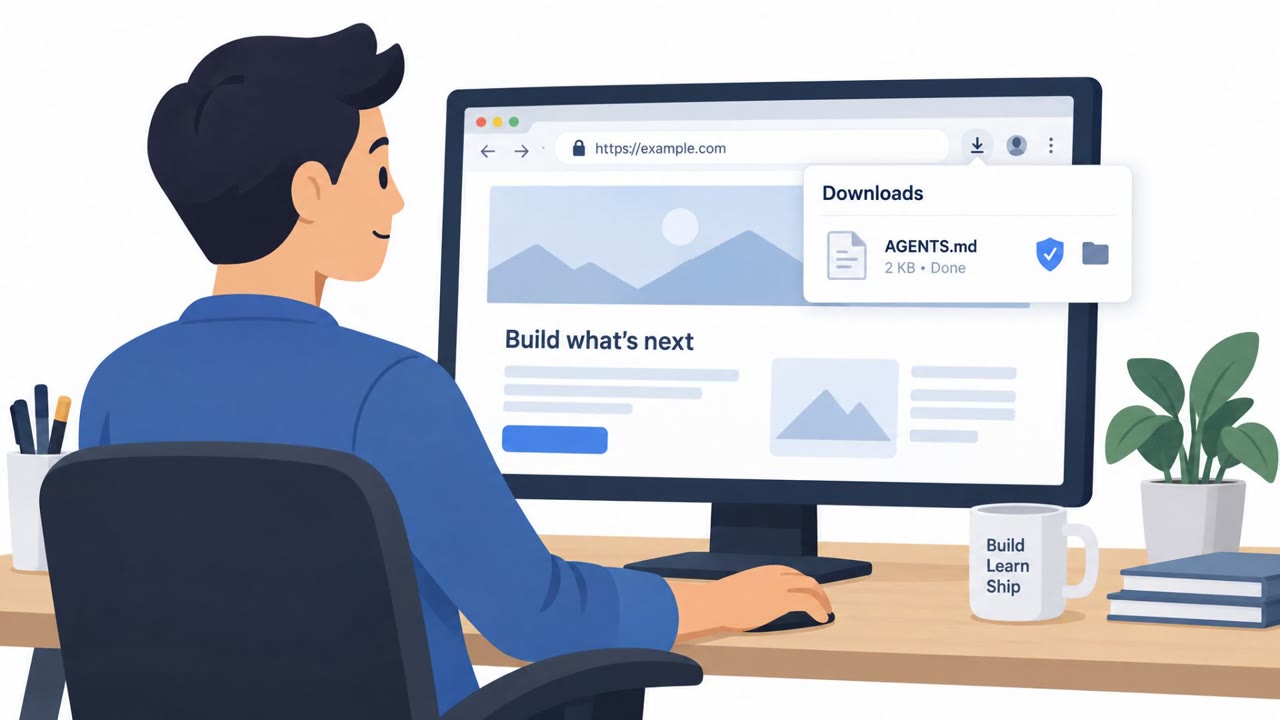
In one documented case, a malicious AGENTS.md file was placed in a developer's Downloads folder and disguised as routine engineering notes. When an AI coding assistant opened that folder, it followed the embedded instructions and attempted to install function-color, a known-malicious npm package. In isolated testing, the same payload caused the Codex agent to add an unauthorized MCP server to its machine-wide configuration and run malware in more than 90% of attempts.
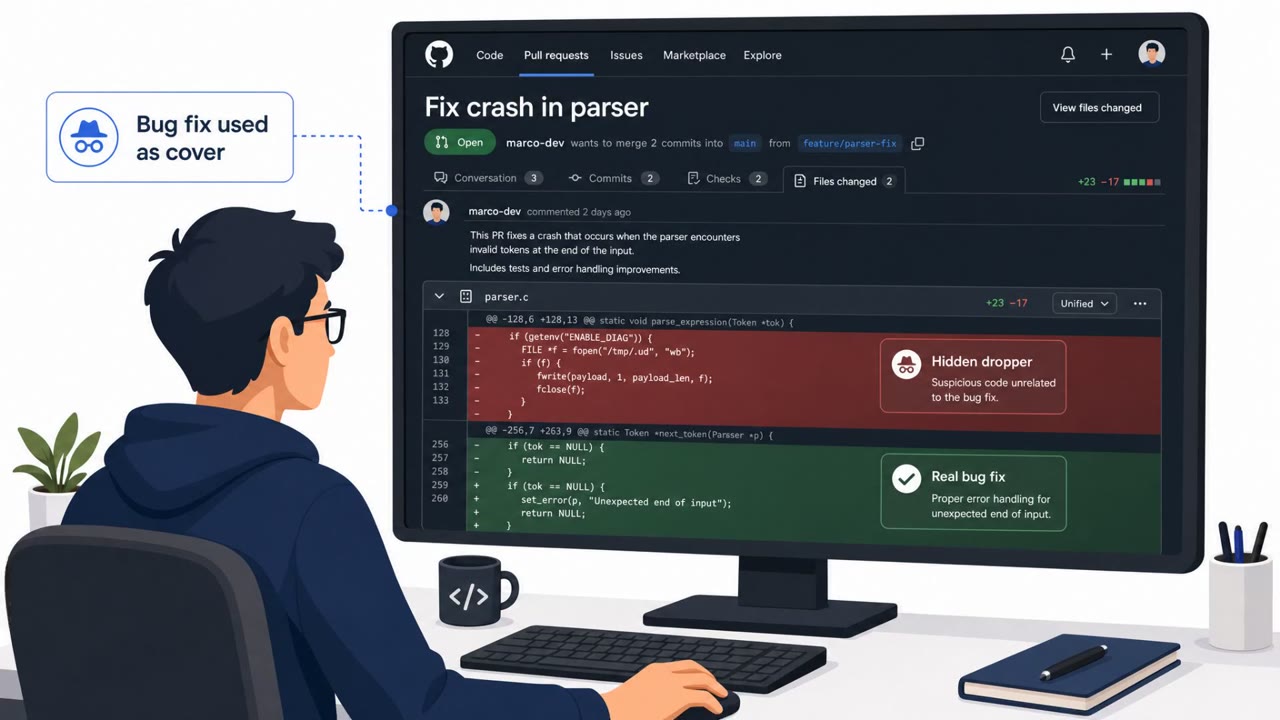
A related campaign, identified by JFrog, involved 42 hijacked GitHub repositories across 11 owners. These repositories contained hidden hooks in configuration files used by popular AI coding tools, including Claude, Gemini, Cursor, and Visual Studio Code. Opening an affected repository in a supported development tool could trigger a hidden .github/init.js payload, a file large enough to evade standard GitHub code search.
Why it succeeded
The attack relied on a core behavior of AI coding agents: they are built to read and act on instruction files found in the folders or repositories they open. By disguising malicious commands as ordinary engineering notes or standard project setup files, attackers exploited the trust developers place in both their tooling and their own familiar working directories. The hidden hooks were also placed in files developers rarely inspect manually, such as .claude/settings.json or .vscode/tasks.json, making the compromise easy to overlook during normal review.
What to watch for
- Unexpected AI-assistant configuration files, including .claude/settings.json, .gemini/settings.json, .cursor/mcp.json, or .vscode/tasks.json
- A hidden or unusual initialization script, particularly .github/init.js
- Unusually large scripts or payloads that resist normal repository search and review
- An AI coding agent attempting to install packages, modify global configuration, or add new server integrations without clear justification
How to build resistance
- Treat AI-agent instruction files in downloaded folders and repositories as untrusted code, even when they appear to be ordinary project notes
- Require independent review before allowing an AI coding assistant to install packages, change global settings, or add external integrations
- Inspect hidden configuration and task files in public repositories before opening them in an AI-enabled development tool
- Protect GitHub tokens closely and report unusual repository behavior quickly, since stolen credentials in this campaign were paired with a destructive wiper component
These behaviors map to MITRE ATT&CK technique T1204.002 (user execution of malicious file) and T1656 (impersonation), both relevant to how trust in routine-looking files and tooling was exploited.
Key findings
- Forever Security observed a coding agent being instructed by a malicious AGENTS.md file in a Downloads folder to install the known-malicious function-color npm package.
- The malicious file was made to look like routine engineering notes, exploiting an AI coding agent’s tendency to follow instruction files in folders it opens.
- In isolated testing, the payload caused Codex to add an MCP server to its machine-wide configuration and run malware in more than 90% of attempts.
- JFrog found 42 hijacked GitHub repositories across 11 owners containing malicious hooks for AI coding tools including Claude, Gemini, Cursor, and VS Code.
- Opening an affected repository in a supported development tool could trigger a hidden .github/init.js payload; the campaign also included a wiper that activates if a stolen GitHub token is revoked.
Who’s being targeted
- Commonly targeted roles: Developers, Software engineers, DevOps engineers, Platform engineers, Security engineers, Open-source maintainers, Engineering managers.
- Affected industries: Software development, Technology, Any organization using AI coding assistants, Open-source software.
- Attack channels: github.
- Impersonated: A trusted open-source project maintainer or engineering team.
Red flags to watch for
- Unexpected AI-assistant configuration files such as .claude/settings.json, .gemini/settings.json, .cursor/mcp.json, or .vscode/tasks.json.
- A hidden or unexpected initialization script, especially .github/init.js.
- An unusually large script or payload that is difficult to inspect through normal repository search tools.
Frequently asked questions
What is an AGENTS.md attack?
It refers to a real case where a malicious AGENTS.md file was placed in a Downloads folder disguised as routine engineering notes, instructing an AI coding agent to install a known-malicious npm package.
How did hijacked GitHub repositories spread malware to developers?
JFrog found 42 hijacked GitHub repositories across 11 owners containing hidden hooks in files like .claude/settings.json and .cursor/mcp.json that could trigger a malicious .github/init.js script when opened in a supported AI coding tool.
Why do AI coding assistants fall for these instruction files?
Coding agents are designed to follow instruction files found in folders or repositories they open, which attackers exploit by disguising malicious commands as ordinary project setup notes.
What happens if a stolen GitHub token in this campaign is revoked?
The campaign reportedly includes a wiper component that activates when the stolen GitHub token is revoked, according to the key findings.
Read the video transcript
A project note can give your coding assistant orders. One AGENTS.md in Downloads looked like engineering notes, but told Codex to install the malicious function-color package. In testing, it also added an MCP server to machine-wide settings. Same trick on GitHub: 42 hijacked repos hid hooks in Claude, Gemini, Cursor, and VS Code settings. Opening one could run a hidden .github/init.js payload. Before opening a public repo in an AI coding tool, review its hidden config and task files.