Recent Defense Sector Cyber Attacks

Page 3 of 3
Laundry Bear Uses Zero-Click Zimbra Email Trap

Laundry Bear Uses Zero-Click Zimbra Email Trap

A newly identified Russia-linked threat actor (“Laundry Bear”) is targeting Western organisations with a zero-click technique that can compromise Zimbra webmail simply by viewing a malicious email. The campaign has reportedly stolen sensitive data across multiple sectors and may evolve to target…

July 24, 2026
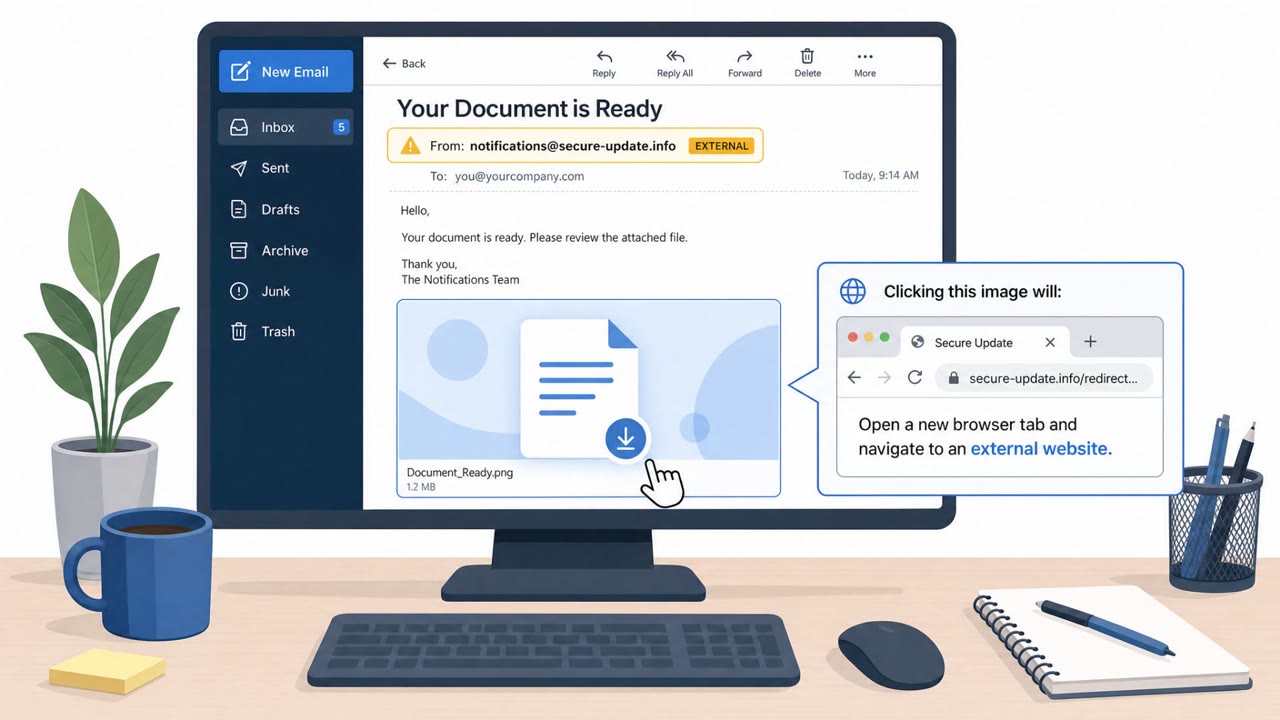
Phishing Email Pushes Fake Notepad++ Plugin

Phishing Email Pushes Fake Notepad++ Plugin

CERT-UA reported a real phishing campaign where victims receive an email with an image attachment that leads (via a shortened link) to a ZIP download. The ZIP contains a script disguised as a PDF, which installs a malicious Notepad++ plugin and sets up an automated task that repeatedly runs malware…

July 24, 2026
TA488 “Half-Click” Emails Hack Zimbra Webmail

TA488 “Half-Click” Emails Hack Zimbra Webmail

A Russian-aligned group (TA488) used malicious emails to exploit a Zimbra webmail flaw so that simply opening or previewing a message triggered compromise, no link click or attachment required. The attackers then stole email data and set up persistent access to compromised mail servers, including…

July 23, 2026
Zero-Click Emails Hit Zimbra Users in Espionage Push

Zero-Click Emails Hit Zimbra Users in Espionage Push

Government agencies and security firms warn that Russia-aligned hackers are using “zero-click” phishing emails to compromise organizations using Zimbra webmail. The attack hides a malicious JavaScript payload inside an email so it runs when the message is opened, aiming to steal recent email,…

July 23, 2026
Zimbra Email View Triggers Russian Data Theft

Zimbra Email View Triggers Russian Data Theft

Government agencies say a Russian-linked group sent specially crafted HTML emails that exploit a Zimbra webmail flaw, so simply viewing the message can trigger data theft, no click required. The campaign has targeted multiple Western sectors since July 2025 and focuses on stealing email content and…

July 23, 2026
Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Researchers at Unit 42 reported a real espionage campaign targeting organizations using Zimbra webmail, including government, defense, transportation and financial sectors. The attackers sent “zero-click” phishing emails disguised as news headlines, where opening/viewing the message could trigger a…

July 23, 2026
Fake Defense Summit Invites Hit Dutch Police

Fake Defense Summit Invites Hit Dutch Police

A Russian-linked group allegedly stole sensitive contact data from the Netherlands National Police after getting access to an employee’s email account. The podcast describes a realistic spearphishing lure: an email invitation to a “European Defence Summit” that includes a link or a QR code in a PDF…

July 23, 2026
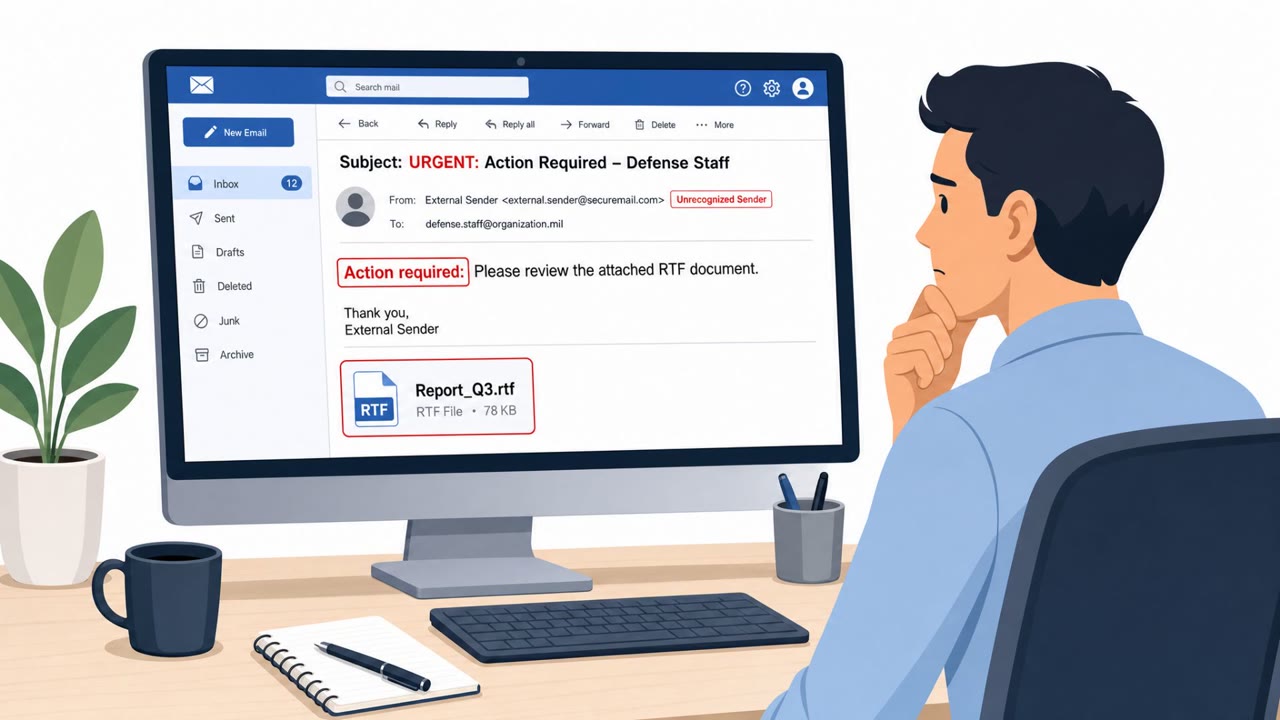
Spear-Phishing RTF Hits Bangladesh Defense Targets

Spear-Phishing RTF Hits Bangladesh Defense Targets

Researchers reported a targeted espionage operation against Bangladesh’s military and defense organizations using spear‑phishing emails with a booby‑trapped RTF document. When opened, the file pulls malicious content remotely and installs an implant that persists on the device while quietly sending…

July 17, 2026
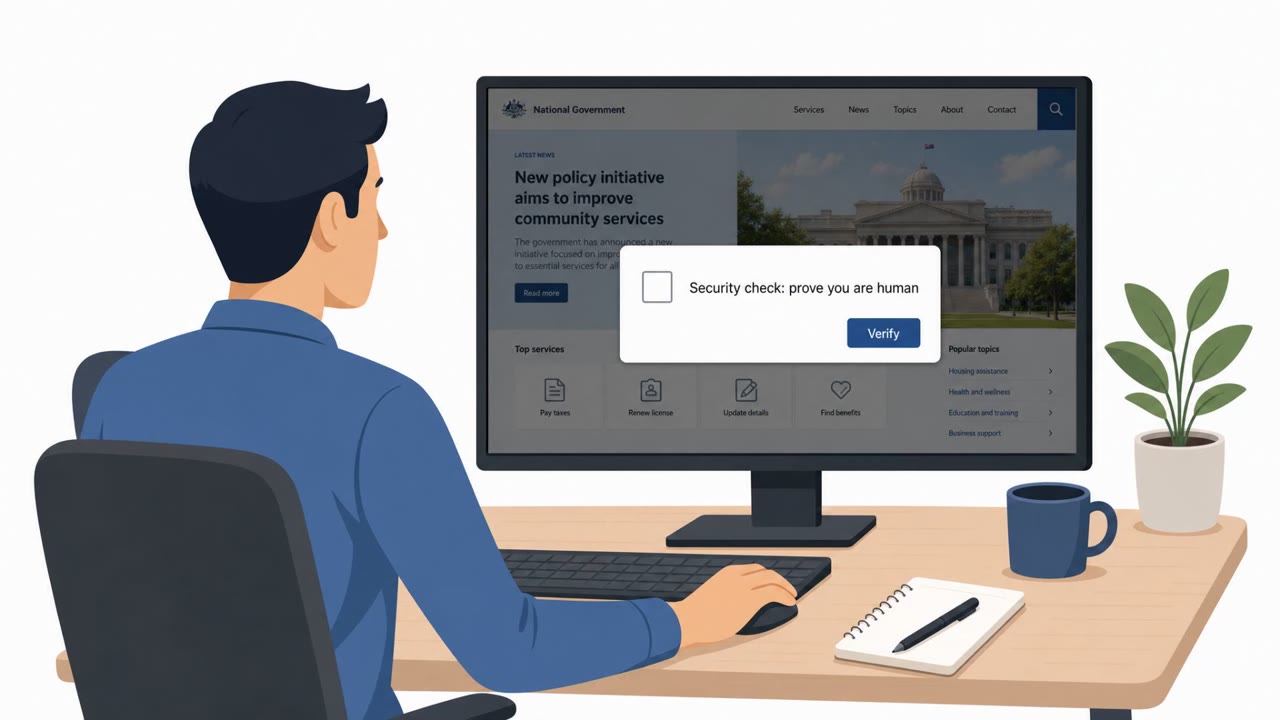
Sandworm Uses Fake CAPTCHAs to Spread Malware

Sandworm Uses Fake CAPTCHAs to Spread Malware

Ukraine’s CERT says the Russia-linked Sandworm group is tricking targets into infecting their own PCs using compromised websites that display fake CAPTCHA checks. Victims are instructed to copy and paste a PowerShell command, which downloads malware and can lead to deeper compromise. CERT also…

July 16, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo