Threat Watcher

Page 6 of 51
ShinyHunters Used Phone Pretexts to Bypass MFA

ShinyHunters Used Phone Pretexts to Bypass MFA

A Register podcast transcript describes real-world activity linked to the ShinyHunters cyber extortion crew, including an FBI-related breach and subsequent arrests. It also notes the group’s reliance on social engineering phone calls where attackers impersonate locked-out contractors or employees…

October 12, 2026
Phishers Hide Prompts to Trick AI Email Summaries

Phishers Hide Prompts to Trick AI Email Summaries

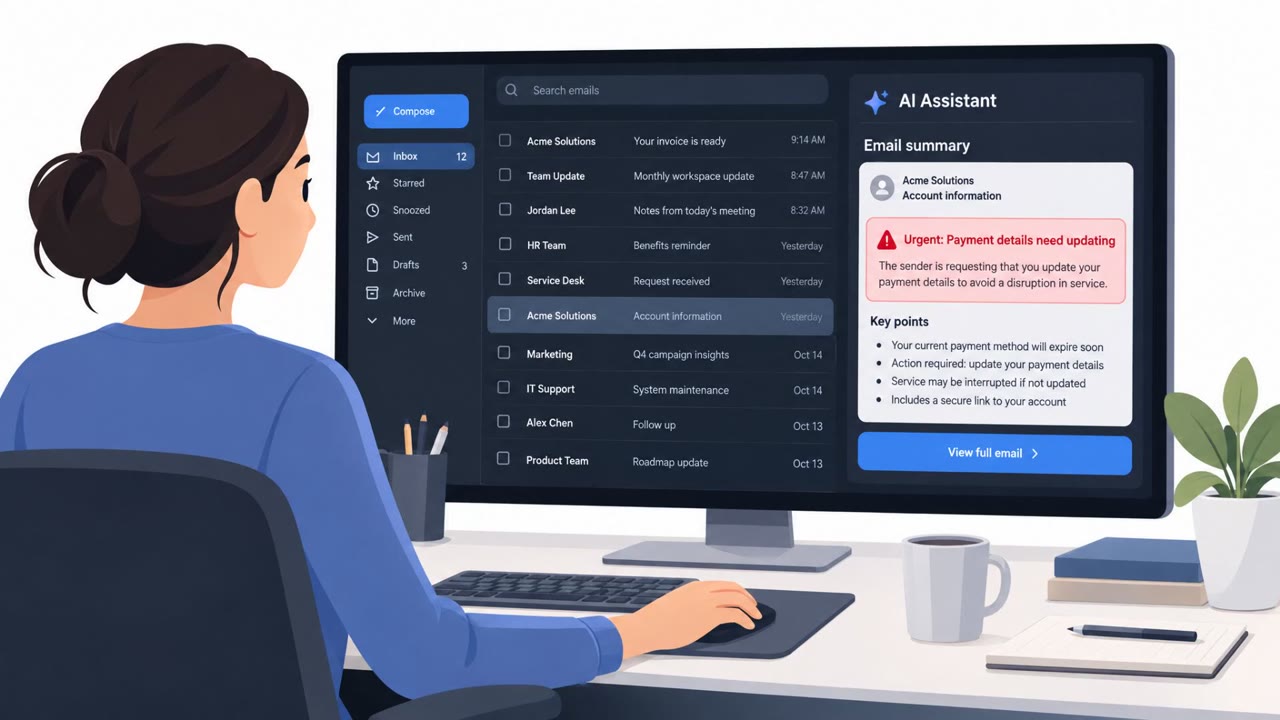
Researchers described phishing emails that contain hidden “prompt injection” instructions aimed at AI assistants that summarize inboxes. The goal is to make the AI present the scam as legitimate or urgent, potentially pushing a user to take risky actions like changing vendor payment details. The…

October 12, 2026
Invoice-Fraud Platform Blasted Pix via Email & SMS

Invoice-Fraud Platform Blasted Pix via Email & SMS

Researchers described two cybercrime operations. While one campaign focused on breaking into websites and infrastructure, a second operation (“Operation Master”) ran an automated invoice-fraud system that sent millions of messages with personalized invoice links designed to trick victims into…

October 12, 2026
China-Linked Hackers Used Fake Web Logins

China-Linked Hackers Used Fake Web Logins

U.S. and international agencies warned that China-linked actors, enabled by a China-based company (Integrity Technology Group), are breaking into organizations including U.S. critical infrastructure. A key technique described is altering legitimate webpages to show fake login prompts that steal…

October 12, 2026
YouTubers Phished via Fake Sponsorship Deals

YouTubers Phished via Fake Sponsorship Deals

Scammers are targeting YouTube creators by posing as brands offering sponsorships and sending personalized emails that reference the creator’s videos. Victims are directed to a convincing fake collaboration platform and then prompted to sign in with Google, putting their accounts at risk.

October 11, 2026
Calendar Invites Used to Steal Logins

Calendar Invites Used to Steal Logins

Attackers are sending calendar invitations that auto-appear in tools like Google Calendar, tricking people into clicking links or calling “support” numbers. The calendar event often mimics voicemails, payment receipts, or auto-renewals and leads to fake login pages (Microsoft/Google/PayPal) or…

October 11, 2026
Silent Ransom Group: $207M via Calls, Not Malware

Silent Ransom Group: $207M via Calls, Not Malware

Silent Ransom Group allegedly extorted law firms by using phone calls and social engineering to trick employees into giving access or uploading sensitive files, without encrypting data. Leaked internal chats suggest 27 law firms paid roughly $207M in a six‑month span, with individual payments…

October 10, 2026
New Unicode Trick Makes Fake URLs Look Real

New Unicode Trick Makes Fake URLs Look Real

Researchers demonstrated how attackers can register lookalike web domains using two specific Unicode characters that Chromium-based browsers may display as trustworthy, normal-looking URLs. This can make phishing and typosquatting sites appear legitimate to employees, increasing the chance they…

October 10, 2026
Fake Dubai Airports Recruiters Target Developers

Fake Dubai Airports Recruiters Target Developers

Researchers linked an Iran-aligned campaign to recruitment-themed social engineering that tricked a targeted Iraqi software engineer into downloading a fake "Dubai Airports" careers portal and then opening a trojanized Visual Studio coding test. The lure abused normal developer workflows so malware…

October 10, 2026
Single Prompt Stole AWS AgentCore Credentials

Single Prompt Stole AWS AgentCore Credentials

Researchers described how an external user with only chat access to an Amazon Bedrock AgentCore agent could prompt it to fetch a cloud credential endpoint and inadvertently reveal temporary AWS credentials. Those credentials could then be used to enumerate other agents, access container images,…

October 9, 2026
ASOS App Push Alert Used for Extortion

ASOS App Push Alert Used for Extortion

Attackers used social engineering to access an ASOS employee account connected to Snowflake, then used ASOS’s own app notification system to broadcast an extortion message directly to customers. The incident also involved suspected large-scale customer data theft, which increases the risk of highly…

October 9, 2026
Asos App Push Used to Broadcast Ransom Demand

Asos App Push Used to Broadcast Ransom Demand

A ransomware crew that compromised retailer Asos used the company’s own mobile app push notifications to send an extortion message directly to customers. The message claimed the attackers had fully compromised Asos’s Snowflake environment and threatened to leak data if the company didn’t engage.…

October 9, 2026
ASOS App Push Alert Used to Extort Customers

ASOS App Push Alert Used to Extort Customers

Attackers abused ASOS’s own mobile app messaging to send customers a threatening push notification claiming ASOS’s Snowflake environment was compromised and demanding engagement to avoid a data leak. ASOS confirmed the notification was unauthorized and warned customers to watch for follow-on…

October 9, 2026
ASOS Breach Began With Tricked Employee Login

ASOS Breach Began With Tricked Employee Login

ASOS confirmed attackers got into customer-data systems after tricking an employee into handing over login credentials. Stolen data reportedly included not only names and contact details, but also customers’ shopping searches, which could enable highly convincing follow-on scams and phishing.…

October 9, 2026
MATCHBOIL Spearphish Tricks Users Into Running Script

MATCHBOIL Spearphish Tricks Users Into Running Script

ESET reports that Russia-aligned group UAC-0099 is using spearphishing emails with malicious links to deliver a downloader called MATCHBOIL. The attack relies on tricking a person into manually running a downloaded VBScript, which then fetches and installs further malware and sets up persistence…

October 9, 2026
Fake Ransomware “Rescue” Firm Allegedly Took Millions

Fake Ransomware “Rescue” Firm Allegedly Took Millions

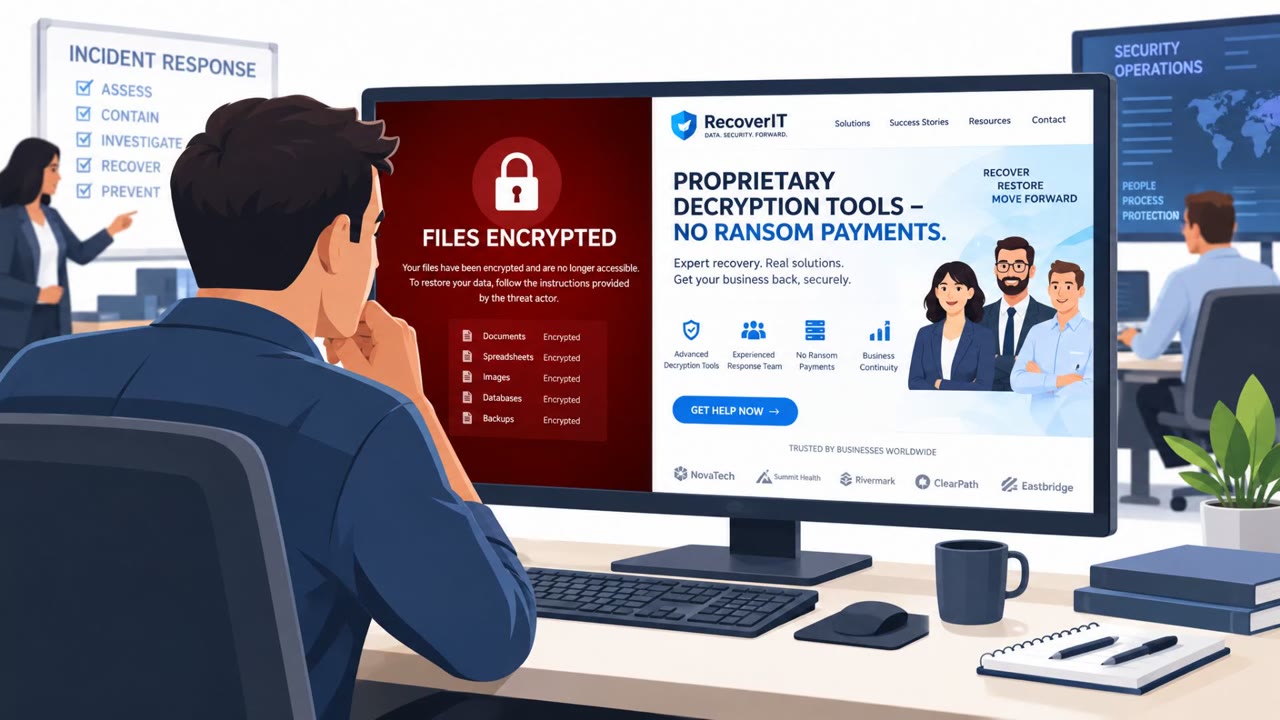
U.S. prosecutors say the owner of MonsterCloud told ransomware victims he could recover data with proprietary tools and avoid paying criminals, but instead allegedly paid the ransom and charged clients far more. The scheme reportedly used a paid “analysis” step where clients shared the ransom note…

October 8, 2026
Power BI Phish Pushes ScreenConnect Downloads

Power BI Phish Pushes ScreenConnect Downloads

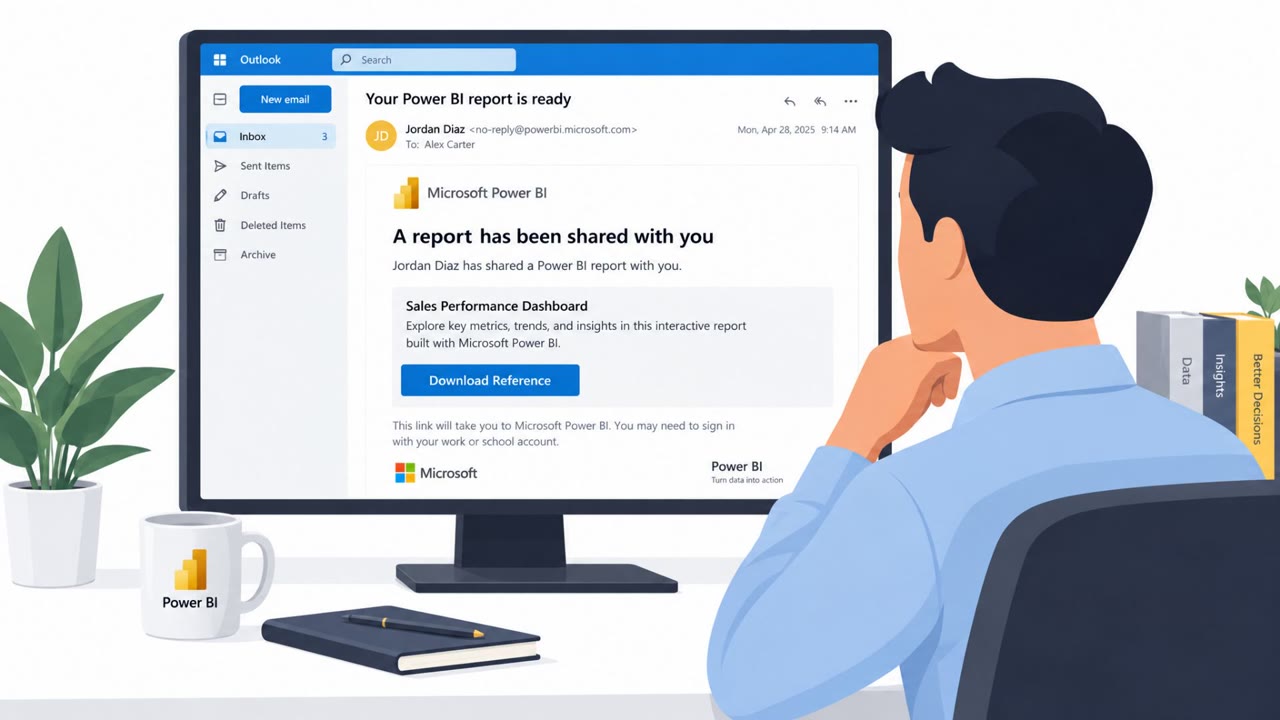
A weekly threat roundup includes multiple real-world social engineering campaigns, including a phishing operation that abuses legitimate Power BI domains to look trustworthy and trick users into downloading a remote-access tool installer. It also describes a WhatsApp-delivered lure that tricks…

October 8, 2026
Fake Police Reply Lures Ukraine Officials

Fake Police Reply Lures Ukraine Officials

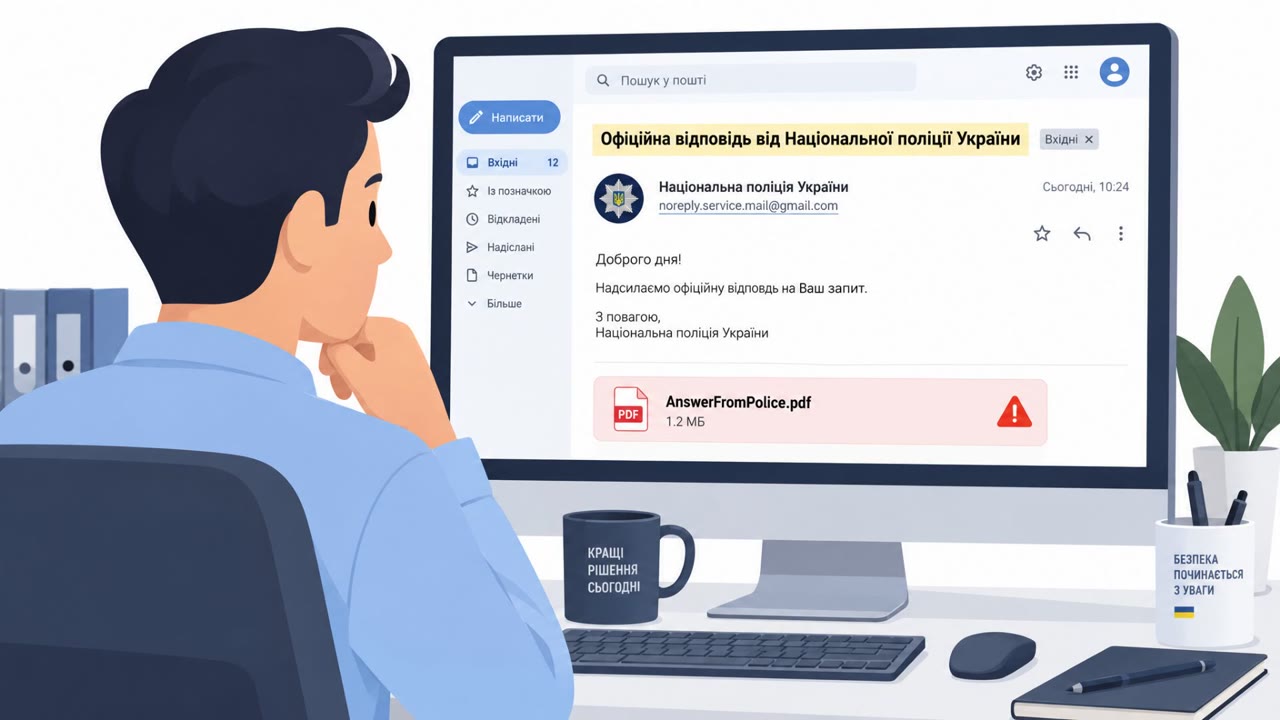
Russia-aligned actor UAC-0099 targeted Ukrainian government personnel using malware (ASHVEIN) that steals credentials and enables remote control. A key lure described is a malicious .NET file that shows a decoy Microsoft Word document pretending to be an official response from Ukraine’s National…

October 8, 2026
Extortion Gang Plots Office Infiltration of Law Firms

Extortion Gang Plots Office Infiltration of Law Firms

Leaked chat logs linked to the Silent Ransom Group describe efforts to pressure U.S. law firms through extortion and, unusually, by sending in-person “agents” to physically enter offices and copy data. The FBI previously warned that people tied to the group were posing as IT staff to gain access,…

October 8, 2026
ASOS Breach: Impersonation Stole Employee Login

ASOS Breach: Impersonation Stole Employee Login

ASOS says an attacker got into an employee account by impersonating a trusted contact to steal login credentials. Those credentials were then used to access third-party platforms and send a legitimate-looking push notification to customers claiming a Snowflake hack and directing them to a Telegram…

October 8, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo