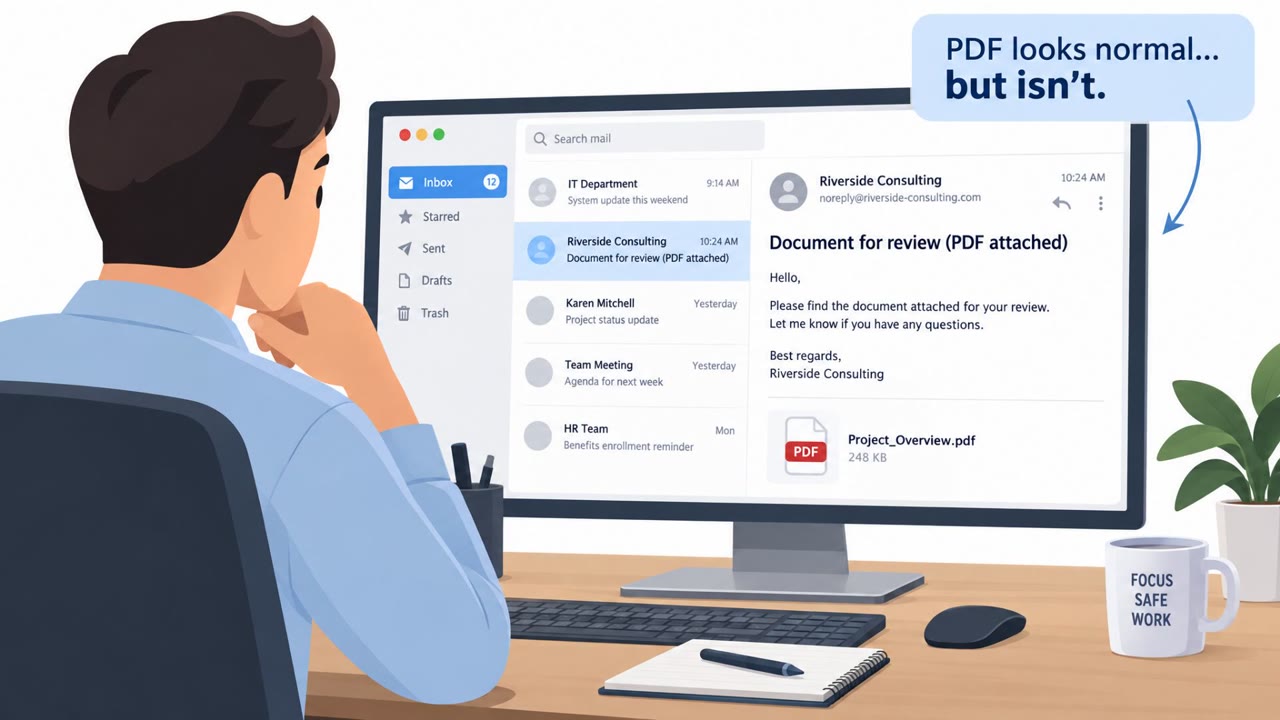
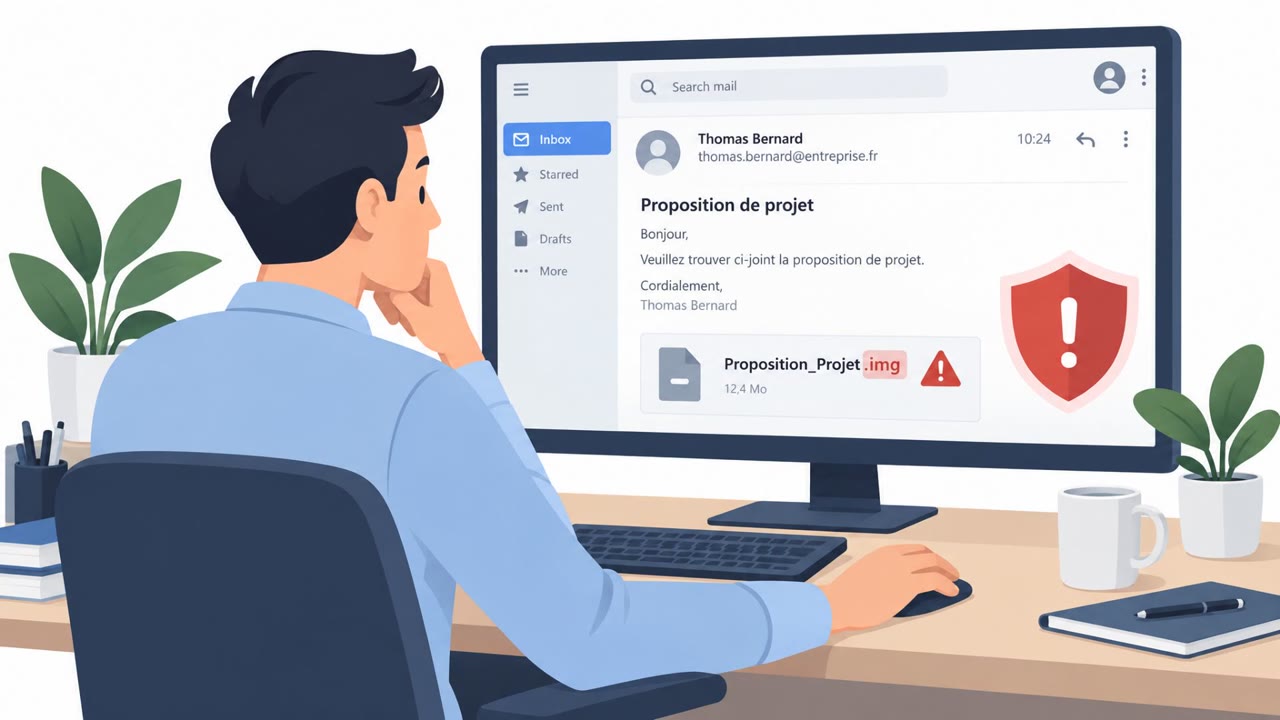
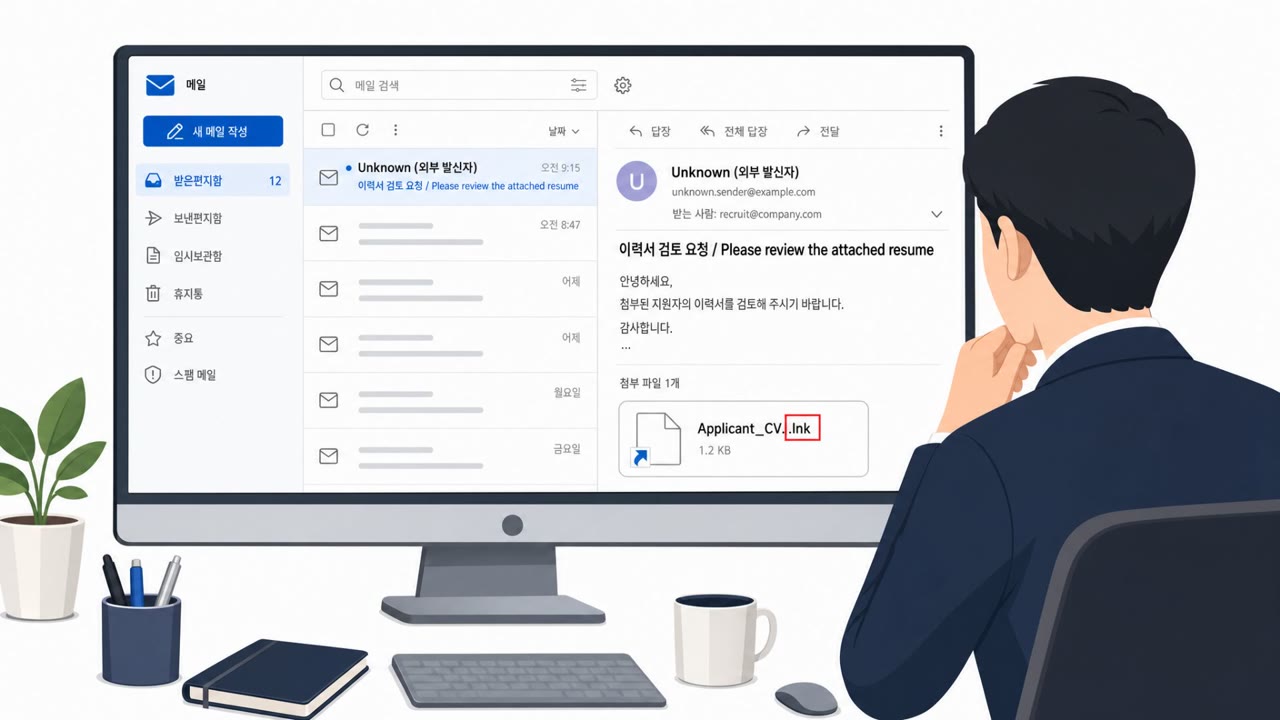
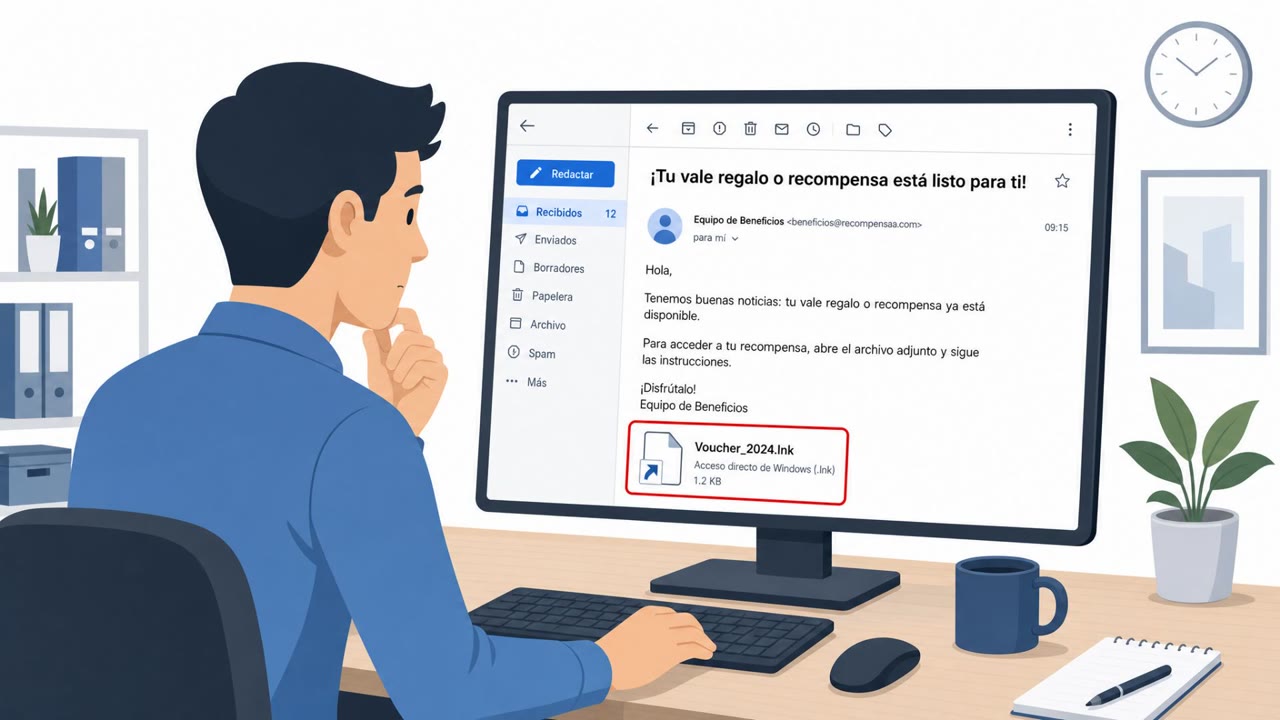
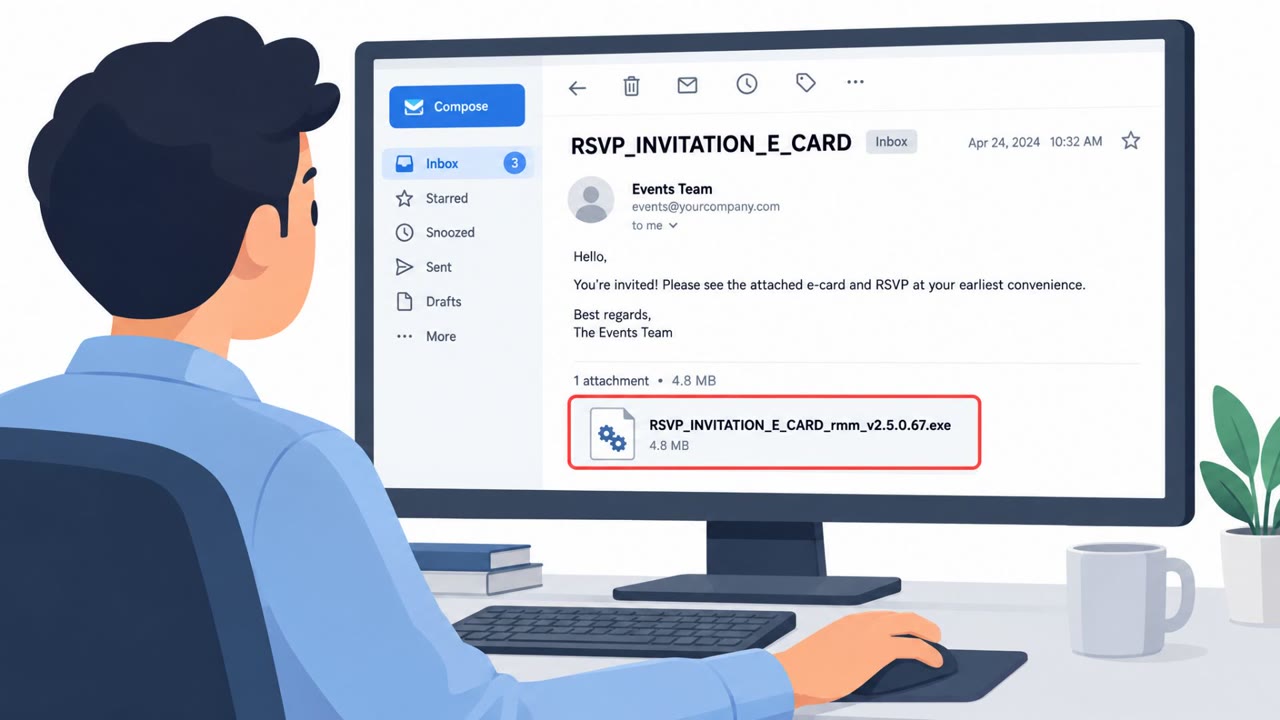
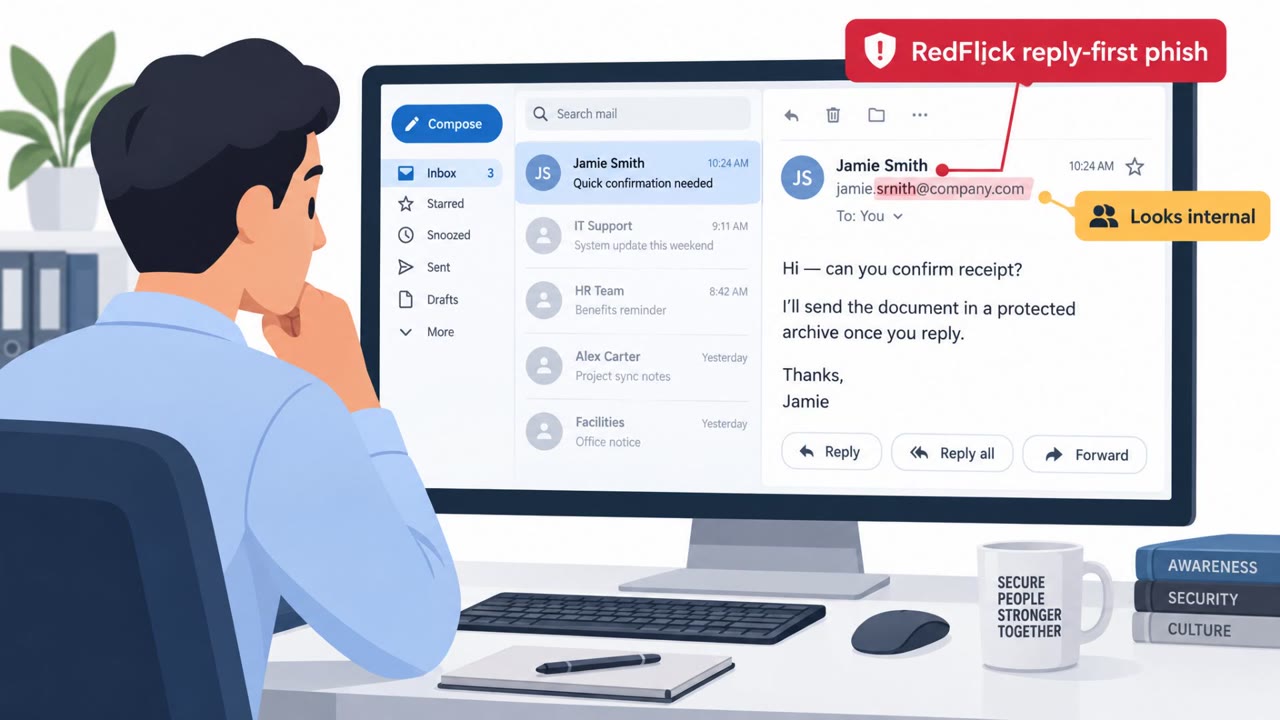
A Rust-based remote access trojan (CikaBika Bot) was delivered using a document-themed lure that included a malicious Windows shortcut (LNK) and a PDF containing an embedded payload. Once installed, it used Discord as its command-and-control channel to run commands, collect information, and steal data. This is a realistic, repeatable phishing-style workflow that can be used for employee training simulations around opening unexpected “document” files.
Key findings
- CikaBika Bot was delivered using a document-themed lure that included a malicious LNK file and a PDF with an embedded payload.
- The malware leveraged Discord for command-and-control (C2), reconnaissance, remote execution, and data exfiltration (using ngrok in observed activity).
- The infection chain included a loader and multiple Windows techniques (e.g., PowerShell UAC bypass and DLL search-order hijacking).
Who’s being targeted
- Commonly targeted roles: All employees, Executive assistants, HR, Finance, Operations.
- Attack channels: email.
- Impersonated: Unknown sender (document delivery / shared document pretext).
Awareness takeaways
- Treat unexpected “document” emails as suspicious, especially if they include shortcut (LNK) files or unusual attachments.
- Remind staff that real business documents should not require running shortcuts or executables; use approved sharing platforms instead.
- Teach teams that attackers can use legitimate services (like Discord) as hidden control channels, so “it looks normal” is not a safety signal.
Red flags to watch for
- Unexpected document delivery, especially from an unknown sender
- Attachment includes an LNK (shortcut) or double-extension style file rather than a normal document
- Pressure to open/run a file instead of using a trusted document-sharing method
Read the video transcript
You get an email: “Here’s the document,” with a PDF… and a weird extra file next to it. That extra file is a Windows shortcut, an LNK. Click it, and a Rust-based remote access trojan called CikaBika Bot silently installs, then phones home over Discord. From there, CikaBika Bot can run commands, snoop around your files, and stream data out through Discord and ngrok, all while just looking like a normal document you opened. If you ever see a “document” email with a shortcut file like .lnk or anything that wants you to run it, don’t open it, forward it to the security team and delete it.