Voucher Lure Drops RAT via FTP Banner Tricks

The Hacker News · High sophistication
Last updated August 25, 2026

Researchers reported a real malware campaign where attackers use Spanish-language “voucher claim” messages to trick people into running a Windows Shortcut file. After the user clicks it, the malware pulls commands from an FTP server’s welcome banner and continues downloading additional payloads, ultimately installing remote-access trojans (E4del and PINHOLE).

Key findings

  • Attackers used Spanish-language voucher-claim lures to get users to run a Windows Shortcut (LNK).
  • The campaign used an unusual technique: putting attacker commands in an FTP server’s welcome banner (a “dead drop resolver”).
  • A multi-stage chain pulled further commands and payloads via FTP banner(s), WebDAV, and PowerShell, ultimately delivering E4del and PINHOLE RATs.
  • One payload was “masquerading as Discord” (a signed Electron app).
  • PINHOLE used “high-reputation platforms like Pinterest and SurveyMonkey as DDRs” and “proxy the communication through Cloudflare Workers.”

Who’s being targeted

  • Commonly targeted roles: All employees, Finance, HR, Operations, IT Helpdesk.
  • Attack channels: email.
  • Impersonated: Voucher or rewards program (unspecified).

Awareness takeaways

  • Treat unexpected “voucher/reward claim” messages as suspicious, especially if they ask you to run an attached file.
  • Never run Windows Shortcut (LNK) attachments from email unless IT/security explicitly verifies them.
  • Be alert to files or installers that pretend to be well-known apps (e.g., Discord) or “updates,” even if they look professional.

Red flags to watch for

  • Unexpected voucher/reward claim message
  • Attachment is a Windows Shortcut (.LNK) rather than a normal document
  • Pressure to click/run a file to redeem a voucher
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

You get an email in Spanish: "Tu vale está listo, abre el archivo para reclamar tu voucher." Looks harmless, right? But that attachment is a Windows Shortcut, a .LNK. Once you run it, it secretly talks to an FTP server and reads commands hidden in the server’s welcome banner, then chains into PowerShell and WebDAV to drop remote‑access trojans like E4del and PINHOLE. Here’s the nasty twist: one payload pretends to be a polished Discord installer, and PINHOLE can even hide its traffic behind high‑reputation sites like Pinterest or SurveyMonkey and route through Cloudflare Workers. To you, it just looks like normal web traffic. Your move: if an email about a voucher or reward includes a .LNK shortcut, don’t open it, forward it to the security team and delete it.

Similar attacks

Larva-24009 Lures Firms With Fake Doc Attachments

Larva-24009 Lures Firms With Fake Doc Attachments

AhnLab reports Larva-24009 has continued phishing campaigns through 2026, sending emails that trick employees into opening fake “document” attachments that are actually shortcut (LNK) files. When opened, the attachment runs hidden PowerShell commands, shows a decoy document, and silently downloads…

August 3, 2026
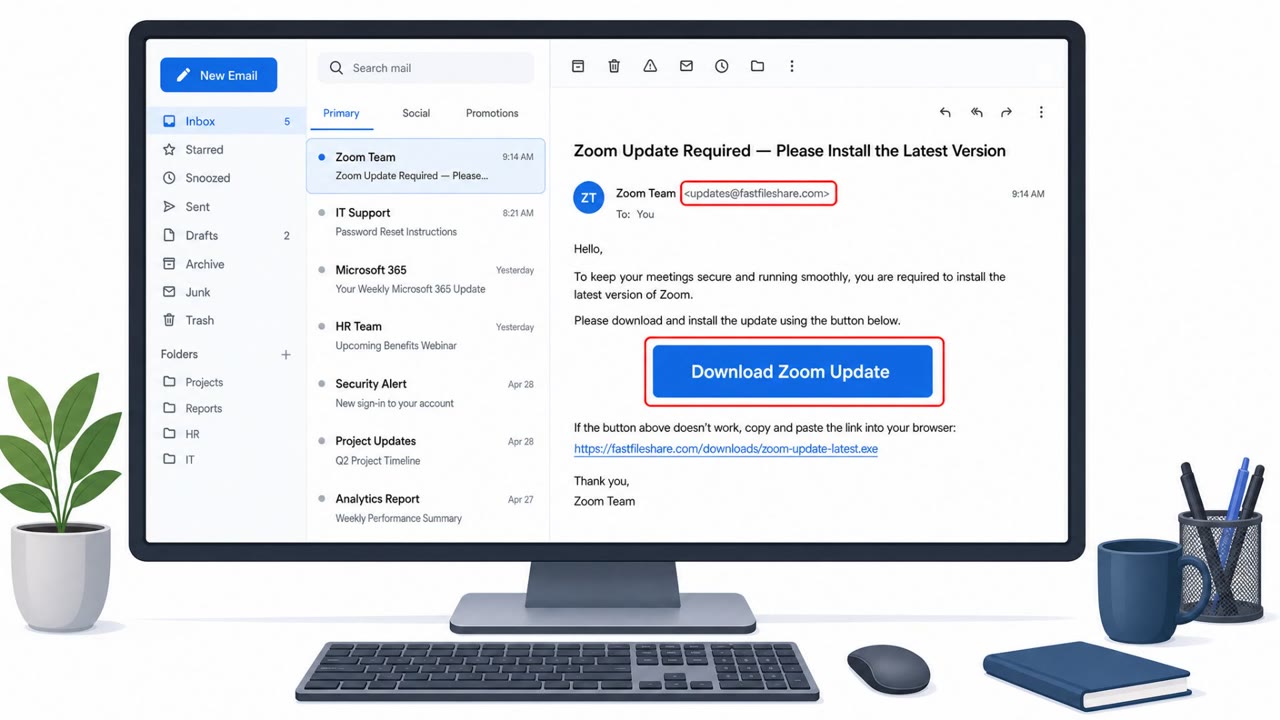
Fake Zoom/Adobe Updates Drop ScreenConnect Backdoor

Fake Zoom/Adobe Updates Drop ScreenConnect Backdoor

Researchers described an active phishing campaign that tricks people with fake Adobe/Zoom update and “document review” themes to install the legitimate ScreenConnect remote-access tool. Once installed, attackers get persistent remote control of the victim’s computer while blending in as normal IT…

August 4, 2026
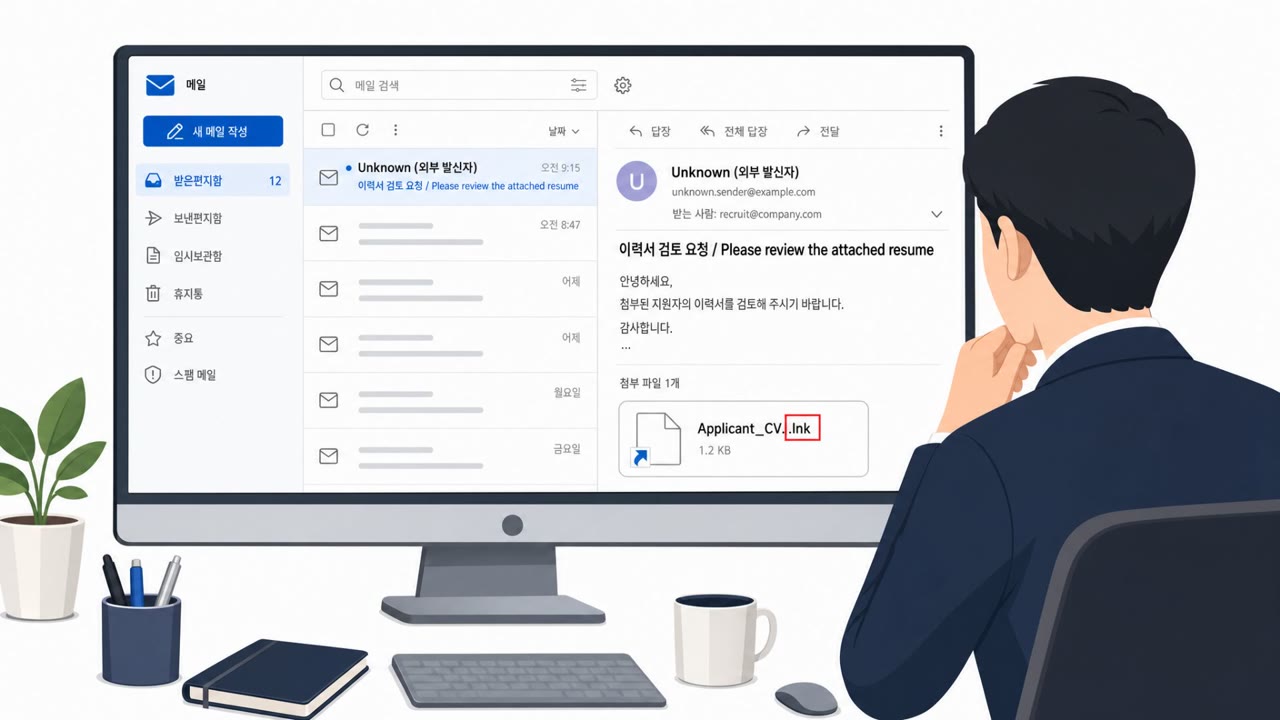
Korea APTs Push LNK “Resume” Spear‑Phish

Korea APTs Push LNK “Resume” Spear‑Phish

AhnLab reports that many APT attacks targeting organizations in South Korea in July 2026 started with spear‑phishing emails that delivered malicious Windows shortcut (LNK) files disguised as legitimate documents (including resumes). When opened, the LNK runs scripts that install…

August 28, 2026
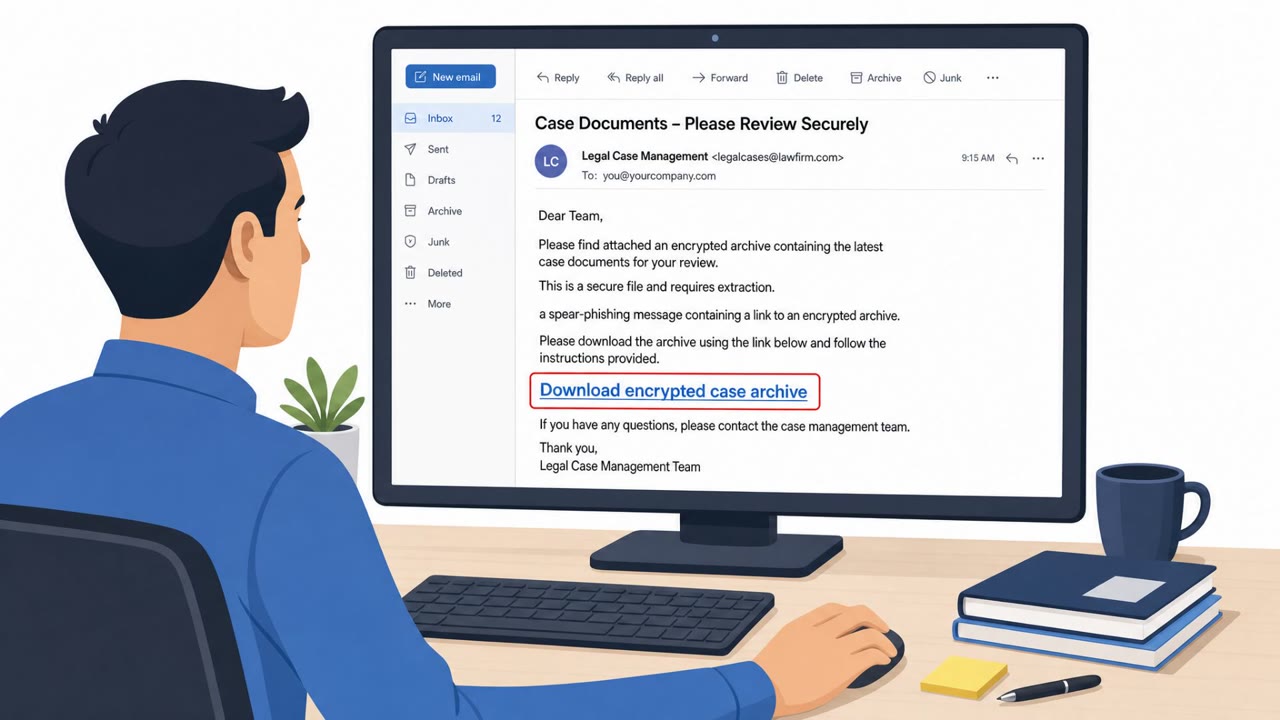
“Case Documents” Lure Hits Law Firm via LNK

“Case Documents” Lure Hits Law Firm via LNK

Researchers reported a real spear‑phishing intrusion against a law firm where attackers sent a message with a link to an encrypted archive. The archive contained a Windows shortcut (LNK) disguised as “Case Documents,” and running it launched a multi‑stage loader (“HollowFrame”) that ultimately…

July 31, 2026
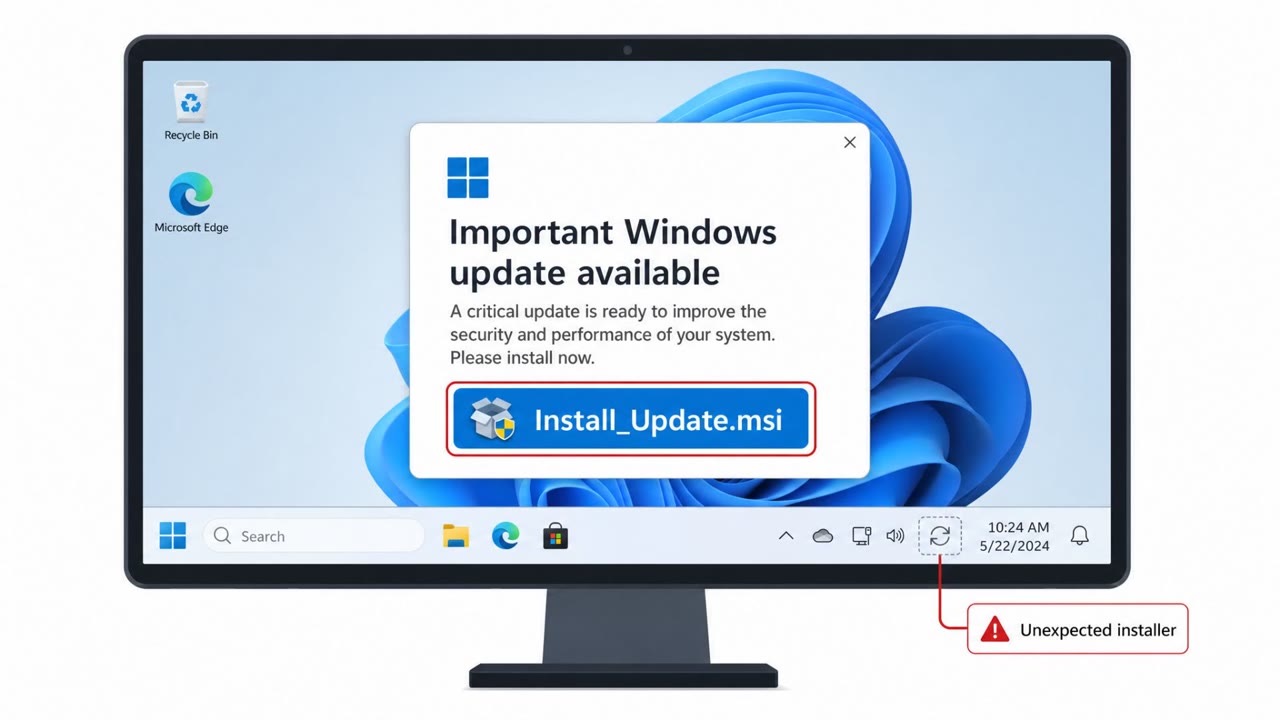
Chaos RAT Masquerades as Windows Update

Chaos RAT Masquerades as Windows Update

Cisco Talos reports a remote access trojan (msaRAT) linked to the Chaos ransomware group that hides its command-and-control traffic inside legitimate Chrome/Edge browser activity. The malware is delivered as a fake “Windows update” MSI and, once run, launches a browser in a special debug mode to…

July 23, 2026
Fake Recruiters & Cloud Email Fuel New Phishing

Fake Recruiters & Cloud Email Fuel New Phishing

This roundup describes real-world social engineering where attackers impersonate recruiters on LinkedIn and lure developers into running “coding tests” that install malware. It also outlines active phishing campaigns that abuse trusted cloud services (Google, AWS, Azure, Cloudflare) to send…

September 2, 2026