Attackers compromised legitimate Ukrainian websites and showed visitors a fake CAPTCHA/Cloudflare-style “verification” prompt to trick them into installing malware. The infection chain drops Lunex (aka Psychedelic Stealer), which disables security monitoring using a vulnerable AMD driver and then steals browser passwords, session cookies, and crypto wallet data.
How the Attack Worked
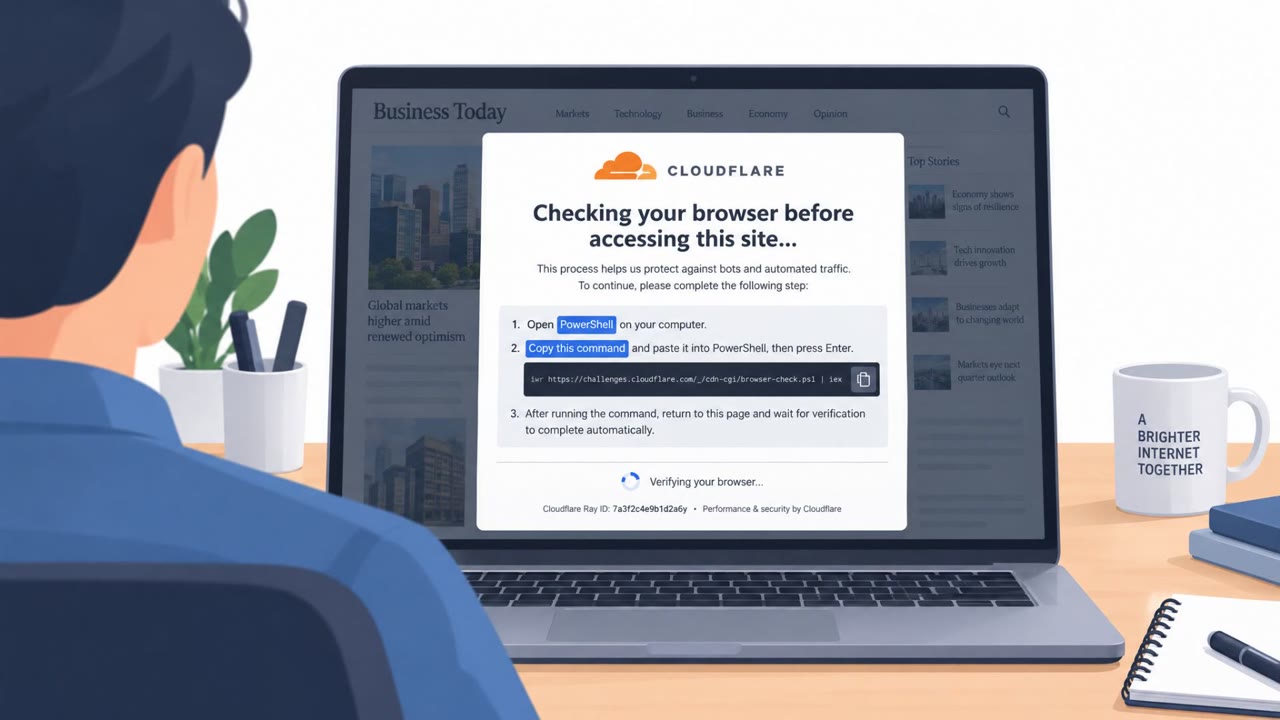
This attack chain begins on legitimate Ukrainian websites that have been compromised. Attackers inject an iframe element designed to serve a ClickFix-style lure, a fake Cloudflare verification page that asks visitors to complete a CAPTCHA or security check. Instead of a normal verification, the page instructs users to download and run a bogus MSI installer. Once executed, the chain deploys Lunex Stealer, also known as Psychedelic Stealer, which uses a bring your own vulnerable driver technique with an AMD Radeon driver to blind security monitoring tools while keeping them appearing to run normally.
Why It Succeeded
The lure works because it appears on websites users already trust, removing the usual suspicion attached to unfamiliar domains. A CAPTCHA or security verification prompt feels routine and expected, so the request to run an installer or follow verification steps does not immediately register as unusual. The technical evasion compounds this: disabling security tools without stopping them from running means monitoring systems may not flag the compromise in real time, giving the stealer time to harvest browser passwords, session cookies, and cryptocurrency wallet data across seven Chromium-based browsers.
What to Watch For
- Unexpected verification or CAPTCHA prompts that ask you to download or run software
- A security check appearing on a site you normally trust without prior notice
- Any instructions to run an MSI installer or terminal commands to "fix" access or continue browsing
- Unusual browser behavior following a verification prompt, including new processes or slowdowns
Building Resistance
Organizations across retail, healthcare, manufacturing, and professional services should train all employees, IT helpdesk staff, and security operations teams to treat CAPTCHA-style verification prompts with caution, especially when they request an installer or command execution. Finance teams with cryptocurrency exposure face added risk given the stealer's wallet-targeting capability. Encourage staff to report suspicious verification pages rather than complete them, and reinforce that even familiar, trusted websites can be compromised and used to deliver malware through injected content.
Key findings
- Attackers used compromised Ukrainian websites to deliver a “ClickFix-style Cloudflare verification” fake CAPTCHA lure.
- The chain used bogus MSI installers to start infection and ultimately deploy LunexStealer (aka Psychedelic Stealer).
- Lunex used a ‘bring your own vulnerable driver’ (BYOVD) method with an AMD Radeon driver (PDFWKRNL.sys) to ‘blind’ security tools while leaving them running.
- The stealer targets credentials/data from seven Chromium-based browsers and steals crypto wallet data.
- LunexStealer communicated with a Lunex panel at 193.178.159[.]128 over HTTP for information theft and control.
- One observed panel resolved to multiple phishing domains, indicating the platform also supports brand-impersonation phishing.
Who’s being targeted
- Commonly targeted roles: All employees, IT Helpdesk, Security Operations, Finance (crypto exposure).
- Affected industries: Retail, Healthcare, Manufacturing, Professional Services.
- Attack channels: website.
- Impersonated: Cloudflare verification / site security check.
Red flags to watch for
- Unexpected verification/CAPTCHA that asks you to download/run an installer
- Security check appears on a site you normally trust (could be compromised)
- Any prompt that leads to running an MSI or commands to ‘fix’ access
Frequently asked questions
What is the ClickFix fake CAPTCHA attack?
It is a lure where attackers inject a fake Cloudflare-style verification page onto compromised legitimate websites, prompting visitors to run an installer or commands to prove they are human, which instead installs malware.
What does Lunex Stealer do once installed?
Lunex, also known as Psychedelic Stealer, uses a vulnerable AMD driver to blind security tools while leaving them appearing to run, then steals browser passwords, session cookies, and cryptocurrency wallet data from seven Chromium-based browsers.
Can a trusted website still be dangerous?
Yes. The attackers compromised legitimate Ukrainian websites and injected an iframe to serve the fake CAPTCHA lure, showing that a familiar site does not guarantee safety.
What are the warning signs of this attack?
Red flags include an unexpected verification or CAPTCHA prompt asking you to download or run an installer, a security check appearing on a normally trusted site, and any instructions to run an MSI file or commands to fix access.
Read the video transcript
You land on a trusted site and a Cloudflare-style page pops up: “Please verify you are human to continue.” Looks normal, right? Here’s the trick: that “ClickFix-style Cloudflare verification” is fake. The compromised site pushes a bogus MSI installer that drops Lunex Stealer, which quietly blinds your security tools and raids your browser passwords, session cookies, and crypto wallets. The aha: real CAPTCHAs never make you download an MSI. If a “security check” suddenly tells you to run an installer to fix access, even on a site you trust, that’s a Lunex-style trap. If any CAPTCHA or Cloudflare-style page asks you to download or run anything, stop, close the tab, and report it to security with a screenshot and the site address.