Recent Retail Cyber Attacks

Attacks on retailers and e-commerce platforms, from gift card scams to credential phishing against store and corporate staff. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

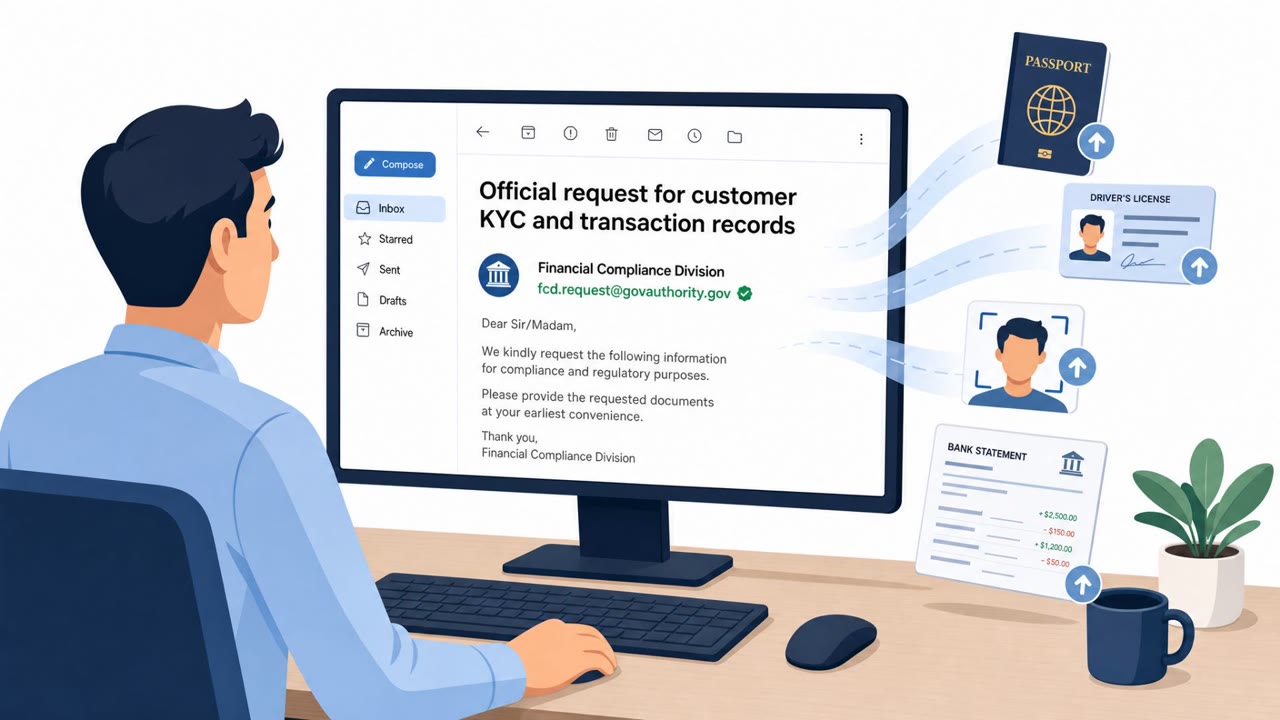
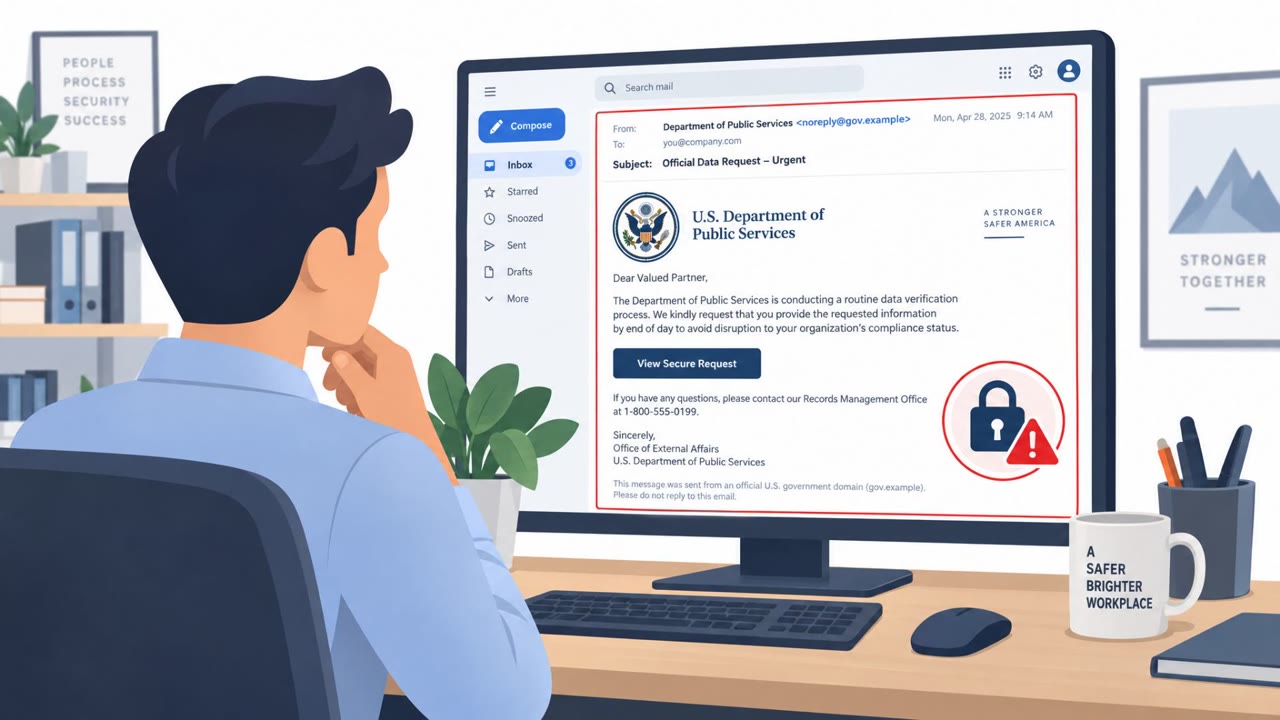
Revolut Fooled by Govt Impersonation Email

Revolut Fooled by Govt Impersonation Email

A person posing as a government agency used an email address on that agency’s real domain to obtain sensitive customer records from Revolut. The same weekly roundup also describes a fake antivirus renewal web page impersonating Avast, telling victims their subscription renewed for €129.99 and…

September 20, 2026
Brevo Breach Spread Malware via ‘Prove You’re Human’

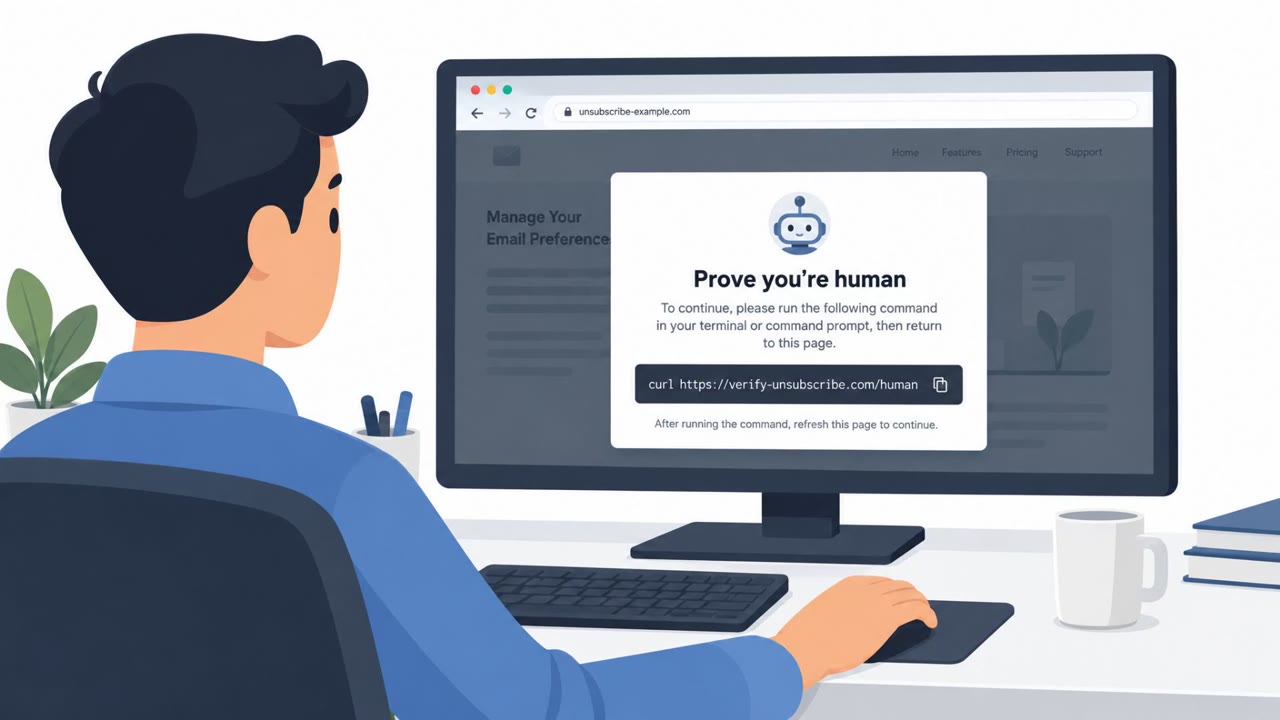
Brevo Breach Spread Malware via ‘Prove You’re Human’

Attackers breached Brevo and used a stolen Cloudflare API key to inject malicious code into Brevo-hosted scripts that thousands of customer websites load. Visitors saw a fake “prove you’re human” prompt meant to trick them into running a command, and logged-in WordPress admins risked having a…

September 18, 2026
Trusted Channels Hijacked for Phishing and Malware

Trusted Channels Hijacked for Phishing and Malware

The article describes multiple real-world social engineering operations this week, including phishing sent from a legitimate Trezor newsletter channel and malware pushed through a verified HBO Max Reddit ad account. It also highlights a large-scale network of fake online stores impersonating real…

September 18, 2026
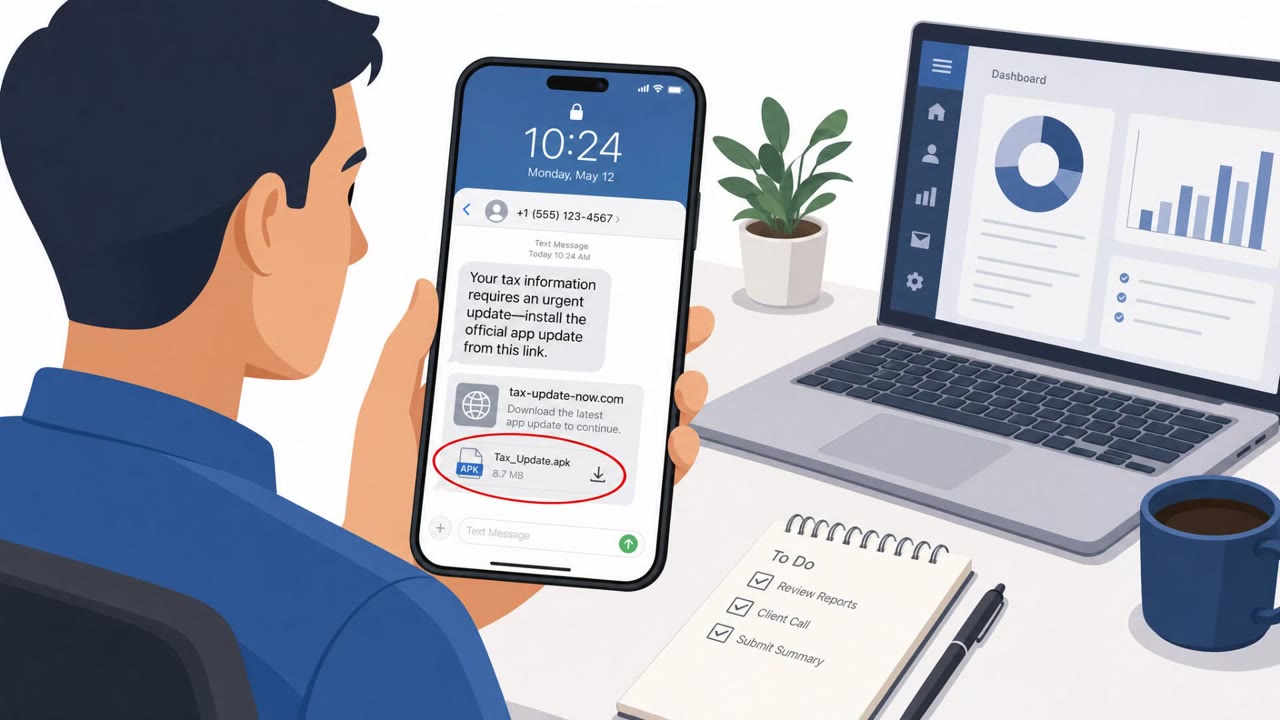
RatHat Smishing Lure Pushes Android Sideloading

RatHat Smishing Lure Pushes Android Sideloading

Researchers described an Android Trojan (“RatHat”) that starts with scam texts or malicious ads and tricks people into installing a fake app from a bogus download page. After installation, it pressures victims to grant Accessibility permissions using fake excuses or incentives, then uses those…

September 18, 2026
Abandoned CDN Domain Hijack Risks Web Users

Abandoned CDN Domain Hijack Risks Web Users

A previously abandoned CDN domain was re-registered, and thousands of websites still reference hostnames under it, meaning a new, unknown owner can control what those sites load without any change on the sites themselves. The article also describes a real, recent “ClickFix” social-engineering…

September 18, 2026
Brevo Hack Served ClickFix Malware to 100K Sites

Brevo Hack Served ClickFix Malware to 100K Sites

Brevo suffered a supply-chain compromise where attackers injected malicious JavaScript into Brevo-hosted pages and customer-embedded website scripts, affecting over 100,000 sites. Visitors were shown a fake “Cloudflare, verify you are human” prompt designed to trick them into running a command on…

September 18, 2026
Fake bpost Customs Fee Scam Steals Bank Details

Fake bpost Customs Fee Scam Steals Bank Details

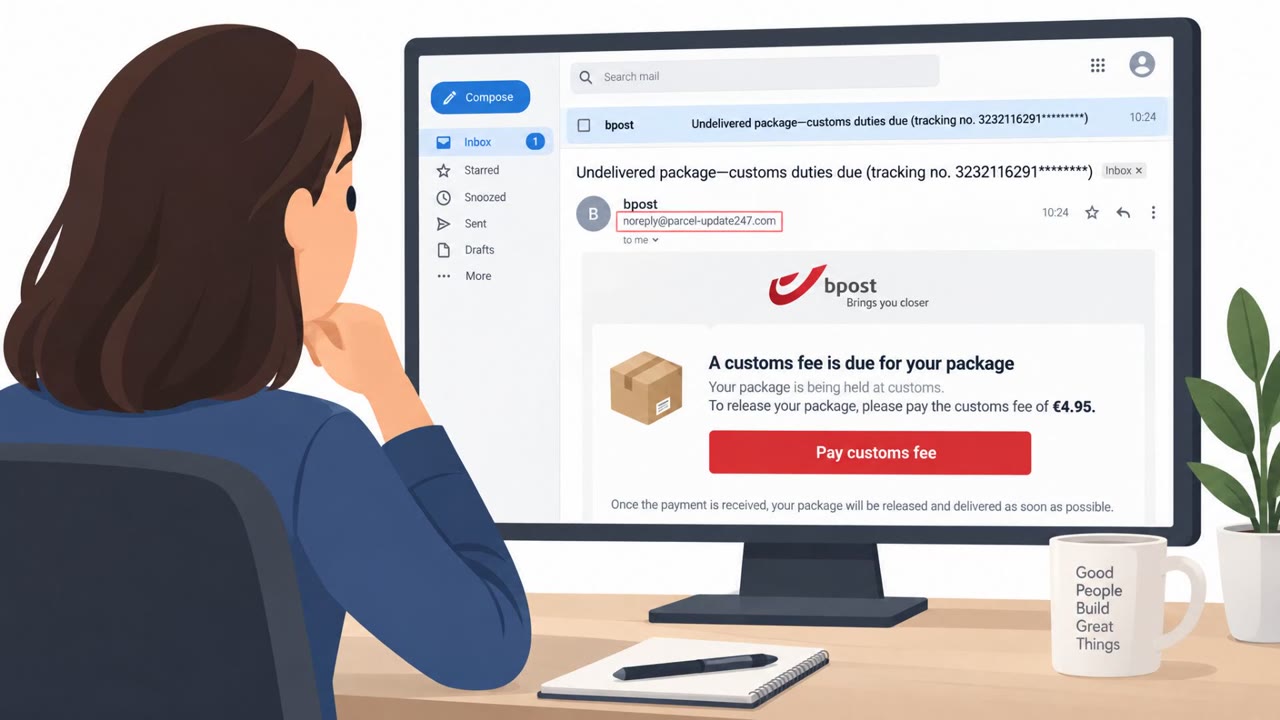
A real phishing campaign impersonated postal couriers (including Belgium’s bpost) to trick people into paying a small “customs fee” for an undelivered parcel. Victims were sent to a fake courier website that collected personal details, then escalated to stealing full card and banking (IBAN)…

September 18, 2026
Fake Movie Torrent Drops MovieReaper Trojan

Fake Movie Torrent Drops MovieReaper Trojan

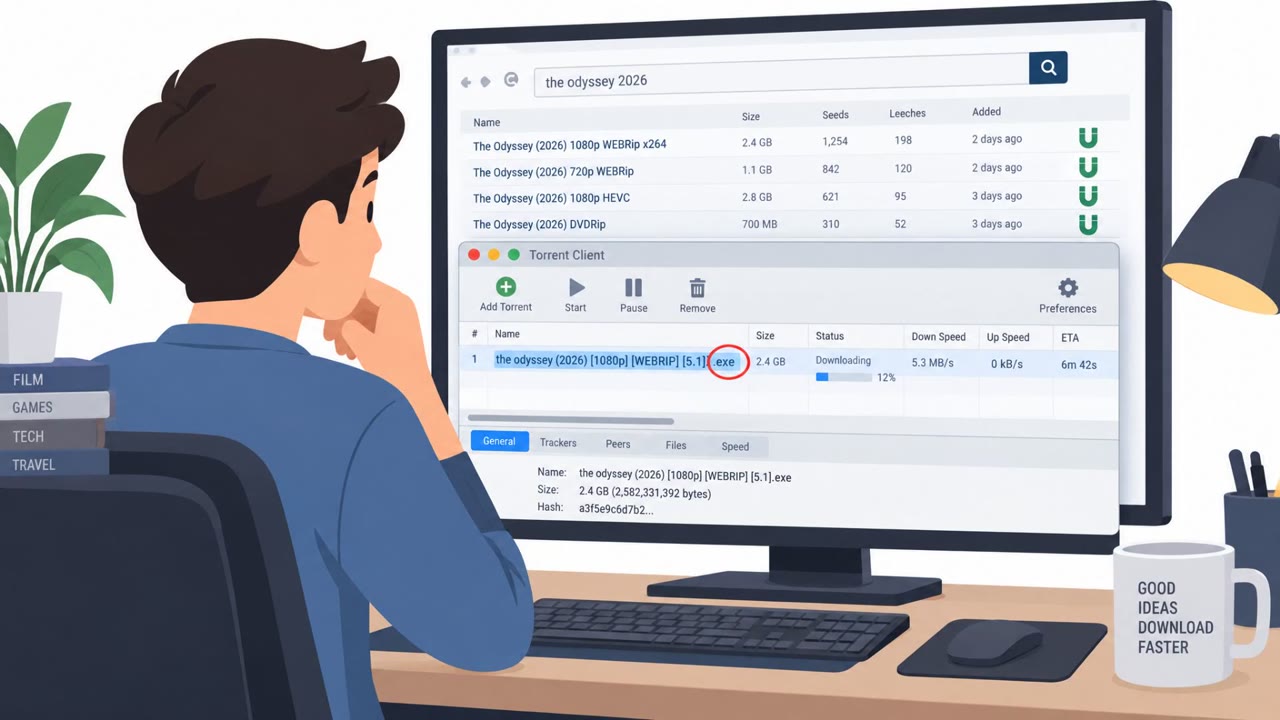
A real malware campaign dubbed “MovieReaper” infected users who tried to download popular movies from torrent trackers. Attackers abused a compromised public torrent-file repository so that magnet links returned a different torrent that downloaded a Windows .exe disguised as a movie file, which…

September 17, 2026
AT&T Insider Aided SIM-Swap Bank Heists

AT&T Insider Aided SIM-Swap Bank Heists

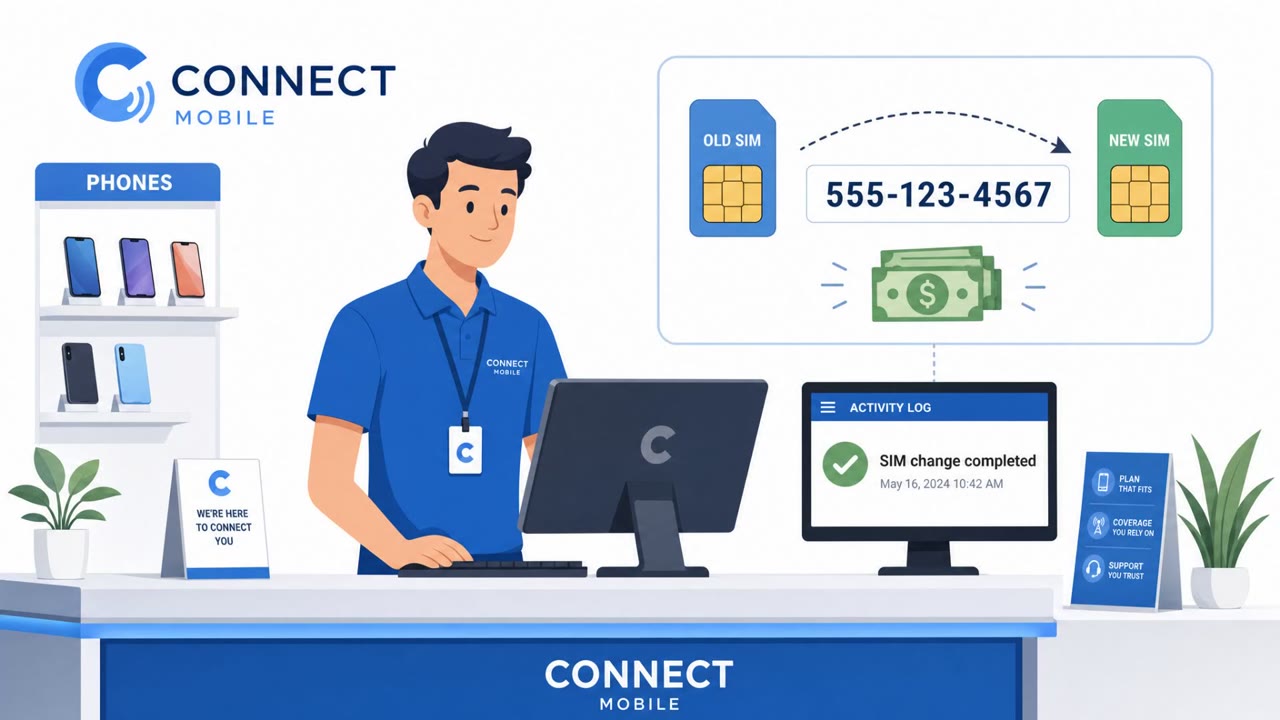
A former AT&T retail employee helped a SIM-swap crew hijack customers’ phone numbers, letting the criminals intercept SMS two-factor codes and reset online banking passwords. The gang then attempted (and in one case succeeded) to wire large sums from victims’ bank accounts, often to accounts in…

September 15, 2026
Fake Bitrefill Sites Steal Crypto via Search Results

Fake Bitrefill Sites Steal Crypto via Search Results

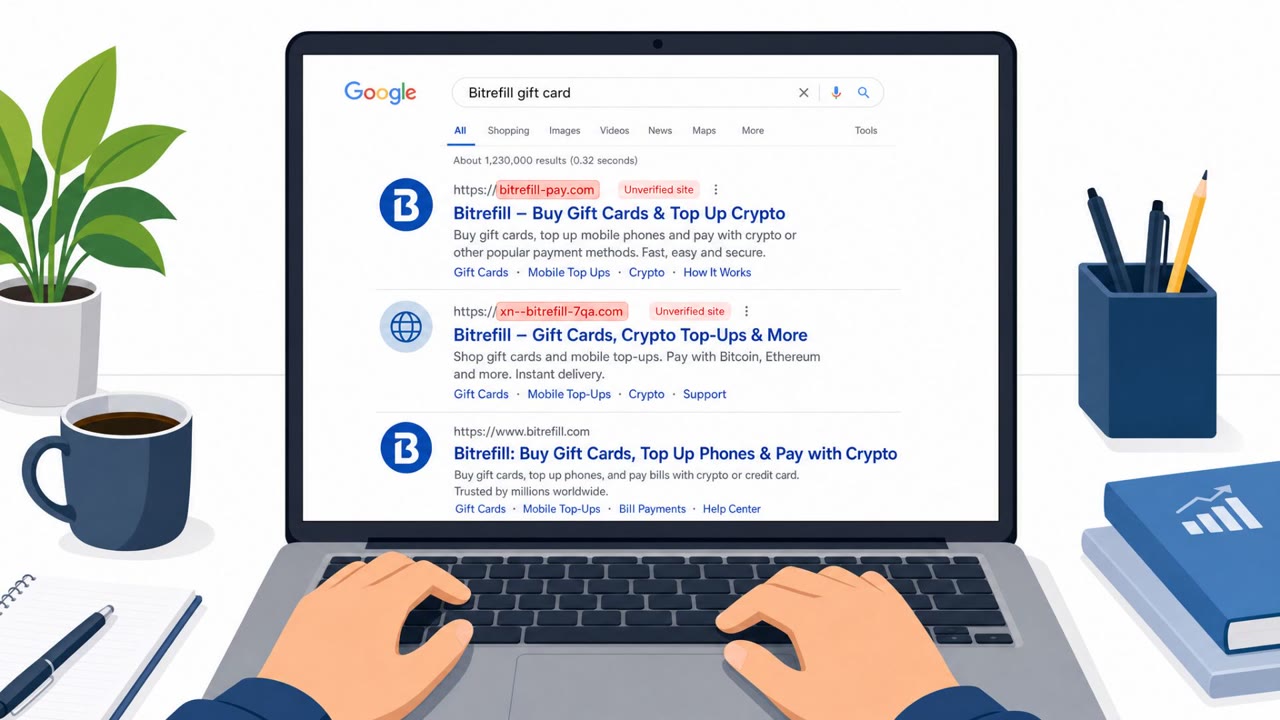
Scammers are using lookalike Bitrefill domains that appear in search results to trick people into buying gift cards or top-ups. The fake sites copy Bitrefill’s branding and checkout flow, then display a QR code and crypto address so victims unknowingly pay the scammers instead of Bitrefill. Because…

September 15, 2026
Revolut Tricked by Fake Government Email

Revolut Tricked by Fake Government Email

Revolut disclosed it was deceived into sharing highly sensitive customer data after receiving fraudulent information requests that appeared to come from a legitimate government email domain. The attacker’s email passed domain authentication, making it harder to detect, and the shared data may…

September 14, 2026
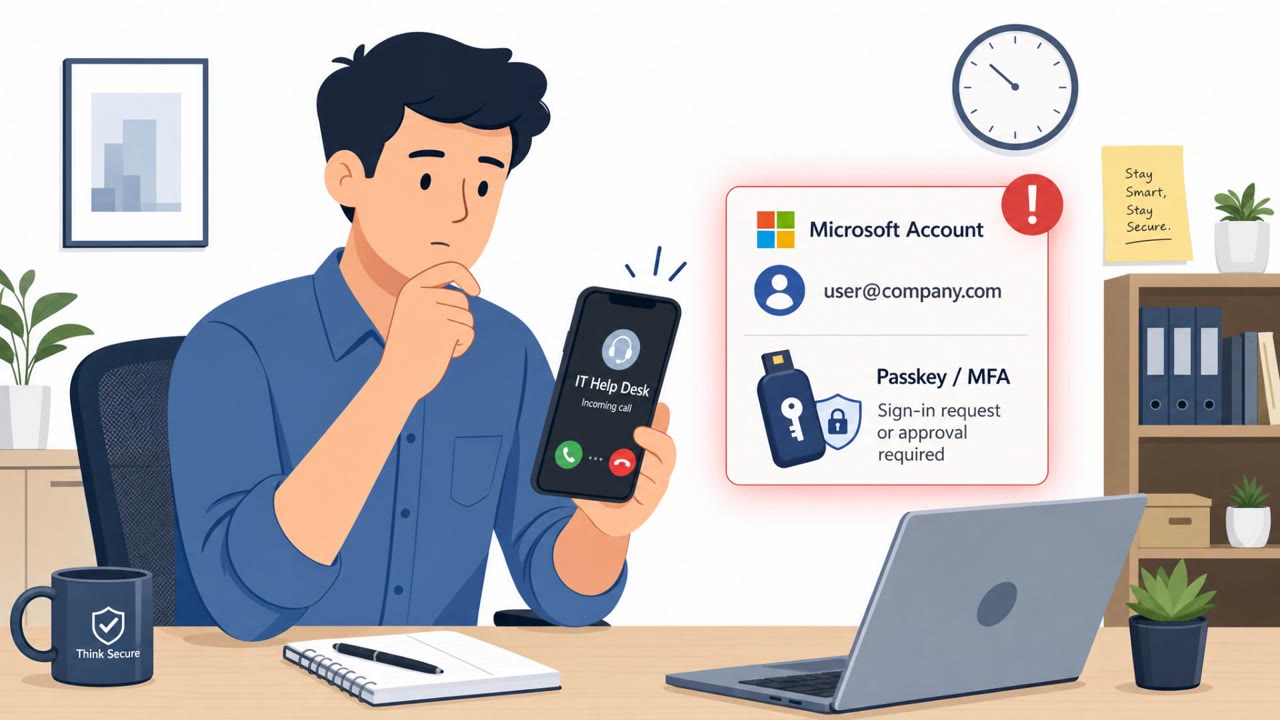
Passkey Helpdesk Scam Hijacks Microsoft Accounts

Passkey Helpdesk Scam Hijacks Microsoft Accounts

Microsoft described two real-world campaigns: an invoice fraud blast impersonating executives to trick finance teams into ACH payments, and a passkey-themed helpdesk scam that steals or bypasses authentication to take over Microsoft cloud accounts. In the second campaign, victims are called or…

September 13, 2026
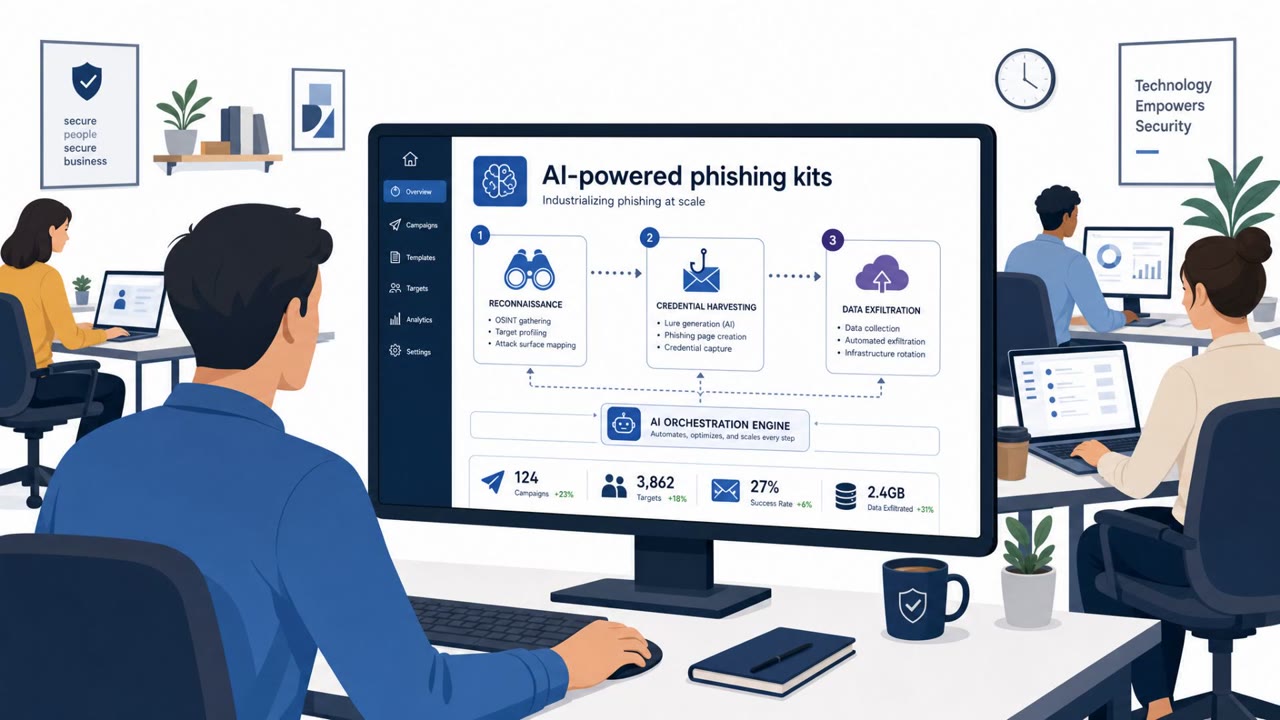
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
Gigabud Clones Banking Apps in Hidden Work Profile

Gigabud Clones Banking Apps in Hidden Work Profile

Researchers say the Android banking Trojan “Gigabud” can trick victims into installing a fake app, then create a separate Android work profile and run a cloned banking app inside it. Attackers can perform fraudulent transactions from that cloned app, which may reduce the chance that bank defenses…

September 11, 2026
Pig Butchering Scams Drive $12.7B Crypto Losses

Pig Butchering Scams Drive $12.7B Crypto Losses

FinCEN reports that overseas scam centers stole about $12.7B from U.S. victims since 2023, largely through “pig butchering” style cryptocurrency investment scams. Scammers build trust using fake personas (often romance or “financial adviser” roles), then pressure victims to buy crypto and send it…

September 10, 2026
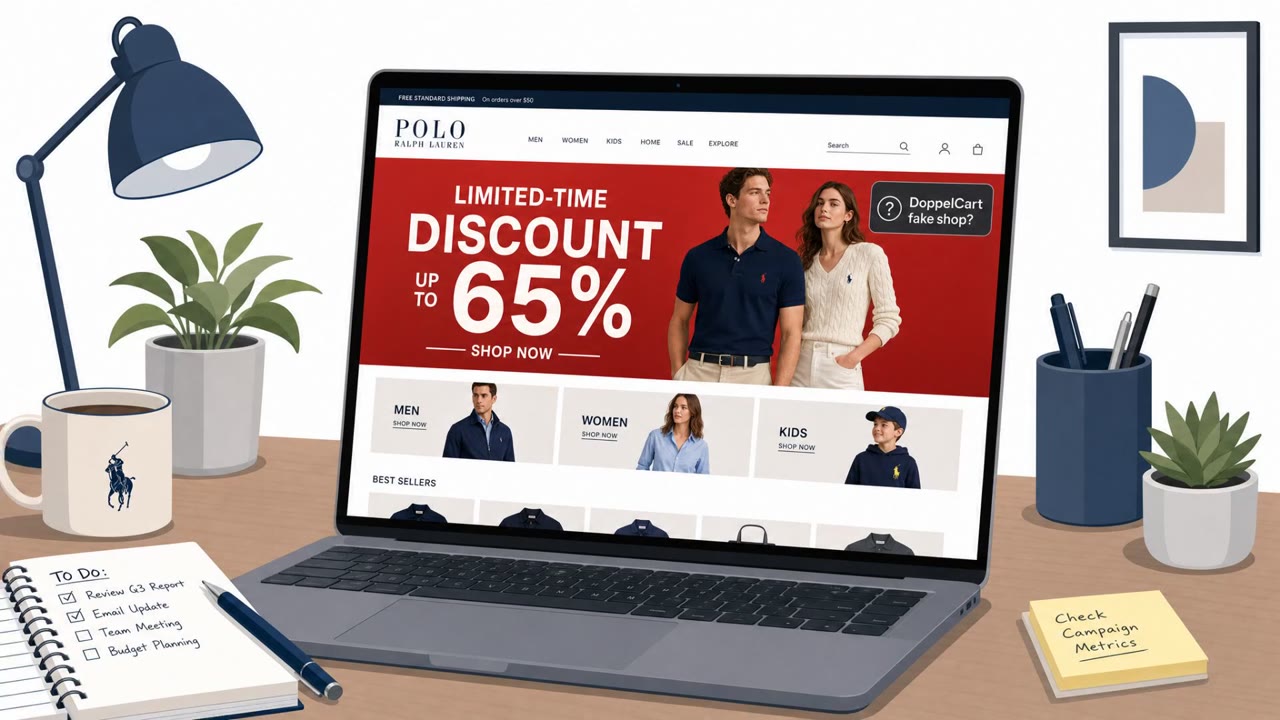
DoppelCart Fake Shops Steal Payment Details

DoppelCart Fake Shops Steal Payment Details

Researchers uncovered a massive network of over 119,000 fake online stores that copy real brands to trick shoppers into entering payment details. The cloned sites look legitimate and use big discounts to create urgency, but the checkout pages capture card and personal data that criminals can reuse…

September 10, 2026
AI-Assisted CEO Invoice Scam Pushes $50K ACH

AI-Assisted CEO Invoice Scam Pushes $50K ACH

Microsoft reports a real, large-scale email campaign that impersonated company executives and ServiceNow to pressure accounts payable teams into sending nearly $50,000 via ACH/bank transfer. The emails bundled a CEO “approval,” a fake ServiceNow-branded invoice, and a fabricated forwarded thread to…

September 10, 2026
Fake M&A Wire Fraud and Trezor Phishing Alert

Fake M&A Wire Fraud and Trezor Phishing Alert

This bulletin describes multiple real-world scams where attackers manipulate trust to steal money or sensitive data. Notably, attackers impersonated executives to pressure legal teams into moving M&A discussions to WhatsApp/personal email to trigger international wire transfers, and Trezor users…

September 10, 2026
119,000 Fake Shops Clone Brands to Steal Cards

119,000 Fake Shops Clone Brands to Steal Cards

Researchers found a massive network of nearly 119,000 look‑alike online stores that copy real retailers’ branding and product pages. These fake shops lure buyers with big discounts and then capture payment card details (and sometimes bank one‑time codes) during checkout, sending the data to…

September 9, 2026
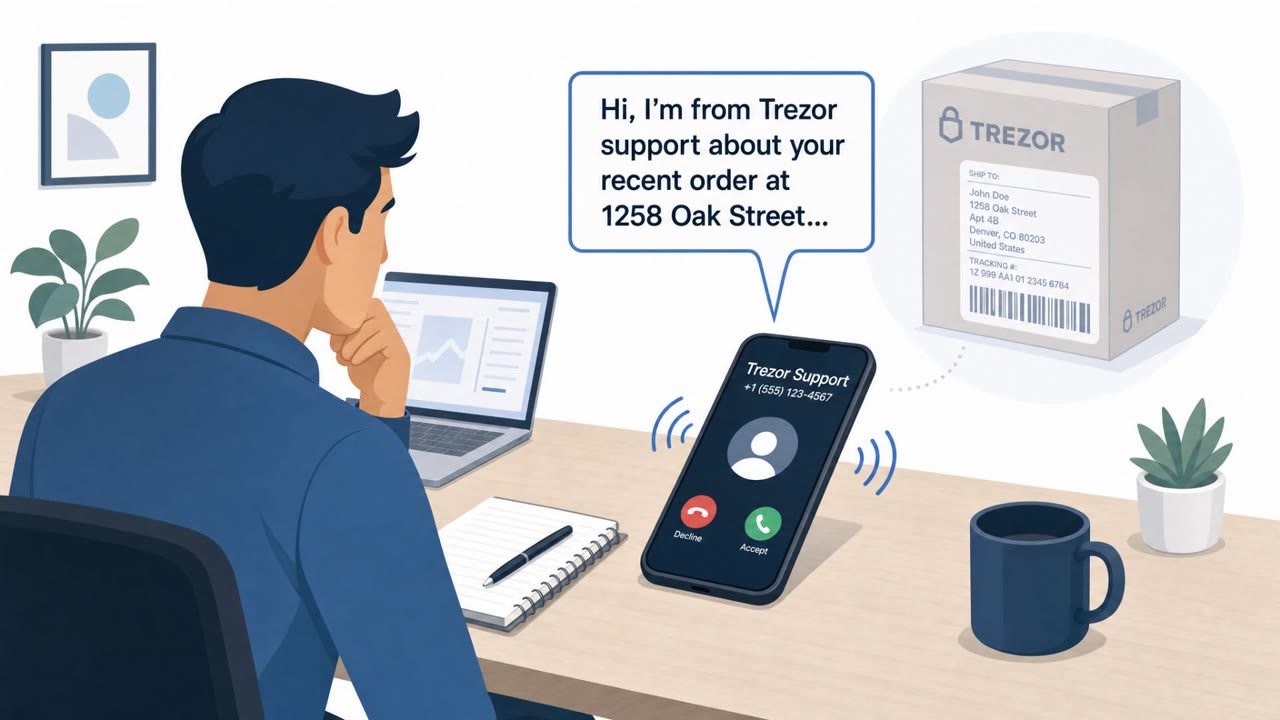
Trezor Users Targeted by Phishing Calls & QR Letters

Trezor Users Targeted by Phishing Calls & QR Letters

After a breach at shipping partner ShipMonk, attackers obtained Trezor customers’ contact and shipping details, increasing the risk of scams. Reports on Reddit indicate customers have already received phishing phone calls and physical letters containing QR-code phishing lures. Trezor warned…

September 8, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo