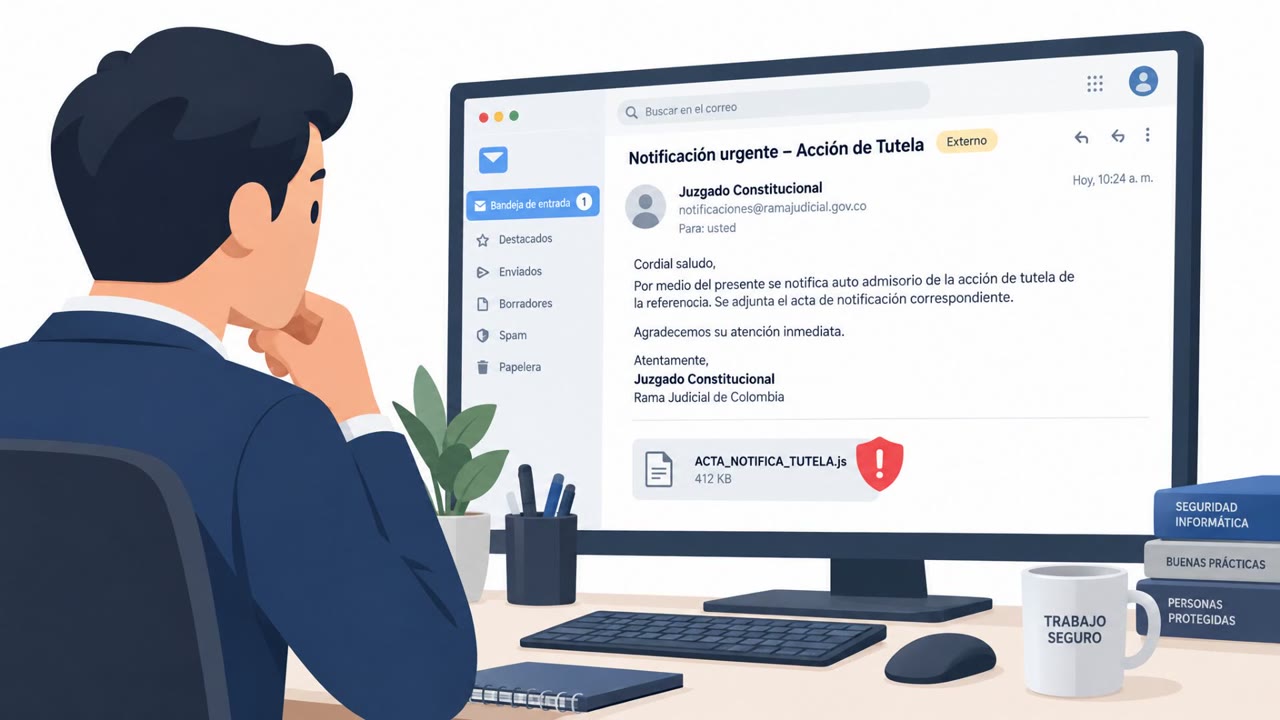
Russia-aligned Gorbag targeted Ukrainian government, law-enforcement, and defense organizations with spear-phishing emails disguised as official administrative fines or tax notices. The emails carried malicious attachments, including macro-enabled Excel files, that installed data-stealing malware to collect browser data, VPN settings, and sensitive documents.
Key findings
- Gorbag has targeted Ukrainian organizations since at least February 2025, especially law enforcement, justice entities, local administrations near the front line, and the defense sector.
- The group used government-themed spear-phishing lures involving administrative fines or taxes.
- One observed delivery method used a macro-enabled Excel spreadsheet that ran a VBA payload to install BeautyStealer.
- BeautyStealer collected browser data, VPN configurations, RDP configurations, KeePass databases, Office files, archives, and email-related files.
- Stolen information was compressed and sent to an attacker-controlled Telegram chat or a custom command-and-control server.
- Gorbag also exploited the patched WinRAR vulnerability CVE-2025-8088 to execute GIFTEDCROOK through a DLL sideloading chain.
Who’s being targeted
- Commonly targeted roles: Government employees, Law enforcement, Justice-sector staff, Local administration personnel, Defense-sector personnel, Finance and tax-processing staff, Executive assistants.
- Affected industries: Government, Law enforcement, Justice agencies, Local administration, Defense.
- Attack channels: email.
- Impersonated: Government or public-administration authority.
Awareness takeaways
- Treat unexpected fine, tax, or other government-action messages as suspicious, especially if they include an attachment. Verify the notice through an independently known official contact channel before opening anything.
- Do not enable macros or content in an Excel attachment received by email unless its legitimacy has been independently confirmed.
- Protect and report potential exposure of browser credentials, VPN files, RDP settings, and password-manager databases quickly, since these can enable further access to the organization.
- Remember that a simple-looking attachment can support a serious espionage operation; report suspicious government-themed messages rather than assuming they are routine paperwork.
Red flags to watch for
- An unsolicited government-themed message uses pressure around a fine or tax obligation.
- The attachment is a macro-enabled Excel file (.XLSM).
- The recipient is asked to enable content or macros in a spreadsheet.
Read the video transcript
A government fine lands in your inbox. It looks like routine paperwork. Gorbag sends these notices to Ukrainian offices. The attachment is an Excel .XLSM file. Click 'Enable Content,' and its macro can install BeautyStealer. Here's the twist: the 'fine' is bait. BeautyStealer can take browser data, VPN and RDP settings, KeePass databases, and documents, then send them to a Telegram chat. Unexpected fine or tax notice? Before opening the attachment, call the agency using a number you already know.