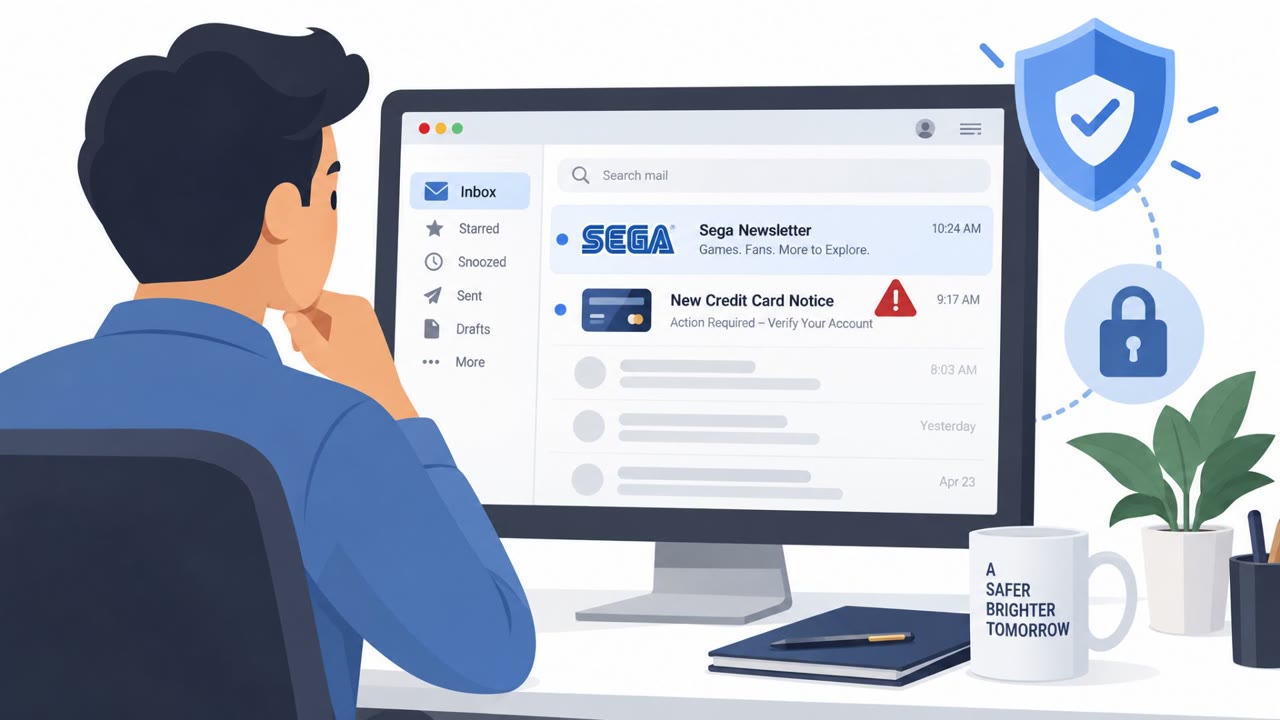
Hackers Spoof Banks in Japan Phishing Blast

About DFIR · Medium sophistication
Last updated November 16, 2026

Attackers who breached Arara’s email distribution service used it to send millions of phishing emails that impersonated credit card companies and banks. The campaign affected customers of the service, including organizations connected to Osaka’s online administrative services platform, showing how a trusted third-party email system can be abused to make fraudulent messages appear credible.

Key findings

  • Hackers accessed the Arara email distribution service, which was used by contractor TKC Corporation.
  • Arara said the November 2 cyberattack exposed 77 million email addresses belonging to nearly 400 customers.
  • Attackers abused the email service to send millions of phishing messages impersonating credit card companies and banks.
  • More than 1 million email addresses tied to Osaka’s online administrative services platform were reportedly exposed.

Who’s being targeted

  • Commonly targeted roles: All employees, Finance and accounts-payable teams, Administrative staff, Third-party/vendor management teams, IT and security teams.
  • Affected industries: Government, Financial services, Technology and online services.
  • Attack channels: email.
  • Impersonated: Credit card company or bank.

Awareness takeaways

  • Treat unexpected bank or credit-card messages as suspicious, even if they appear to come through a familiar or trusted email service.
  • Do not use links or phone numbers in an unexpected financial message; independently contact the bank or card provider through a known official channel.
  • Limit exposure from third-party email platforms and ensure suppliers can quickly report and contain compromises involving customer contact data.

Red flags to watch for

  • The sender claims to be a bank or card company but the message arrives unexpectedly.
  • The message uses urgency around an account or payment issue.
  • A familiar bulk-email service or trusted sender infrastructure can make an impersonation email appear more credible.
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

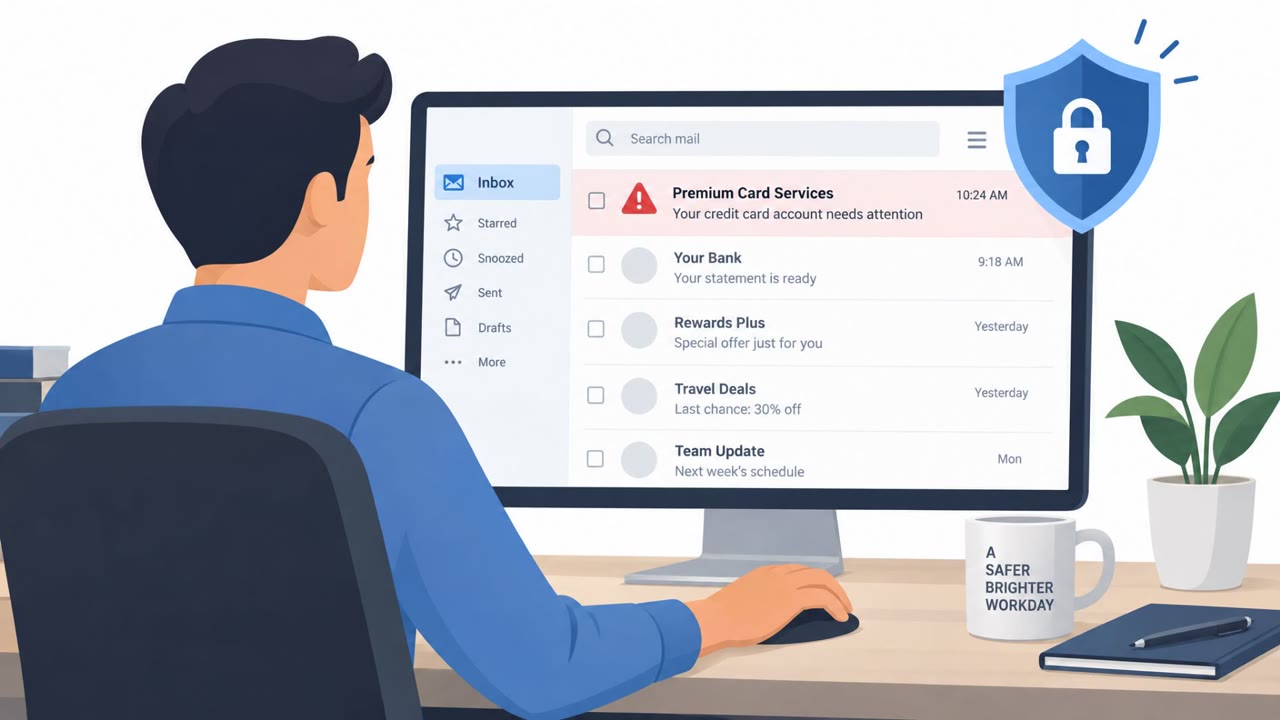
“Notice regarding your credit card account.” Looks routine? Not so fast. After Arara’s email service was breached, it was used to send millions of messages posing as banks and card companies. The familiar delivery system made the emails look credible. Here’s the catch: a trusted delivery service doesn’t prove the message is from your bank. Unexpected account warning? Urgent payment issue? Don’t trust the link, or the phone number inside. Instead, contact your bank using the number on your card, not anything in that email.

MITRE ATT&CK techniques

Similar attacks

Arara Breach Fuels Card-Brand Phishing

Arara Breach Fuels Card-Brand Phishing

After attackers compromised newsletter provider Arara, they sent more than seven million emails pretending to come from credit card companies. The incident exposed Sega newsletter subscriber email addresses along with data from hundreds of other organizations, creating a credible opportunity for…

November 11, 2026
COLD RELIC Turns Stolen Trust Into Phishing

COLD RELIC Turns Stolen Trust Into Phishing

Russian espionage group COLD RELIC used stolen employee identities, contact lists, and business context from one cloud breach to convincingly target people at other organizations. It impersonated known professional contacts over a secure messaging app, then sent phishing links that led to relevant…

November 17, 2026
Fake Defense Jobs Deliver GravityRAT Spyware

Fake Defense Jobs Deliver GravityRAT Spyware

Pakistan-aligned hackers reportedly used convincing fake recruitment websites to lure Indian defense workers and military personnel into downloading spyware. The sites borrowed trusted defense-company branding and claimed their Google Play app was still under review, steering visitors to download…

November 17, 2026
Fake Myanmar Election PDFs Hide Stealthy RAT

Fake Myanmar Election PDFs Hide Stealthy RAT

A cyberespionage group targeting Southeast Asian government organizations used phishing pages and lookalike government domains to distribute malware disguised as PDF documents. Victims who opened the apparent PDF instead launched a remote-access tool, while a decoy election-related document…

November 17, 2026
Arara Breach Sends 7.13M Card Phishing Emails

Arara Breach Sends 7.13M Card Phishing Emails

Attackers compromised Arara Message, a Japanese email delivery platform, potentially exposing about 77 million email addresses across roughly 380 client companies. They then used the trusted service to send up to 7.13 million suspicious emails that impersonated credit card companies and asked…

November 3, 2026
Fake Recruiters Target Job Seekers With Malware

Fake Recruiters Target Job Seekers With Malware

Iran-aligned DarkBlinders used convincing recruitment offers while posing as Dubai Airports recruiters to target a high-value job seeker in Iraq. The victim was asked to complete what appeared to be a coding assessment, but the assessment package installed malware. The group also used lookalike…

November 2, 2026