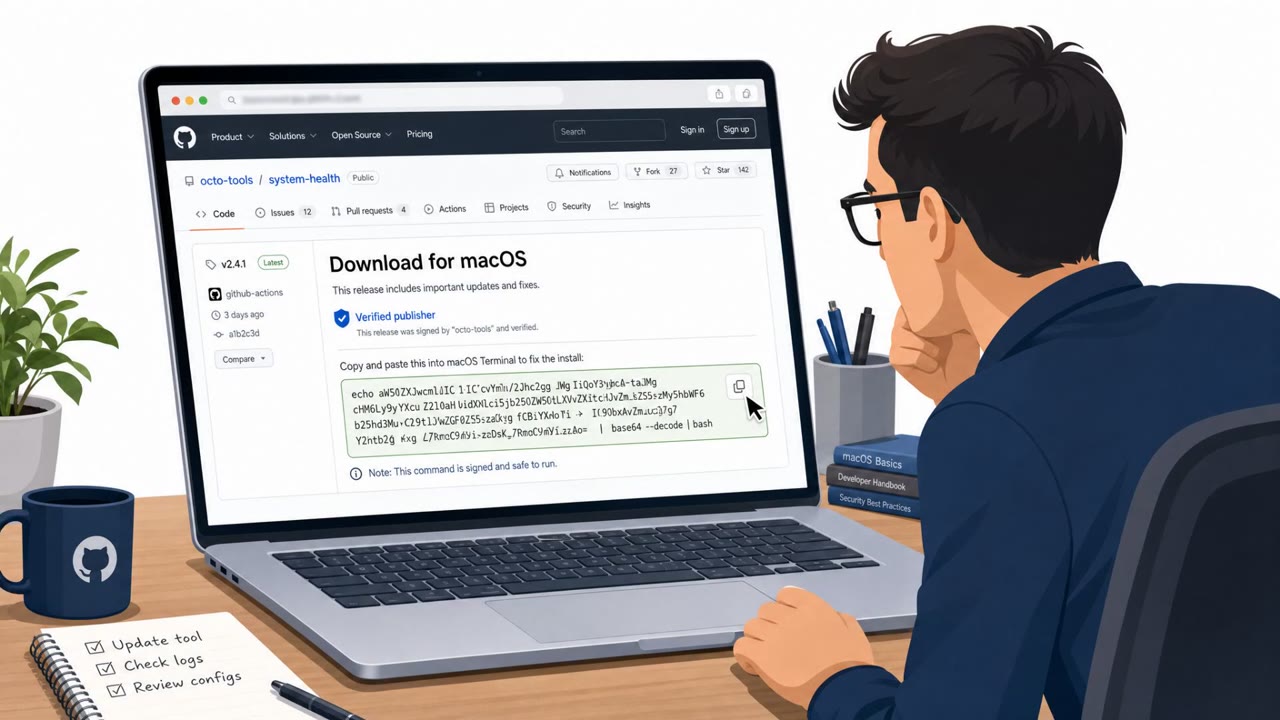
Kaspersky reports a real-world MacSync infostealer campaign seen in September 2026 that tricks users into installing fake or cracked macOS apps. The attack uses staged downloads (including iCloud Calendar content) and then prompts the user for an administrator password using realistic-looking pop-ups that mimic the impersonated app and a macOS warning.
Key findings
- MacSync is a macOS info/crypto stealer sold as malware-as-a-service (MaaS) and observed in the wild in September 2026.
- Attackers distributed it by disguising it as "free or cracked versions of popular applications" and "under the guise of new software," including a fake crypto wallet named "Toria," promoted on X and Telegram.
- The campaign used malicious DMG images and multi-stage droppers/loaders, including delivery of commands hidden inside an iCloud Calendar file (abusing the calendar DESCRIPTION field).
- The infostealer prompts users for an "administrator password" and shows a follow-up fake macOS-style warning claiming the app is corrupted and offering to move it to the trash.
- Persistence mechanisms included a LaunchAgent and injecting commands into shell startup files (e.g., .zshrc) and Git hooks.
Who’s being targeted
- Commonly targeted roles: All employees (macOS users), Finance teams, IT/helpdesk, Executives and admins with local admin rights.
- Affected industries: Cross-industry (macOS users), Cryptocurrency users.
- Attack channels: website, telegram, email.
- Impersonated: A crypto wallet app brand ("Toria"), A legitimate macOS application (the pop-up is adapted to match the impersonated app).
Awareness takeaways
- Treat “free/cracked” software and brand-new apps promoted on social media/Telegram as high risk; require employees to use approved software sources.
- Train users to stop and verify when a newly installed app immediately asks for an administrator password.
- Teach users that “app is corrupted, move to trash” pop-ups can be fake and may appear after credential theft; report it rather than clicking through.
- Include cloud-service abuse in awareness messaging (attackers can use legitimate services like iCloud as part of delivery).
Red flags to watch for
- Brand-new or unfamiliar app name promoted via social media/Telegram
- Software not found in official vendor channels (e.g., App Store / known publisher)
- Installer delivered as a DMG from a promotional page rather than a trusted source
- Unexpected request for an administrator password immediately after launching a newly installed app
- Password prompt appears outside normal corporate software installation flow
- Follow-on “corrupted application” warning right after providing the password
Read the video transcript
Imagine this: a shiny new crypto wallet called “Toria” pops up on X and Telegram, promising a free macOS app. You download the Toria DMG, open it, and the “wallet” instantly asks for your Mac administrator password, then shows a fake macOS alert saying the app is corrupted and can be moved to the trash. That’s MacSync infostealer doing its job. Behind that, MacSync is a malware‑as‑a‑service infostealer. It came from a malicious DMG, pulls extra commands from things like an iCloud Calendar file, and then digs in using LaunchAgents and edits to files like .zshrc and Git hooks. If any new Mac app, especially a “free” or social‑media‑only one, immediately asks for your admin password or says it’s corrupted, stop. Close it and report it to IT Security right away.