Recent Education Sector Cyber Attacks

Page 6 of 6
Fake ShinyHunters Sextortion Demands $2,000

Fake ShinyHunters Sextortion Demands $2,000

A sextortion email campaign is using real leaked email addresses from ShinyHunters-related data dumps to make threats sound credible. The scammers impersonate the “ShinyHunters hacking group,” claim they recorded victims via webcam, and demand $2,000 in Bitcoin within 48 hours. Reporting indicates…

July 27, 2026
Tax and SSA Phish Push Cruciferra Malware Loader

Tax and SSA Phish Push Cruciferra Malware Loader

Researchers report multiple real-world email phishing campaigns that used tax and government-benefit themes to trick people into downloading malware. The campaigns used a “crypter” service called Cruciferra to hide malicious files and help malware run while avoiding detection. Targets included…

July 27, 2026
Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

Rogue Wi‑Fi Portals Steal Microsoft 365 Logins

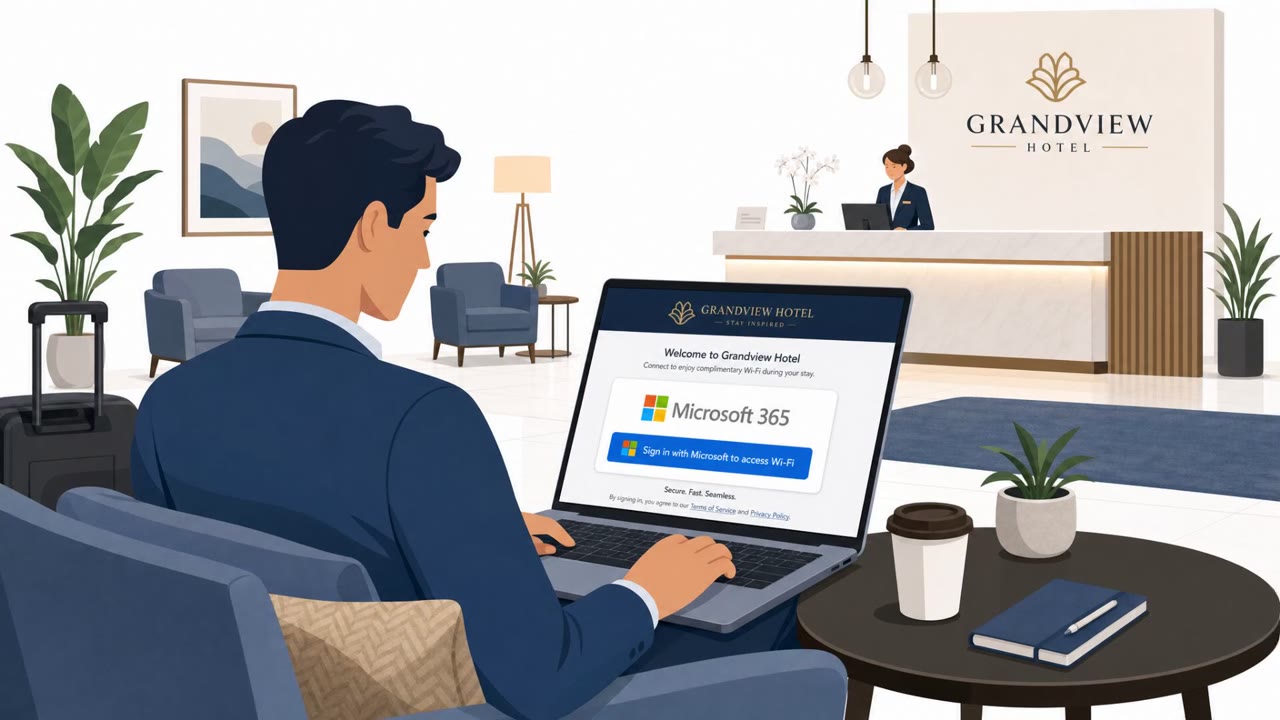
ReliaQuest reports attackers are compromising public Wi‑Fi “captive portal” gateways (such as in hotels and conference centers) and changing their DNS settings to redirect users to attacker-controlled pages. The goal is to harvest traveling employees’ Microsoft 365 credentials using…

July 27, 2026
Hotel Wi‑Fi DNS Poisoning Steals Work Logins

Hotel Wi‑Fi DNS Poisoning Steals Work Logins

Researchers reported an ongoing campaign where attackers compromise hotel and conference venue Wi‑Fi routers and quietly redirect visitors’ web traffic through attacker-controlled systems. This can lead to corporate usernames and passwords being captured even when the victim does not click a…

July 24, 2026
Laundry Bear Uses Zero-Click Zimbra Email Trap

Laundry Bear Uses Zero-Click Zimbra Email Trap

A newly identified Russia-linked threat actor (“Laundry Bear”) is targeting Western organisations with a zero-click technique that can compromise Zimbra webmail simply by viewing a malicious email. The campaign has reportedly stolen sensitive data across multiple sectors and may evolve to target…

July 24, 2026
Zimbra Email View Triggers Russian Data Theft

Zimbra Email View Triggers Russian Data Theft

Government agencies say a Russian-linked group sent specially crafted HTML emails that exploit a Zimbra webmail flaw, so simply viewing the message can trigger data theft, no click required. The campaign has targeted multiple Western sectors since July 2025 and focuses on stealing email content and…

July 23, 2026
Fake Claude Download Used in JadeProx Attacks

Fake Claude Download Used in JadeProx Attacks

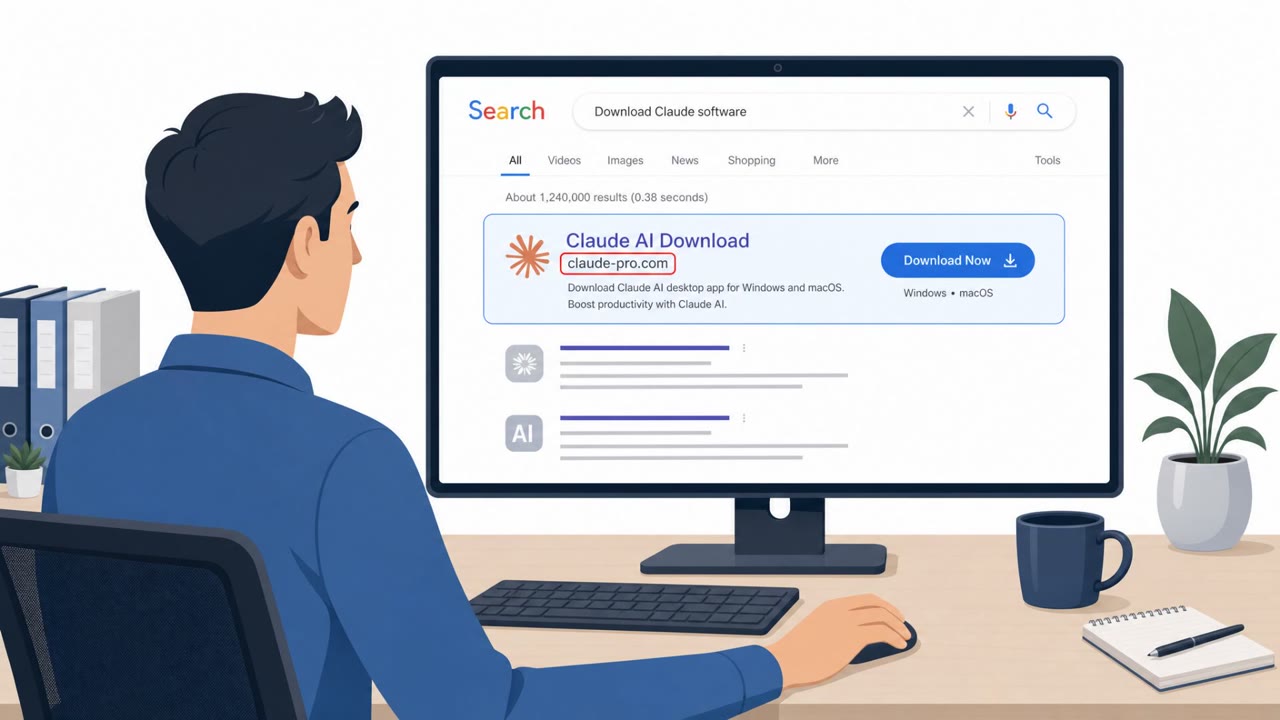
Investigators found evidence of a China-linked operation (tracked as JadeProx) targeting government, healthcare, and education organizations, including spear-phishing and a fake software download site. One campaign impersonated Anthropic’s Claude using a lookalike domain to deliver a malicious…

July 23, 2026
Kimsuky Poses as Diplomats in LNK Phishing

Kimsuky Poses as Diplomats in LNK Phishing

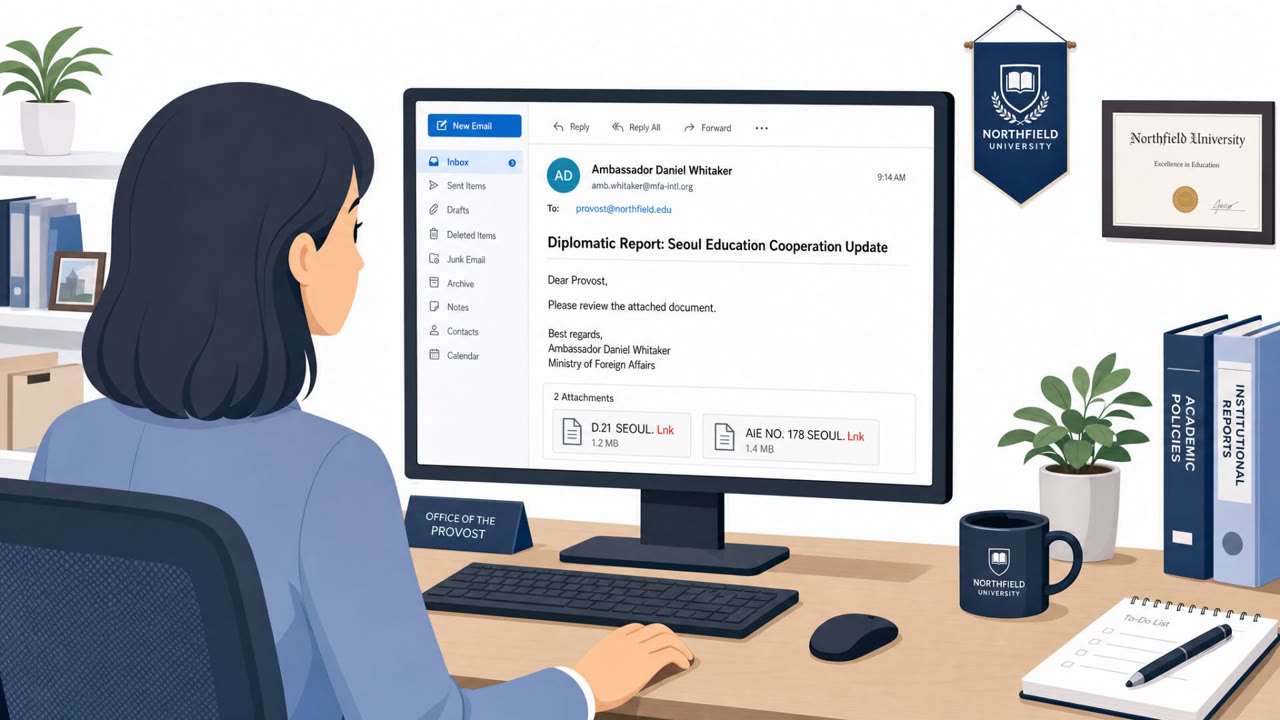
AhnLab reports real-world spear-phishing attacks by the Kimsuky group that impersonate diplomatic personnel and trick targets into opening disguised LNK “document” attachments. Opening the fake document launches scripts that install tools like the PebbleDash backdoor and PrxClient proxy, enabling…

July 23, 2026
Kratos PhaaS Takedown: Fake Microsoft Logins

Kratos PhaaS Takedown: Fake Microsoft Logins

German and international law enforcement disrupted the infrastructure behind “Kratos,” a phishing-as-a-service kit used at scale to steal Microsoft account logins. The kit provided convincing Microsoft-themed fake login pages designed to steal passwords and session cookies, which could help…

July 21, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo