Recent Education Sector Cyber Attacks

Attacks on universities, school districts, and edtech platforms, where phishing campaigns target staff, faculty, and students alike. Each entry is broken down with an original video explainer, key findings, and the red flags your team should watch for. How we produce these.

FBI: Fake Cops Swindle $1.6B via Threat Calls

FBI: Fake Cops Swindle $1.6B via Threat Calls

The FBI says scammers posing as law enforcement or government officials stole over $1.6B since January 2025, mainly by calling victims and threatening arrest, fines, or legal trouble unless they pay. Variants include jury-duty threats, targeted calls to medical professionals about license issues,…

September 18, 2026
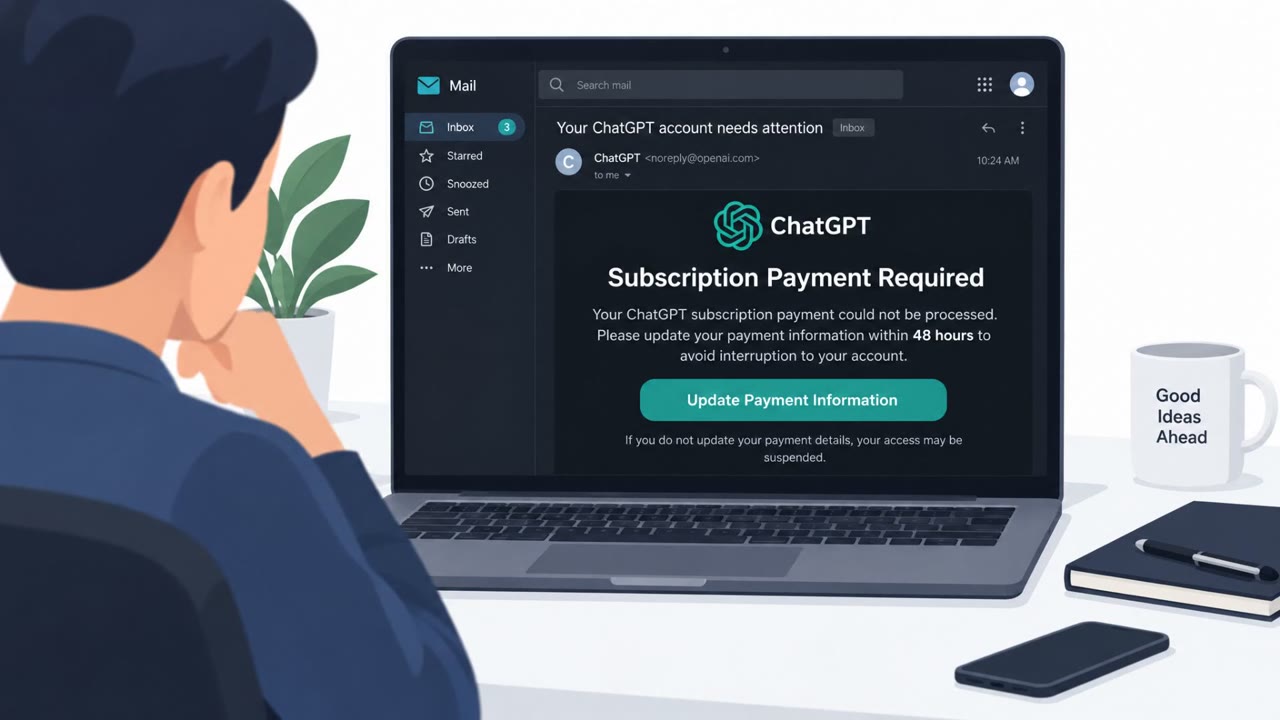
Fake ChatGPT Invoice Steals Login Credentials

Fake ChatGPT Invoice Steals Login Credentials

Cofense observed a real phishing email that impersonates OpenAI/ChatGPT billing to trick users into “updating” payment details. The email uses the real ChatGPT logo, urgency (“48 hours”), and a prominent button to drive clicks to a lookalike ChatGPT login page. Any credentials entered are harvested…

September 17, 2026
AI “Agents” Flood Inboxes With Spam Pitches

AI “Agents” Flood Inboxes With Spam Pitches

The article describes real-world examples of unsolicited emails that claim to be sent by “AI agents,” pitching services, interviews, coverage, and paid work. It includes specific subject lines and message excerpts that show a repeatable workflow: automated outreach that tries to prompt recipients…

September 15, 2026
Fake Downloads and Extensions Steal Sessions Fast

Fake Downloads and Extensions Steal Sessions Fast

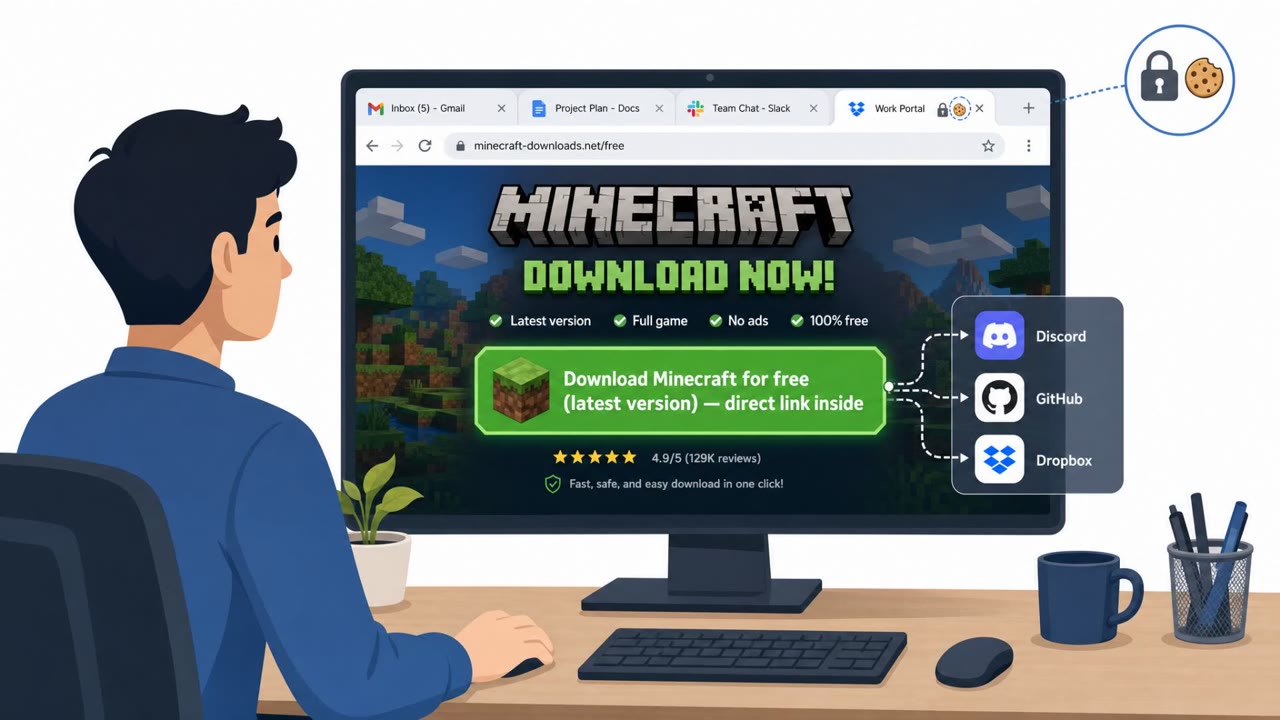
The article highlights real, ongoing campaigns where attackers trick people into installing malware via fake software-download websites and a disguised browser extension. These lures are used to steal credentials, browser cookies, and authenticated sessions, letting attackers take over accounts…

September 11, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

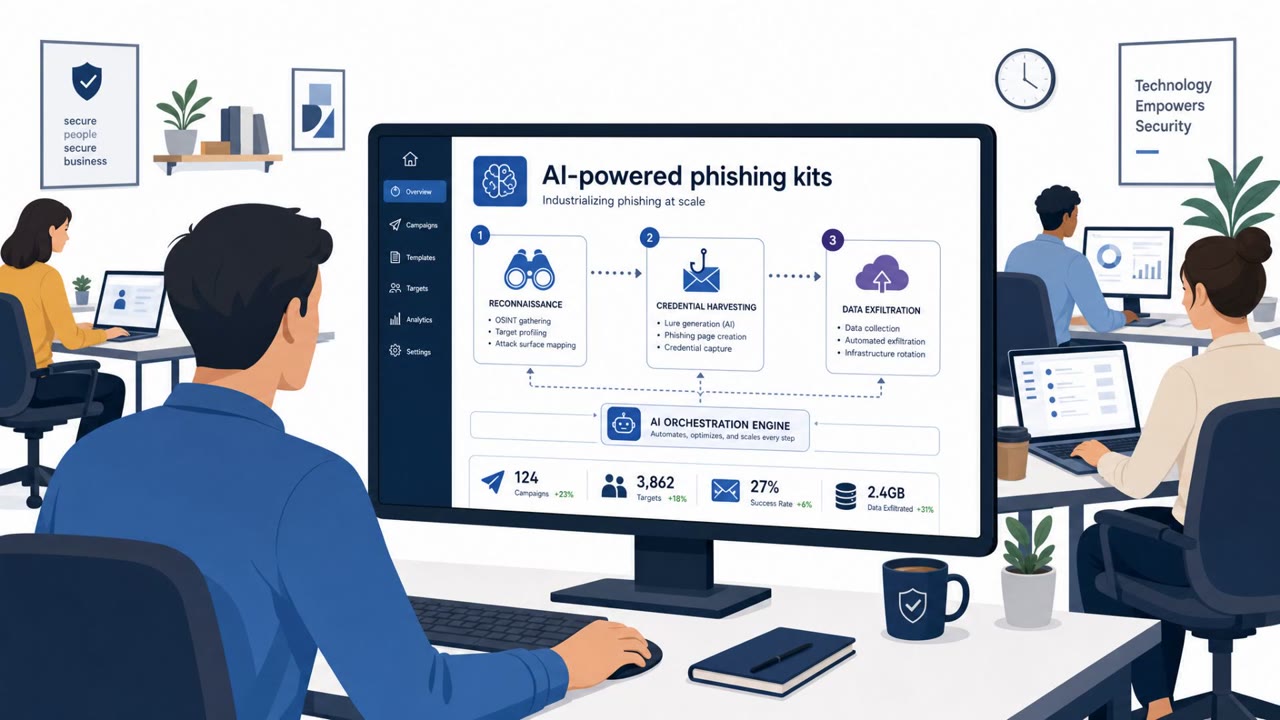
Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
One-Click Sogou Link Trick Dropped GRAYRABBIT

One-Click Sogou Link Trick Dropped GRAYRABBIT

Researchers reported a real intrusion where a China-linked group used a crafted link to exploit Sogou Input Method on Windows and install the GRAYRABBIT backdoor. Victims were lured into opening a special link (potentially via email or chat), which redirected Sogou’s built-in browser to an…

September 11, 2026
Fake Title IX Claims Push Zoho Assist RAT

Fake Title IX Claims Push Zoho Assist RAT

A real phishing campaign is using fabricated sexual misconduct (Title IX-style) allegations to pressure university staff into clicking a link and installing Zoho Assist, a legitimate remote-access tool being abused as malware. The emails impersonate university leaders and route victims through a…

September 10, 2026
Fake Minecraft Sites Keep Spreading WeedHack

Fake Minecraft Sites Keep Spreading WeedHack

Attackers are tricking Minecraft players into downloading malware by cloning legitimate mod/client websites and manipulating search results so the malicious pages appear highly ranked. Even after the malware’s command-and-control systems were disrupted, the fake sites and trusted file-hosting links…

September 8, 2026
Fake LinkedIn Tests and Job Interviews Push Malware

Fake LinkedIn Tests and Job Interviews Push Malware

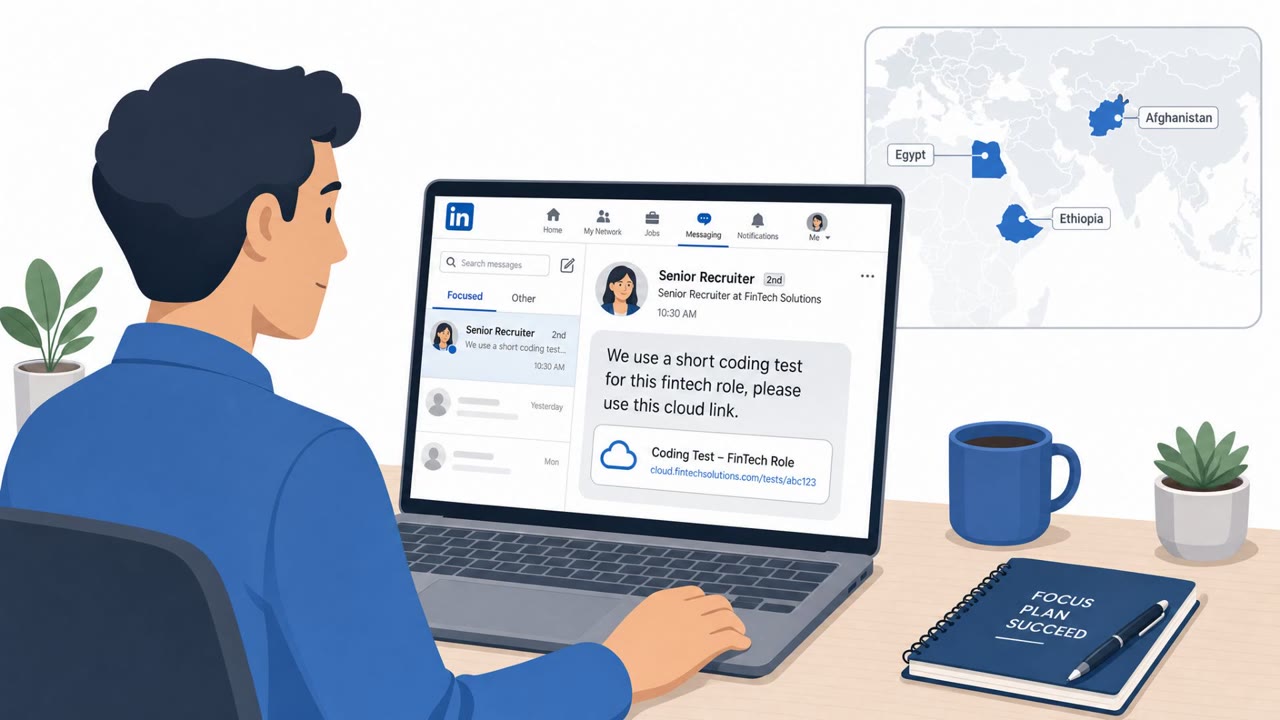
This weekly threat bulletin includes real-world campaigns where attackers impersonate recruiters and use fake hiring steps to trick people into running malicious files. One campaign uses fake LinkedIn coding tests delivered via cloud links, and another uses fake job interviews with trojanized macOS…

September 7, 2026
Fake CAPTCHA Trick Tied to Berlin Gov Data Leak

Fake CAPTCHA Trick Tied to Berlin Gov Data Leak

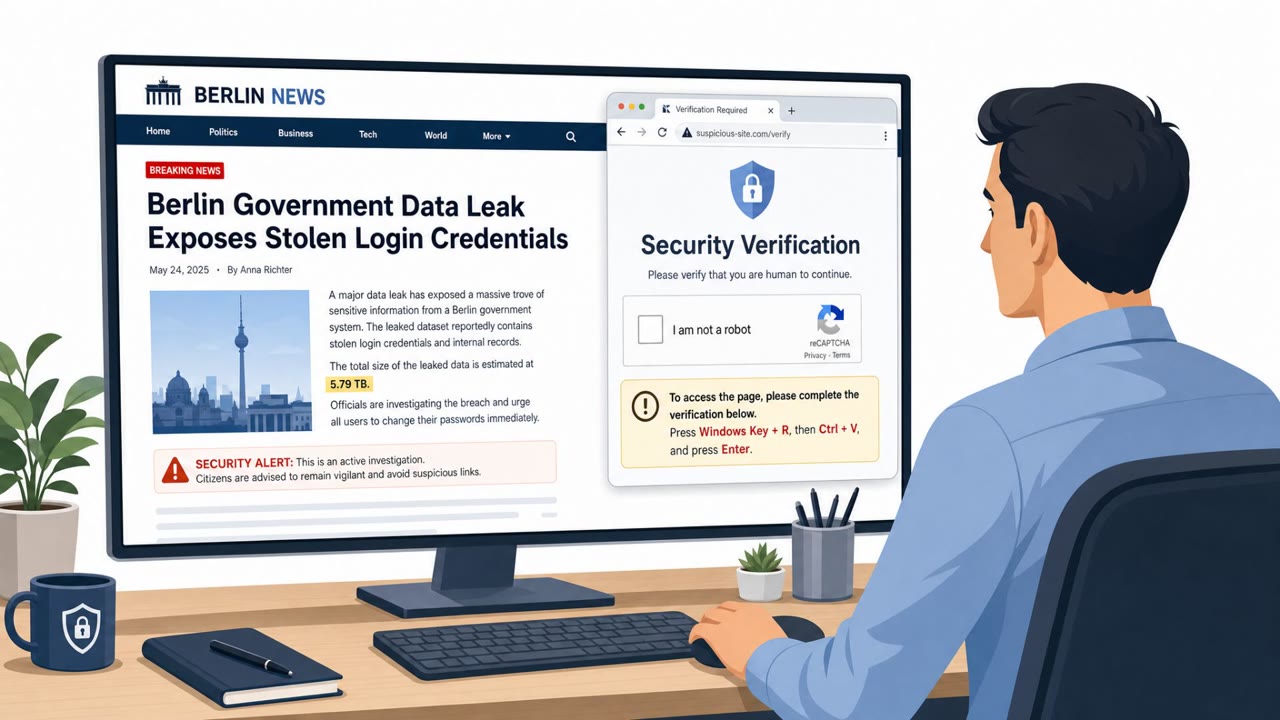
Berlin authorities are investigating a new release of stolen government data, including published login credentials. Germany’s cyber agency also warned of a related campaign where attackers compromise websites and use fake CAPTCHA pages to trick visitors into running malicious commands, enabling…

September 7, 2026
RMM Phish Uses Tax & UPS Lures in 46 Countries

RMM Phish Uses Tax & UPS Lures in 46 Countries

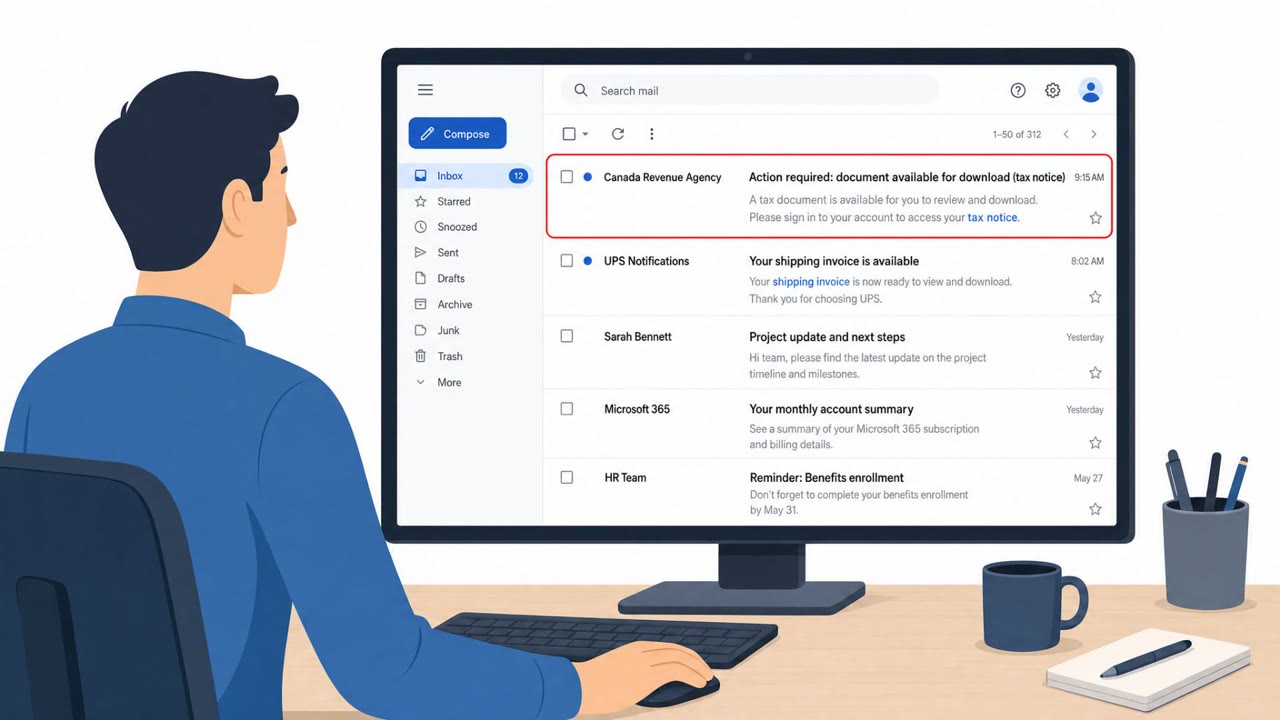
Researchers describe a real phishing operation that tricks people into installing legitimate remote monitoring and management (RMM) tools so attackers can remotely control devices. The campaign uses familiar-looking documents (tax forms, UPS/shipping notices, Adobe PDFs, invoices, and Social…

September 3, 2026
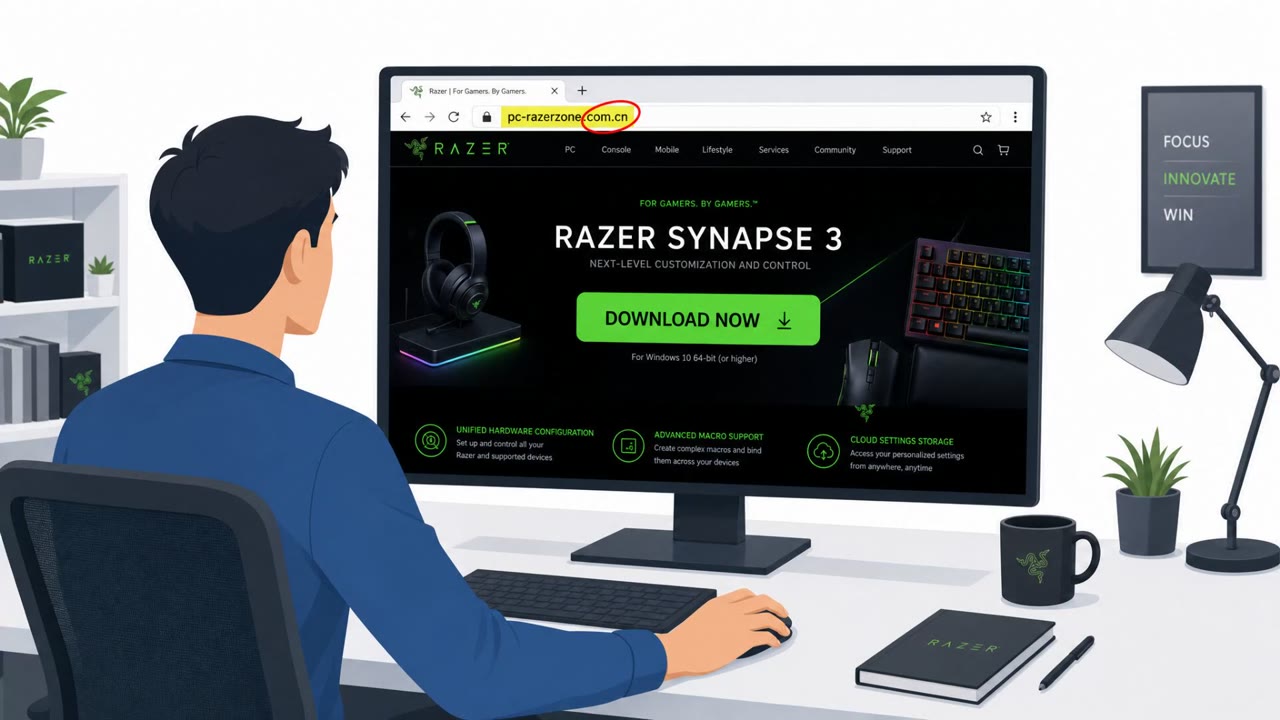
Fake Download Sites Push Trojanized Installers

Fake Download Sites Push Trojanized Installers

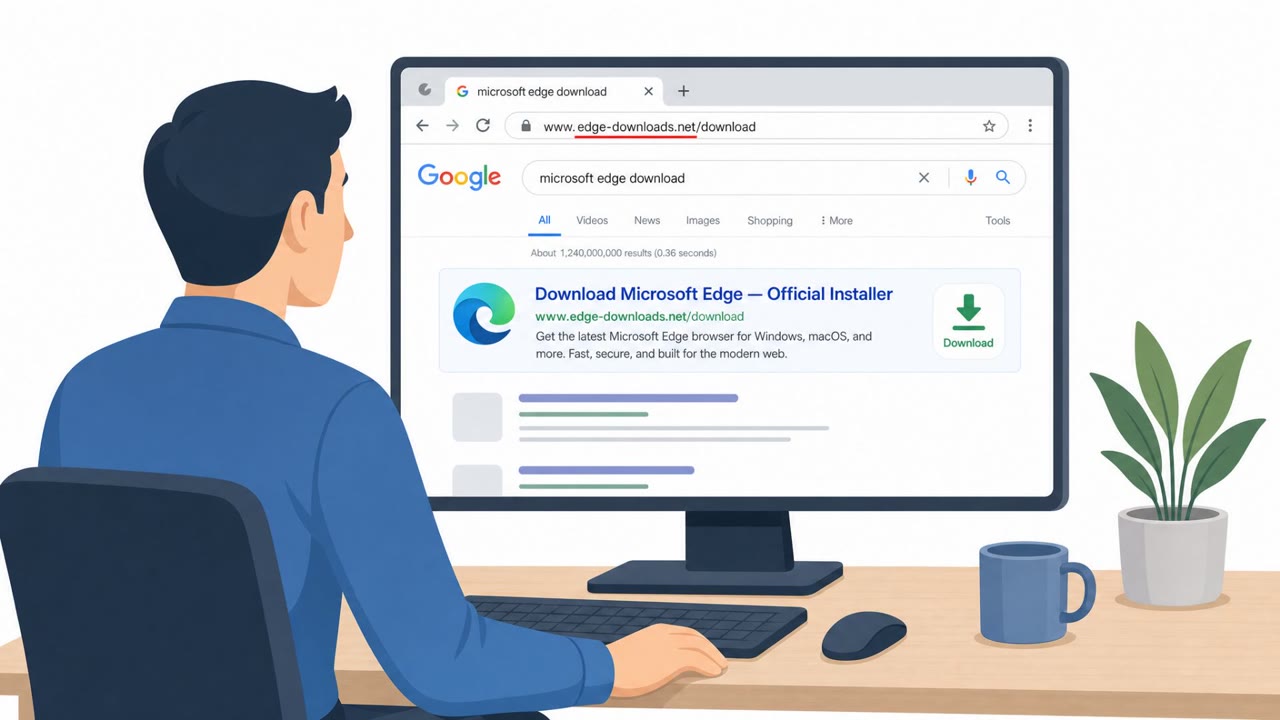
Microsoft reports a real campaign where attackers set up look-alike software download websites (impersonating known brands) to trick employees into installing trojanized “installers.” Once run, the malware persists on the device, weakens security settings, and connects to attacker-controlled…

September 3, 2026
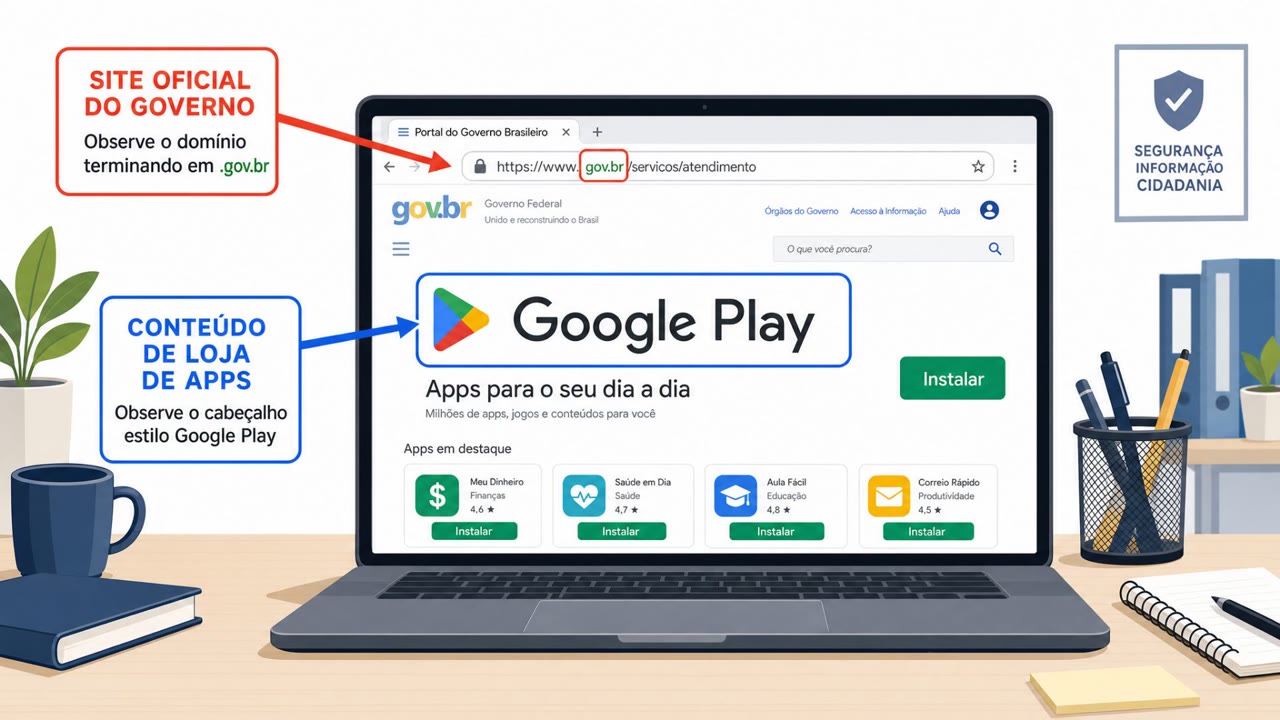
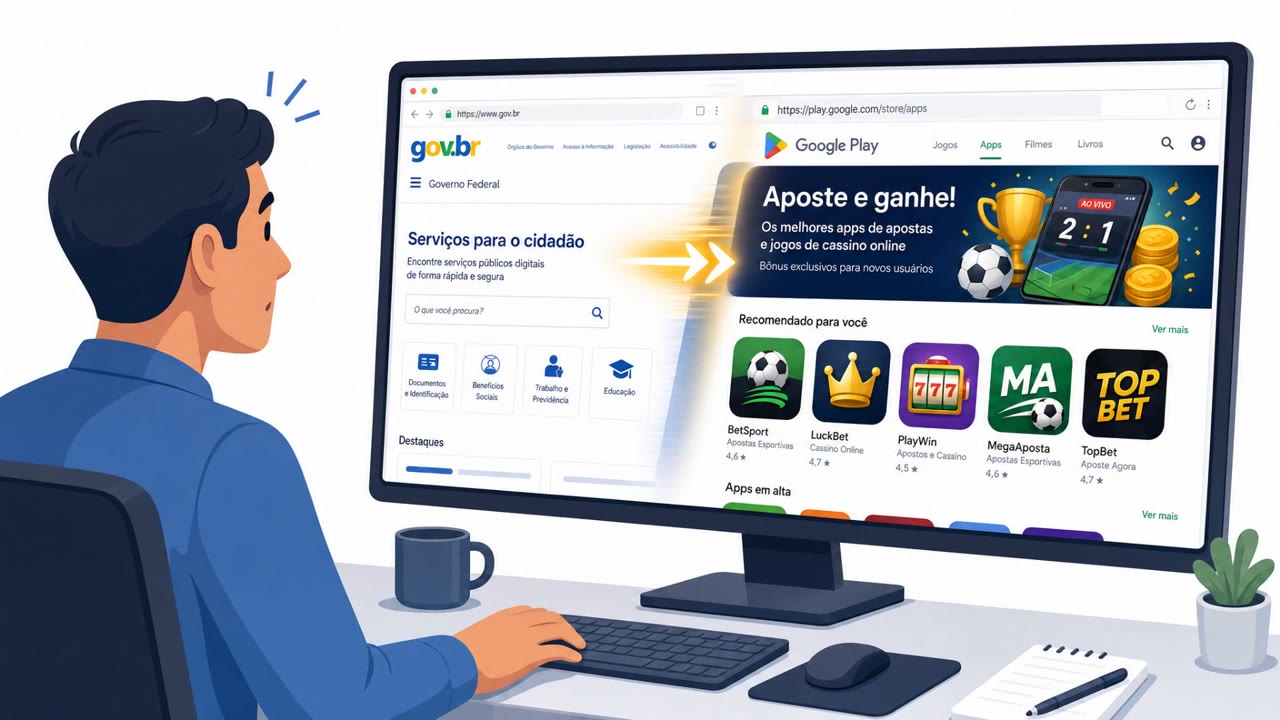
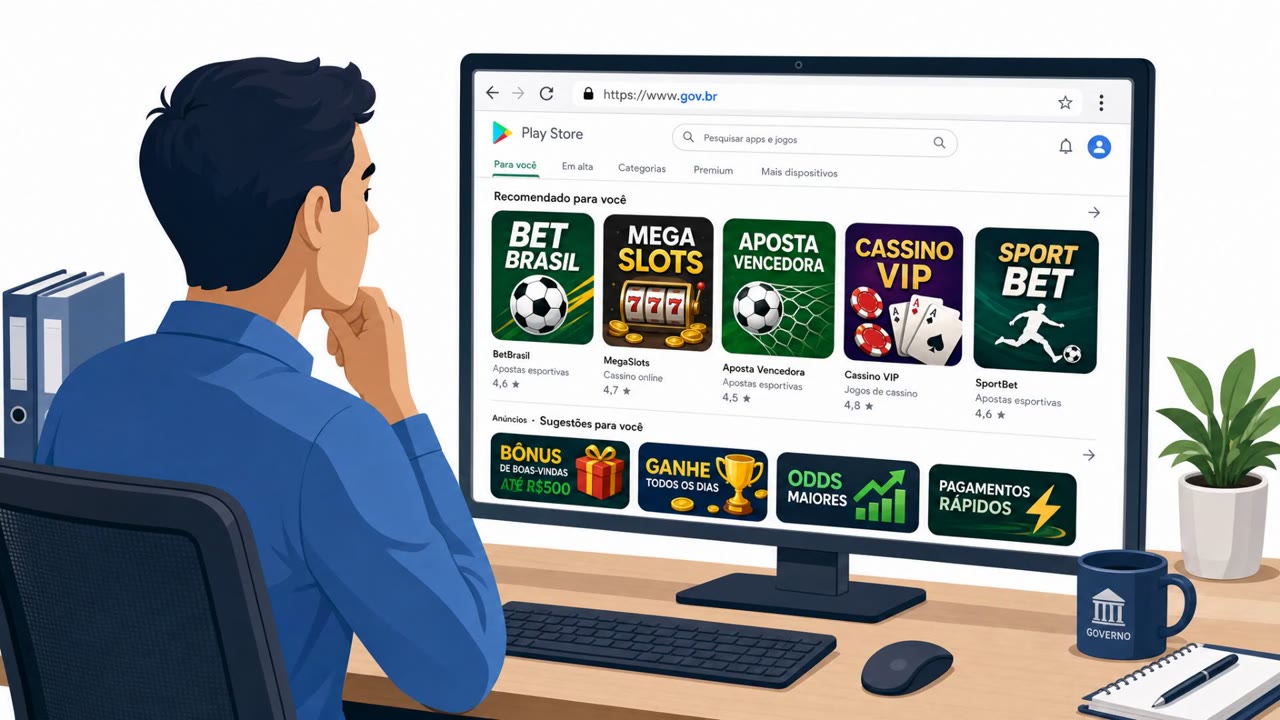
Gov Sites Redirected to Fake App Stores for Betting

Gov Sites Redirected to Fake App Stores for Betting

Researchers say compromised Brazilian government and education websites were altered with malicious Apache modules that silently rerouted visitors to attacker-controlled pages. The fake pages impersonated trusted app stores (Google Play, Microsoft Store, Amazon) to funnel people toward online…

September 2, 2026
Gambling Goblin Hijacks Gov Sites for Phishing

Gambling Goblin Hijacks Gov Sites for Phishing

Researchers say a Chinese-speaking cybercrime group compromised Brazilian government and education websites and used them as “trusted” entry points to quietly redirect visitors to attacker-run phishing pages. The fake pages impersonated well-known app stores (Google Play, Microsoft Store, Amazon)…

September 2, 2026
Gov Websites Hijacked to Push Fake App Stores

Gov Websites Hijacked to Push Fake App Stores

Check Point Research reports a real campaign where a Chinese-speaking actor compromised Brazilian government and education websites and used them as stealthy “front doors” to redirect visitors to attacker-controlled phishing pages. The fake pages impersonate trusted app stores (Google Play,…

September 2, 2026
Fake Download Sites Push Malware Installers

Fake Download Sites Push Malware Installers

Microsoft reports an active campaign where attackers set up counterfeit software download pages that mimic well-known brands and trick users into installing malware. Victims visit a look-alike vendor site, click “Download now,” then run a bundled installer that drops persistent malware and connects…

September 2, 2026
Mirage2FA Phishing Kit Steals Microsoft 365 Sessions

Mirage2FA Phishing Kit Steals Microsoft 365 Sessions

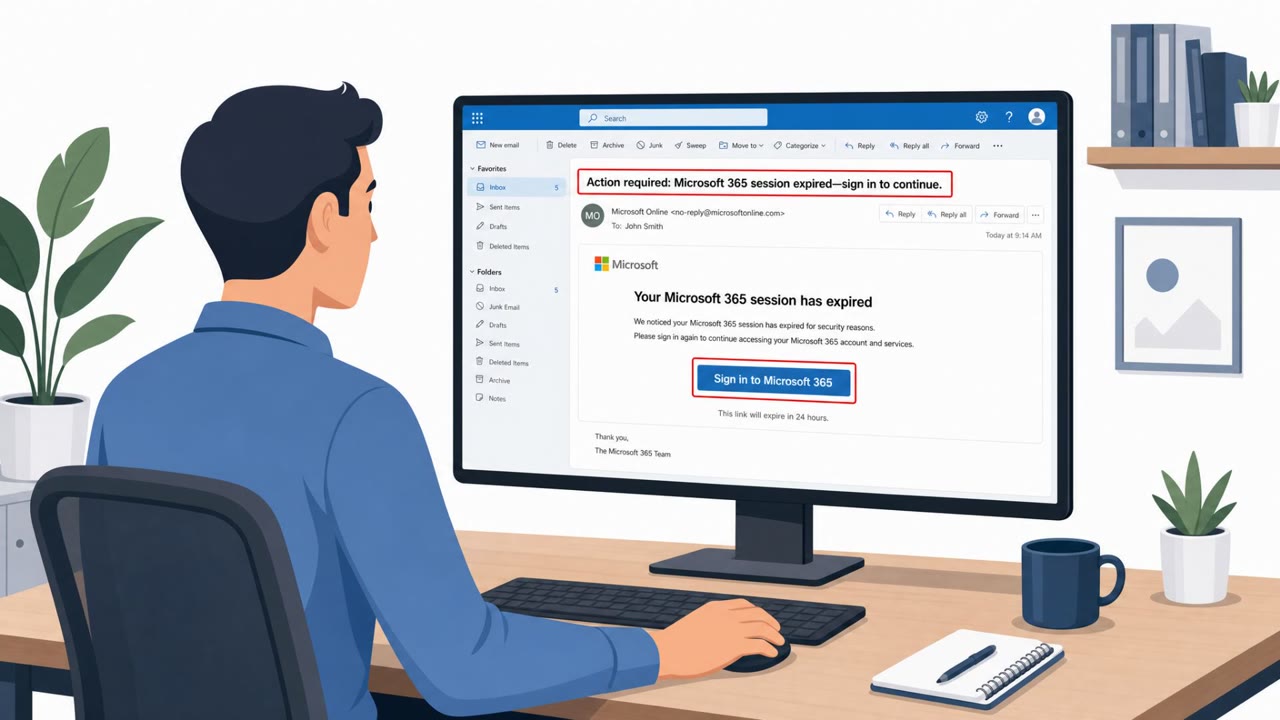
A phishing-as-a-service toolkit called Mirage2FA has been targeting organizations by abusing real Microsoft 365 login pages through a man-in-the-middle proxy. The attackers capture usernames, passwords, and live two-factor authentication codes, then take over the user’s session using stolen session…

August 31, 2026
Fake Think Tank Pushed Pro‑Russia Content Using AI

Fake Think Tank Pushed Pro‑Russia Content Using AI

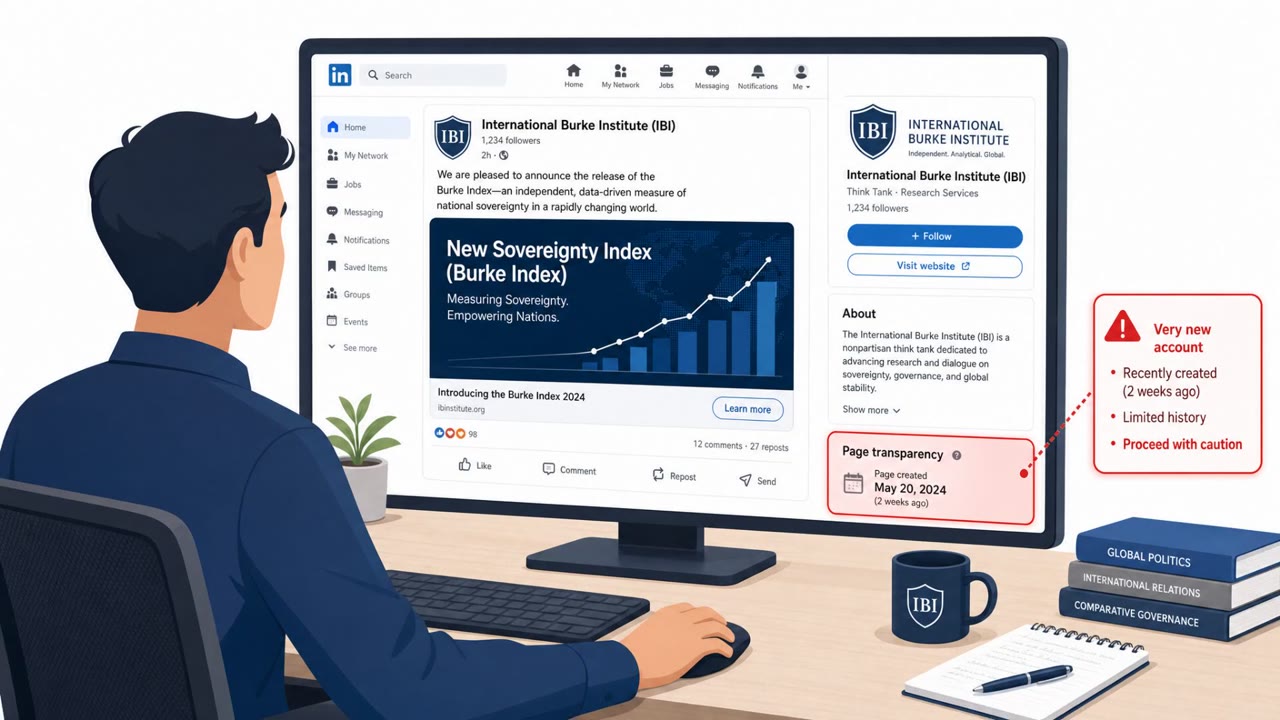
OpenAI says it removed Russia-linked ChatGPT accounts used to support a covert influence campaign promoting a fake think tank brand called the “International Burke Institute” (IBI). The operators used AI mainly to create and translate social media posts that looked credible and drove people to an…

August 27, 2026
Interpol Busts Romance, Crypto & Sextortion Rings

Interpol Busts Romance, Crypto & Sextortion Rings

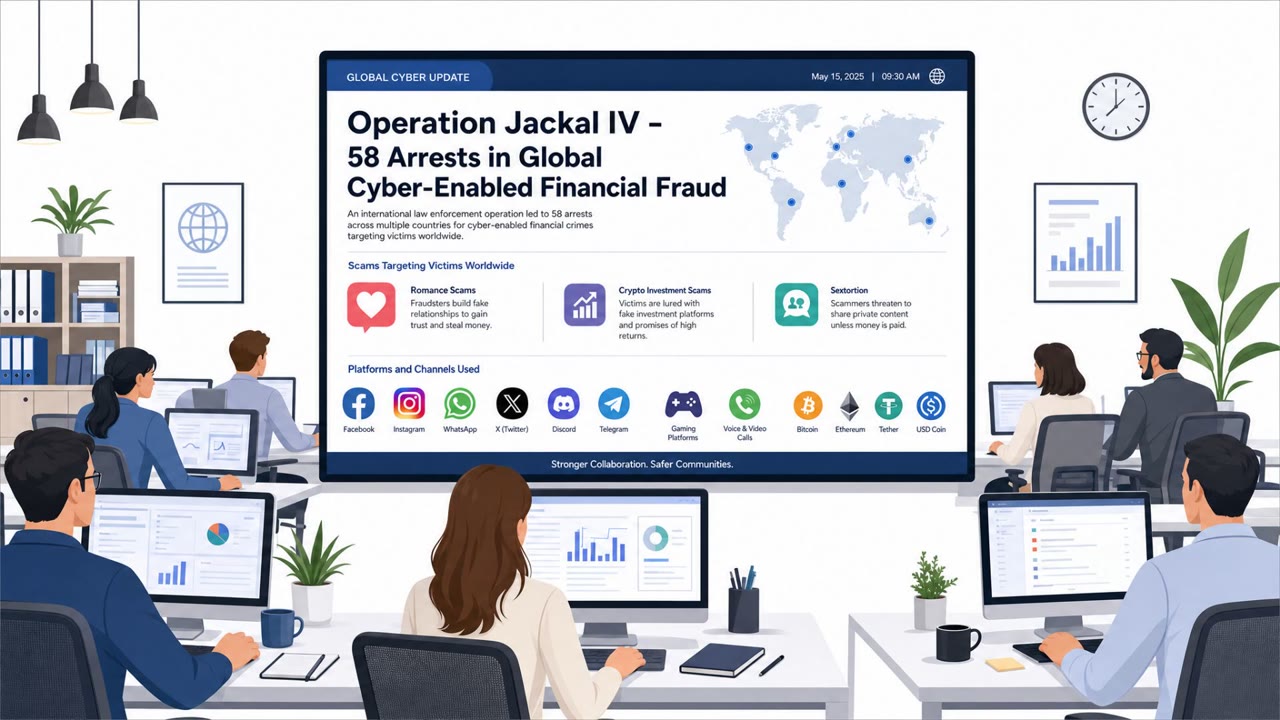
Interpol said an eight-month operation across 22 countries led to 58 arrests tied to cyber-enabled financial fraud, including romance scams, cryptocurrency/investment scams, and business email compromise. Authorities described how scammers build trust with victims (including minors) on social and…

August 25, 2026
Fake Minecraft Clients Push WeedHack Malware

Fake Minecraft Clients Push WeedHack Malware

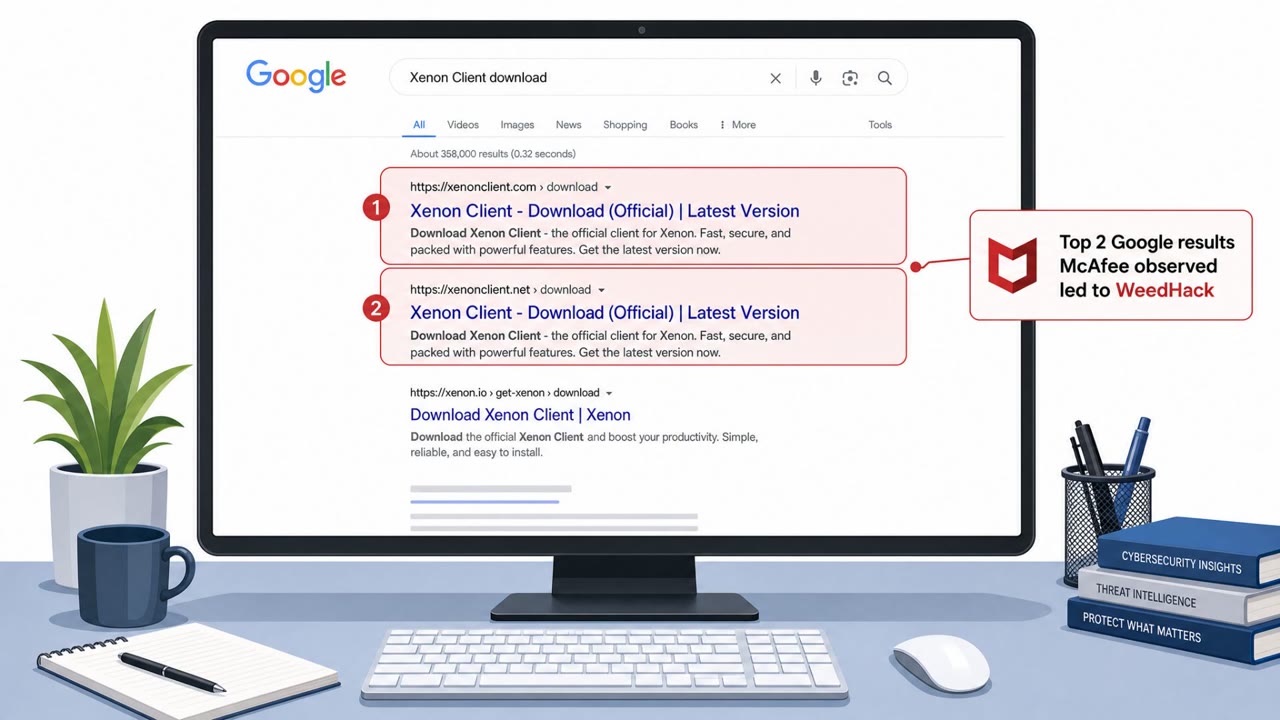
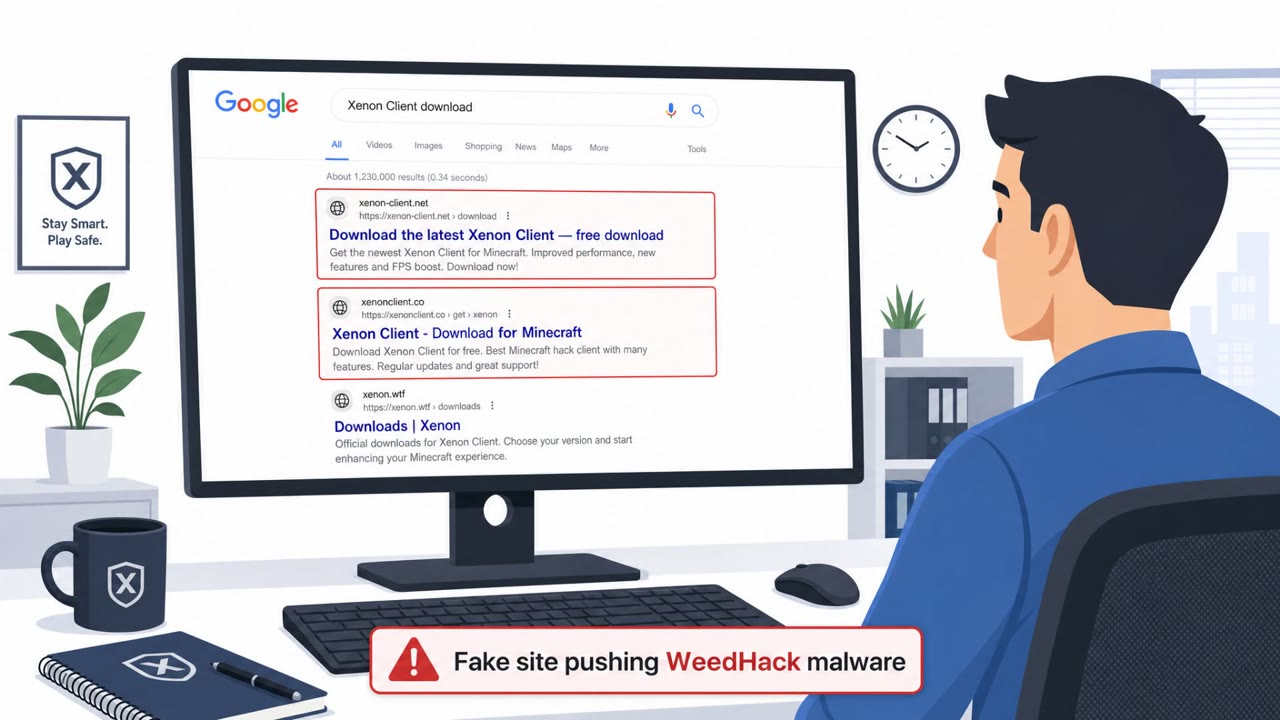
Attackers are tricking Minecraft players into downloading malware by impersonating popular Minecraft clients and resellers in Google search results. Even after the campaign’s command-and-control infrastructure was taken down, the operation continued by shifting distribution to common file-hosting…

August 25, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo