Recent Healthcare Cyber Attacks

Page 2 of 6
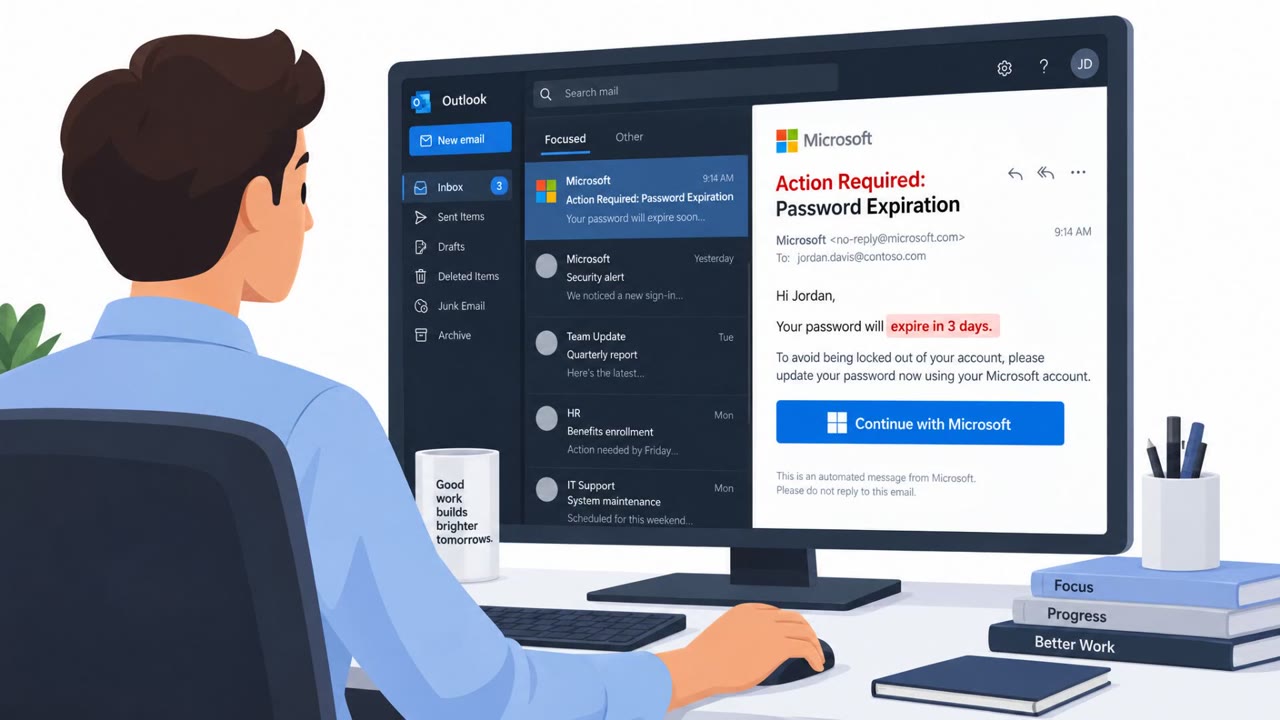
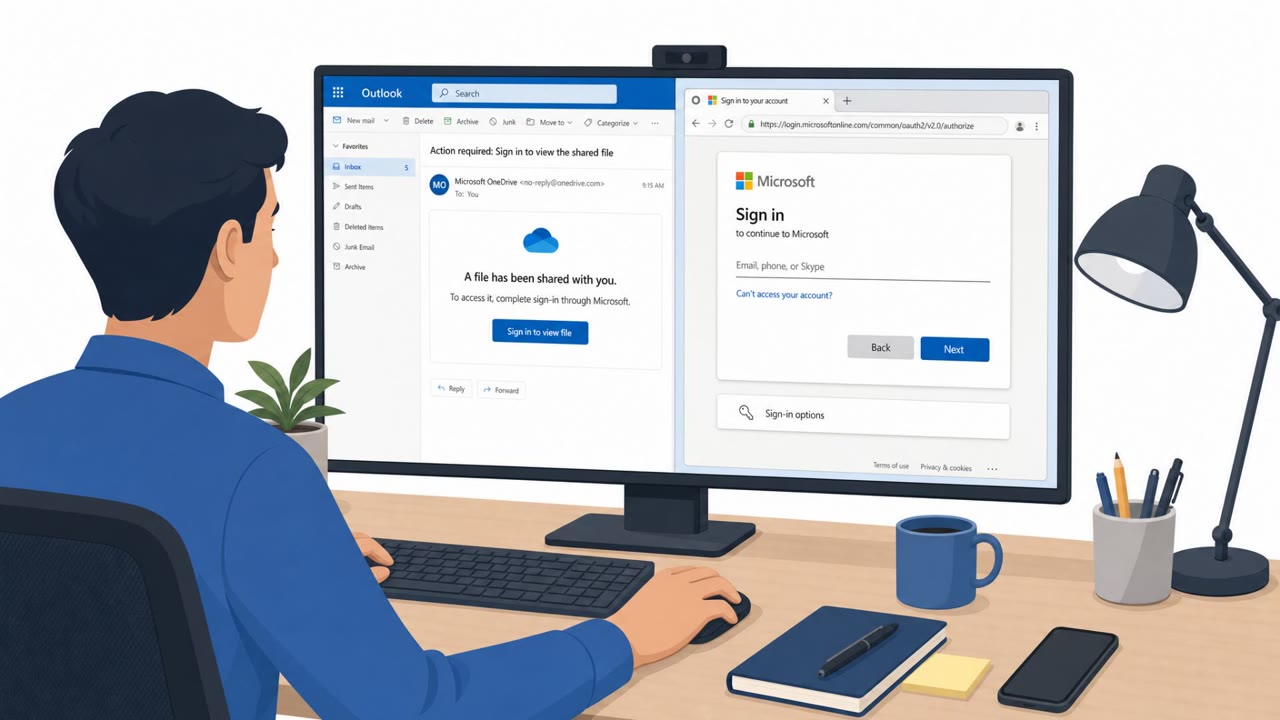
EvilTokens Used Device-Code Phish + AI for BEC

EvilTokens Used Device-Code Phish + AI for BEC

Microsoft disrupted EvilTokens, a phishing-as-a-service operation linked to thousands of compromised Microsoft 365 inboxes. The group used “device code” phishing to steal valid session tokens (not passwords) and then used an AI chatbot to scan mailboxes and help craft business email compromise…

September 22, 2026
Device-Code Phishing Service Hit After 12K Breaches

Device-Code Phishing Service Hit After 12K Breaches

Microsoft and partners disrupted “EvilTokens,” a phishing-as-a-service platform Microsoft links to over 12,000 compromised inboxes across more than 10,000 organizations. The service used deceptive emails to trick people into pasting a “device code” into Microsoft’s real sign-in page…

September 22, 2026
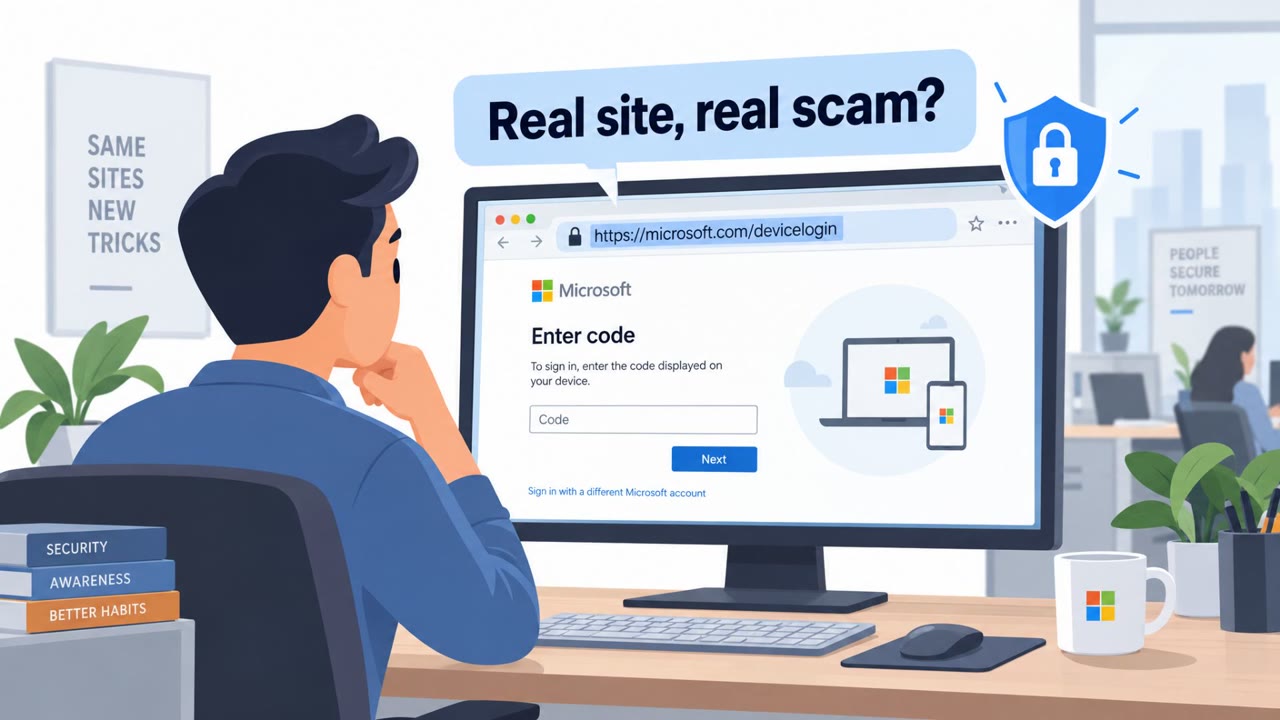
EvilTokens Uses Device Codes to Bypass MFA

EvilTokens Uses Device Codes to Bypass MFA

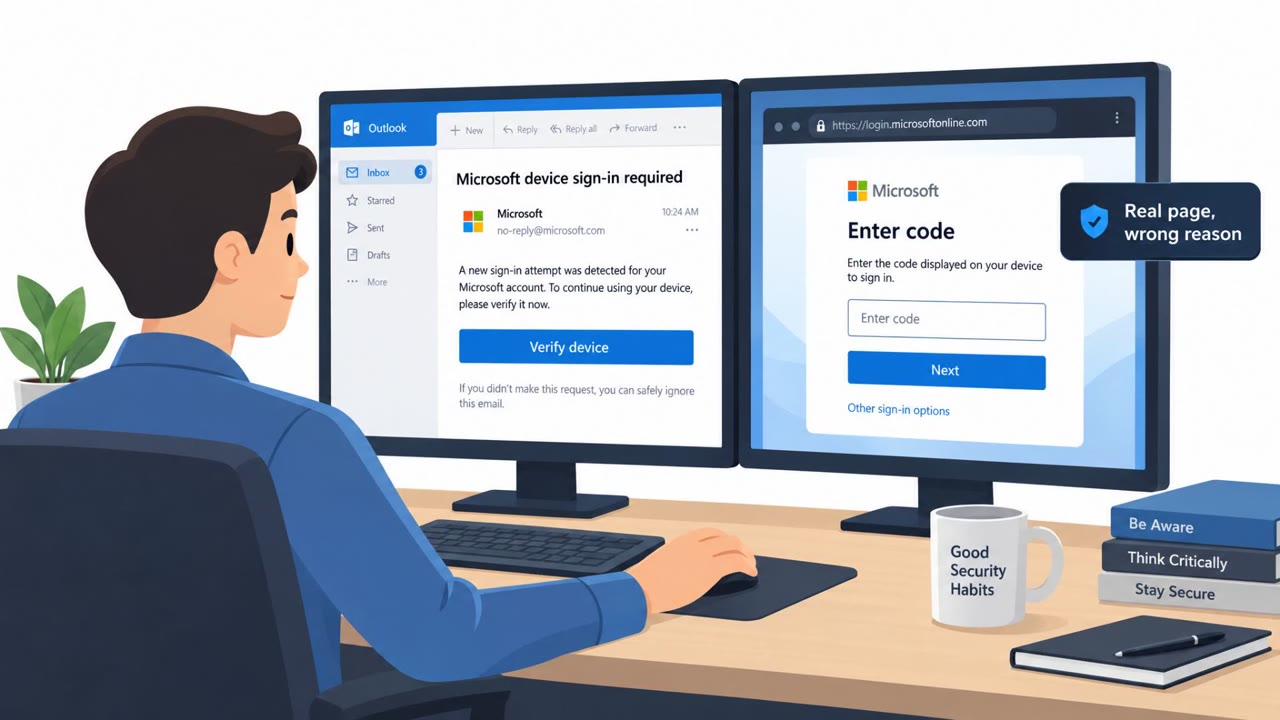
Microsoft reports that the EvilTokens phishing-as-a-service platform helped criminals compromise thousands of organizations by tricking users into completing a legitimate Microsoft “device code” login. The lure drives victims to enter a short code at microsoft.com/devicelogin, which unknowingly…

September 22, 2026
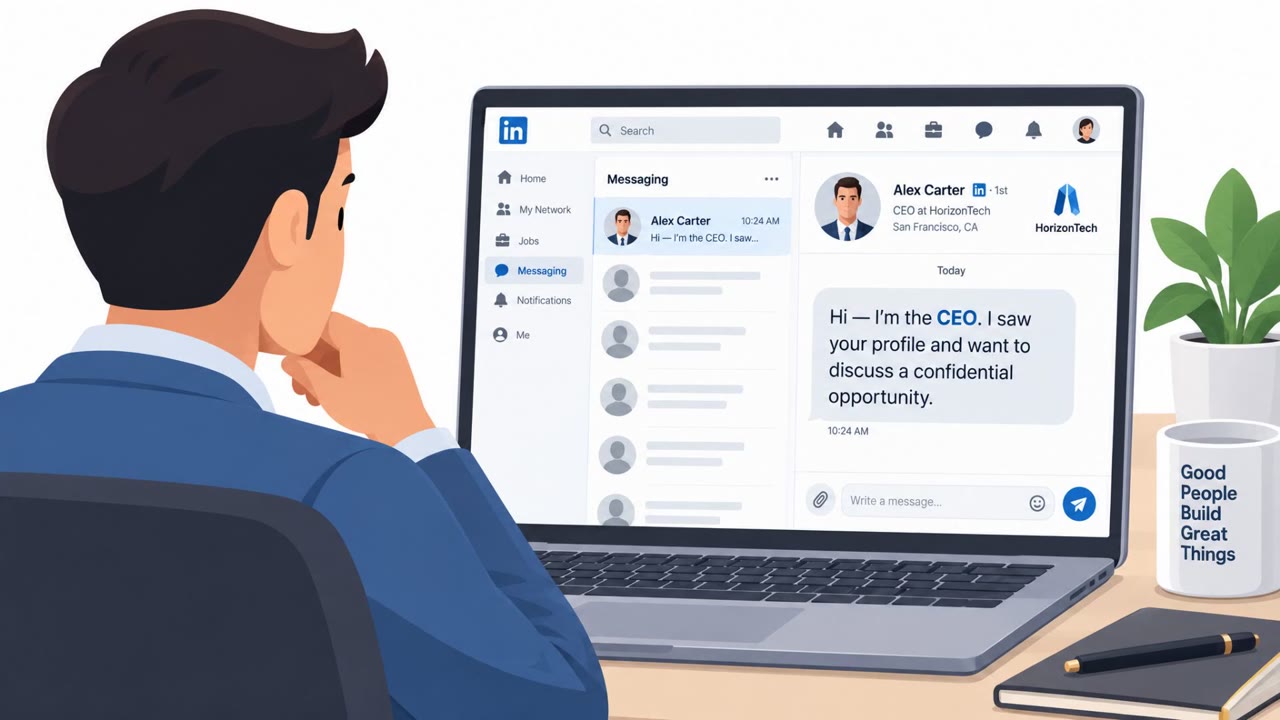
Fake CEOs on LinkedIn Fuel IP & Data Theft

Fake CEOs on LinkedIn Fuel IP & Data Theft

A CSC report describes real-world scams where criminals impersonate executives and brands online to steal personal or payment information. Examples include fake CEOs contacting people on LinkedIn with bogus job offers, and lookalike “FIFA” domains used for fake ticket sales, travel offers, and…

September 22, 2026
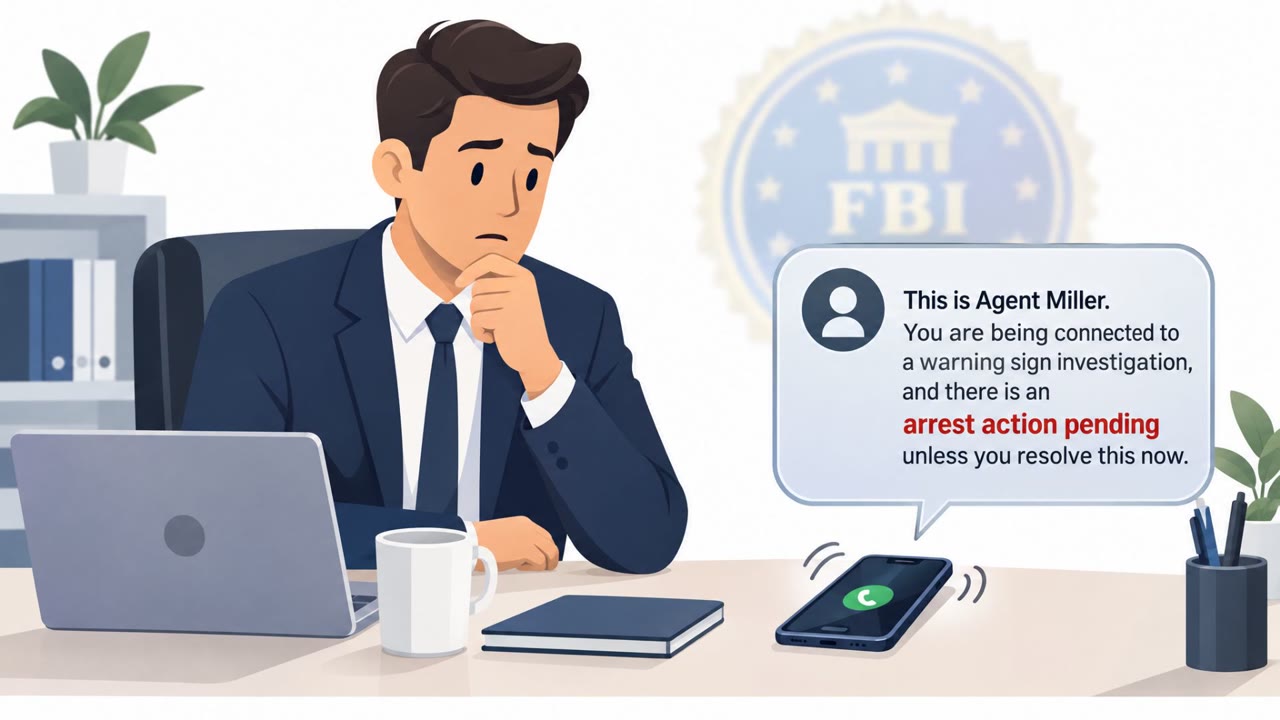
Fake Cops Threaten Arrest to Force Payments

Fake Cops Threaten Arrest to Force Payments

The FBI warns about phone scams where callers impersonate police or federal agents and threaten arrest unless the victim pays immediately. The scams use pressure tactics (keeping victims on the phone, urging secrecy) and push hard-to-trace payments like prepaid cards, crypto, wire transfers, or…

September 21, 2026
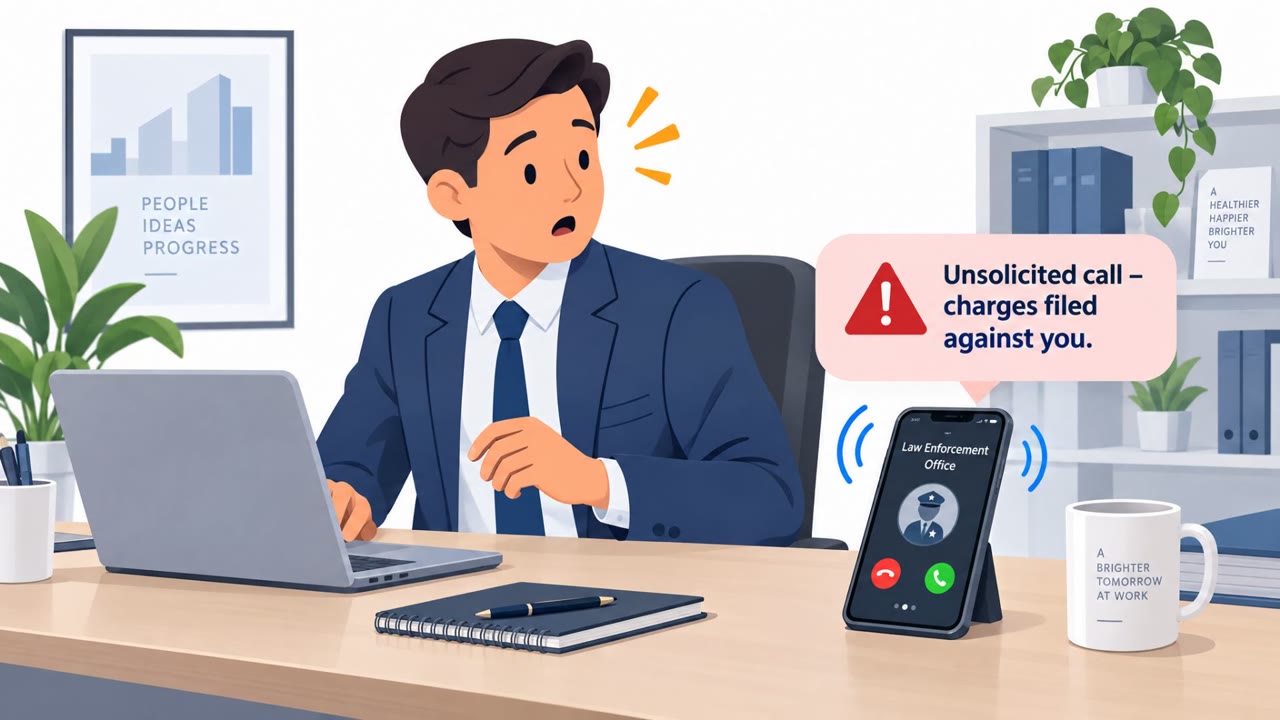
FBI: Fake Cops Swindle $1.6B via Threat Calls

FBI: Fake Cops Swindle $1.6B via Threat Calls

The FBI says scammers posing as law enforcement or government officials stole over $1.6B since January 2025, mainly by calling victims and threatening arrest, fines, or legal trouble unless they pay. Variants include jury-duty threats, targeted calls to medical professionals about license issues,…

September 18, 2026
AI Voice Agents Fuel New Phone Fraud Wave

AI Voice Agents Fuel New Phone Fraud Wave

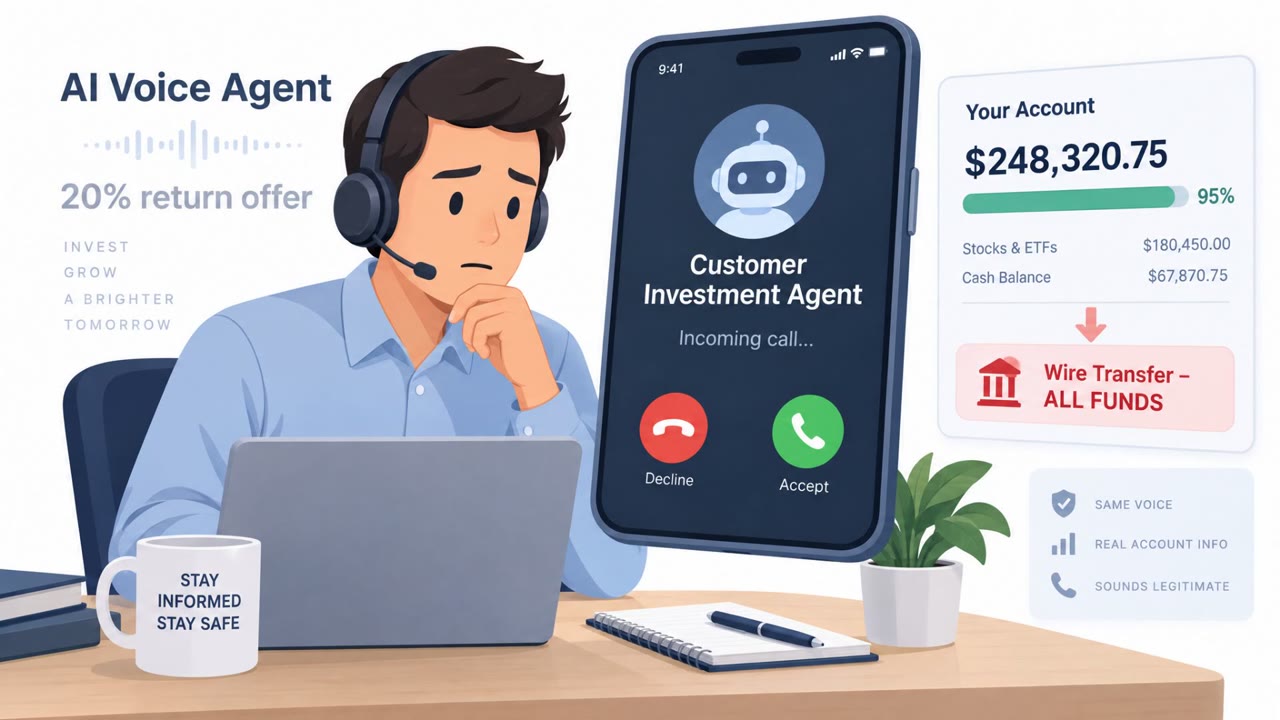
The article describes real-world cases where AI agents interacted with banks and contact centers, including an investment agent that nearly wired out a customer’s funds after encountering a scam offer. It also highlights AI voice agents calling enterprises at high volume, sometimes lying about…

September 18, 2026
Fake Helpdesk Passkey Setup Steals Cloud Access

Fake Helpdesk Passkey Setup Steals Cloud Access

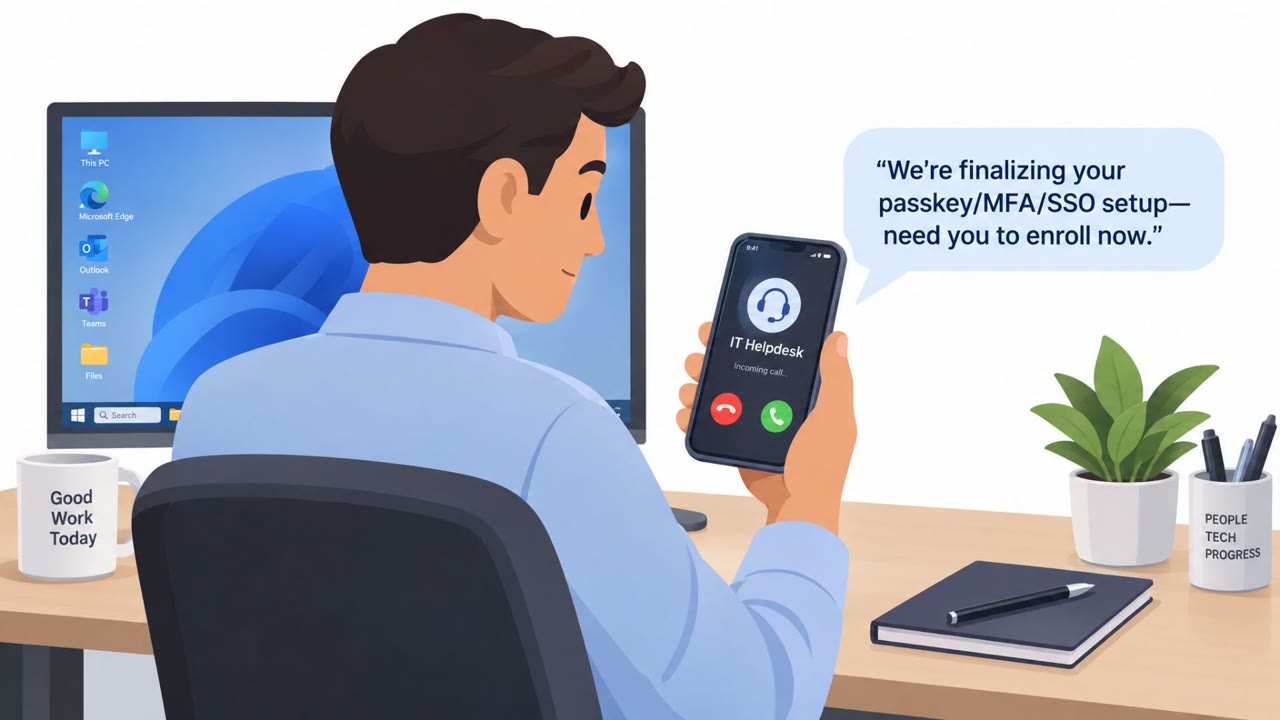
The article describes real intrusions where attackers impersonate a company helpdesk and lure employees into "passkey, MFA, or SSO setup" steps. Victims are sent links via text (often to personal phones), leading to account takeover through adversary-in-the-middle phishing or device-code…

September 16, 2026
N0va Phishkit Uses Trusted Apps to Steal SSO Access

N0va Phishkit Uses Trusted Apps to Steal SSO Access

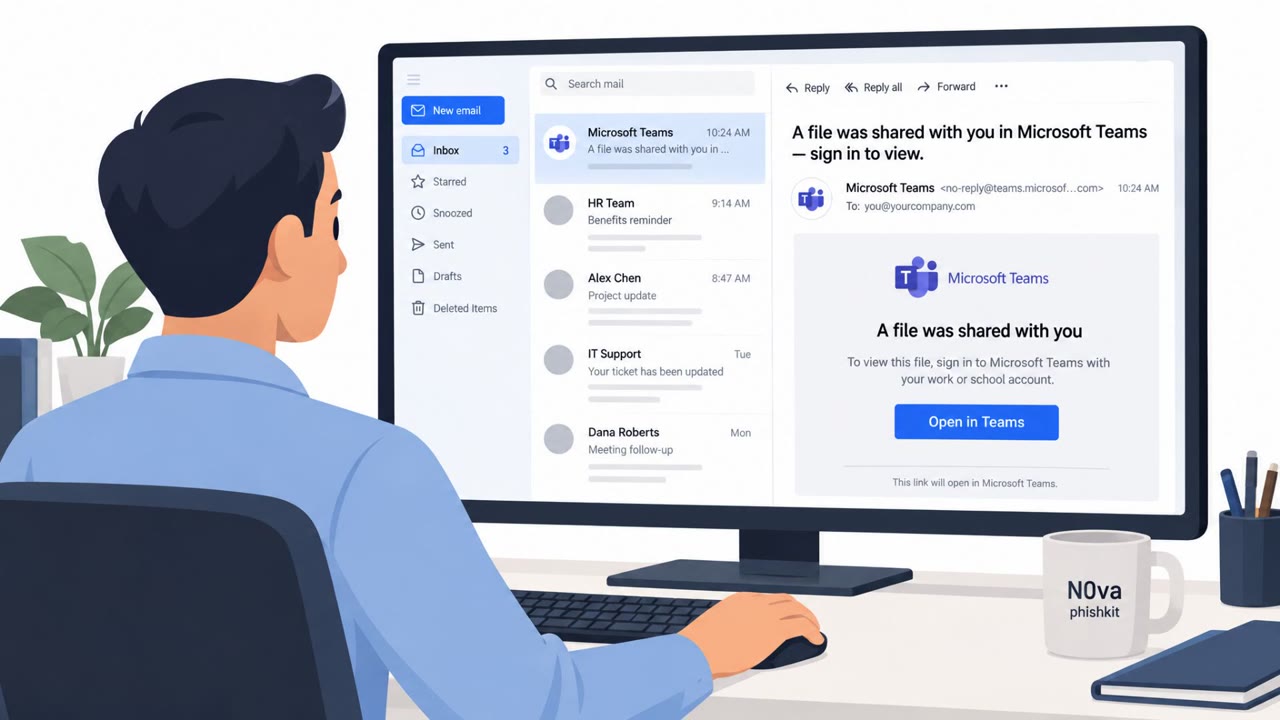
A phishing kit dubbed N0va is targeting organizations in North America and Europe by impersonating familiar business services (like Microsoft Teams/SharePoint and DocuSign) and pushing victims through legitimate sign-in flows. By capturing authentication tokens rather than dropping obvious malware,…

September 16, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

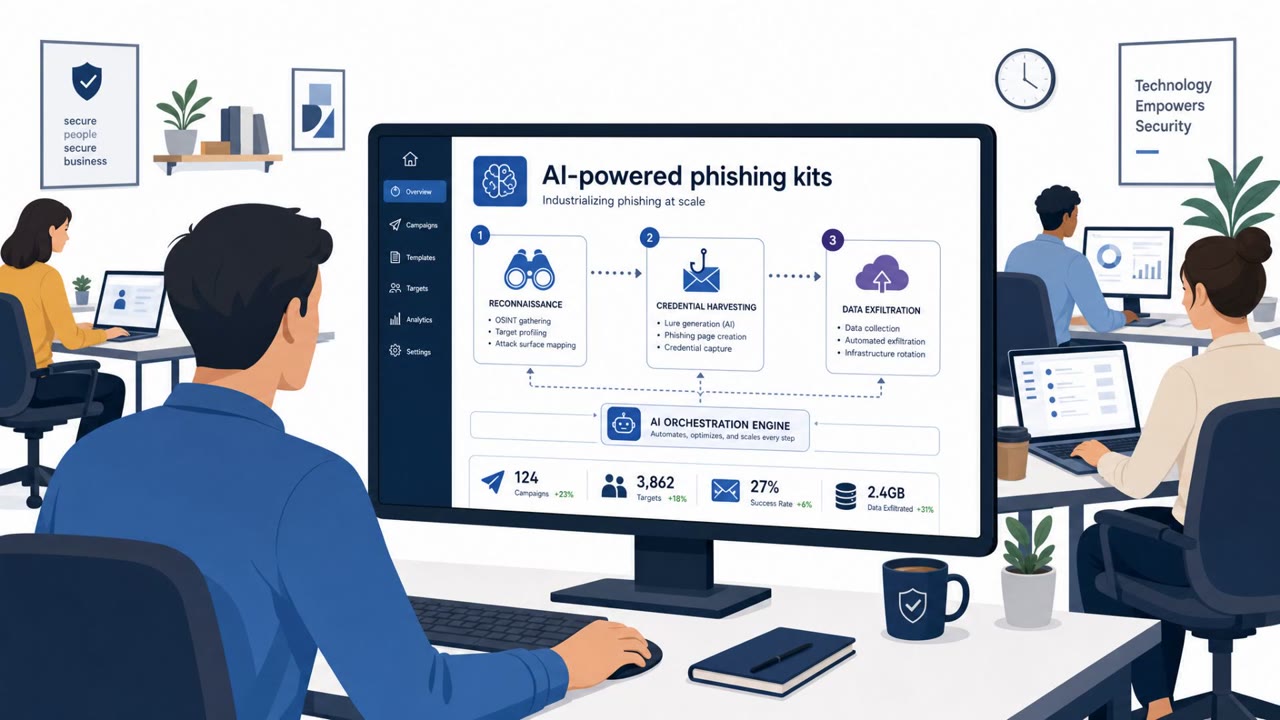
Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
N0va Device-Code Phish Steals Microsoft Sessions

N0va Device-Code Phish Steals Microsoft Sessions

Researchers reported a real phishing operation (“N0va” phishkit) that tricks people into signing into Microsoft through a legitimate Microsoft page, but for an attacker-started session. Victims can complete MFA and still grant the attacker access and refresh tokens, letting the attacker operate as…

September 11, 2026
Fraudsters Can Remotely “Brick” Phones for $3

Fraudsters Can Remotely “Brick” Phones for $3

Researchers showed that attackers can abuse mobile carriers’ “lost/stolen phone” reporting process to get devices blocked from the cellular network, even when the devices were never lost. With only a prepaid account and a target device’s IMEI number, blocking can cost just a few dollars and take…

September 11, 2026
Fake Title IX Claims Push Zoho Assist RAT

Fake Title IX Claims Push Zoho Assist RAT

A real phishing campaign is using fabricated sexual misconduct (Title IX-style) allegations to pressure university staff into clicking a link and installing Zoho Assist, a legitimate remote-access tool being abused as malware. The emails impersonate university leaders and route victims through a…

September 10, 2026
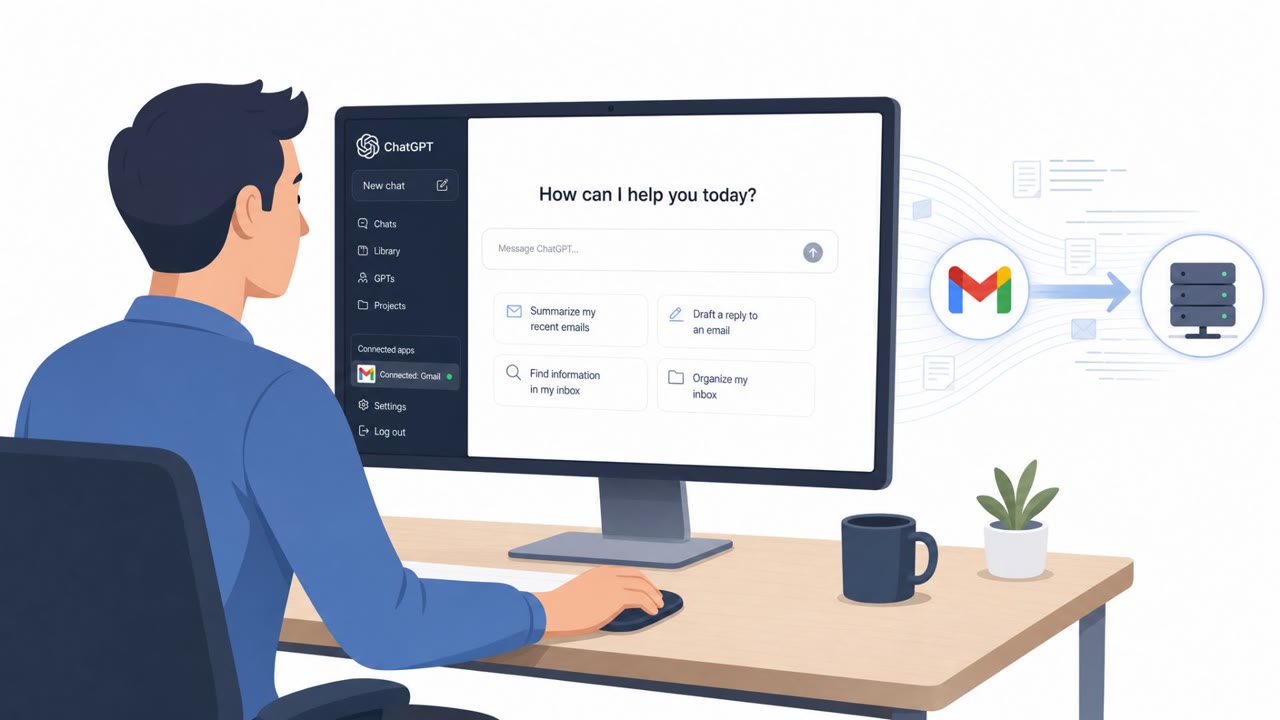
Hidden Prompts Hijack ChatGPT Connected Apps

Hidden Prompts Hijack ChatGPT Connected Apps

Check Point demonstrated a prompt-injection technique where a hidden instruction inside ChatGPT can make a user’s session quietly run extra tasks using the session’s existing permissions. In the proof of concept, the victim’s ChatGPT (with Gmail connected) pulled email data and relayed it to an…

September 9, 2026
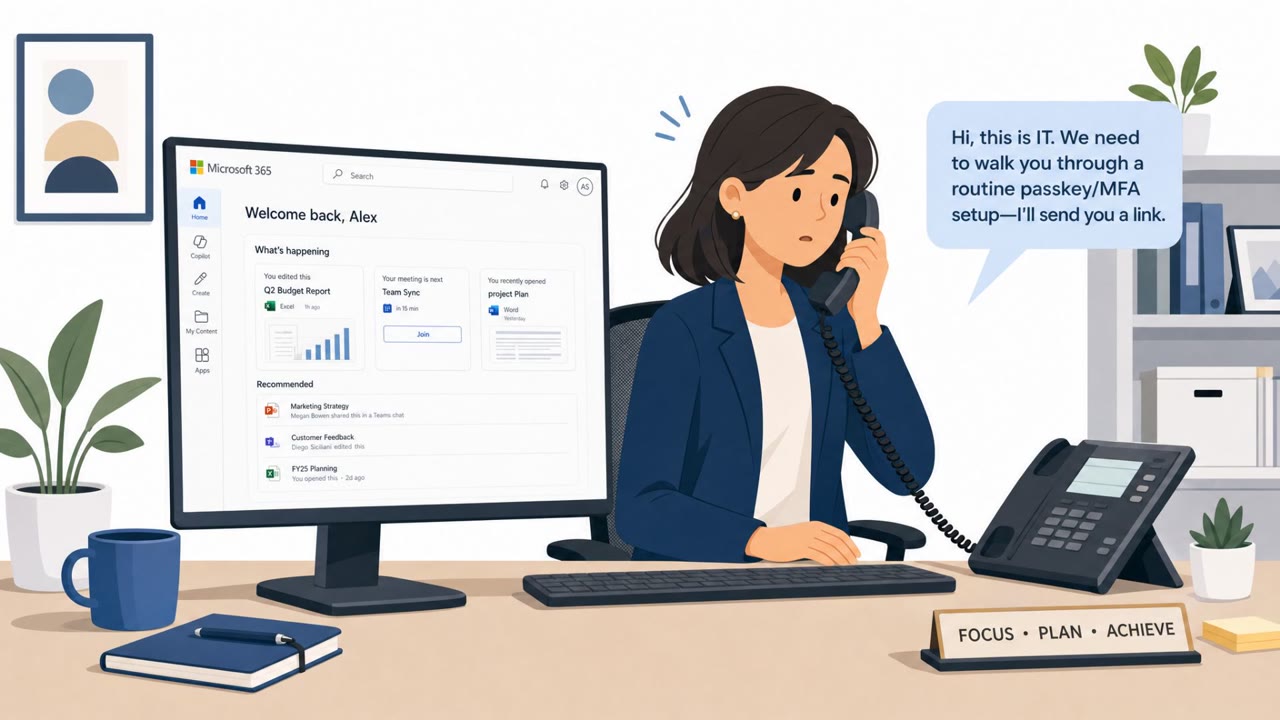
Fake IT Help-Desk Calls Steal M365 Sessions

Fake IT Help-Desk Calls Steal M365 Sessions

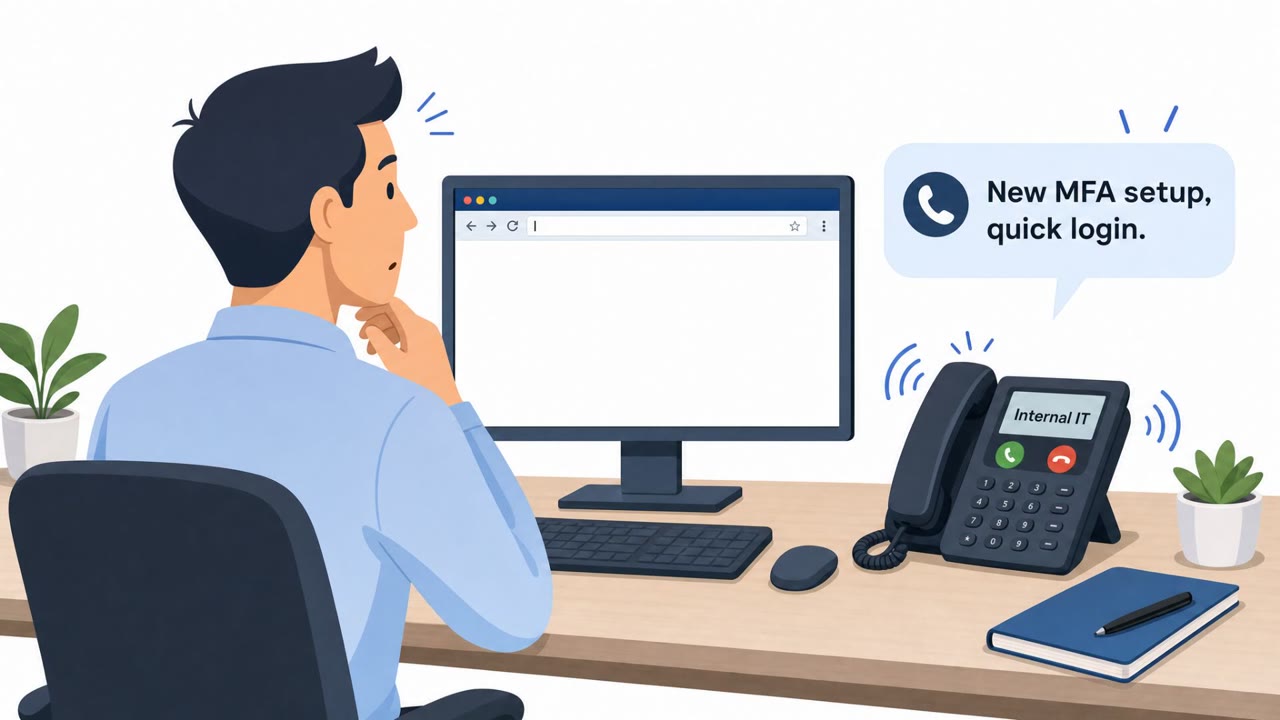
Arctic Wolf reports a wave of phone-based social engineering where attackers pose as internal IT, guide executives through “routine” MFA/passkey setup, and then send a company-branded login link that steals Microsoft 365 credentials and session tokens. Once inside, attackers methodically inventory…

September 8, 2026
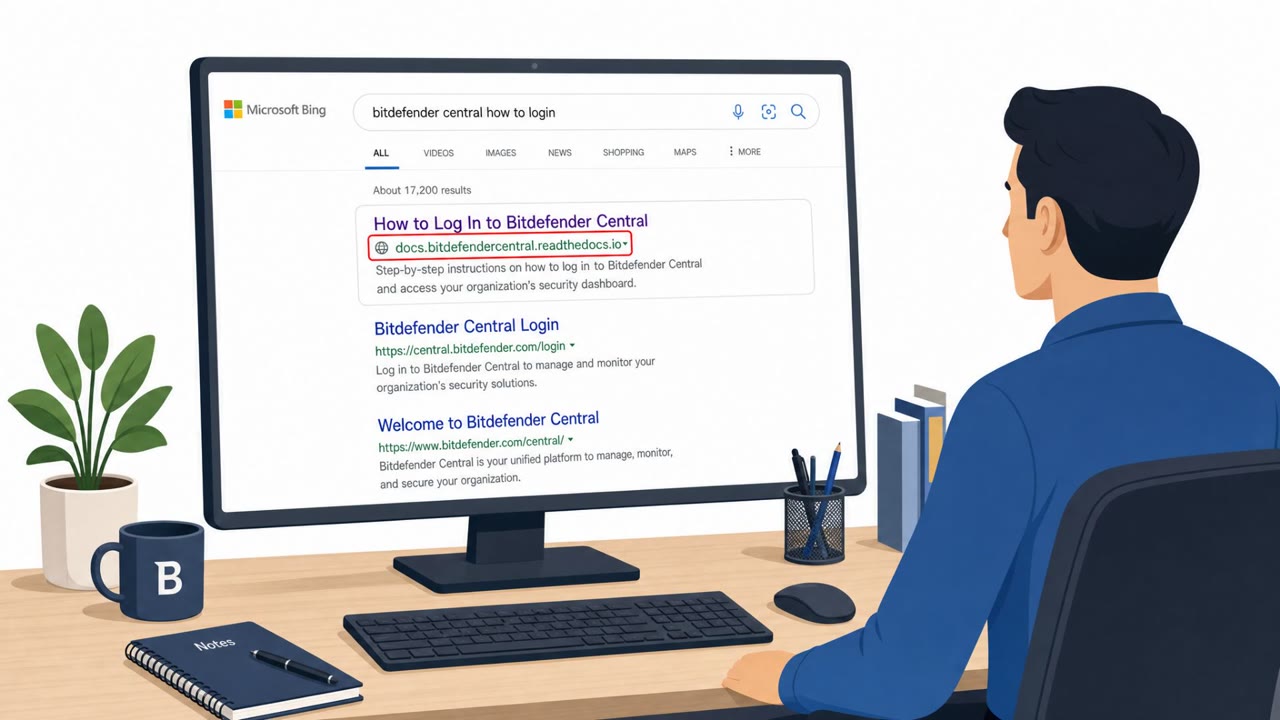
BengalSEO Tricks Bing Users Into Malware & Scam Calls

BengalSEO Tricks Bing Users Into Malware & Scam Calls

Researchers uncovered a long-running “SEO poisoning” operation that manipulates Bing search results to push people onto fake support and activation pages. Victims are steered through a chain of redirects to either download a malware-laced ZIP (MayaBot) or be pressured into calling a fake…

September 8, 2026
Fake IT Help Desk Calls Steal M365 Data, Extort

Fake IT Help Desk Calls Steal M365 Data, Extort

Threat actors are calling employees while pretending to be internal IT/help desk staff and directing them to fake Microsoft 365 login pages. The goal is to capture credentials and MFA approvals, steal session tokens, then access and exfiltrate data from SaaS services like SharePoint, OneDrive, and…

September 7, 2026
Fake CAPTCHA Trick Tied to Berlin Gov Data Leak

Fake CAPTCHA Trick Tied to Berlin Gov Data Leak

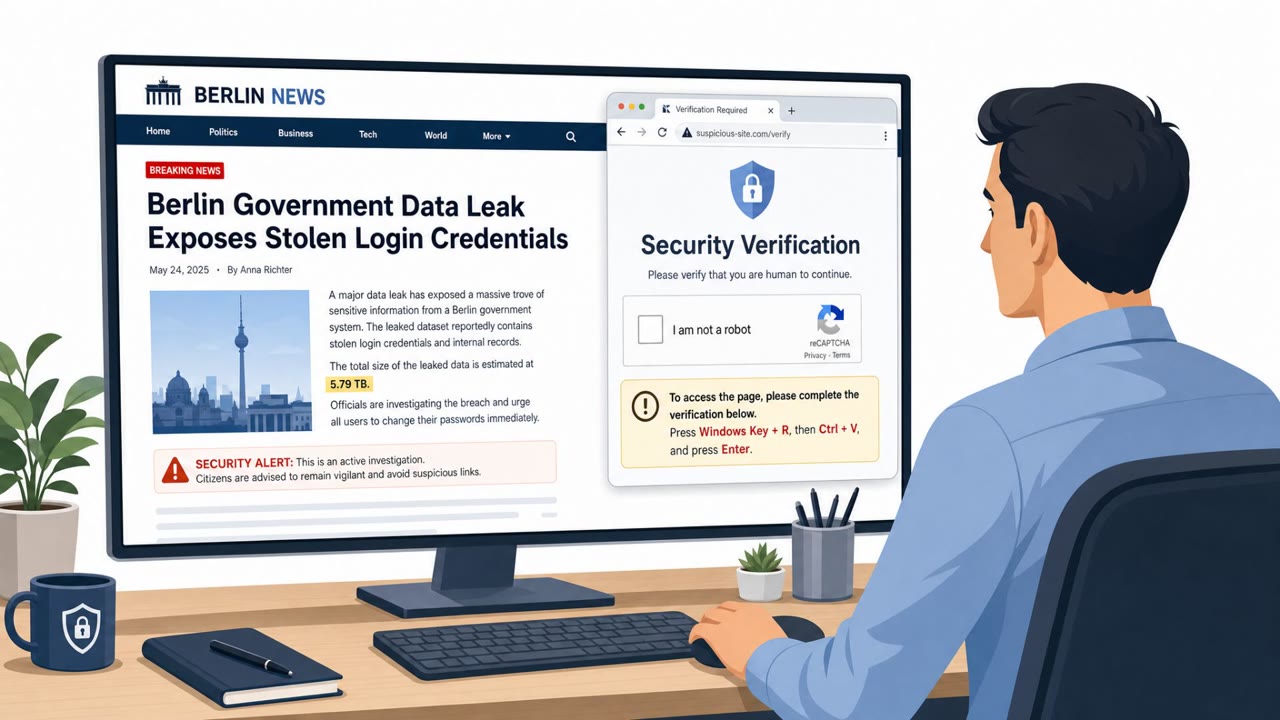
Berlin authorities are investigating a new release of stolen government data, including published login credentials. Germany’s cyber agency also warned of a related campaign where attackers compromise websites and use fake CAPTCHA pages to trick visitors into running malicious commands, enabling…

September 7, 2026
Recruiter, RMM, and Vishing Scams Hit Hard

Recruiter, RMM, and Vishing Scams Hit Hard

This weekly roundup includes multiple real-world social-engineering and phishing-style operations, including fake recruiter outreach pushing malicious Android apps, phishing emails that trick users into installing remote management tools, and vishing that reportedly led to compromised Okta…

September 4, 2026
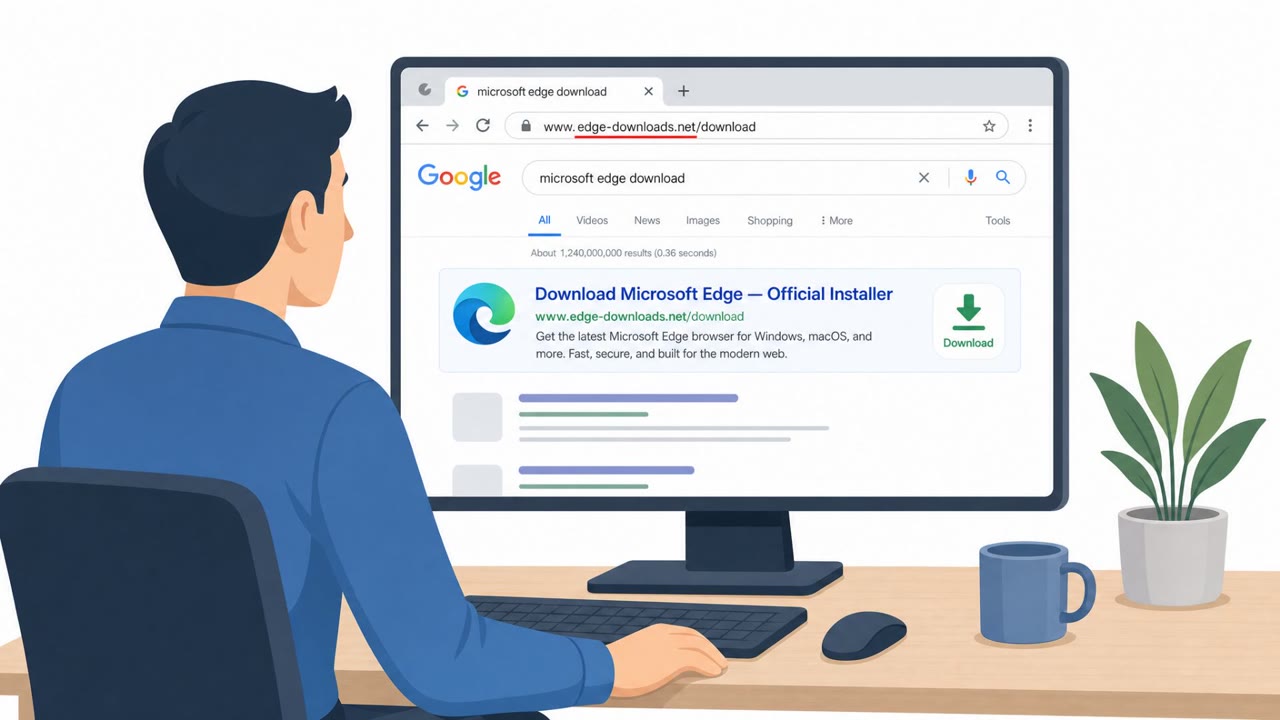
Fake Download Sites Push Trojanized Installers

Fake Download Sites Push Trojanized Installers

Microsoft reports a real campaign where attackers set up look-alike software download websites (impersonating known brands) to trick employees into installing trojanized “installers.” Once run, the malware persists on the device, weakens security settings, and connects to attacker-controlled…

September 3, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo