Recent Healthcare Cyber Attacks

Page 3 of 8
Microsoft Takes Down 1B-Message Phishing Bazaar

Microsoft Takes Down 1B-Message Phishing Bazaar

Microsoft and Health-ISAC disrupted a Chinese-language phishing marketplace ecosystem (YAM Store, CoGUI, and Iron Man) that enabled criminals to send over a billion malicious messages globally. The services sold phishing kits, compromised accounts, and infrastructure, and were frequently used to…

October 14, 2026
Microsoft Busts Massive Phishing Kit Network

Microsoft Busts Massive Phishing Kit Network

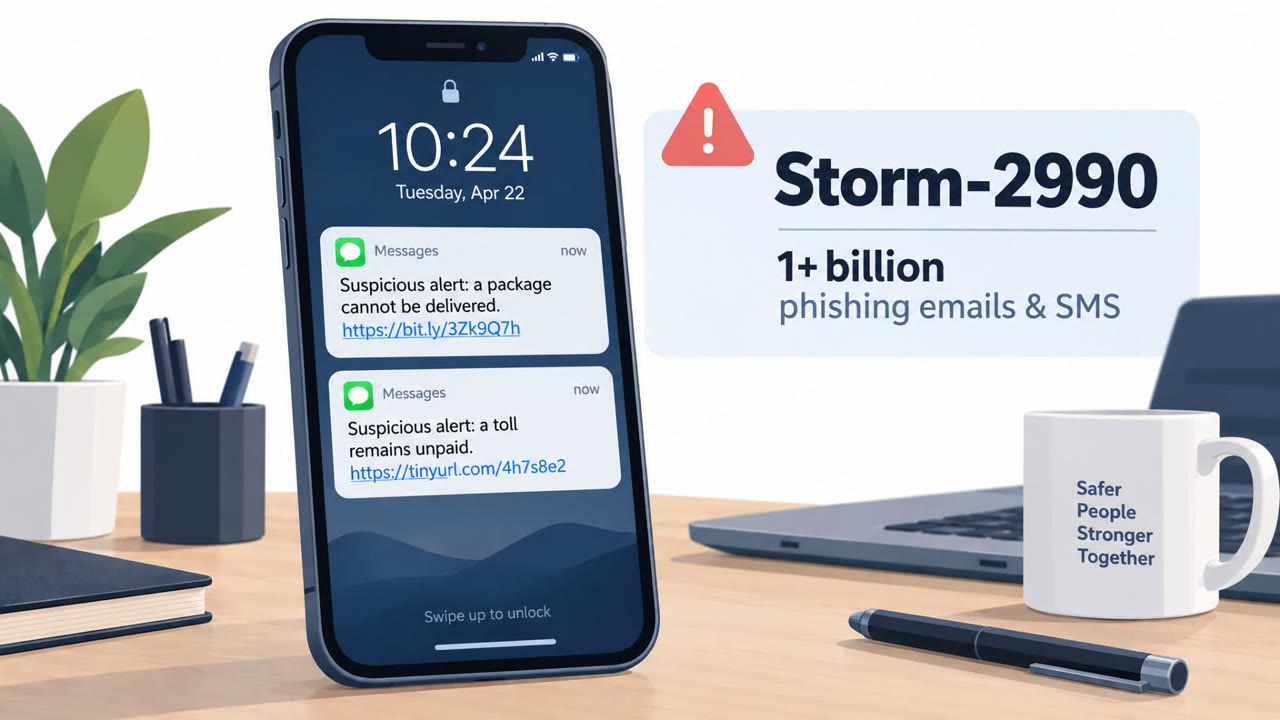
Microsoft and partners disrupted a Chinese-language phishing kit ecosystem (tracked as Storm-2990) used to send over 1 billion malicious email and SMS messages to more than 75,000 organizations worldwide. The kits used common “urgent alert” scams (delivery issues, unpaid tolls, bank or tax…

October 14, 2026
North Korean Fake IT Workers Ran US Laptop Farms

North Korean Fake IT Workers Ran US Laptop Farms

US authorities arrested two Americans accused of helping North Korean “fake IT workers” get hired remotely at US companies and route company laptops into US-based “laptop farms.” The scheme used stolen or fake identities and location-masking tools so overseas workers could appear to be working from…

October 14, 2026
North Korean Fake IT Workers Infiltrate Hiring

North Korean Fake IT Workers Infiltrate Hiring

North Korean-linked actors are using fake identities to get hired into remote IT roles, then leveraging that trusted access to steal data or attempt to deploy malware. The article describes real cases (including KnowBe4 and Netskope) and explains how the scheme scales using fabricated personas,…

October 14, 2026
Fake ChatGPT ‘Outage’ Lures Users Into Malware

Fake ChatGPT ‘Outage’ Lures Users Into Malware

Attackers are using sponsored Google ads to route people to a malicious “custom GPT” that looks like ChatGPT, even while the user is logged in on the real ChatGPT domain. The fake GPT displays a convincing “service availability” message and pushes a link to a “backup domain” that ultimately…

October 2, 2026
Browser Scams: ClickFix, OAuth & Session Theft

Browser Scams: ClickFix, OAuth & Session Theft

The article describes how real-world attackers are shifting common breach activity into the web browser, including phishing that steals live sessions, fake “copy/paste to fix” prompts (ClickFix), and OAuth consent/device-code tricks. It highlights how these browser-based lures can bypass MFA and…

September 30, 2026
ShinyHunters Talked Into Odido via Spoofed Login

ShinyHunters Talked Into Odido via Spoofed Login

Dutch police are investigating ShinyHunters after a phone-based social engineering incident helped attackers break into Odido, the Netherlands’ largest mobile provider. Investigators say the caller persuaded an employee to log into a spoofed website, which was then used to steal data on more than…

September 28, 2026
Vishing Wave Hits Healthcare With MFA Reset Traps

Vishing Wave Hits Healthcare With MFA Reset Traps

Threat groups are actively targeting healthcare and pharma staff using phone-based social engineering (“vishing”) and look‑alike medical domains to steal employee login credentials. Researchers say attackers pressure employees to click password-reset or MFA-reset links, and multiple…

September 28, 2026
Fake CAPTCHA ‘ClickFix’ Spreads Lunex Stealer

Fake CAPTCHA ‘ClickFix’ Spreads Lunex Stealer

Attackers compromised legitimate Ukrainian websites and showed visitors a fake CAPTCHA/Cloudflare-style “verification” prompt to trick them into installing malware. The infection chain drops Lunex (aka Psychedelic Stealer), which disables security monitoring using a vulnerable AMD driver and then…

September 26, 2026
Fake Cloudflare CAPTCHA Pushes MSI Malware

Fake Cloudflare CAPTCHA Pushes MSI Malware

Attackers compromised real Ukrainian business websites and showed visitors a fake Cloudflare verification page. The lure tricks people into running a Windows Installer command (via Windows+R), which installs “Psychedelic Stealer” to steal saved browser passwords and cryptocurrency wallet data.

September 25, 2026
QR Codes Hijacked via Abandoned Branded Domains

QR Codes Hijacked via Abandoned Branded Domains

A researcher demonstrated that attackers can take over a company’s branded QR-code subdomain (e.g., qr.company.com) if the company stops using a QR vendor but forgets to remove the DNS record. Anyone scanning a legitimate printed QR code can then be redirected to an attacker-controlled website,…

September 25, 2026
Device-Code Phish + Fake Recruiter Interview Lures

Device-Code Phish + Fake Recruiter Interview Lures

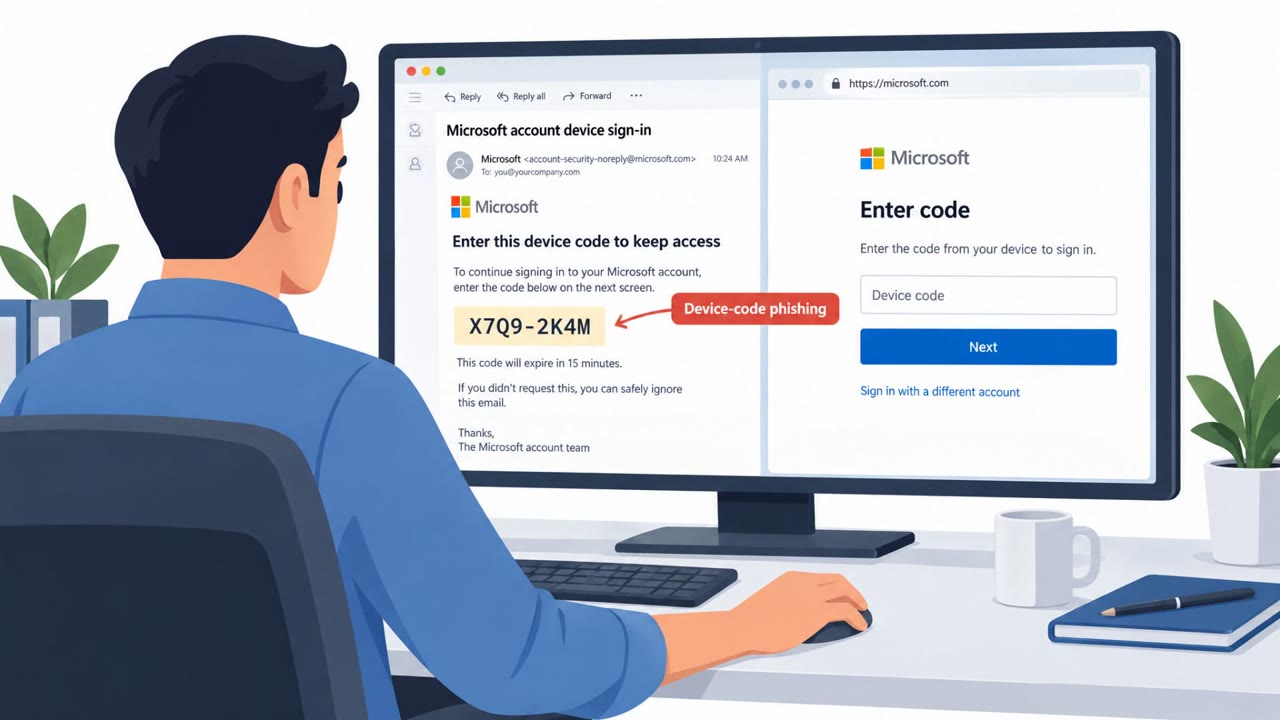
This news roundup describes multiple real-world social engineering operations, including a device-code phishing service that stole access to over 12,000 inboxes and a North Korean campaign posing as recruiters to trick developers during fake coding interviews. The attackers used legitimate login…

September 24, 2026
Astrana Staff Fooled by Spoofed Phone Calls

Astrana Staff Fooled by Spoofed Phone Calls

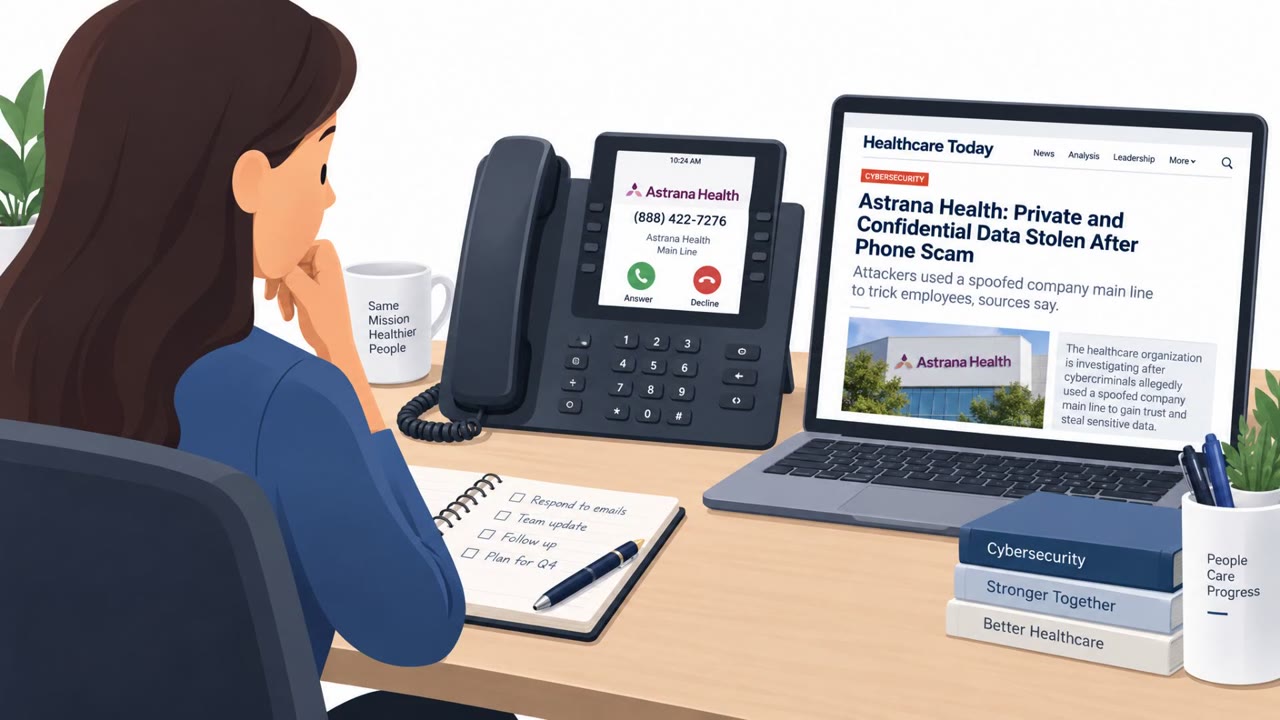
Astrana Health disclosed that attackers stole private and confidential data after using social engineering to trick employees. The attackers impersonated Astrana personnel and spoofed the company’s main phone number to contact staff, leading to unauthorized access to servers and data exfiltration.

September 24, 2026
EvilTokens Used Device-Code Phish to Fuel BEC

EvilTokens Used Device-Code Phish to Fuel BEC

Microsoft disrupted “EvilTokens,” a subscription cybercrime service that stole Microsoft account access using device-code phishing and then used AI-style automation to rapidly mine victims’ inboxes for payment and org-chart details. The goal was to quickly craft believable payment-fraud messages…

September 23, 2026
Microsoft Disrupts ‘EvilTokens’ Phishing Service

Microsoft Disrupts ‘EvilTokens’ Phishing Service

Microsoft says it disrupted the “EvilTokens” phishing-as-a-service platform, which it links to compromises of over 12,000 inboxes across more than 10,000 organizations. The service used AI to tailor phishing emails to a victim’s role and to analyze compromised inboxes to identify trusted…

September 23, 2026
EvilTokens MFA Phish Hijacked 12,000 Inboxes

EvilTokens MFA Phish Hijacked 12,000 Inboxes

Microsoft and partners disrupted “EvilTokens,” a phishing service that helped criminals break into more than 12,000 mailboxes across 10,000+ organizations. Victims were tricked into entering an authentication code on a real Microsoft sign-in page, letting attackers capture access tokens and get…

September 23, 2026
EvilTokens Used Device-Code Phish + AI for BEC

EvilTokens Used Device-Code Phish + AI for BEC

Microsoft disrupted EvilTokens, a phishing-as-a-service operation linked to thousands of compromised Microsoft 365 inboxes. The group used “device code” phishing to steal valid session tokens (not passwords) and then used an AI chatbot to scan mailboxes and help craft business email compromise…

September 22, 2026
Device-Code Phishing Service Hit After 12K Breaches

Device-Code Phishing Service Hit After 12K Breaches

Microsoft and partners disrupted “EvilTokens,” a phishing-as-a-service platform Microsoft links to over 12,000 compromised inboxes across more than 10,000 organizations. The service used deceptive emails to trick people into pasting a “device code” into Microsoft’s real sign-in page…

September 22, 2026
EvilTokens Uses Device Codes to Bypass MFA

EvilTokens Uses Device Codes to Bypass MFA

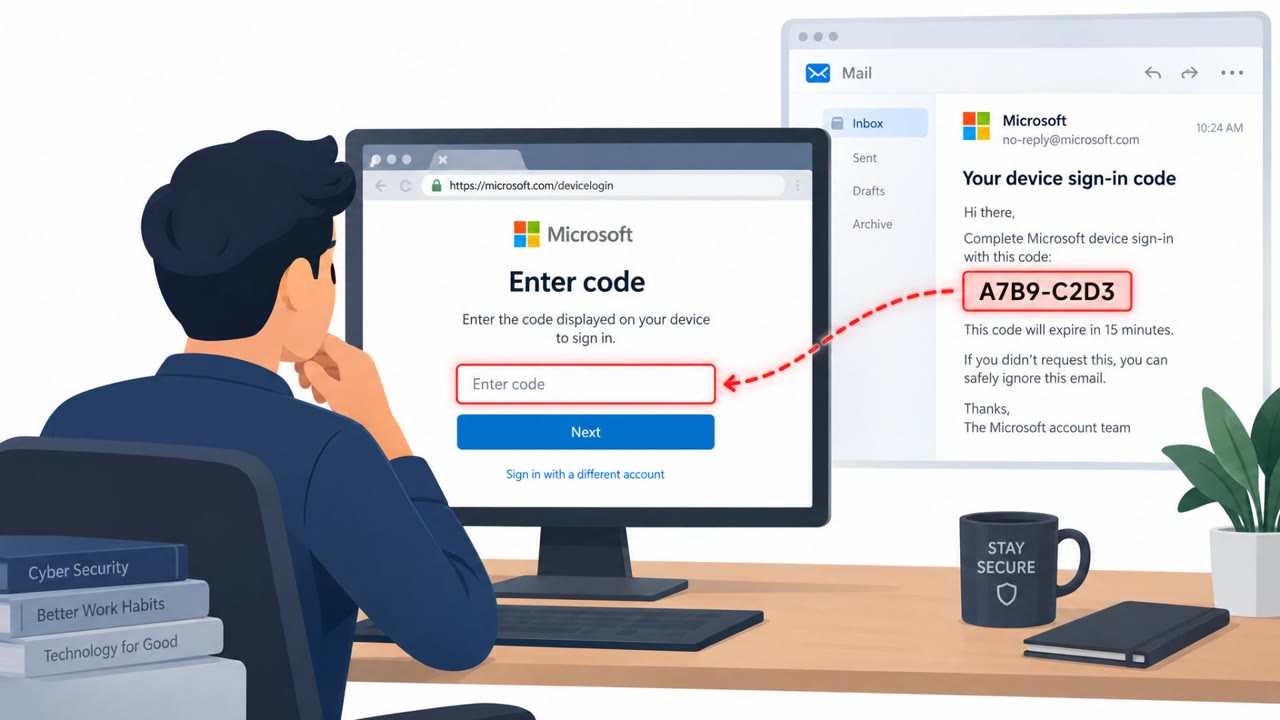
Microsoft reports that the EvilTokens phishing-as-a-service platform helped criminals compromise thousands of organizations by tricking users into completing a legitimate Microsoft “device code” login. The lure drives victims to enter a short code at microsoft.com/devicelogin, which unknowingly…

September 22, 2026
Fake CEOs on LinkedIn Fuel IP & Data Theft

Fake CEOs on LinkedIn Fuel IP & Data Theft

A CSC report describes real-world scams where criminals impersonate executives and brands online to steal personal or payment information. Examples include fake CEOs contacting people on LinkedIn with bogus job offers, and lookalike “FIFA” domains used for fake ticket sales, travel offers, and…

September 22, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo