Stolen Microsoft Sessions Fuel Email Takeovers
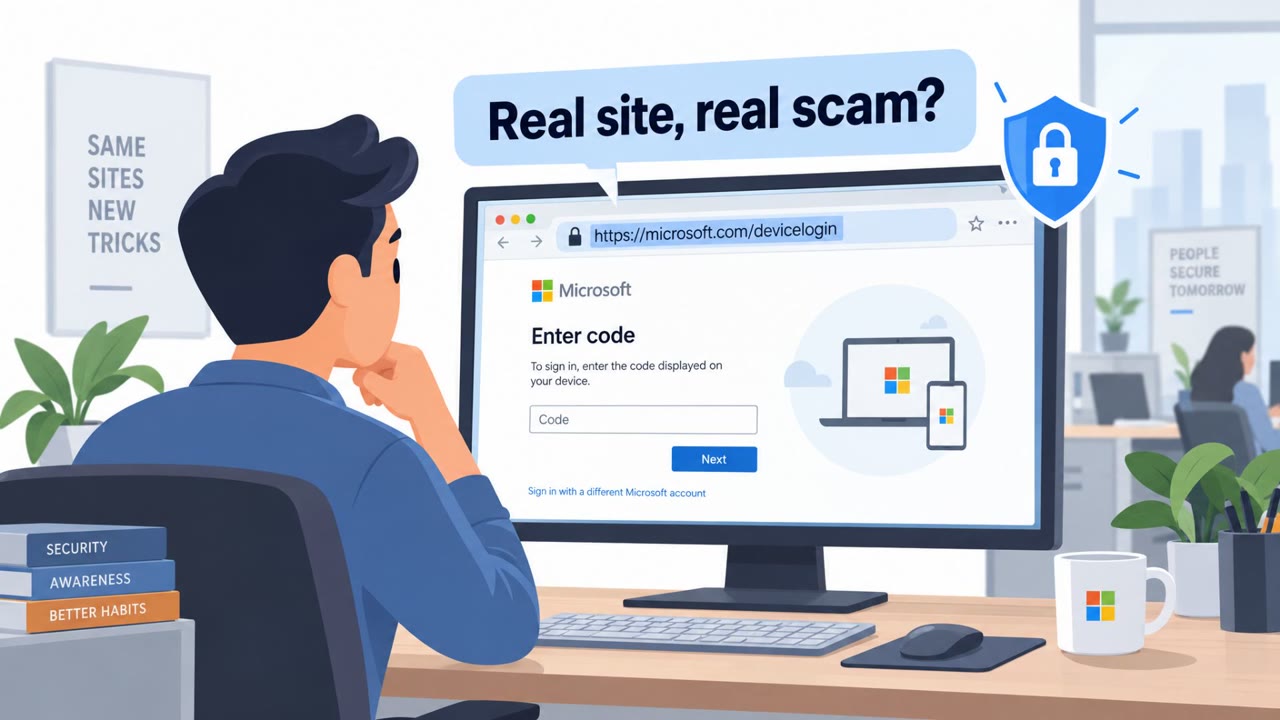
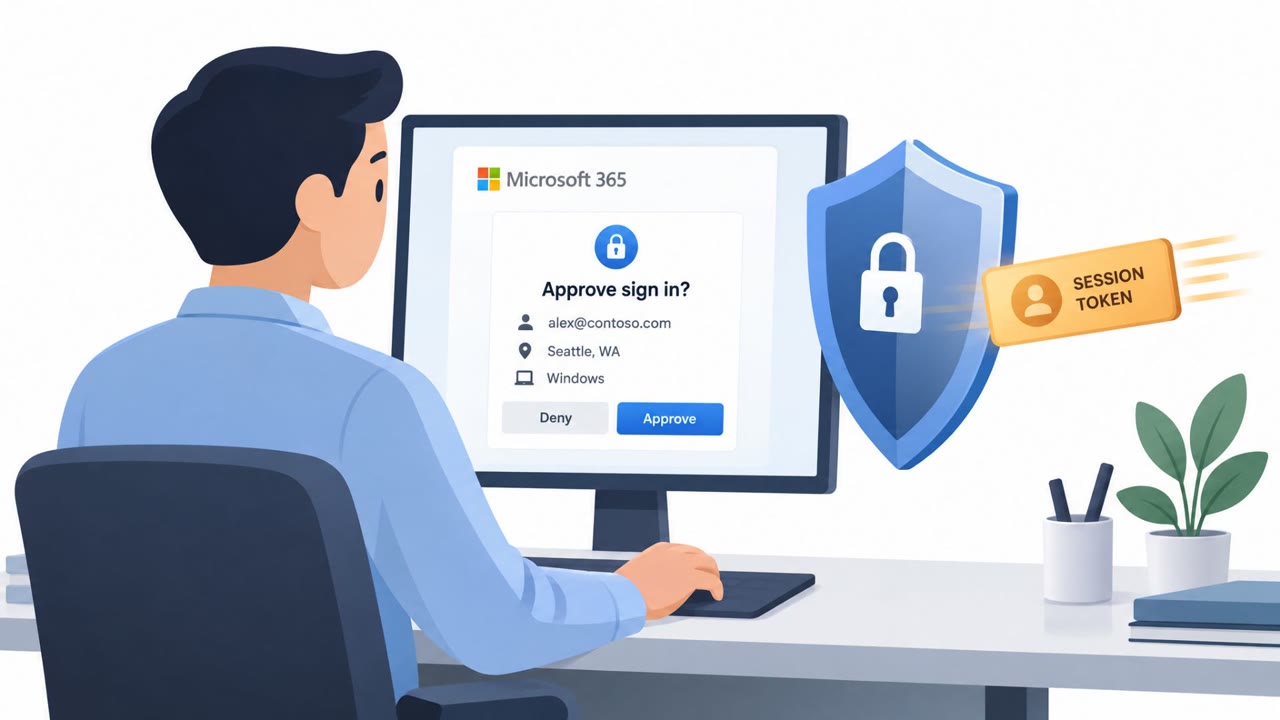
Attackers used fake Microsoft sign-in pages to capture already-authenticated Microsoft 365 sessions, then replayed those sessions to enter business accounts without passwords or new MFA prompts. The campaign affected 79 organizations and expanded access by registering rogue devices, changing MFA…
October 27, 2026