Cisco Talos reports a China-nexus cluster (UAT-11587) using targeted spear‑phishing against government and policy organizations across Asia. The attackers spoof trusted senders and use an email that visually clones Gmail’s attachment preview to trick recipients into clicking a Cloudflare-hosted download link, leading to a multi-stage infection chain that installs the Antino backdoor.
How the attack worked
Cisco Talos documented UAT-11587, a China-nexus cluster conducting targeted spear-phishing against government and policy organizations across Asia, including Taiwan, India, the Philippines, and Cambodia. The group relied on tailored decoy documents and a multi-stage infection chain to gain initial access, rather than a single generic phishing template.
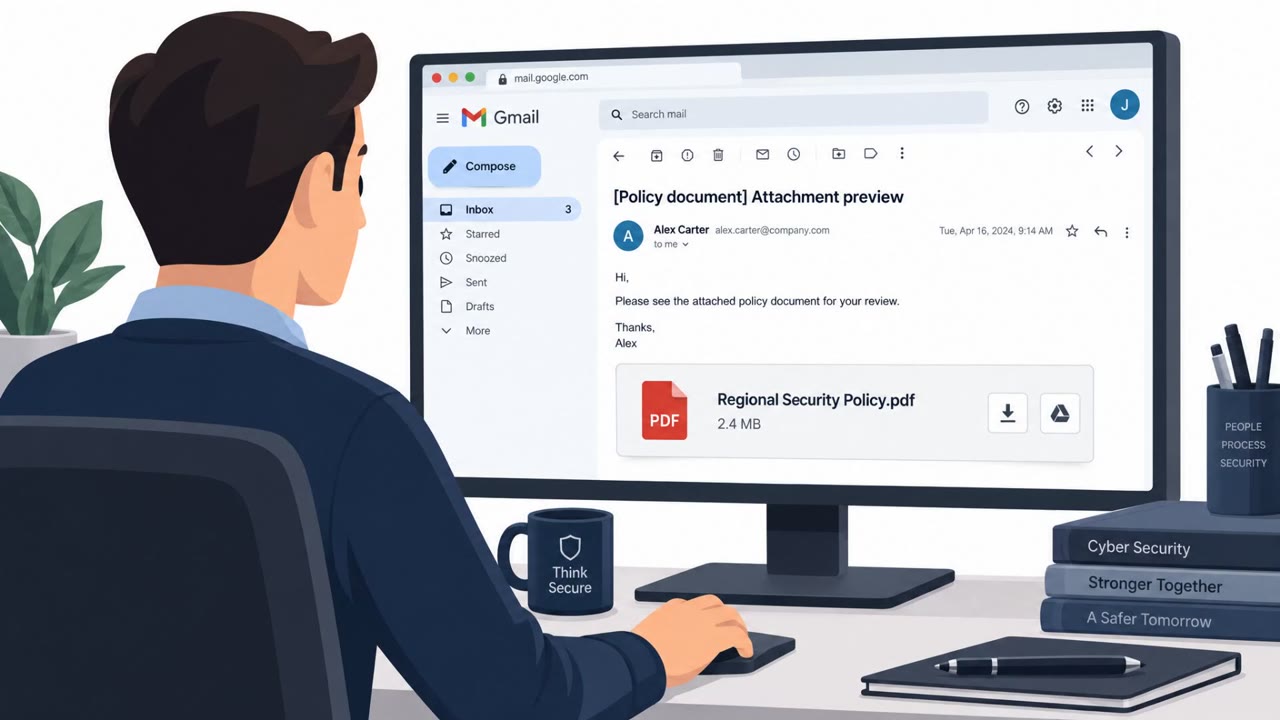
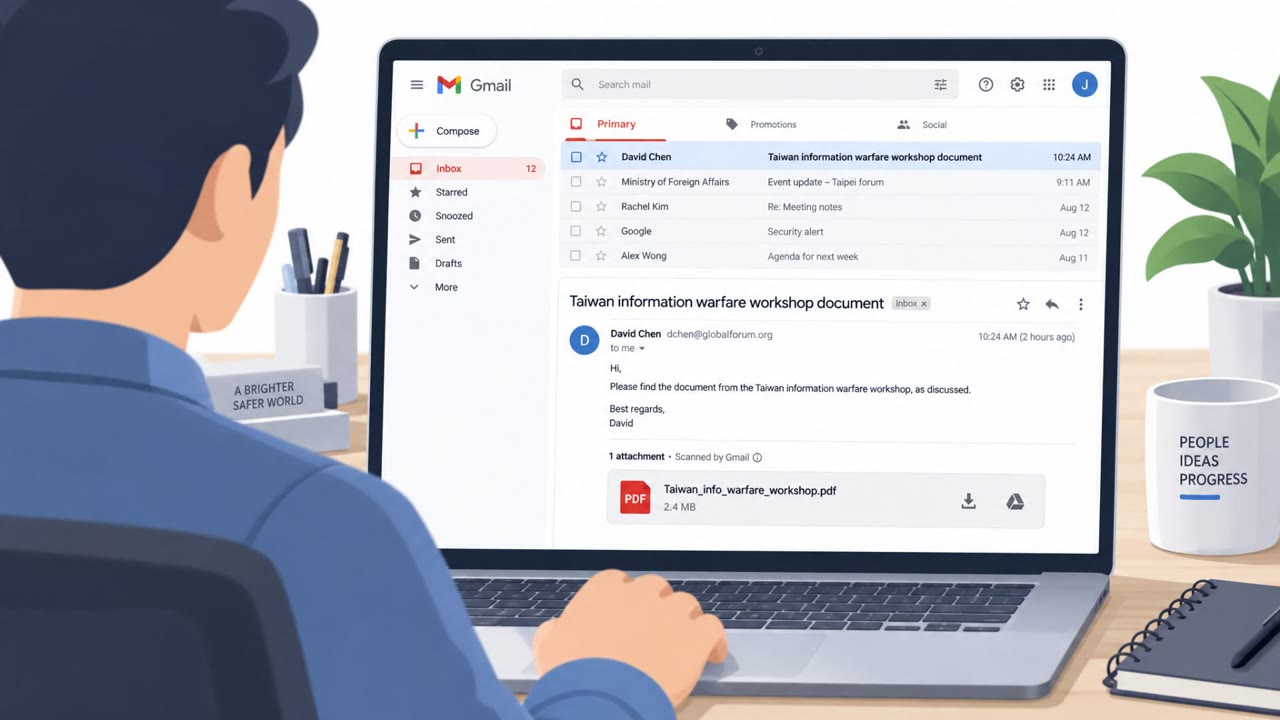
One of the most notable techniques was a visual clone of Gmail's attachment preview placed directly inside the email body. Instead of a real attachment, the entire preview card was wrapped in an anchor tag linking to an attacker-controlled Cloudflare Pages URL. These links included a tracking parameter that allowed per-recipient logging, meaning the attackers could monitor exactly who clicked. The campaign's final payload was a custom Rust backdoor called Antino, which communicates through Microsoft 365 services such as Outlook and OneDrive rather than a dedicated command-and-control server, helping it blend into normal enterprise traffic.
Why it succeeded
The campaign combined two forms of trust abuse. First, sender identities were spoofed so that the visible From header displayed a trusted organization's name, while the actual envelope sender used an attacker-controlled domain sent through Migadu. This misalignment meant messages could still reach inboxes even when DMARC checks failed. Second, the fake Gmail attachment preview exploited a visual interface that recipients see constantly and rarely scrutinize, making the deceptive click feel routine.
Decoy content was also highly tailored, referencing real policy topics and events such as an Indo-Pacific forecast briefing, suggesting the attackers had detailed knowledge of their targets' interests and institutional context.
What to watch for
- Attachment previews that are actually clickable images or cards embedded in the email body rather than genuine file attachments
- Links pointing to unexpected cloud-hosting domains like pages.dev, especially with tracking parameters in the URL
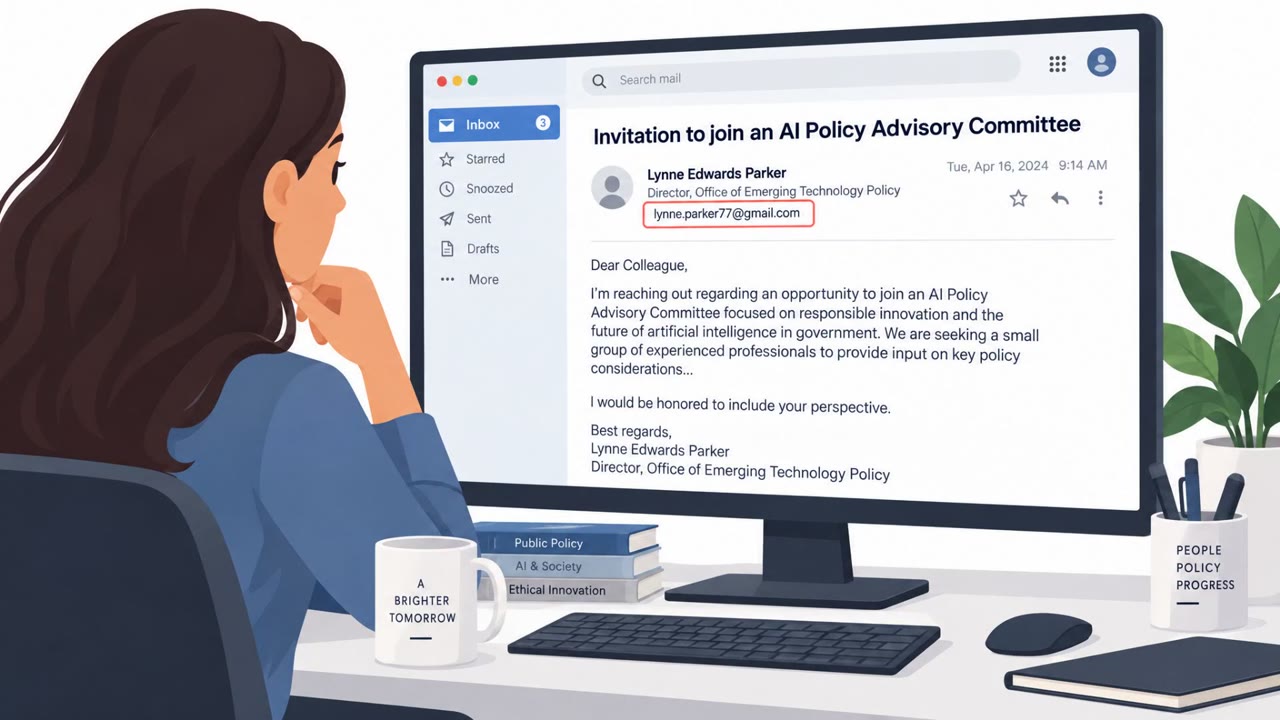
- Sender names that look familiar but whose underlying domain or envelope sender doesn't match the organization
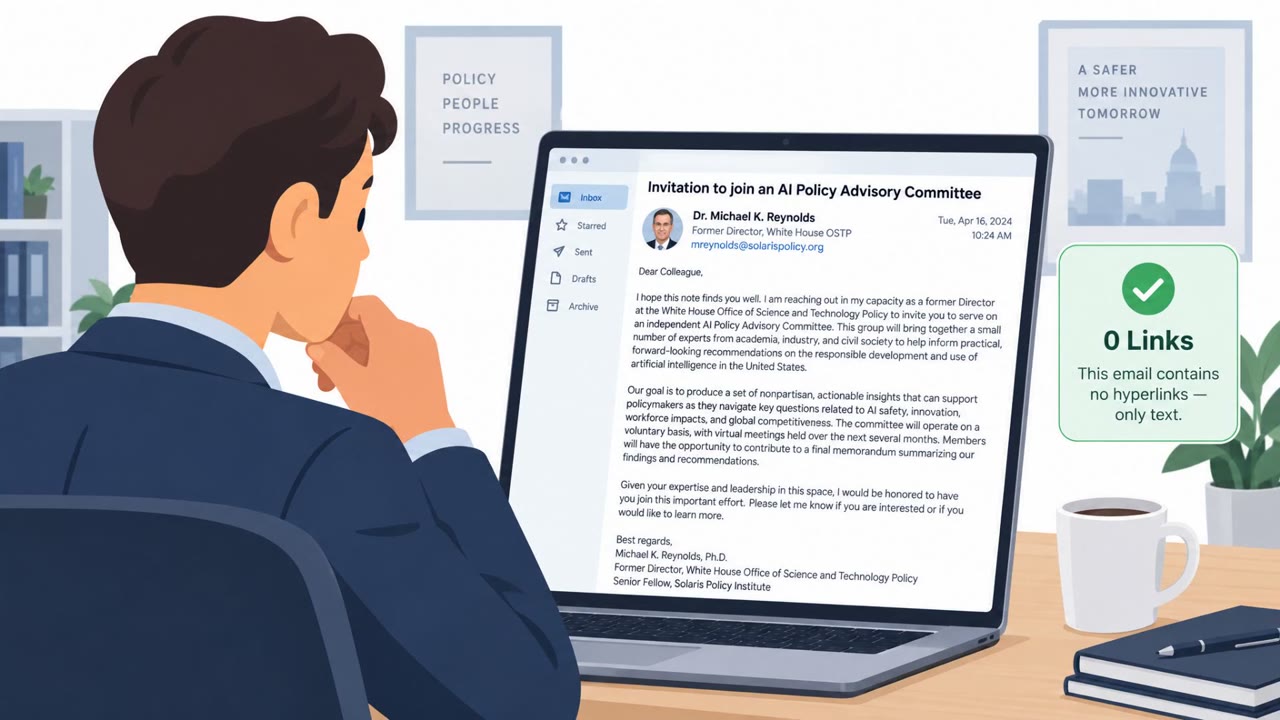
- Unsolicited event invitations or official-looking documents that closely match a recipient's specific job function
Building resistance
Organizations in government, foreign affairs, defense, and policy research should train staff to verify unexpected requests through a separate known channel, inspect links before clicking rather than trusting familiar-looking preview widgets, and treat highly relevant, well-tailored lures with extra caution rather than reduced suspicion.
Key findings
- UAT-11587 targeted government and policy organizations across Asia (including Taiwan, India, the Philippines, and Cambodia) beginning in 2025–2026.
- Initial access repeatedly used spear‑phishing with tailored decoy documents and a multi‑stage infection chain.
- One delivery method cloned Gmail’s attachment preview inside the email body and linked it to an attacker-controlled Cloudflare Pages URL with per-recipient tracking.
- The actor spoofed trusted senders using envelope/from misalignment so messages could reach inboxes even when DMARC failed.
- Final payload included a custom Rust backdoor (“Antino”) that communicates through Microsoft 365 (Outlook/OneDrive) rather than a dedicated command server.
Who’s being targeted
- Commonly targeted roles: Government staff (public administration), Defense / national security personnel, Foreign affairs / diplomatic teams, Legislative / parliamentary staff, Think tank and policy researchers, University researchers and administrators, Government IT and shared services teams, Civil society / human rights organizations.
- Affected industries: Defense and national security, Executive government and public administration, Foreign affairs and diplomatic services, Justice and law enforcement, Legislative and parliamentary institutions, Government IT and e-government shared services, Think tanks and policy research, Universities and research institutions, Civil society and human rights organizations.
- Attack channels: email.
- Impersonated: A trusted organization known to the recipient (spoofed sender identity), A trusted sender identity displayed in the From header (spoofed), An event organizer or official/government policy source (implied by decoy content).
Red flags to watch for
- The “attachment” is actually a clickable image/card inside the email body (not a normal attachment)
- Link goes to an unexpected Cloudflare Pages address (pages.dev) and includes tracking parameters
- Sender appears familiar, but the underlying sender authentication/domain alignment may be wrong
- From address/domain doesn’t match the organization’s real domain when inspected closely
- Unexpected third-party sending service context (message routing) for a sensitive request
- Unusual urgency or context mismatch for the purported sender
- Unexpected event/document arriving out of the blue (even if it looks highly relevant)
- Decoy uses real organizations/experts to appear credible but lacks normal verification steps
- Attachment/link behavior is unusual (e.g., redirects to cloud-hosted downloads)
Frequently asked questions
What is UAT-11587?
UAT-11587 is a China-nexus threat cluster that Cisco Talos observed spear-phishing government and policy organizations across Asia, including Taiwan, India, the Philippines, and Cambodia, starting in 2025.
How did the fake Gmail attachment trick work?
The attackers recreated Gmail's native attachment preview widget inside the email HTML body, and the entire attachment card was wrapped in an anchor tag pointing to an attacker-controlled Cloudflare Pages URL rather than a real file.
How did the sender spoofing bypass DMARC?
Messages were sent through Migadu using an attacker-controlled envelope sender domain while the visible From header showed the impersonated organization's identity, so the receiving provider still accepted the message despite the DMARC failure.
What payload did this campaign deliver?
The infection chain ultimately installed a custom Rust backdoor called Antino, which communicates through Microsoft 365 services like Outlook and OneDrive instead of a dedicated command server.
Read the video transcript
Picture this: you get an email that looks like Gmail, with a familiar contact and a clean attachment preview card. But in recent attacks on policy teams across Asia, that ‘attachment’ was just a fake Gmail widget. The whole card was one big link to a Cloudflare Pages download, kicking off a multi-stage Antino backdoor infection that hides inside Microsoft 365 traffic. Here’s the catch: the sender name looks trusted, but the real sending domain is different, and the ‘attachment’ sits inside the message. Hover it and you see a pages.dev link with tracking parameters, not a normal file or your organization’s domain. If an email shows a Gmail-style attachment card that opens a pages.dev link, stop. Don’t click it, forward it to security and confirm the file through your usual channel instead.