Attackers are sending fake, exclusive Anthropic AI-event invitations that use familiar GoTo Webinar branding to lure enterprise employees. Victims who register are routed through CAPTCHA checks, a fake Zoom-style event page, and spoofed Google or Microsoft sign-in pages designed to steal work credentials.
How the attack worked
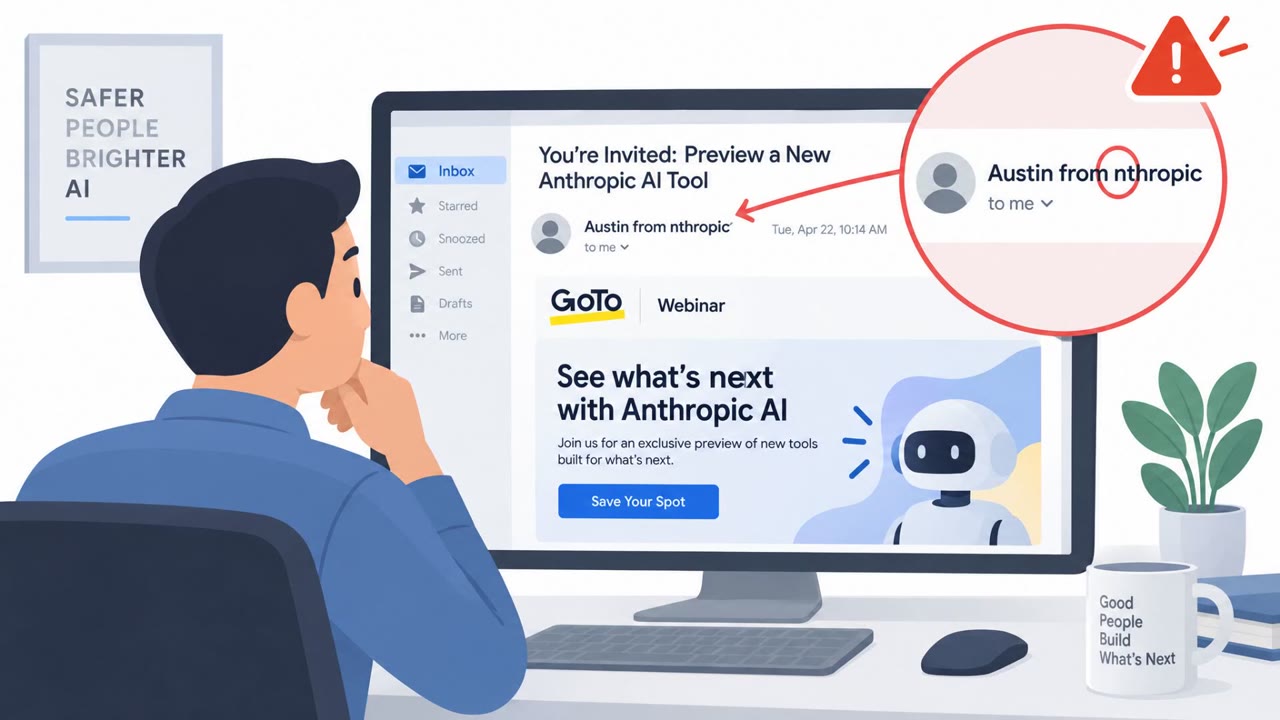
This campaign used an invitation only Anthropic AI preview as bait, promising a focused conversation on frontier AI models to a select group of recipients. The email impersonated GoTo Webinar and appeared to come from customercare@gotowebinar[.]com, but the displayed sender name read Austin from nthropic, dropping the A in Anthropic. Clicking the registration link sent victims through a shortened, compromised URL and a CAPTCHA page before landing on a Zoom style registration page. From there, choosing Continue with Google or Continue with Microsoft triggered a second CAPTCHA and finally a spoofed Google or Microsoft sign in page designed to harvest work credentials.
Why it succeeded
The lure exploited curiosity and fear of missing out around a private preview of new AI technology, which is the kind of invitation an ambitious employee would want to accept without delay. The attack also layered legitimate looking elements such as GoTo Webinar branding, CAPTCHA checks, and familiar Google or Microsoft login pages, each of which made the overall flow feel routine even though it changed branding at every step. CAPTCHA pages were reportedly included specifically to block security scanners and automated analysis tools, extending the campaign's reach before detection.
What to watch for
- A sender name or domain that looks almost right but is subtly off, such as nthropic instead of Anthropic.
- Branding that shifts across the journey, for example an email styled as GoTo Webinar, a registration page styled as Zoom, and a login page styled as Google or Microsoft.
- Lookalike domains with extra words or dashes, such as a Google style domain ending in a nonstandard extension or a Microsoft style domain combining office.com with unrelated text.
- A login page that gives no confirmation and does not redirect to a real vendor site after credentials are entered.
How to build resistance
Employees should verify unexpected AI preview or private event invitations through a known account representative or trusted contact before registering, rather than acting on urgency alone. Teams should be trained to stop and investigate whenever branding changes across an email, a meeting page, and a sign in page, since that inconsistency is a strong indicator of a credential phishing flow. Readers should also get in the habit of checking the full domain on any sign in page, since logos and page design can be convincingly mimicked even when the underlying domain is not legitimate. Finally, organizations should have a clear process for employees to reset passwords and request an account activity review immediately if they suspect they entered credentials into one of these pages, since the damage is done as soon as credentials are submitted.
Key findings
- The campaign uses an invitation-only Anthropic AI preview as an exclusivity and fear-of-missing-out lure.
- The email impersonates GoTo Webinar and appears to come from customercare@gotowebinar[.]com, but the displayed sender name is "Austin from nthropic."
- A shortened link leads victims to a compromised URL, then through CAPTCHA pages intended to block security scanners and analysis tools.
- Victims see a Zoom-spoofed registration page before being sent to imitation Google or Microsoft sign-in pages.
- The fake Microsoft page captures usernames and passwords; the fake Google page reportedly captures usernames only.
- The campaign shifts between GoTo Webinar, Zoom, Google, and Microsoft branding, creating inconsistencies that users can use as warning signs.
Who’s being targeted
- Commonly targeted roles: All enterprise employees, Technology and innovation teams, Google Workspace users, Microsoft 365 users, Executives, Security awareness teams.
- Affected industries: Enterprise organizations, Technology and AI users, Organizations using Google Workspace, Organizations using Microsoft 365.
- Attack channels: email, website.
- Impersonated: GoTo Webinar and Anthropic, Google or Microsoft.
Red flags to watch for
- The sender name is "Austin from nthropic," missing the "A" in Anthropic.
- The branding changes from GoTo Webinar in the email to a Zoom-style registration page and then Google or Microsoft login pages.
- The registration flow uses CAPTCHA pages before presenting a login prompt.
- The destination domain uses misleading subdomains and dashes rather than an official vendor domain.
- The Google lookalike domain is goo[.]gle-access-eventregister[.]icu, not a Google-owned domain.
- The Microsoft lookalike domain is office[.]com-access-sharepoint[.]com, not an official Microsoft domain.
- After credentials are entered, the page provides no confirmation and does not redirect to a legitimate vendor site.
Frequently asked questions
How does the fake Anthropic AI preview attack work?
Victims get an invitation email impersonating GoTo Webinar for an exclusive Anthropic session, then are routed through CAPTCHA checks, a Zoom-spoofed registration page, and finally a fake Google or Microsoft sign-in page that captures their work credentials.
What are the warning signs of this phishing campaign?
The sender name is listed as Austin from nthropic, missing the A in Anthropic, and the branding shifts from GoTo Webinar to Zoom to Google or Microsoft across the flow, which is inconsistent with a legitimate event registration.
What should I do if I entered credentials on one of these pages?
Reset the password immediately and have the account's activity reviewed, since attackers have already captured the credentials once they are submitted.
Does the fake Google or Microsoft page steal passwords too?
The fake Microsoft page captures both usernames and passwords, while the fake Google page reportedly captures only usernames.
Read the video transcript
An exclusive Anthropic AI preview? Check who invited you. The email looks like GoTo Webinar. Its short link leads through CAPTCHAs to a Zoom-style registration page, then asks you to continue with Google or Microsoft. That brand-hopping is the tell. The Microsoft lookalike at office[.]com-access-sharepoint[.]com isn't Microsoft, and it collects your work username and password. Before registering, ask your known Anthropic contact if the invitation is real.