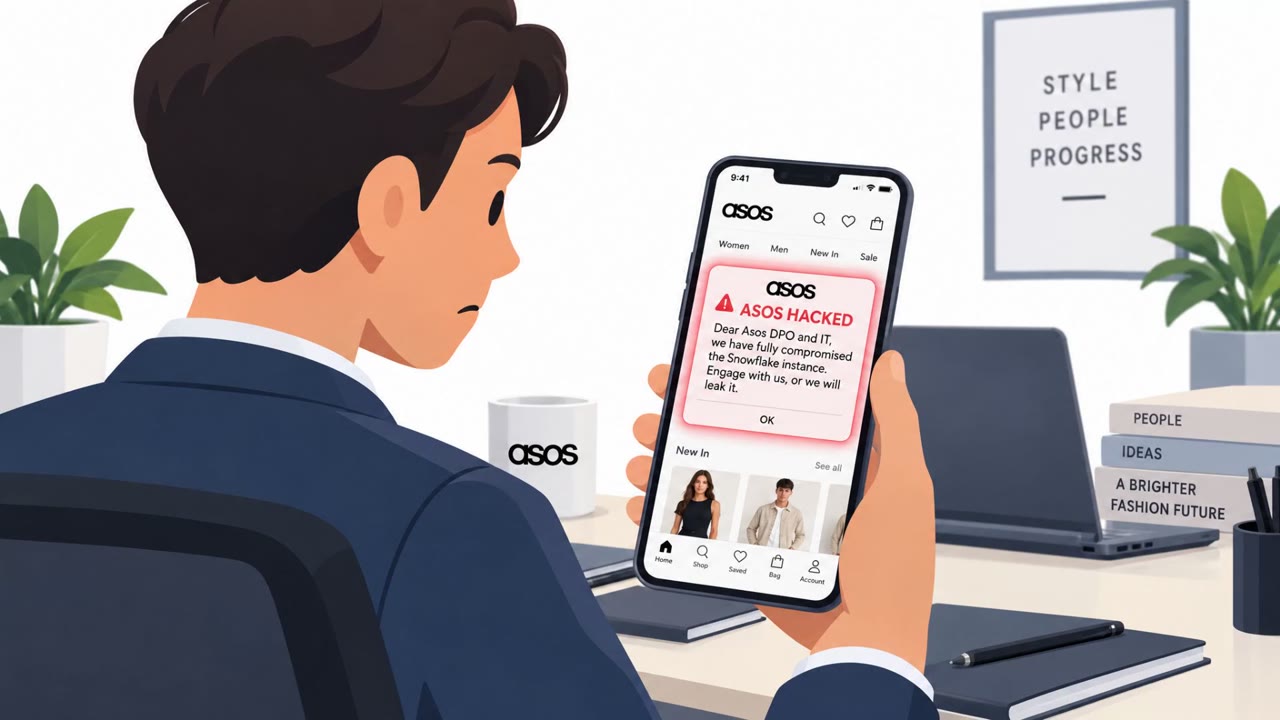
Asos customers received a mobile app notification claiming the retailer was “fully compromised” and warning of a Snowflake data breach. The alert included a link that redirected users to a Telegram channel allegedly run by a new cyber gang (“Xuanye”), suggesting a social-engineering attempt designed to drive attention and potentially set up follow-on scams.
How the Attack Worked
Asos customers received a mobile app push notification titled "Asos hacked," claiming the retailer was fully compromised. The message referenced a Snowflake data breach, stating "we have fully compromised the Snowflake instance," and included a link. Instead of leading to an official Asos page, the link redirected recipients to a Telegram channel allegedly operated by a previously unknown group calling itself Xuanye. The scenario relied on urgency and alarming language rather than any verified breach confirmation from Asos.
Why It Succeeded
The notification arrived through a channel customers normally trust, the app's own push notification system, which lent it unearned credibility. Threatening phrases like "fully compromised" are designed to trigger panic and reduce critical thinking before a user checks whether the message is legitimate. Because the group behind the message was previously unknown, experts suggested the notification itself might have been an attempt to grab wider attention rather than a confirmed security event.
What to Watch For
- Security alerts delivered as broad app notifications rather than through normal in-app account messaging or support channels
- Links that redirect to third-party messaging apps like Telegram instead of an official company domain or help page
- Alarmist or threatening language, such as claims of being "fully compromised," intended to create panic and urgency
- Unfamiliar group names claiming responsibility, which may be unverified or exaggerated
Building Resistance
High-profile incidents, real or fabricated, create ideal conditions for follow-on phishing. Customers should expect copycat messages claiming to be from the company, asking them to reset a password, confirm payment details, check an order, or claim a refund. The safest response is to ignore links in unsolicited alerts entirely and instead navigate directly to the company's official site or app to verify any claims.
For organizations, this incident is a reminder that customer-facing teams, including customer support, digital/eCommerce, marketing/CRM functions that manage push notifications, security operations, and executive leadership responsible for incident communications, should have a rapid verification and messaging plan ready. Clear, pre-approved communication templates help customers quickly distinguish real company communications from spoofed alerts, reducing the window of opportunity for attackers to exploit confusion during a suspected or fabricated incident.
Key Takeaway
Treat unexpected security incident alerts with skepticism, especially when they push you toward third-party messaging platforms instead of official support channels. Pausing to verify through trusted, direct channels before clicking any link remains the most reliable defense against this type of social engineering attempt.
Key findings
- Customers received a push notification titled “Asos hacked” containing a link that redirected to Telegram.
- The message text claimed: “we have fully compromised the Snowflake instance.”
- The link led to “a telegram channel operated by an apparent cyber gang called the Xuanye group.”
- Experts noted the group was previously unknown and the notification “might be an attempt to grab wider attention.”
- Third parties warned that high-profile incidents often trigger follow-on phishing using password reset/refund/order-payment pretexts.
Who’s being targeted
- Commonly targeted roles: Customer Support, Digital/eCommerce, Marketing/CRM (push notifications), Security Operations, Executive leadership (incident communications).
- Affected industries: Online retail / e-commerce, Retail (fashion).
- Attack channels: website, telegram.
- Impersonated: Asos (app notification / security alert).
Red flags to watch for
- Unusual security alert delivered as a broad app notification rather than in-app account messaging/support channels
- Link sends users to Telegram instead of an official Asos domain/help page
- Threatening language about being “fully compromised” designed to create panic/urgency
Frequently asked questions
What happened in the fake Asos hacked alert?
Customers received a push notification titled "Asos hacked" claiming the company was fully compromised, with a link that redirected to a Telegram channel run by a group calling itself Xuanye.
Why would attackers push users to Telegram?
Experts noted the group was previously unknown, and the alert might have been an attempt to grab wider attention, potentially setting up follow-on scams through the Telegram channel.
What should customers watch for after a high-profile incident like this?
Be cautious of unexpected security alerts pushing you to third-party messaging apps instead of official support pages, and expect copycat phishing using password reset, refund, or order-payment pretexts.
How can organizations build resistance to this type of attack?
Security teams should prepare incident communications in advance, remind customers that legitimate alerts come through official channels, and monitor for follow-on phishing after any publicized security notification.
Read the video transcript
Imagine this pops up on your phone: notification from Asos saying, “Asos hacked.” This real alert told customers, “we have fully compromised the Snowflake instance” and linked them to a Telegram channel run by a so‑called Xuanye group. Here’s the trick: a broad “Asos hacked” blast, threatening language, and then a jump to Telegram instead of an official Asos help page. That’s priming you for follow‑on scams like fake password resets or refunds. If you see a security alert that pushes you to Telegram or any messaging app, don’t tap it, open the company’s website or app yourself and check there.