The FBI attributed the theft of roughly $6.3 billion from Binance to North Korea's TraderTraitor operation, which is linked to the Lazarus Group. The reported Binance breach began with a compromised DevOps engineer laptop, while the group has previously used fake job offers and recruitment exercises to obtain employee access at cryptocurrency organizations.
What happened
The FBI attributed the theft of roughly $6.3 billion from Binance to TraderTraitor, a North Korean operation linked to the Lazarus Group. According to Binance, the intrusion began with a compromised DevOps engineer's laptop, which gave attackers access to a service container and allowed them to authorize withdrawals they had no business making. Investigators expect the stolen funds to be swapped for Ethereum and moved through DeFi platforms and instant swap services to hinder tracing.
The recruitment angle
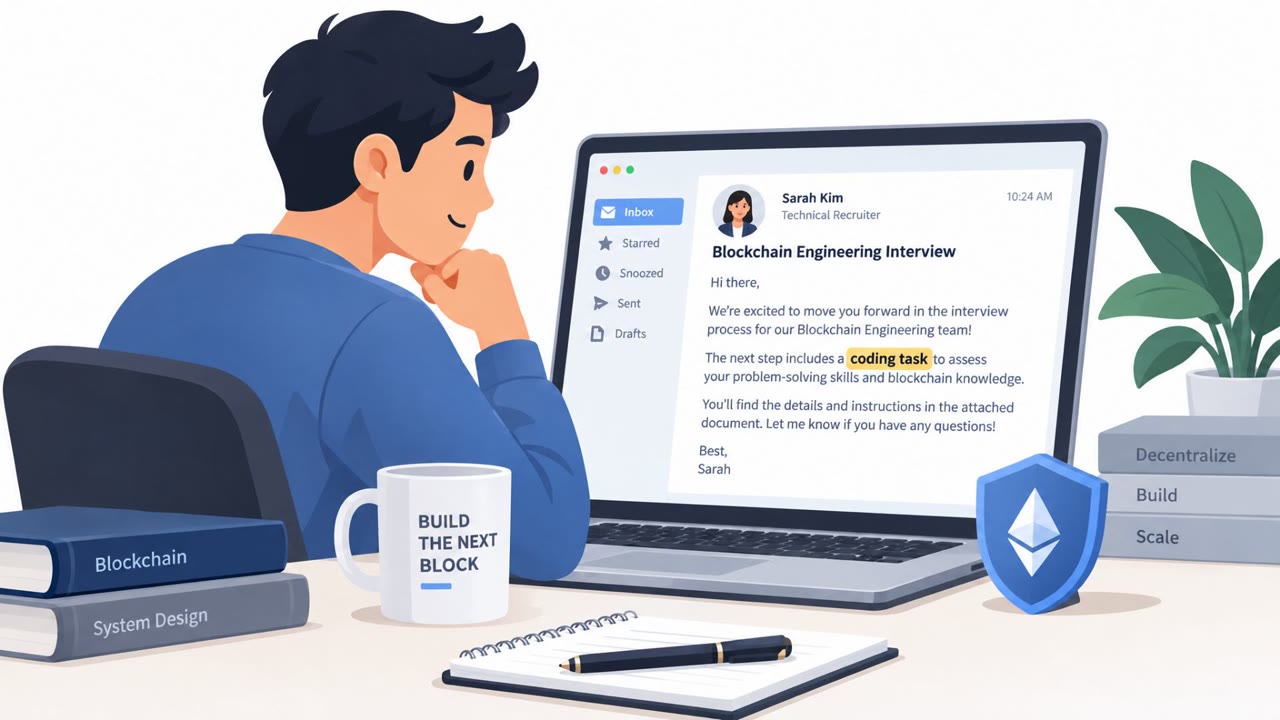
The article notes that TraderTraitor has previously used fake job offers and recruitment exercises to persuade employees at cryptocurrency organizations to hand over access to their employer's systems. This pattern suggests that an unsolicited recruiter contact, often arriving over LinkedIn or email, can be an entry point into highly privileged technical environments. A fabricated hiring process can ask a candidate to run unverified material or request access that a legitimate recruiter would never need.
Why this kind of attack succeeds
- Engineering and DevOps staff often hold privileged access to production systems, making their individual devices high-value targets.
- Recruitment contact feels routine and is rarely treated with the same suspicion as unsolicited emails from unknown vendors or customers.
- A technical exercise or take-home assignment gives an attacker a plausible reason to ask a candidate to download and run code.
- Verifying a recruiter's legitimacy through an official careers channel is an extra step that is easy to skip under time pressure.
What to watch for
- An unsolicited role or recruiter approaches an employee with an unusual technical exercise.
- The recruitment process requests employer-system access or asks the candidate to run unverified material.
- The opportunity cannot be verified through the supposed employer's official careers channel.
Building resistance
Organizations, especially cryptocurrency exchanges and virtual asset service providers, should treat unsolicited job offers and recruitment exercises as potential security risks when they involve requests to access work systems or run recruiter-supplied materials. DevOps and other privileged technical staff should have a clear, fast path to report suspected laptop compromise, since their access can enable outsized damage if misused. Recruiting and HR teams can also help by reinforcing that legitimate hiring processes never require access to an employer's internal systems. On the financial side, virtual-asset providers should screen transactions against official indicators, including published wallet addresses tied to known stolen funds, to limit the movement of proceeds after an incident occurs.
Key findings
- The FBI attributed the October 29 Binance theft to TraderTraitor, a North Korean operation linked to the Lazarus Group.
- Binance said the intrusion began with a compromised DevOps engineer's laptop, allowing access to a service container and unauthorized withdrawals.
- The article reports that TraderTraitor has previously used fake job offers and recruitment exercises to persuade employees to give access to employer systems.
- Investigators expect the attackers to swap stolen funds for Ethereum and use DeFi platforms and instant swap services to hinder tracing.
- The FBI urged exchanges and virtual-asset providers to block transactions involving identified stolen-fund wallet addresses.
Who’s being targeted
- Commonly targeted roles: DevOps engineers, IT administrators, Cloud and platform engineering teams, Cryptocurrency exchange employees, Recruiting and HR teams, Security operations teams.
- Affected industries: Cryptocurrency exchanges, Virtual asset service providers, Financial services.
- Attack channels: linkedin, email.
- Impersonated: Recruiter or prospective employer.
Red flags to watch for
- An unsolicited role or recruiter approaches an employee with an unusual technical exercise.
- The recruitment process requests employer-system access or asks the candidate to run unverified material.
- The opportunity cannot be verified through the supposed employer's official careers channel.
Frequently asked questions
How did the Binance breach start?
Binance said the intrusion began with a compromised DevOps engineer's laptop, which gave attackers access to a service container and allowed unauthorized withdrawals.
Who is behind the attack?
The FBI attributed the October 29 theft to TraderTraitor, a North Korean operation linked to the Lazarus Group.
What tactics does TraderTraitor use to gain access?
The group has previously used fake job offers and recruitment exercises to persuade employees to hand over access to their employer's systems.
What should exchanges do to help trace stolen funds?
The FBI urged exchanges, blockchain analytics firms, and other virtual asset providers to block transactions involving identified stolen-fund wallet addresses.
Read the video transcript
A recruiter messages you on LinkedIn. The role sounds perfect. Then comes the exercise: run their file, or use your work access. That’s not a hiring test. TraderTraitor has used fake recruitment to get into employer systems. Here’s why it matters: Binance said its breach began on a DevOps engineer’s compromised laptop. From there, intruders reached a service container and authorized withdrawals. If a recruiter’s exercise needs your work access or their file, stop and report the message to security.