Threat Watcher

Page 11 of 51
Malicious Packages Turn Dev Installs Into Cloud Breaches

Malicious Packages Turn Dev Installs Into Cloud Breaches

The article describes real supply-chain campaigns where attackers hid credential-stealing code inside trusted open-source packages and developer tools. When a developer or CI system installed the package, the malware ran immediately, stole cloud and pipeline credentials, and enabled unauthorized…

September 28, 2026
Device-Code Phishing and “ClickFix” Lures Spread

Device-Code Phishing and “ClickFix” Lures Spread

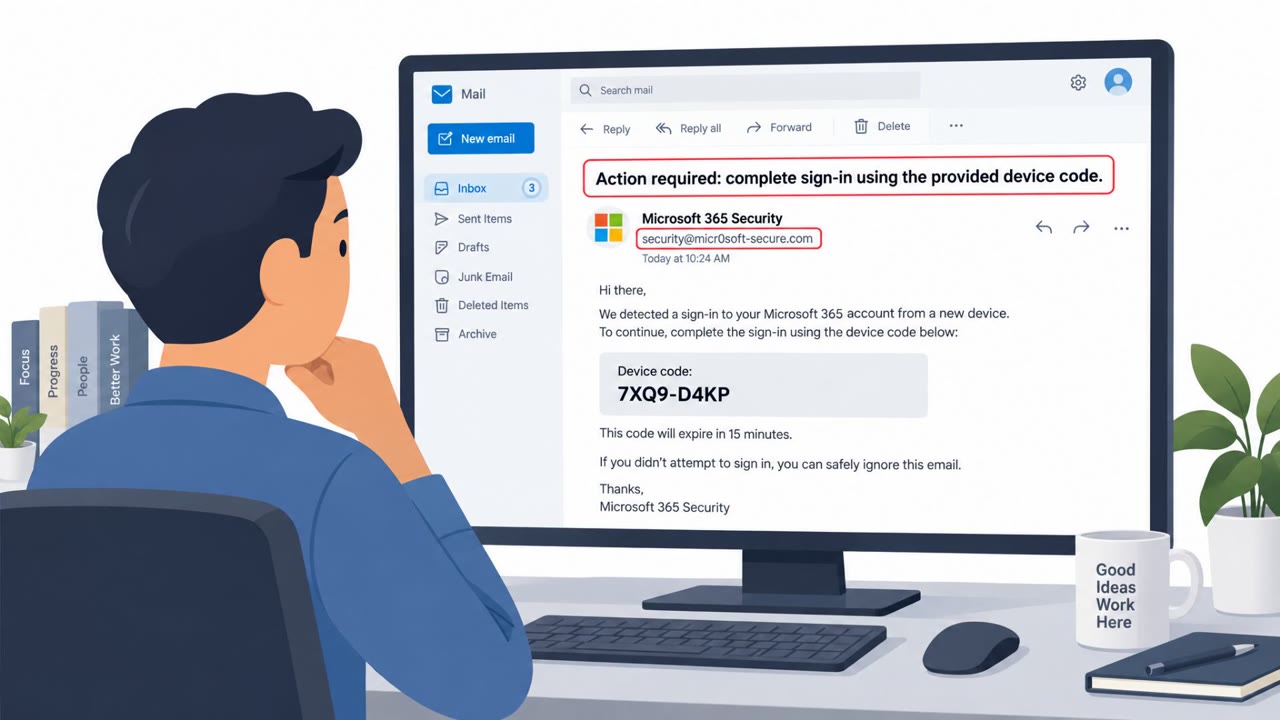
This weekly recap highlights multiple real-world campaigns where attackers trick users into taking actions that grant access, without needing to steal passwords directly. Notable examples include “device code” phishing (victims are instructed to enter a short code to approve an attacker session)…

September 28, 2026
Google Ads ‘Locked PC’ Scam Pushes Fake Support Calls

Google Ads ‘Locked PC’ Scam Pushes Fake Support Calls

A malicious Google Ads campaign showed convincing “computer locked/infected” warnings to Windows and Mac users and pressured them to call fake tech-support numbers. The goal was to confuse people into paying for bogus support, sharing personal information, or allowing remote access, not to actually…

September 28, 2026
Fake GIWA Bridge Trick Drains 767 ETH

Fake GIWA Bridge Trick Drains 767 ETH

Scammers convinced DYORSWAP to integrate a fake version of the upcoming GIWA blockchain, making it look legitimate to users. More than 1,300 wallets then sent roughly 767 ETH (about $2M) to a spoofed bridge contract, which was quickly drained and routed through Tornado Cash.

September 28, 2026
Vishing Wave Hits Healthcare With MFA Reset Traps

Vishing Wave Hits Healthcare With MFA Reset Traps

Threat groups are actively targeting healthcare and pharma staff using phone-based social engineering (“vishing”) and look‑alike medical domains to steal employee login credentials. Researchers say attackers pressure employees to click password-reset or MFA-reset links, and multiple…

September 28, 2026
Fake CAPTCHA ‘ClickFix’ Spreads Lunex Stealer

Fake CAPTCHA ‘ClickFix’ Spreads Lunex Stealer

Attackers compromised legitimate Ukrainian websites and showed visitors a fake CAPTCHA/Cloudflare-style “verification” prompt to trick them into installing malware. The infection chain drops Lunex (aka Psychedelic Stealer), which disables security monitoring using a vulnerable AMD driver and then…

September 26, 2026
Fake Bank Cards in the Mail Still Work

Fake Bank Cards in the Mail Still Work

Criminals in parts of Europe have been mailing fake “replacement” bank cards or letters claiming a card is expiring, pushing victims to scan a QR code or visit a URL to “activate” the card. The QR code redirects to a fake banking site that harvests login and account details, potentially giving…

September 26, 2026
Soldier Used Others’ Email to Get Exploit Help

Soldier Used Others’ Email to Get Exploit Help

A U.S. Army soldier ("Kiberphant0m") tied to major telecom data thefts was sentenced to 70 months in prison. Prosecutors say that while jailed, he used other inmates’ email accounts to get someone on the outside to ask commercial AI tools for vulnerability details and even “real world working”…

September 25, 2026
Fake “Google Security” Vishing Script Exposed

Fake “Google Security” Vishing Script Exposed

Researchers spotted a Telegram job ad recruiting callers to impersonate the “Google Account Security Team” and run voice-phishing calls. The ad absurdly claimed “NO SCRIPT READING” while also publishing the exact phone script to use, showing a repeatable, real-world vishing workflow.

September 25, 2026
Drive‑By RCE via VS Code DebugMCP Server

Drive‑By RCE via VS Code DebugMCP Server

Researchers reported a critical issue in Microsoft’s DebugMCP (v1.1.4) where a developer could be tricked into visiting a malicious webpage and end up with attacker code running on their machine. The attack abuses a locally running, unauthenticated server on port 3001 plus DNS rebinding to send a…

September 25, 2026
Android Trojan Pushed via Fake Google Play Pages

Android Trojan Pushed via Fake Google Play Pages

A new Android banking trojan called RemControl is being distributed through fake Google Play pages pretending to offer the TVTap IPTV app. After victims install it and grant powerful Accessibility permissions, it can place fake login screens over real banking apps and give attackers remote control…

September 25, 2026
Fake “Wavel” Wallet Site Drops PamStealer on Macs

Fake “Wavel” Wallet Site Drops PamStealer on Macs

Researchers report a new PamStealer variant that lures macOS users to a fake cryptocurrency wallet website and tricks them into running a script-based installer. The malware downloads a decryption tool and relies on a live server key exchange, making the real payload harder to analyze and helping…

September 25, 2026
Fake Cloudflare CAPTCHA Pushes MSI Malware

Fake Cloudflare CAPTCHA Pushes MSI Malware

Attackers compromised real Ukrainian business websites and showed visitors a fake Cloudflare verification page. The lure tricks people into running a Windows Installer command (via Windows+R), which installs “Psychedelic Stealer” to steal saved browser passwords and cryptocurrency wallet data.

September 25, 2026
Rust Maintainers Phished via Fake “Conference Call”

Rust Maintainers Phished via Fake “Conference Call”

An unknown group suspected to be North Korean state hackers targeted Rust language team members and high-profile package (“crate”) maintainers with phishing that lures victims into a fake conference call. When the victim tries to join, they are told they must install a “video codec” or update…

September 25, 2026
Placeholder Domain Hijacked for ClickFix Scam

Placeholder Domain Hijacked for ClickFix Scam

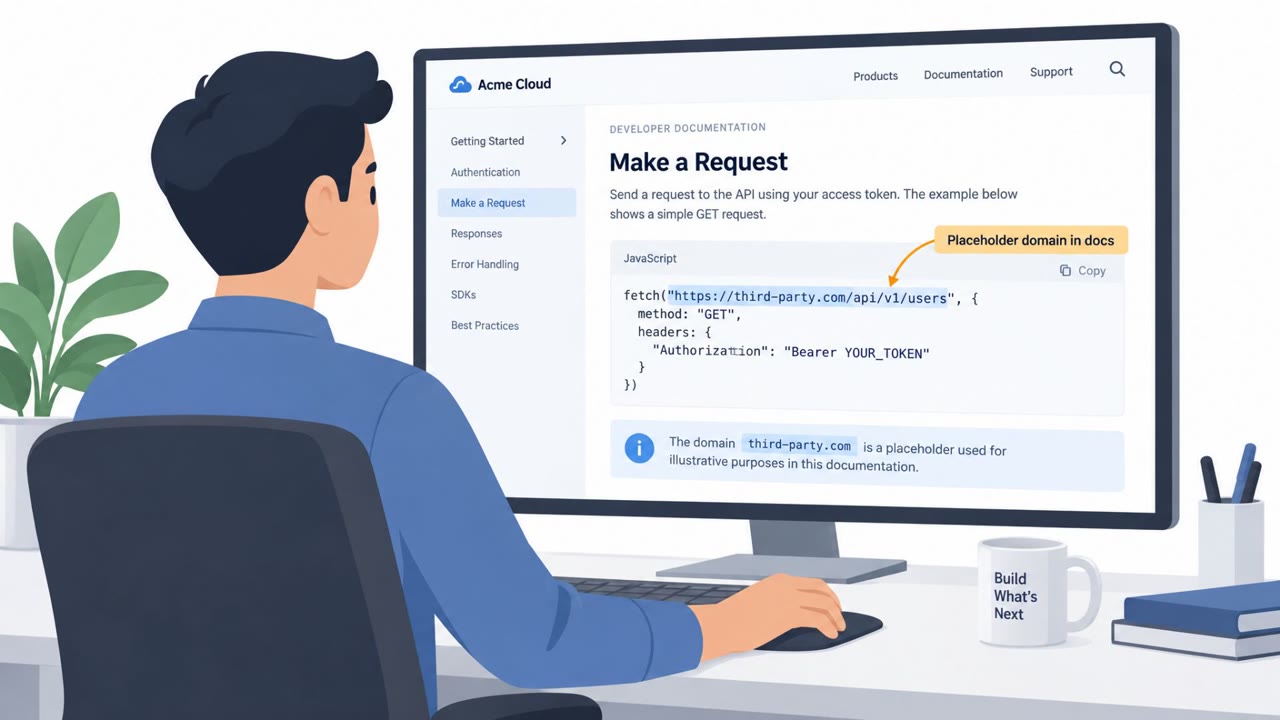
Attackers registered a long-used “placeholder” domain (third-party[.]com) that appears in developer documentation and code examples, then used it to trick Windows visitors with a fake Cloudflare-style verification page. The site tries to convince people to open the Windows Run box and paste a…

September 25, 2026
EvilTokens Device-Code Phishing Hits 12K Inboxes

EvilTokens Device-Code Phishing Hits 12K Inboxes

Microsoft says it disrupted “EvilTokens,” an AI-powered phishing-as-a-service operation used to break into email accounts at scale. The service automated device-code login phishing end-to-end, helping criminals steal authentication tokens and enable business email compromise across more than 10,000…

September 25, 2026
Bitcoin ATM Payment Demand? It’s a Scam Script

Bitcoin ATM Payment Demand? It’s a Scam Script

The article describes a common fraud pattern where scammers impersonate police, government officials, or other trusted authorities over the phone to pressure victims into paying via a Bitcoin/crypto ATM. The victim is told their money is at risk, instructed to withdraw cash, and then directed to…

September 25, 2026
SalesBleed: Poisoned Leads Trigger Slack Phish

SalesBleed: Poisoned Leads Trigger Slack Phish

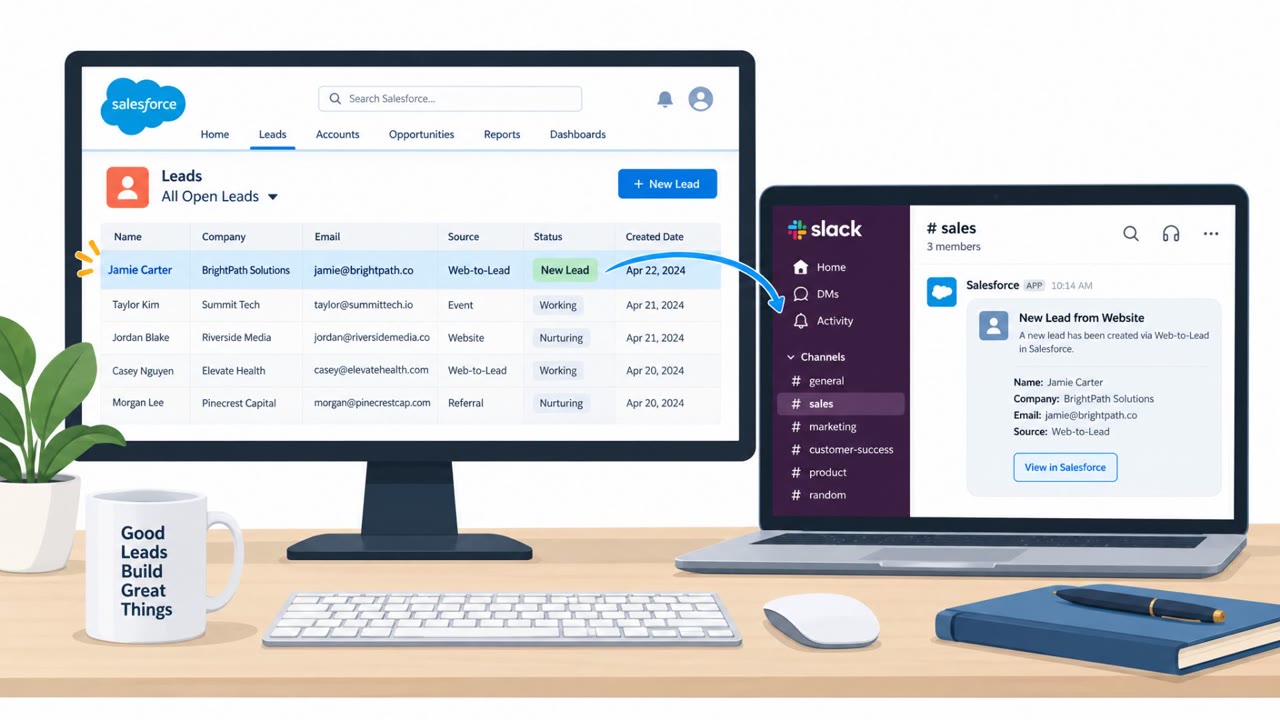
Researchers say three “SalesBleed” flaws in Salesforce Agentforce could let attackers plant malicious instructions inside a Web-to-Lead form submission that later causes an Agentforce agent to leak CRM data or post phishing in Slack. The attack can stay hidden until an employee asks Agentforce to…

September 25, 2026
Fake TVTap Pages Push RemControl Banking Trojan

Fake TVTap Pages Push RemControl Banking Trojan

Researchers say a new Android banking trojan (“RemControl”) tricks people into installing a fake TVTap app update from spoofed Google Play-style pages. Once installed, it persuades victims to grant Accessibility permissions, giving attackers remote control and enabling theft of banking credentials…

September 25, 2026
AliExpress Fake Site Pushes “Add to Browser” Scam

AliExpress Fake Site Pushes “Add to Browser” Scam

Researchers tracked a live phishing flow that used 10 newly-registered “disposable” domains as entry points that redirected visitors to a fake AliExpress-themed site. The end site impersonated a shopping-assistant brand and pushed a browser extension, putting users at risk of credential and payment…

September 25, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo