U.S. prosecutors charged three people with allegedly using AI-generated CEO and attorney impersonations to steal about $129 million from companies worldwide. The group reportedly emailed accounting teams about confidential transactions, used AI voice and video calls to reinforce the request, and then directed employees to a fake attorney who instructed them to wire money.
How the attack worked
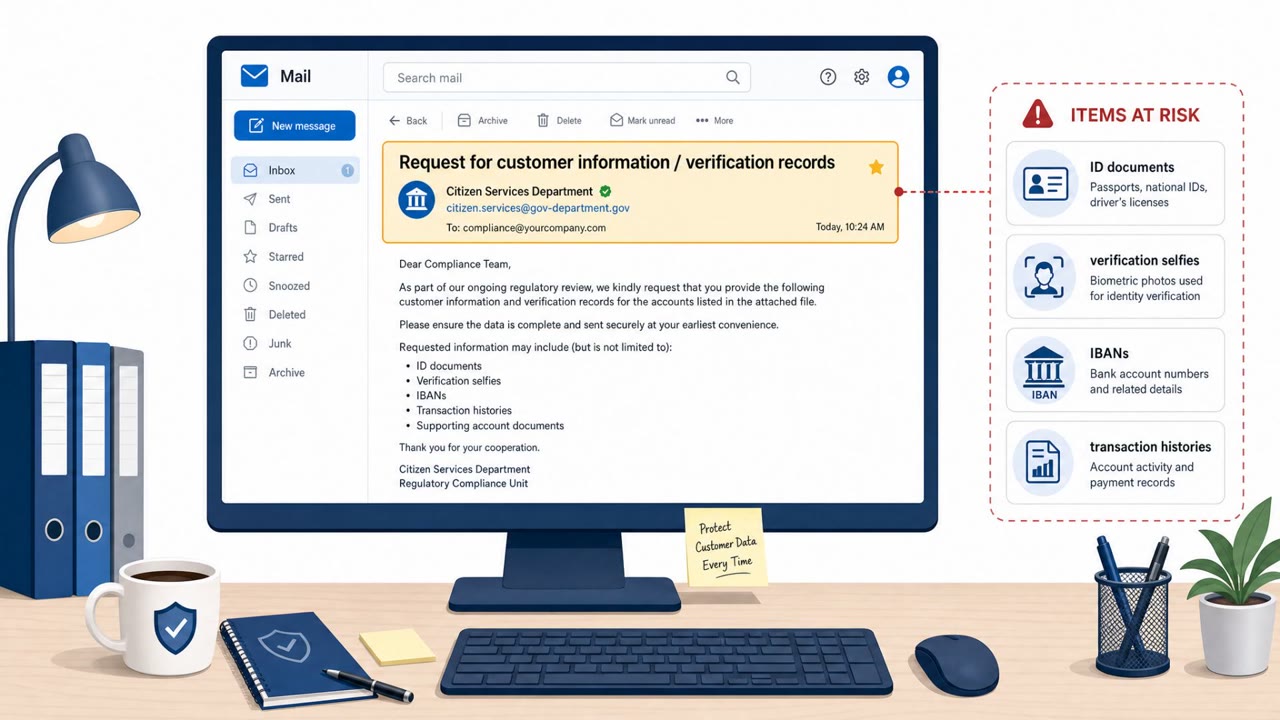
Prosecutors allege three defendants ran a scheme targeting thousands of companies worldwide over more than a year and a half, allegedly stealing around $129 million. The attack began with an email sent to accounting departments, purporting to come from the company's CEO and asking for help with a confidential financial transaction. To reinforce the request, the group allegedly coordinated a phone or video call using AI to mimic the CEO's voice and, at times, their image. Once the employee was engaged, the attackers directed them to contact an attorney at a major law firm, who was also impersonated, and that fake attorney instructed the employee to wire large payments to bank accounts across the world. Prosecutors allege the funds were then converted to cryptocurrency to obscure their origin before being distributed among the participants.
Why it succeeded
This scheme combined several pressure points that are difficult for an individual employee to resist in the moment:
- A request appearing to come directly from a senior executive, carrying implicit authority.
- Emphasis on confidentiality, which discourages employees from checking with colleagues or managers.
- AI-generated voice and sometimes video, which made the impersonation feel more credible than a text-only email.
- A second impersonated authority figure, a law firm attorney, that added legitimacy to the wire instructions.
- Routing the transaction outside normal approval channels by relying on an unverified call rather than established internal processes.
What to watch for
Accounting, finance, treasury, accounts payable, payroll, executive assistants, legal staff, and senior executives should watch for:
- An unusual, confidential financial request sent directly to accounting rather than through normal channels.
- Pressure to act quickly or outside standard payment-approval procedures.
- A request that relies on a phone or video call instead of verified internal contact methods.
- Being directed to a new attorney or legal contact in connection with an executive's financial request.
- Instructions to wire large payments to unfamiliar accounts, especially overseas.
How to build resistance
- Treat any unexpected executive request for a confidential payment as high risk and verify it through a known, independent contact method before acting.
- Do not treat a familiar-sounding voice or video image as proof of identity; rely on established callback and approval procedures for high-value payments.
- Independently verify attorneys and payment instructions through a trusted law-firm contact directory rather than information provided during the call.
- Require out-of-band confirmation and multi-person approval for large or unusual wire transfers, particularly when urgency or secrecy is emphasized.
Key findings
- Three defendants allegedly targeted thousands of companies globally over more than a year and a half.
- The operation focused on accounting departments and began with emails pretending to come from the CEO.
- The group allegedly used AI to mimic the CEO's voice and, at times, image during phone or video calls.
- Victims were directed to an impersonated major-law-firm attorney who instructed them to wire large payments to overseas accounts.
- Prosecutors allege the funds were converted to cryptocurrency to obscure their origin before distribution to the participants.
Who’s being targeted
- Commonly targeted roles: Accounting, Finance, Treasury, Accounts Payable, Payroll, Executive assistants, Legal, Senior executives.
- Affected industries: Healthcare, Banking, Financial technology, Investment management, Pet food manufacturing.
- Attack channels: email, vishing.
- Impersonated: Company CEO, Attorney at a major law firm.
Red flags to watch for
- An unusual confidential financial request sent directly to accounting.
- Pressure to act outside normal payment-approval procedures.
- A request that relies on an unverified phone or video call rather than known internal contact methods.
- The attorney is introduced through an unexpected executive request rather than a verified legal-contact process.
- The request directs a large wire payment to an unfamiliar account.
- The caller's identity is not verified using a known, independently sourced law-firm phone number.
Frequently asked questions
How did the AI CEO deepfake fraud scheme work?
Attackers emailed accounting departments posing as the CEO requesting help with a confidential financial transaction, then followed up with phone or video calls using AI to mimic the CEO's voice and sometimes image, before directing victims to wire money through an impersonated attorney.
Why did accounting employees fall for the fake CEO calls?
The use of AI-generated voice and video made the calls sound and look like a real executive, and the requests were framed as urgent and confidential, pressuring employees to bypass normal payment verification steps.
Who was impersonated in this scheme?
The defendants allegedly impersonated company CEOs and an attorney at a major law firm to convince accounting staff to wire large payments to overseas bank accounts.
How can organizations defend against this type of fraud?
Treat unexpected executive payment requests as high risk, verify callers through known independent contact methods, require multi-person approval for large wires, and never rely on voice or video alone as proof of identity.
Read the video transcript
Your CEO calls about a secret deal. Sounds real? That’s the trap. In an alleged $129 million scheme, accounting teams got emails saying, ‘I need your help with a confidential financial transaction.’ Then came a call with an AI-mimicked CEO voice, and sometimes video. Next, a supposed major-law-firm attorney gives overseas wire instructions. Here’s the giveaway: the familiar voice doesn’t verify the request. Secrecy plus a new account bypasses normal approvals. Before any wire, call your CEO using the number in your company directory, not the number in that email.