A real malware campaign called Yoba used fake GitHub projects advertising supposed ChatGPT and Claude desktop applications. Victims were lured by high-ranking Google results and download buttons, then ran ZIP-packaged installers that appeared legitimate but gave attackers control of the device. The campaign used trusted signed software to help hide the malware, making unofficial downloads especially risky.
How the attack worked
The Yoba campaign relied on counterfeit GitHub projects that posed as desktop versions of popular AI tools, using names like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. These projects used GitHub Pages sites to describe the fake software and displayed download buttons that pointed to ZIP files stored in GitHub Releases. Inside the ZIP was a legitimate signed Setup.exe bundled with a malicious DLL. Once run, the malware established persistence through a scheduled task disguised as a Microsoft component and ultimately delivered an XMRig cryptocurrency miner, communicating through Tor.
Why it succeeded
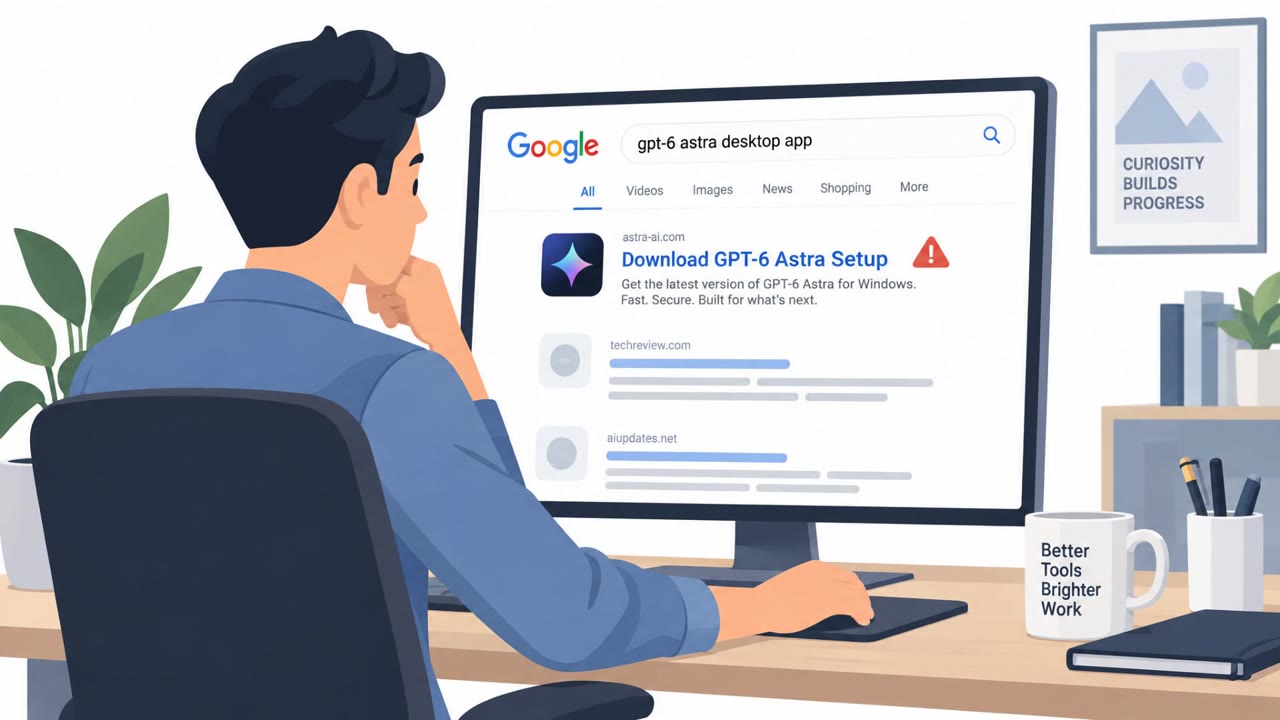
The campaign exploited trust in two places at once: search engine rankings and GitHub itself. SEO poisoning tuned titles, descriptions, and hosting domains so the fake projects appeared near the top of Google results, even though they had no connection to OpenAI or Anthropic. Because many developers and knowledge workers already trust GitHub as a platform, the projects looked credible to visitors who assumed that ranking highly and being hosted on a well-known code repository implied legitimacy. Bundling a legitimate signed installer alongside the malicious DLL added another layer of apparent authenticity.
What to watch for
- Software offered through an unofficial GitHub project rather than a vendor's official website.
- Product names suggesting unreleased or unfamiliar versions, such as GPT-5.6 Sol or GPT-6 Astra.
- A high Google search ranking or a GitHub download button treated as proof of legitimacy.
- Downloads delivered as ZIP files instead of installers from an official vendor site.
- Repository pages where the owner, account age, commit history, and contributor activity have not been verified.
How to build resistance
Organizations and individuals can reduce exposure to campaigns like Yoba by reinforcing a few habits. Download AI tools only from official vendor websites such as openai.com or anthropic.com, rather than from search results or third-party GitHub projects. Treat a high Google ranking as a discovery aid, not proof of safety, since SEO poisoning can place malicious pages above legitimate ones. Before trusting any GitHub-hosted tool, check the repository owner, account age, commit history, and whether it has genuine contributors. Finally, avoid running unfamiliar software with administrator rights and involve IT review when a tool requests elevated permissions, since limiting administrator access and blocking unknown software sources can reduce the damage from campaigns that reuse this approach under new branding as AI tools evolve.
Key findings
- The Yoba campaign used counterfeit GitHub projects for alleged AI desktop apps called GPT-5.6 Sol, GPT-6 Astra, and Claude Opus.
- Attackers used SEO poisoning to place the fake projects near the top of Google search results, exploiting trust in both search rankings and GitHub.
- Download buttons led to GitHub Release ZIP files containing a legitimate signed Setup.exe alongside a malicious DLL.
- The malware established persistence through a scheduled task disguised as a Microsoft component and ultimately delivered an XMRig cryptocurrency miner through Tor.
- The same operators had previously used a Cursor.exe lure, showing that the campaign can change branding as AI tools become popular.
Who’s being targeted
- Commonly targeted roles: Developers, IT and help desk teams, Knowledge workers, Employees using AI tools, Students and researchers, Security operations teams.
- Affected industries: Technology and software development, Information and Media, Professional Services, Education, Any organization with employees downloading AI tools.
- Attack channels: website.
- Impersonated: OpenAI or Anthropic AI software project, ChatGPT or Claude application provider.
Red flags to watch for
- The software is offered through an unofficial GitHub project rather than the vendor's official website.
- The product name suggests an unreleased or unfamiliar version, such as GPT-5.6 Sol or GPT-6 Astra.
- A search result or GitHub download button is treated as proof that the software is legitimate.
- The result ranks highly in Google but is not hosted on openai.com or anthropic.com.
- The repository owner, account age, commit history, and contributor activity are not verified.
- The download is a ZIP file instead of an installer obtained from the official vendor site.
Frequently asked questions
How did the Yoba malware campaign trick victims?
Attackers created fake GitHub projects advertising desktop apps named GPT-5.6 Sol, GPT-6 Astra, and Claude Opus, then used SEO poisoning so the pages ranked near the top of Google search results.
What happened after someone downloaded the fake AI app?
The ZIP file from GitHub Releases contained a legitimate signed Setup.exe alongside a malicious DLL, which established persistence disguised as a Microsoft component and ultimately delivered an XMRig cryptocurrency miner through Tor.
How can users avoid fake AI tool downloads like this?
Download AI tools only from official vendor websites such as openai.com or anthropic.com, and before trusting a GitHub project, check the repository owner, account age, commit history, and real contributor activity.
Why did this campaign succeed despite being hosted on GitHub?
Because many developers trust GitHub as a platform, the fake projects looked legitimate, and a high Google ranking was mistaken for proof of safety even though it resulted from SEO poisoning.
Read the video transcript
Google puts “GPT-6 Astra” near the top. Looks promising? That’s SEO poisoning. Yoba’s fake GitHub projects advertise GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. Their download buttons lead to GitHub Release ZIPs. Here’s the trap: the ZIP pairs a signed Setup.exe with a malicious DLL. Run it, and Yoba can persist as a fake Microsoft task, then fetch an XMRig miner through Tor. A top result isn’t a trusted download. For AI apps, go directly to openai.com or anthropic.com.