North Korean-linked attackers reportedly used a fake job opportunity, multiple interviews, and a malicious coding assignment to compromise a Binance engineer. The scheme built trust over weeks before asking the employee to download an interview file, giving attackers a foothold in the company’s systems. Similar “contagious interview” campaigns have also targeted crypto holders, wallets, and organizations.
How the attack worked
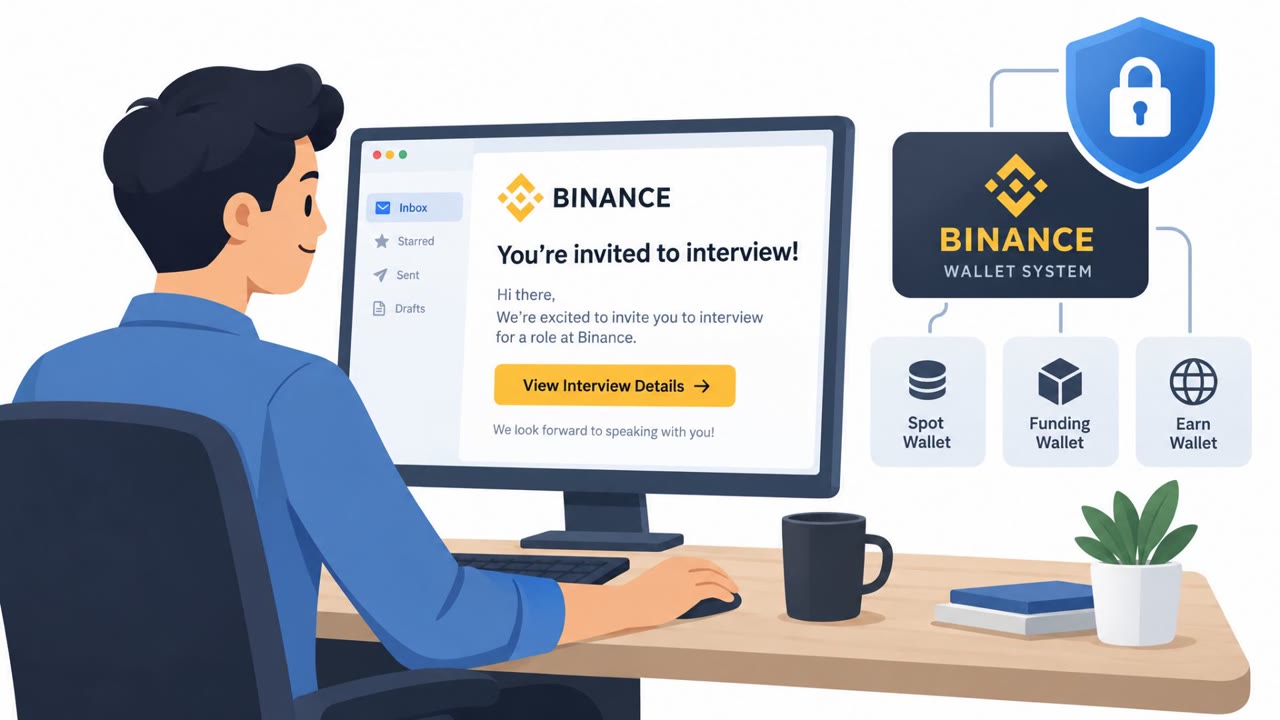
The operation reportedly began with an approach through a legitimate job platform, where attackers posed as a recruiter for a fictitious technology company. Over several weeks, the Binance engineer completed two rounds of credible interviews before being asked to download an interview assignment as the next step in the hiring process. That assignment contained malicious code, which gave the attackers their initial foothold. From there, they deployed malware and moved deeper into Binance systems. This pattern, sometimes called a contagious interview scheme, has reportedly been used in similar form against other crypto holders, wallets, and organizations.
Why it succeeded
The scheme worked because it mirrored a normal hiring process rather than looking like an obvious phishing attempt. Multiple interview rounds built trust over time, making a request to download a file feel like a routine part of the recruitment pipeline rather than a red flag. The target was also valuable: employees with access to sensitive infrastructure are particularly attractive to attackers because their credentials and permissions can open a path into internal systems well beyond their own device.
What to watch for
- Unsolicited recruiting outreach for a role at an unfamiliar or unverifiable company
- A hiring process that asks candidates to download and run code or files from an external source
- Pressure to execute an interview assignment directly on a work device instead of reviewing it in a safe, approved environment
- A long or highly convincing interaction, since attackers may deliberately build trust over weeks before making the critical ask
How to build resistance
Organizations should treat recruiting-themed outreach toward employees with privileged access as a potential security concern, not just an HR matter. Interview assignments or coding exercises should go through an approved review process, ideally in an isolated environment, before ever touching a corporate device. Because credentials and files stolen in these schemes have reportedly led to losses beyond the infected device, including wallet private keys taken from cloud storage, response plans should extend to cloud accounts, browser sessions, and password managers, not just local file cleanup. Recruiting and HR teams, along with security engineers and IT administrators, benefit from shared awareness that a convincing, multi-step interview process does not by itself confirm legitimacy.
Key findings
- Attackers reportedly approached a Binance engineer through a legitimate job platform and built trust over several weeks.
- The employee completed two interviews with a fictitious company before being sent a malicious interview assignment to download.
- The malicious assignment gave attackers an initial foothold, after which they deployed malware and moved deeper into Binance systems.
- Chainalysis attributed more than $14.3 million in losses over 18 months to similar DPRK-linked fake-interview and malware schemes.
- The broader DPRK employment-fraud model includes operatives posing as job applicants to obtain legitimate employment and access sensitive systems.
- Victims in other cases reportedly had wallet private keys stolen from cloud storage, indicating risk beyond files stored directly on the infected device.
Who’s being targeted
- Commonly targeted roles: Software Engineers, Developers, DevOps and Cloud Engineers, Security Engineers, Cryptocurrency and digital-asset staff, IT administrators, Employees with privileged access, Recruiting and Human Resources teams.
- Affected industries: Cryptocurrency exchanges, Financial services, Blockchain and digital-asset companies, Decentralized autonomous organizations (DAOs), Technology companies, Organizations employing remote technical staff.
- Attack channels: linkedin, website, email.
- Impersonated: Recruiter or hiring manager from a fictitious technology company.
Red flags to watch for
- The role is offered through an unfamiliar or unverifiable company.
- A recruitment process asks the candidate to download code or files from an untrusted source.
- The assignment requires execution on a work device rather than review in a safe, approved environment.
Frequently asked questions
How did the fake interview attack on Binance work?
Attackers approached a Binance engineer through a legitimate job platform, conducted two rounds of interviews as a fictitious company, then sent a malicious coding assignment that gave them an initial foothold once downloaded.
Why are employees with privileged access targeted by these schemes?
DPRK-linked actors reportedly use these recruiting lures specifically against employees with privileged infrastructure access, since compromising their credentials provides a path into internal systems.
Is it safe to download a coding assignment during a job interview?
Interview assignments should only be downloaded or run after independently verifying the recruiter and company, and ideally only inside an approved, isolated review environment rather than on a corporate device.
What should be protected if a device is suspected of compromise from this type of attack?
Beyond files on the device itself, cloud storage, browser sessions, password managers, and cryptocurrency wallets should be secured, since credentials gathered early can unlock connected accounts.
Read the video transcript
Two interviews. Weeks of trust. Then a download. A Binance engineer was approached on a legitimate job platform. A fictitious company held two interviews, then sent a coding assignment containing malicious code. That's the contagious-interview trick: the interviews make the file feel safe. Opening it gave access to the work device, then deeper systems. Cloud-stored wallet keys can be exposed too. Before opening any interview assignment on a work device, send it through your approved security review process.