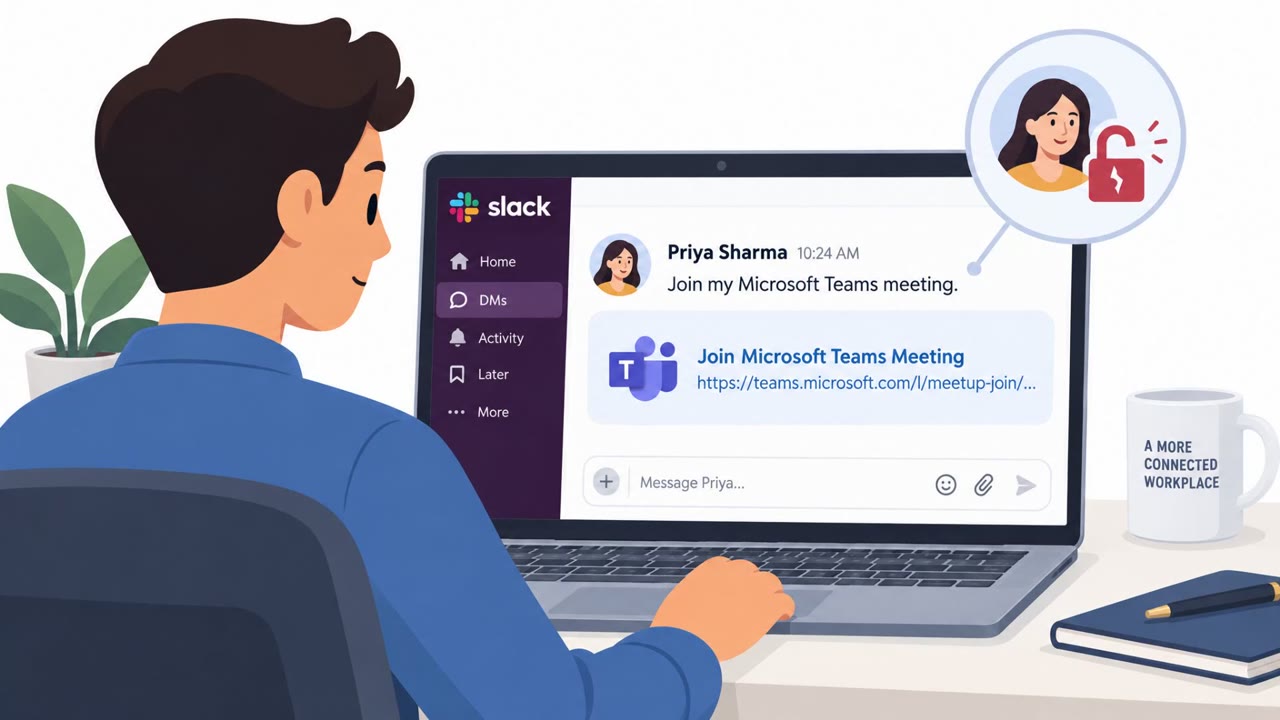
U.S. authorities disrupted North Korea’s “FaceStealer” campaign, which used stolen webcam footage and AI-generated deepfakes to lure people into video calls. During the calls, attackers claimed there was a technical problem and persuaded victims to install supposed fixes that actually delivered cryptocurrency-stealing malware. Technology and cryptocurrency workers, along with maintainers of widely used open-source software, were key targets.
Key findings
- North Korean operators used more than 900 webcam videos, largely taken from prior victims, to make fraudulent video calls appear legitimate.
- Attackers claimed a technical error was disrupting the call and convinced targets to install software that delivered malicious code.
- The campaign targeted technology-company employees, especially cryptocurrency firms, and expanded to maintainers of critical open-source software packages.
- In one reported case, a video call appearing to include a trusted contact persuaded an open-source project maintainer to install malware.
- The compromise enabled delayed theft, including cryptocurrency theft, account hijacking, and access to contacts and communications applications.
Who’s being targeted
- Commonly targeted roles: Technology employees, Cryptocurrency and digital-asset employees, Software developers, Open-source maintainers, Software supply-chain teams, IT support and security teams.
- Affected industries: Technology companies, Cryptocurrency and digital-asset firms, Open-source software development, Software supply chain.
- Attack channels: vishing.
- Impersonated: A seemingly legitimate video-call participant, potentially presented using a previous victim’s webcam video or an AI-generated deepfake, A trusted contact appearing on a video call.
Awareness takeaways
- Do not install software because someone on an unexpected video call says it will fix a technical problem; end the call and verify through an approved support channel.
- Treat video presence as insufficient identity proof, especially when a caller claims to be a trusted contact or influential person.
- Software developers and package maintainers should require established review and approval processes before installing tools or changing dependencies, even when requests appear to come from trusted people.
- Report suspected compromise quickly, since attackers may wait months before stealing funds or taking over accounts.
Red flags to watch for
- An unexpected participant asks you to install software during a call.
- The requested software is not from your organization’s approved support process.
- The caller’s identity is supported only by video appearance, which may be reused footage or a deepfake.
- A trusted-looking contact on video asks for a software installation outside normal development controls.
- The request bypasses code review, approved tooling, or established package-maintenance procedures.
- A call is used to create urgency around a change affecting a widely downloaded software package.
Read the video transcript
Recognize someone on a video call? That’s not proof it’s them. North Korea’s FaceStealer campaign used over 900 webcam videos and AI deepfakes. A caller says, ‘Technical error, install this software so we can continue.’ That ‘fix’ is malware. One trusted-looking call fooled an open-source maintainer; the infection can lead to stolen crypto, hijacked accounts, or poisoned dependencies. If a caller asks you to install a fix, end the call and contact approved IT support.