Entrust reports that fraudsters are using virtual cameras and device emulation to submit fabricated or replayed images and videos during online identity checks. The report also describes scammers persuading real customers or employees to complete verification or authorize actions, turning legitimate people into participants in fraud.
How the Attack Works
This attack breakdown centers on a reported rise in identity verification fraud that exploits both technical weaknesses and human trust. According to Entrust's findings, deepfake detections rose 165% year over year, reflecting a growing reliance on synthetic or manipulated media to pass identity checks.
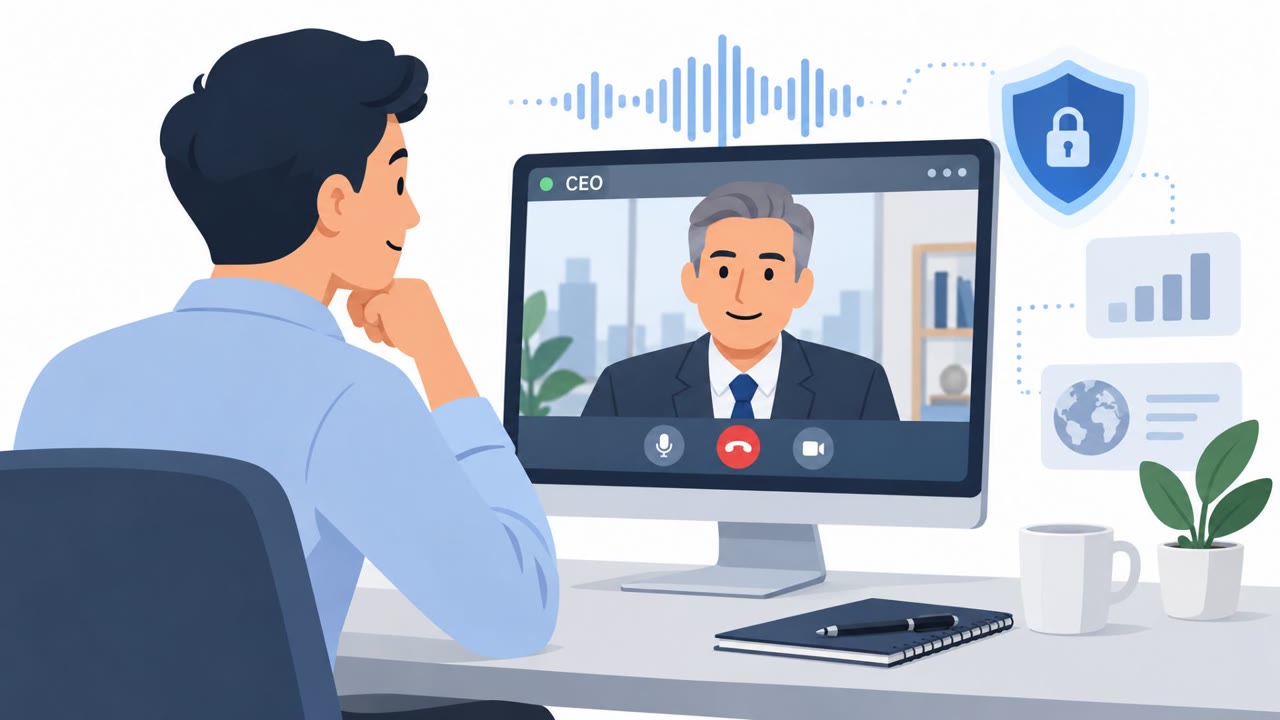
Two technical methods stand out. First, injection attacks feed fabricated images or video directly into verification software, bypassing the device's camera entirely. This is often paired with a virtual camera that presents fabricated footage as if it were a live recording, while device emulation software imitates the phone or computer supposedly submitting the data. Second, stolen photographs and videos, even genuine ones taken from someone else, can be replayed during a verification session without the rightful owner's knowledge or consent.
The Human Element
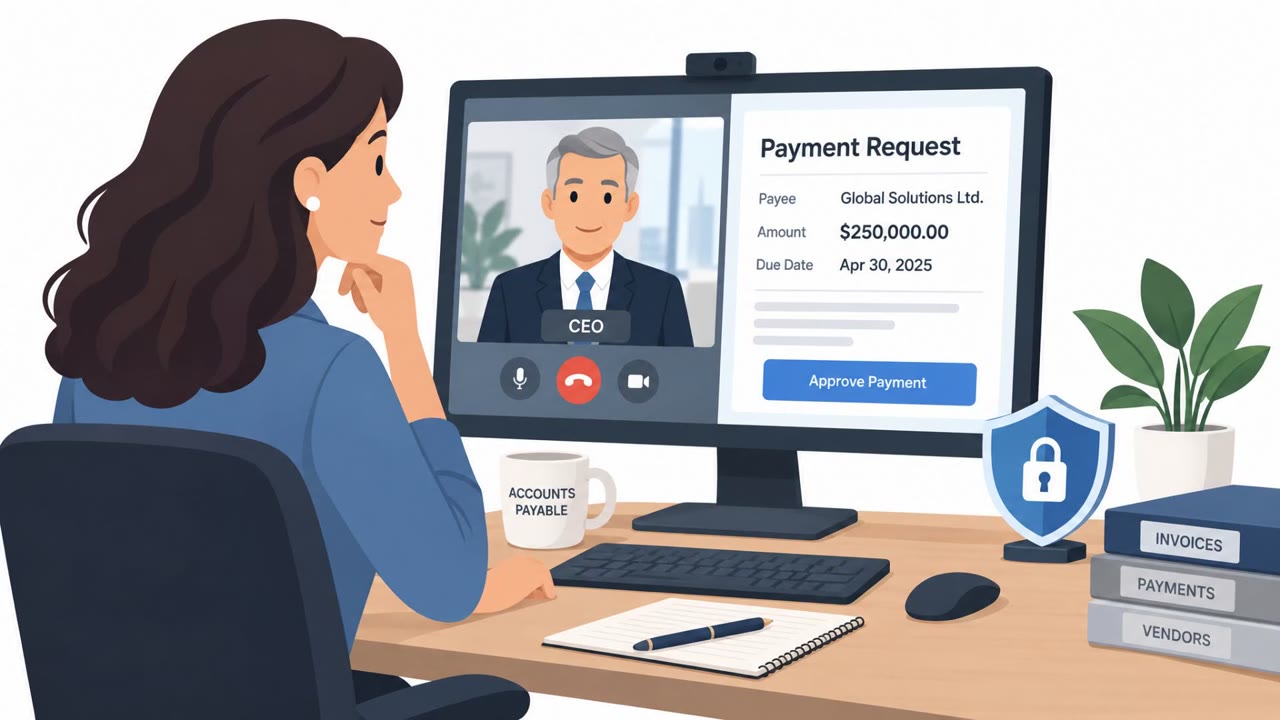
Beyond technical spoofing, the report highlights a social engineering dimension: scammers manipulate real customers or employees into completing identity checks or authorizing actions on the fraudster's behalf. In these cases, the person performing the verification is genuine, but they have been persuaded, under false pretenses, to use their own documents and biometric information in service of someone else's fraud.
This matters because it means identity verification fraud cannot be fully solved by better camera or liveness detection alone. A customer who is tricked into completing a verification step is submitting authentic biometric data, which can pass technical checks even though the underlying transaction is fraudulent.
Why It Succeeds
The combination of technical spoofing and social manipulation succeeds because each method targets a different layer of trust. Device emulation and virtual cameras exploit the assumption that a live camera feed is inherently trustworthy. Manipulating customers or employees exploits the assumption that genuine credentials submitted by a real person indicate a legitimate transaction. Financial services are particularly exposed because verified accounts can unlock access to funds and can be repurposed to support money laundering and further fraud.
What to Watch For
- A camera feed that may originate from a virtual camera rather than a physical device camera
- Device emulation signals suggesting the submitting phone or computer is not genuine
- Seemingly authentic photos or videos that may actually be replayed by someone without rights to use them
- Unsolicited instructions urging a customer or employee to quickly complete a verification step or approve a transaction
Building Resistance
Organizations should treat identity checks as high-risk transactions, verifying that the camera feed and submitting device are genuine rather than relying on how convincing an image appears. Device intelligence that examines the camera, device, and session involved in a submission can help flag irregularities. Equally important is training customers and employees not to follow unsolicited instructions to complete verification, approve transactions, or disclose information, and to independently confirm such requests through an official channel before acting.
Key findings
- Deepfake detections rose 165% year over year in Entrust's dataset.
- Injection attacks can bypass a device camera by using a virtual camera to present fabricated footage as a live recording.
- Device emulation software can imitate the phone or computer making an identity-verification submission.
- Stolen photos and videos can be replayed during verification, even when the media itself is genuine.
- Scammers can manipulate customers into completing identity checks with their genuine documents and biometric information.
- Financial services are a major target because verified accounts can provide access to funds and support money laundering and further fraud.
Who’s being targeted
- Commonly targeted roles: Customers, Customer support teams, Identity verification reviewers, Fraud operations teams, Digital onboarding teams, Finance and payments approvers.
- Affected industries: Financial services, Online identity verification services, Digital account-opening services.
- Attack channels: website.
- Impersonated: A legitimate customer completing a live identity check.
Red flags to watch for
- The camera feed may originate from a virtual camera rather than the user’s physical device camera.
- Device-emulation signals may indicate that the submitting phone or computer is not genuine.
- A seemingly authentic photo or video may be replayed by someone who has no right to use it.
Frequently asked questions
What is an injection attack in identity verification?
It is a method where fraudsters feed fabricated images or video directly into verification software, bypassing the device's actual camera so the system accepts footage that was never genuinely captured live.
Can stolen photos or videos defeat identity verification even if the media is real?
Yes. Stolen photographs and videos can be replayed during a verification session, so even genuine media can be misused by someone who has no right to submit it.
Why are financial services a major target for this type of fraud?
Verified accounts can grant access to funds and can be used to support money laundering and further fraud, making financial services a high-value target for identity check manipulation.
Do employees need to worry about this, or just customers?
Both. Scammers also manipulate customers or employees into approving transactions, disclosing information, or completing identity checks using genuine credentials, turning legitimate people into unwitting participants.
Read the video transcript
That identity-check video looks live. What if it isn’t? Entrust calls this an injection attack: a virtual camera feeds fabricated or stolen video into verification, bypassing the real camera. Device emulation can make the submitting phone look genuine, too. Here’s the catch: even genuine footage can be replayed by someone else. And a scammer may persuade a real customer to complete the check for them. So if an identity check looks convincing, don’t just approve it. Verify the camera and device source first.