Binance said North Korean-linked TraderTraitor stole about $6.3 billion in cryptocurrency after a months-long attack involving fake job interviews and zero-day malware. Separately, Binance is investigating an unverified ShinyHunters extortion claim and warned customers to expect follow-on phishing attempts seeking passwords, 2FA codes, seed phrases, and private keys.
How the Attack Worked
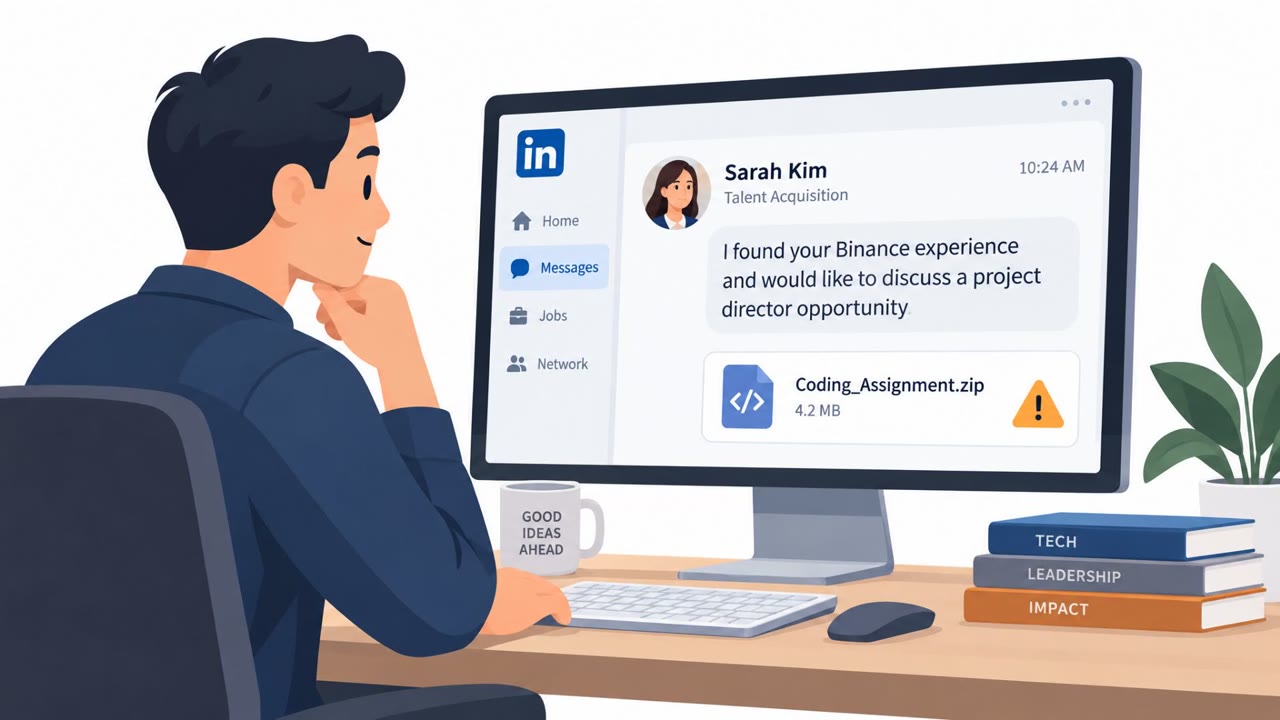
According to reporting, the TraderTraitor group, described as North Korean actors, carried out a months-long, multi-stage operation against Binance that combined fake job interviews with zero-day malware. This allegedly resulted in approximately $6.3 billion in virtual currency being stolen. The use of fake recruitment as an entry point reflects a broader pattern where technical job seekers, including software engineers and developers, are lured into interactions that ultimately deliver malware or compromise credentials.
Separately, Binance is investigating a claim from a group calling itself ShinyHunters, which said it possessed 335.9 million Binance customer records and demanded $900,000, framing the demand as "pay or leak." Binance stated this appears likely to be a scam rather than evidence of an actual systems breach.
Why It Succeeded
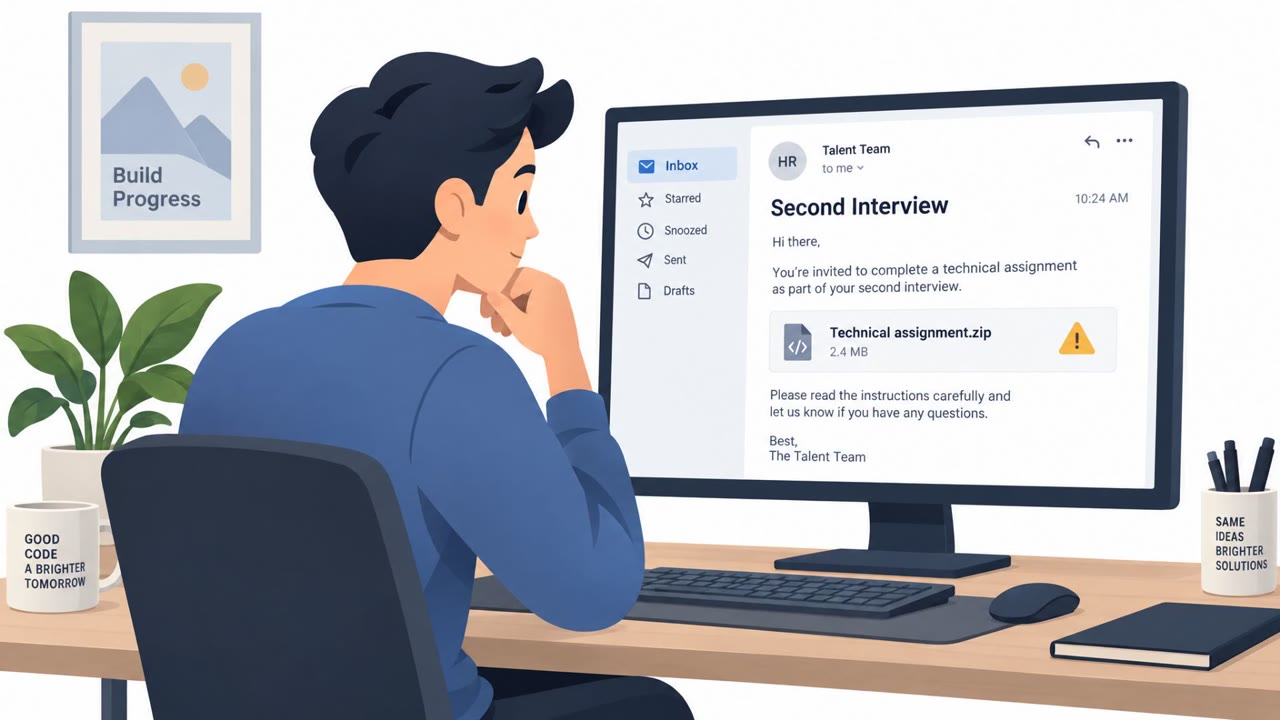
Fake job interviews work because they exploit trust built around a legitimate-seeming hiring process. Targets such as developers and technical job seekers may be asked to run code, open files, or install software as part of an interview exercise, activities that feel routine in a technical recruitment context but can deliver malware undetected. Combined with zero-day exploitation, this gave attackers a path into systems that standard defenses were not prepared to catch.
The extortion claim adds a second layer of risk: even when a breach claim is unverified, the surrounding uncertainty and urgency can be exploited to pressure customers and staff into hasty action.
What to Watch For
- Unsolicited recruitment outreach that asks you to download files, run code, or install tools before any formal hiring step
- Messages referencing a data breach or security incident that urge immediate action
- Any request for passwords, 2FA codes, seed phrases, or private keys, regardless of how official the message appears
- Communications that are not verifiable through a company's official support channels
Binance specifically warned users to be alert for follow-on phishing attempts seeking passwords, 2FA codes, seed phrases, and private keys in the wake of this incident.
Building Resistance
- Treat unsolicited job interviews, especially those involving software or files, as a potential security risk and verify the recruiter and employer through trusted channels before proceeding
- Never provide passwords, 2FA codes, seed phrases, or private keys in response to an unsolicited message, even one referencing an account-security incident
- Be skeptical of breach claims or urgent warnings that pressure action before you can independently confirm them through official support channels
- Encourage technical job seekers and cryptocurrency exchange staff to treat recruitment-related technical exercises with the same caution applied to unknown executables
This case illustrates how impersonation techniques, including fake recruiters, can bypass technical defenses by targeting human trust during a routine process like a job interview.
Key findings
- TraderTraitor, described as North Korean actors, allegedly stole around $6.3 billion in virtual currency from Binance.
- The theft followed a months-long, multi-stage attack that involved fake job interviews and zero-day malware.
- ShinyHunters claimed it possessed 335.9 million Binance customer records and demanded $900,000, but Binance said the claim was likely a scam and found no evidence of a systems breach.
- Binance warned users to watch for follow-on phishing attempts seeking passwords, 2FA codes, seed phrases, and private keys.
Who’s being targeted
- Commonly targeted roles: Software engineers, Developers, Technical job seekers, Cryptocurrency exchange employees, Cryptocurrency users, Customer support teams.
- Affected industries: Cryptocurrency exchanges, Financial services, Blockchain and digital-asset services.
Frequently asked questions
How did attackers use fake job interviews to steal cryptocurrency?
TraderTraitor, described as North Korean actors, ran a months-long, multi-stage attack involving fake job interviews and zero-day malware that allegedly resulted in about $6.3 billion stolen in virtual currency from Binance.
Is the ShinyHunters extortion claim against Binance confirmed?
No, Binance said the claim of possessing 335.9 million customer records was likely a scam rather than evidence of a systems breach, though ShinyHunters demanded $900,000.
What should users watch for after an incident like this?
Binance warned users to expect follow-on phishing attempts seeking passwords, 2FA codes, seed phrases, and private keys.
Who is being targeted in these schemes?
The targets include software engineers, developers, technical job seekers, cryptocurrency exchange employees, and cryptocurrency users.
Read the video transcript
A job interview can be the first step in a crypto theft. Binance says TraderTraitor used fake interviews in a months-long attack involving zero-day malware. The reported loss: roughly $6.3 billion in crypto. And a separate ShinyHunters breach claim? Binance found no evidence of a systems breach. A message about it could instead ask for your password, 2FA code, seed phrase, or private key. The tell: an interview wants a file, or an alert wants secrets. Verify it through the company's official site before doing anything.