Vishing + Fake Login Pages Speed Up Takeovers

eSecurity Planet · High sophistication
Last updated August 4, 2026

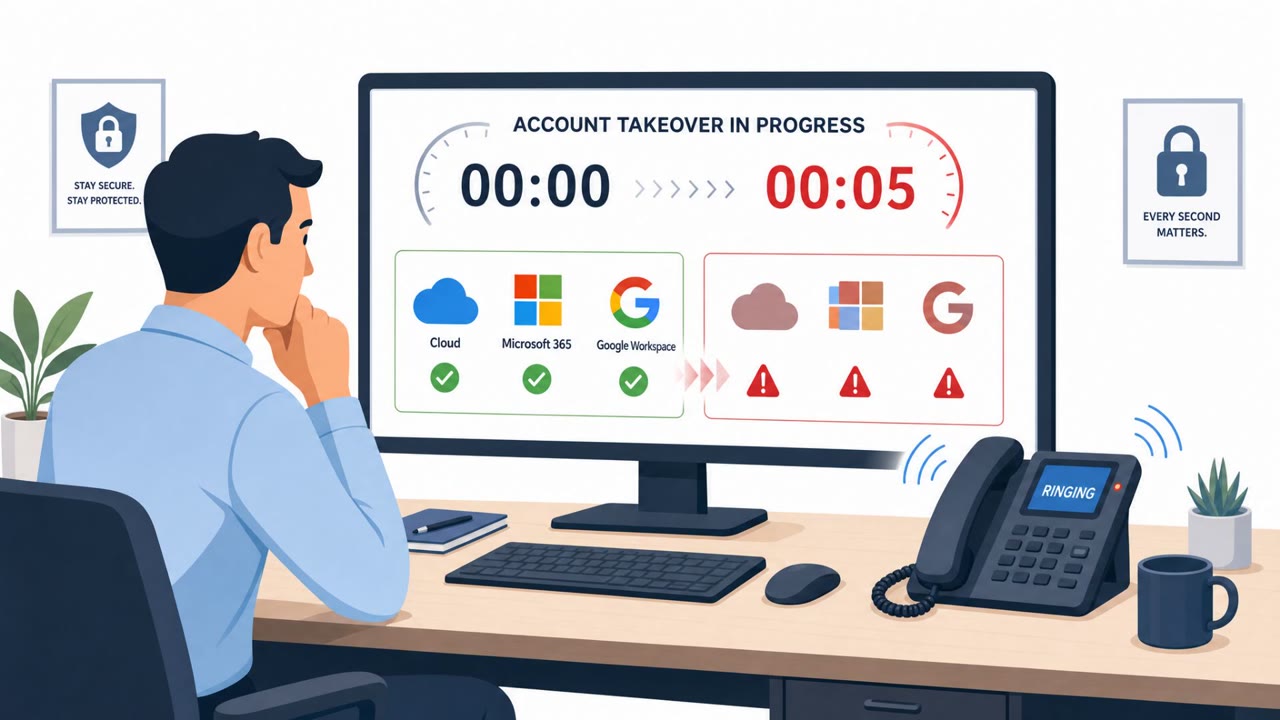
CrowdStrike’s threat hunting report says attackers are increasingly using phone-based impersonation and trusted login flows to break into cloud email and SaaS quickly. The report highlights vishing callers posing as IT support, pushing employees to sign in via attacker-controlled phishing pages, enabling rapid takeover and data theft in minutes.

Key findings

  • CrowdStrike reported a twofold increase in vishing intrusions in the first half of 2026 compared with late 2025.
  • Threat groups impersonated IT personnel and convinced users to authenticate via adversary-in-the-middle (AiTM) phishing pages.
  • Attackers then accessed Microsoft 365 and Google Workspace; one incident went from takeover to data theft in under five minutes.
  • The report also found a 15-fold increase in OAuth device code phishing abusing legitimate Microsoft authentication workflows.

Who’s being targeted

  • Commonly targeted roles: All employees, Executives, IT helpdesk/service desk, Finance, HR.
  • Affected industries: Technology, Financial services, Academic organizations.
  • Attack channels: vishing, website.
  • Impersonated: Internal IT personnel / Helpdesk.

Awareness takeaways

  • Treat unexpected ‘IT support’ calls as suspicious; verify using a known internal number or ticketing system before taking action.
  • Be cautious of any request to sign in during a phone call, attackers may use lookalike login pages to capture access.
  • Respond fast to suspected account compromise because attackers can steal data within minutes once they get access.
  • Train users on modern ‘legitimate workflow’ scams (like OAuth device code prompts) that can steal cloud tokens without ‘hacking’ a password directly.

Red flags to watch for

  • Unsolicited IT call pressuring immediate authentication
  • Being redirected to a login page as part of a phone call
  • Requests to authenticate that don’t match normal IT processes
Try Mirage

Mirage safely runs attacks like this one against your own team, so you find out what happens before a real adversary does.

Get a demo
Read the video transcript

Imagine this: you pick up the phone and hear, “This is IT personnel calling to help you authenticate.” CrowdStrike saw vishing like this double in 2026. Groups like CORDIAL SPIDER and SNARKY SPIDER pose as IT, then walk you to a “secure” Microsoft 365 or Google Workspace login page. Here’s the trick: they use adversary-in-the-middle phishing pages and OAuth device code prompts that look legit. You type your password, approve the sign-in, and in under five minutes they’re inside your email and files. Aha moment: real IT will never make you log in while you’re on the call. If anyone does, hang up and contact IT using our official helpdesk or ticketing system instead.

Similar attacks

Vishing and Device-Code Tricks Drive Cloud Takeovers

Vishing and Device-Code Tricks Drive Cloud Takeovers

CrowdStrike reports attackers increasingly bypass security tools by using trusted login paths, phone-based IT impersonation, and abuse of legitimate cloud and AI services. The report highlights real intrusions where vishing led to single sign-on takeovers and rapid data theft, and where attackers…

August 6, 2026
ChatGPT Billing Phish and Fake Snap Support Scams

ChatGPT Billing Phish and Fake Snap Support Scams

This roundup describes real-world social engineering, including phishing emails that impersonate ChatGPT billing to steal payment card data and a convicted attacker who posed as Snapchat support to trick people into handing over login codes. The common theme is impersonation of trusted brands to…

July 31, 2026
Fake Downloads and Extensions Steal Sessions Fast

Fake Downloads and Extensions Steal Sessions Fast

The article highlights real, ongoing campaigns where attackers trick people into installing malware via fake software-download websites and a disguised browser extension. These lures are used to steal credentials, browser cookies, and authenticated sessions, letting attackers take over accounts…

September 11, 2026
UNC6671 Calls Staff to Steal SaaS Logins

UNC6671 Calls Staff to Steal SaaS Logins

UNC6671 is running real-world voice phishing (vishing) campaigns where callers impersonate IT help desk staff and create urgency around “mandatory” security changes. Victims are pushed to spoofed login pages that capture passwords and MFA codes, enabling attackers to access and steal data from SaaS…

August 7, 2026
Hotel Wi‑Fi Lures and Entra Vishing Hit Users

Hotel Wi‑Fi Lures and Entra Vishing Hit Users

The article reports real-world social engineering operations, including a hotel Wi‑Fi campaign that pushed fake updates and device-code phishing to steal Microsoft 365 access. It also describes an alleged Microsoft Entra vishing campaign tied to data theft claims at Brinks Home, reinforcing the…

August 7, 2026
Passkey “Update” Prompts Fuel New Microsoft Phish

Passkey “Update” Prompts Fuel New Microsoft Phish

Microsoft says attackers are impersonating IT support and using “passkey/MFA/SSO update” requests to trick employees into authenticating attacker-controlled sessions. The campaigns use attacker-in-the-middle phishing sites or device-code logins to capture valid session tokens, then access Microsoft…

September 19, 2026