Recent Government Cyber Attacks

Page 12 of 13
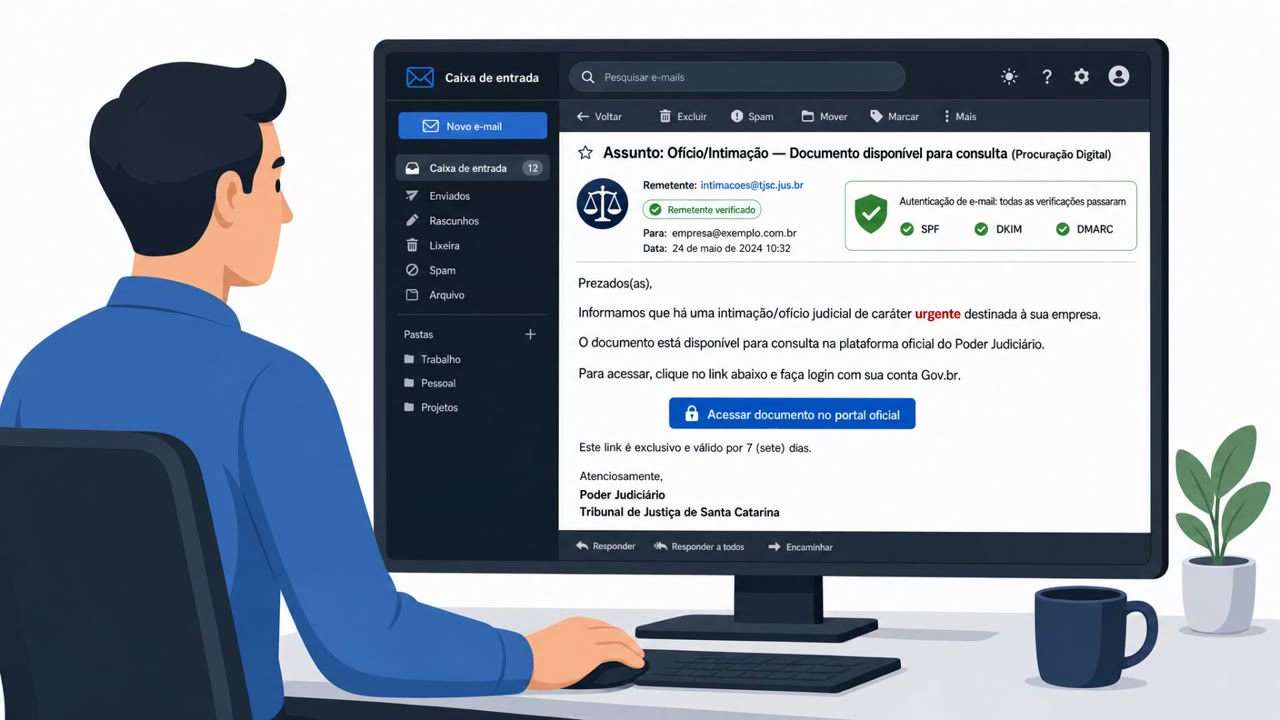
PhantomEnigma Phishes via Hijacked .gov.br Sites

PhantomEnigma Phishes via Hijacked .gov.br Sites

Researchers describe a real phishing-driven malware operation ("PhantomEnigma") that abuses compromised Brazilian government websites and mailboxes to appear trustworthy. Victims are lured with fake law-enforcement style documents (e.g., “Ofício” summons or “Procuração Digital”) and pushed to…

July 28, 2026
QR-PDF Phishing Hits M365, MFA Bypass Surges

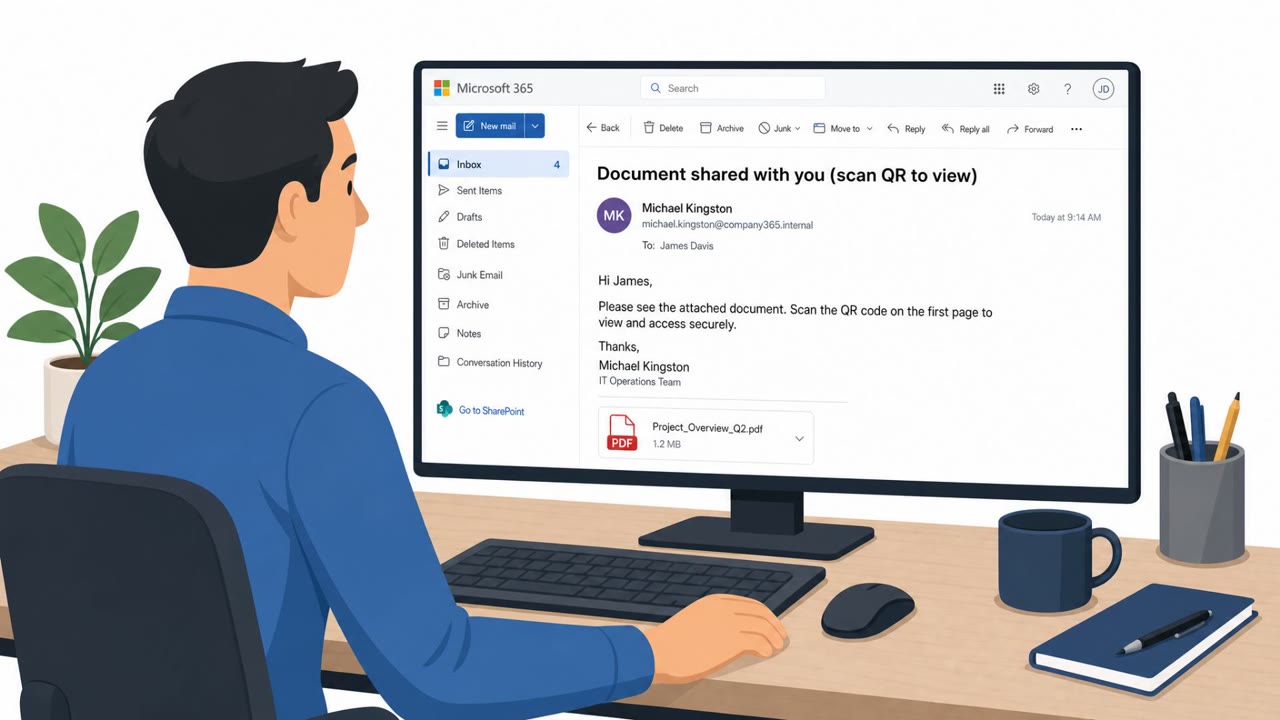
QR-PDF Phishing Hits M365, MFA Bypass Surges

Cisco Talos Incident Response reports that phishing drove initial access in over half of Q2 2026 cases, often using QR codes in PDF attachments and trusted cloud hosting to evade email defenses. Attackers frequently bypassed multi-factor authentication using adversary-in-the-middle proxies,…

July 28, 2026
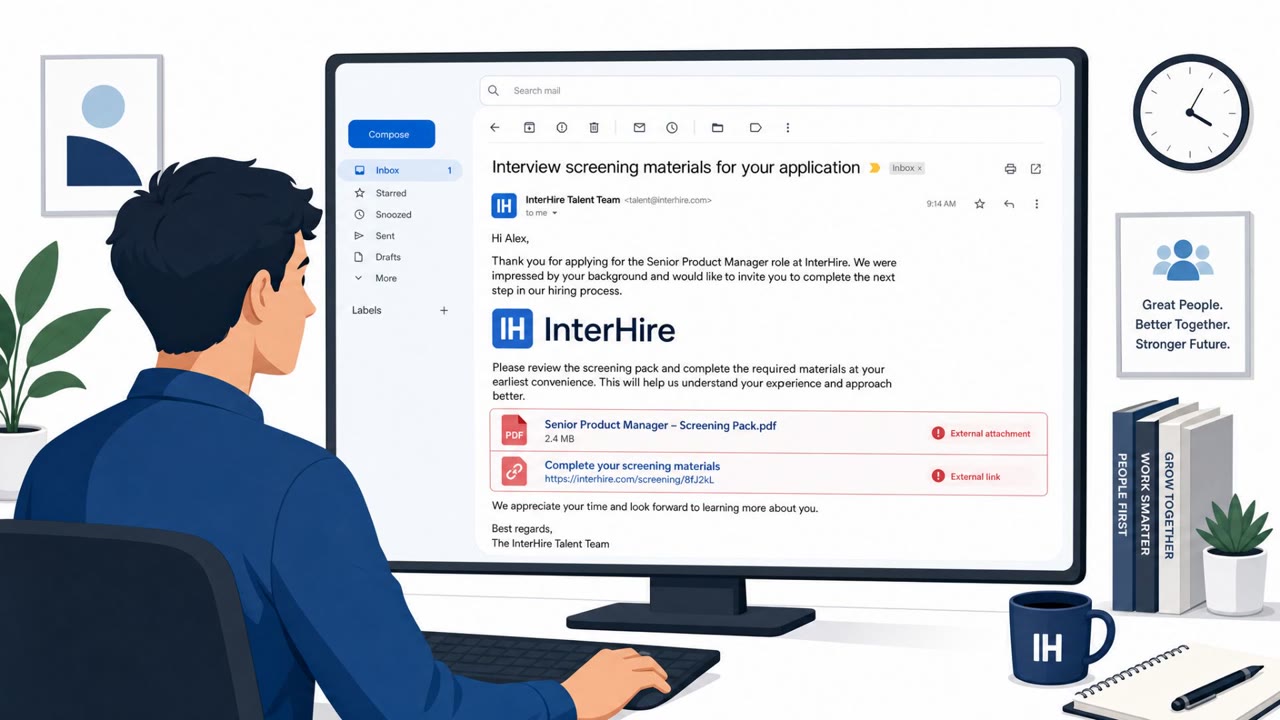
Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Mirage Kitten Uses Fake Hiring Lures to Drop Malware

Researchers report Mirage Kitten (an espionage-focused threat group) targeted organizations in the Middle East and Africa using highly tailored spear‑phishing. The lures included recruitment-themed messages impersonating trusted brands/hiring sites and fake videoconferencing pages that redirected…

July 28, 2026
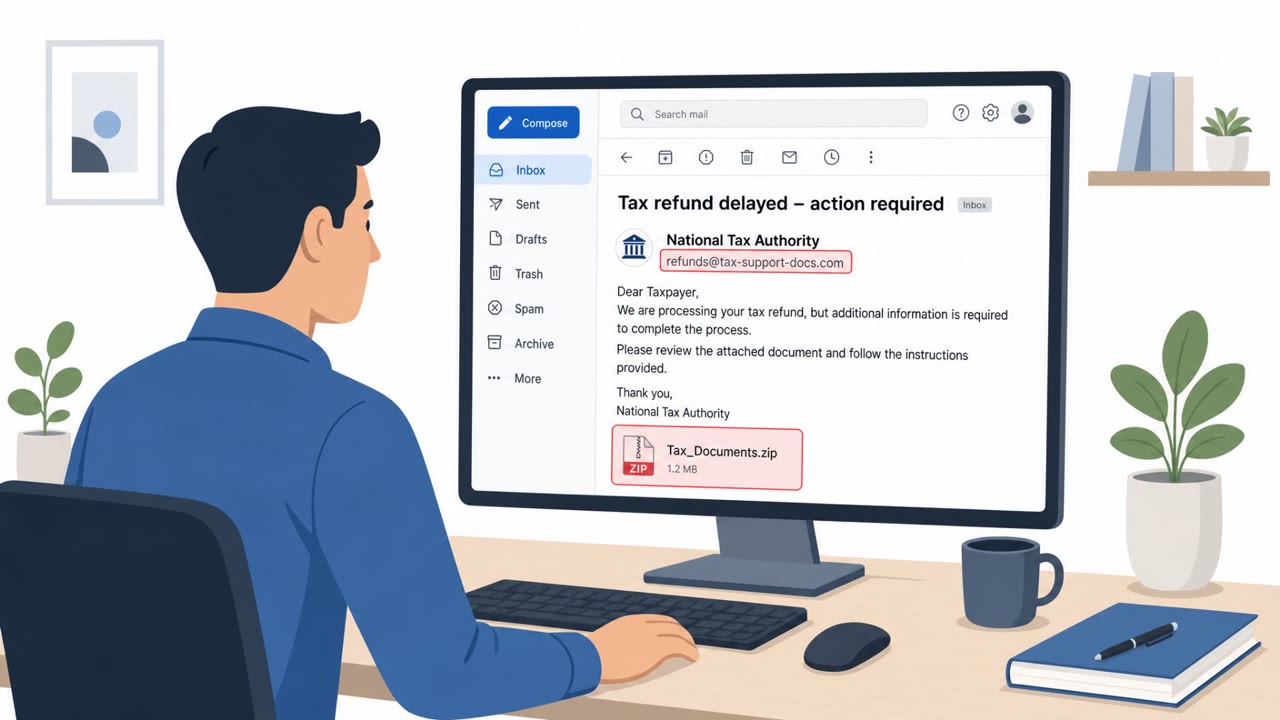
Tax and SSA Phish Push Cruciferra Malware Loader

Tax and SSA Phish Push Cruciferra Malware Loader

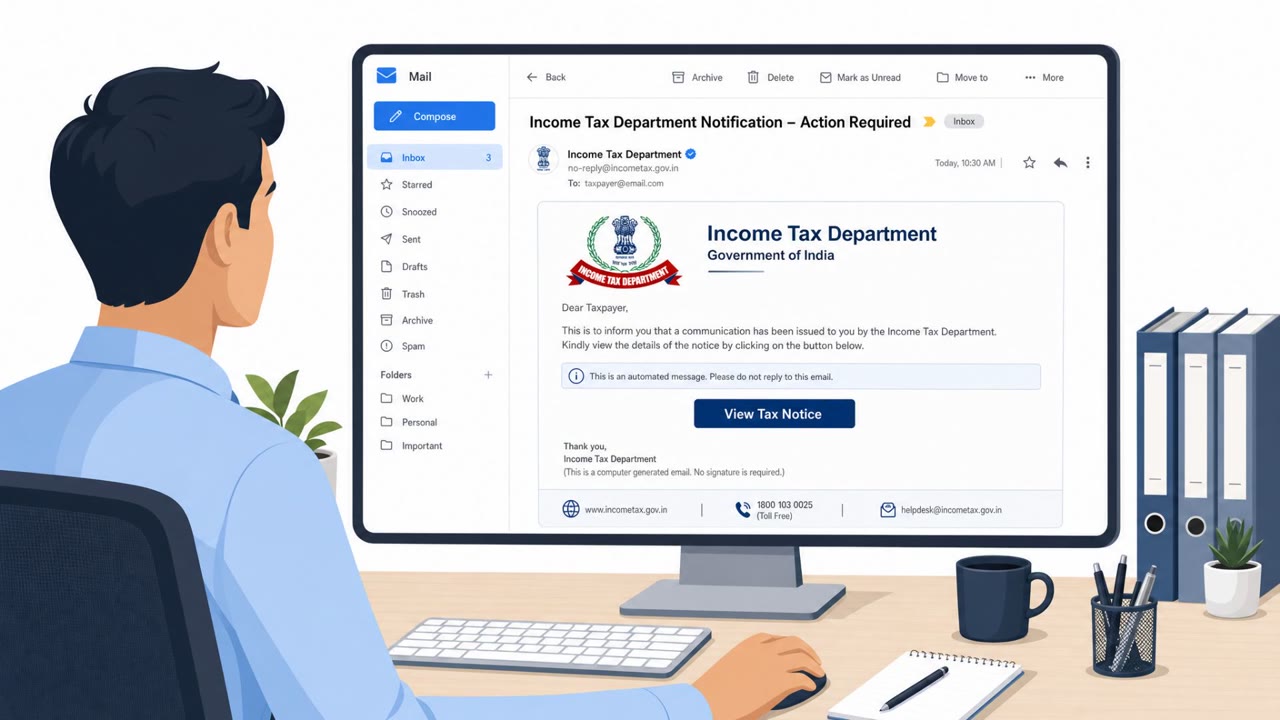
Researchers report multiple real-world email phishing campaigns that used tax and government-benefit themes to trick people into downloading malware. The campaigns used a “crypter” service called Cruciferra to hide malicious files and help malware run while avoiding detection. Targets included…

July 27, 2026
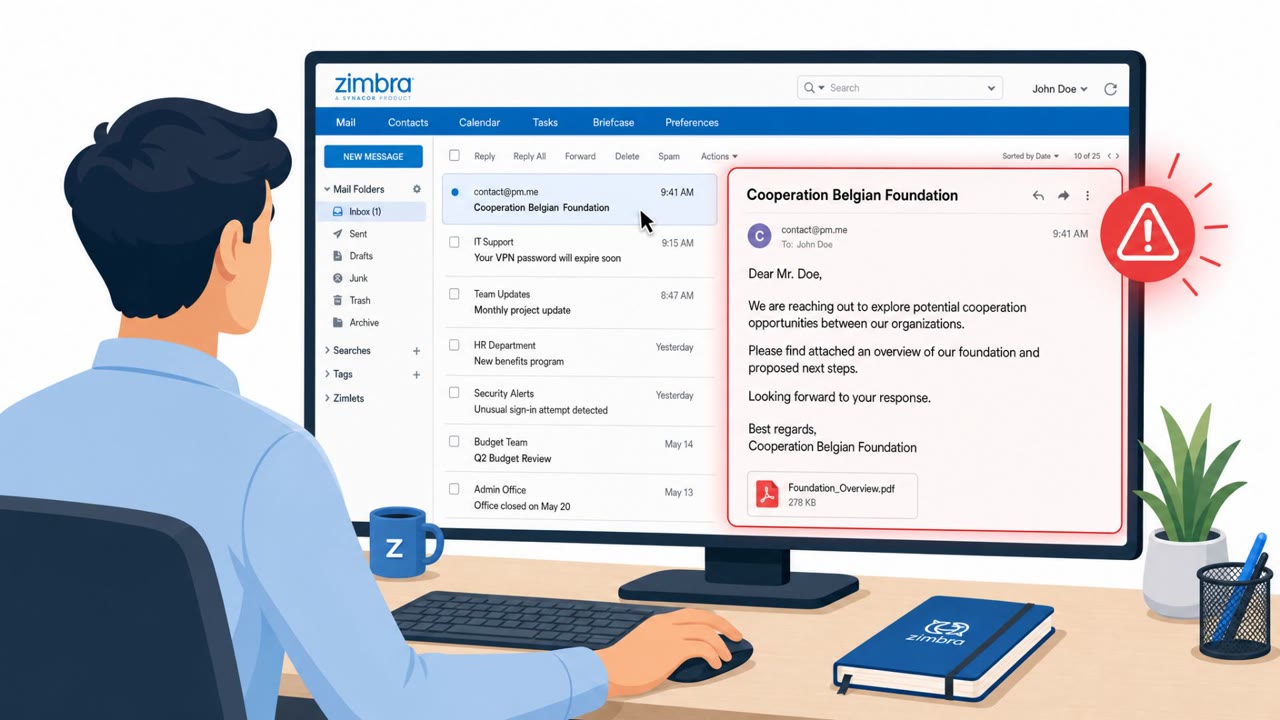
Zimbra Zero-Day Email: Preview Triggers Espionage

Zimbra Zero-Day Email: Preview Triggers Espionage

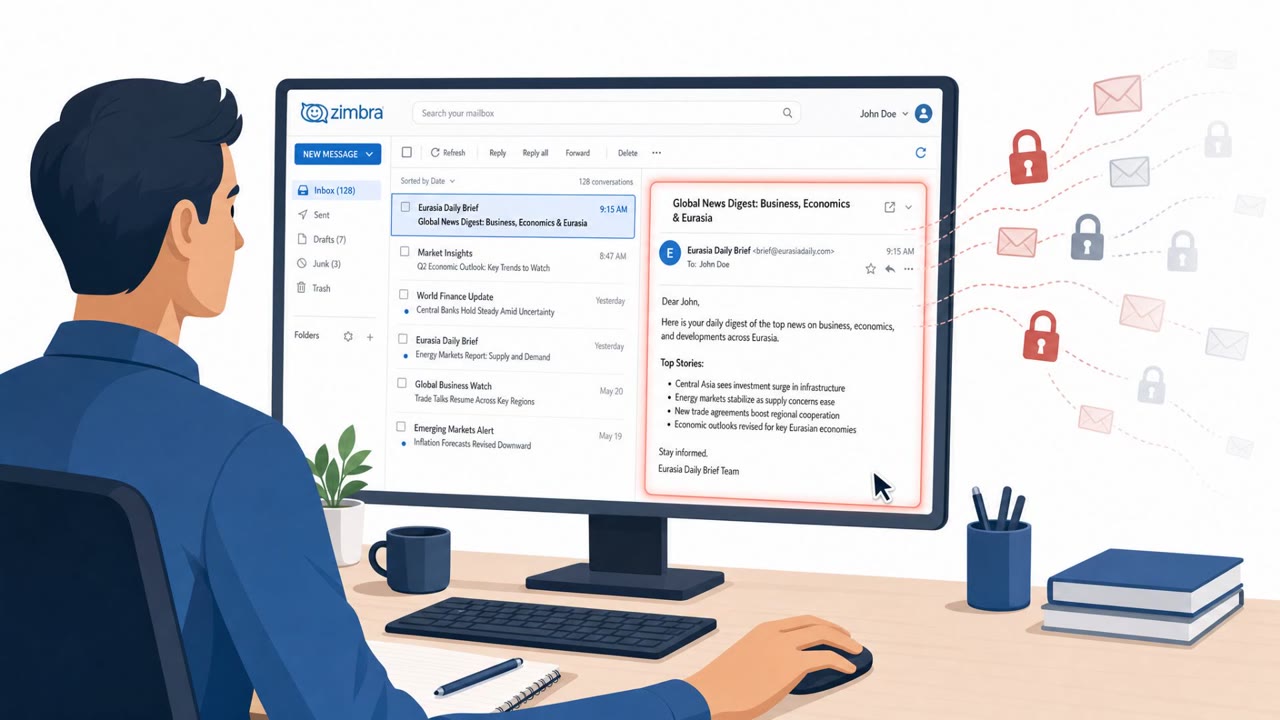
A Russia-aligned espionage group sent specially crafted HTML emails that could compromise vulnerable Zimbra webmail servers just by being opened or previewed, no link clicks or attachments needed. The exploit ran JavaScript inside the email body to steal mailbox data and credentials, then set up…

July 24, 2026
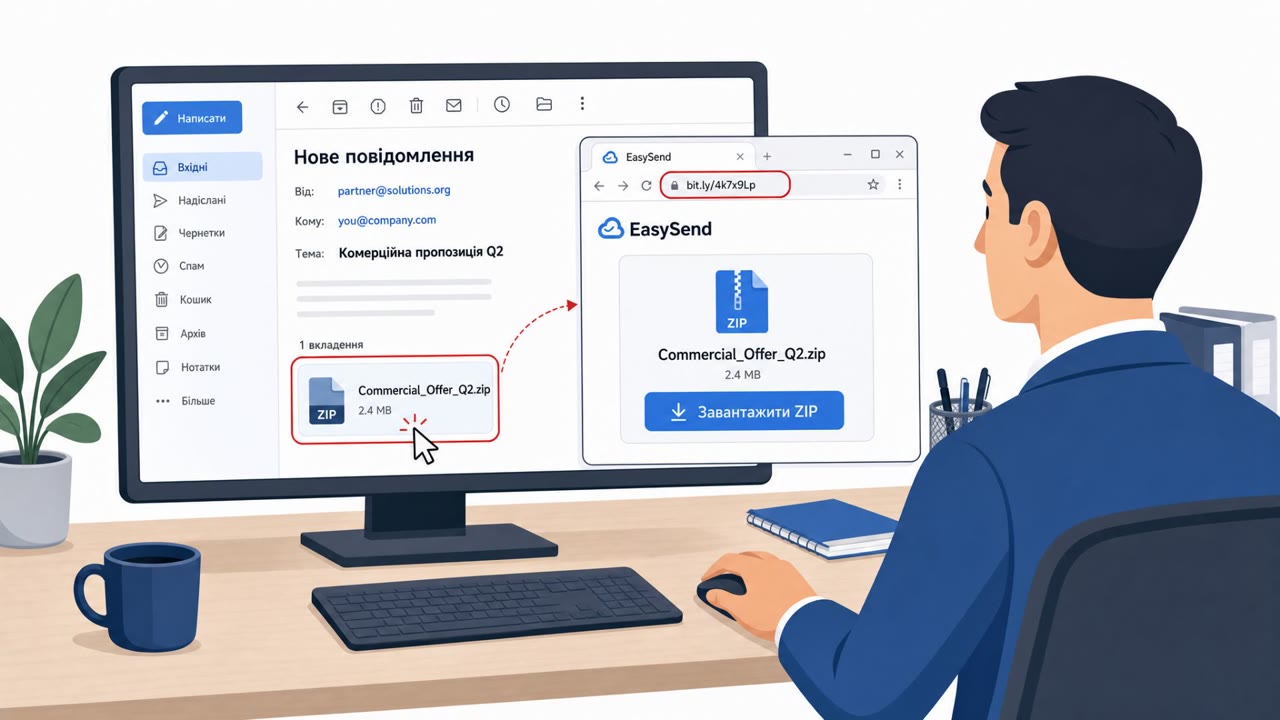
Fake Notepad++ Plugin Used in Ukraine Phish

Fake Notepad++ Plugin Used in Ukraine Phish

CERT-UA reports a real phishing campaign linked to Russia-aligned actor UAC-0099 targeting Ukrainian organizations. Victims receive an email with an image attachment that leads (via a link shortener) to a file-sharing download, where a disguised script installs a trojanized Notepad++ plugin and…

July 24, 2026
Laundry Bear Uses Zero-Click Zimbra Email Trap

Laundry Bear Uses Zero-Click Zimbra Email Trap

A newly identified Russia-linked threat actor (“Laundry Bear”) is targeting Western organisations with a zero-click technique that can compromise Zimbra webmail simply by viewing a malicious email. The campaign has reportedly stolen sensitive data across multiple sectors and may evolve to target…

July 24, 2026
Phishing Email Pushes Fake Notepad++ Plugin

Phishing Email Pushes Fake Notepad++ Plugin

CERT-UA reported a real phishing campaign where victims receive an email with an image attachment that leads (via a shortened link) to a ZIP download. The ZIP contains a script disguised as a PDF, which installs a malicious Notepad++ plugin and sets up an automated task that repeatedly runs malware…

July 24, 2026
TA488 “Half-Click” Emails Hack Zimbra Webmail

TA488 “Half-Click” Emails Hack Zimbra Webmail

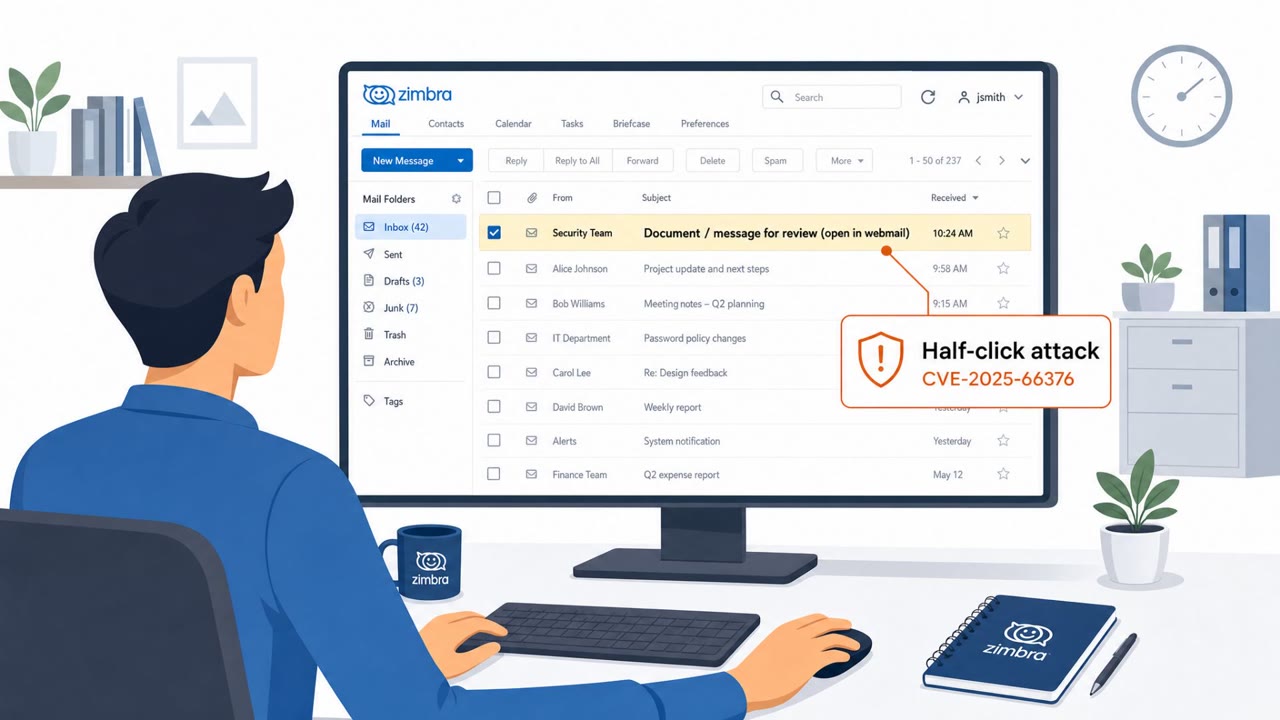
A Russian-aligned group (TA488) used malicious emails to exploit a Zimbra webmail flaw so that simply opening or previewing a message triggered compromise, no link click or attachment required. The attackers then stole email data and set up persistent access to compromised mail servers, including…

July 23, 2026
Zero-Click Emails Hit Zimbra Users in Espionage Push

Zero-Click Emails Hit Zimbra Users in Espionage Push

Government agencies and security firms warn that Russia-aligned hackers are using “zero-click” phishing emails to compromise organizations using Zimbra webmail. The attack hides a malicious JavaScript payload inside an email so it runs when the message is opened, aiming to steal recent email,…

July 23, 2026
Fake Claude App and Alert Apps Drive New Scams

Fake Claude App and Alert Apps Drive New Scams

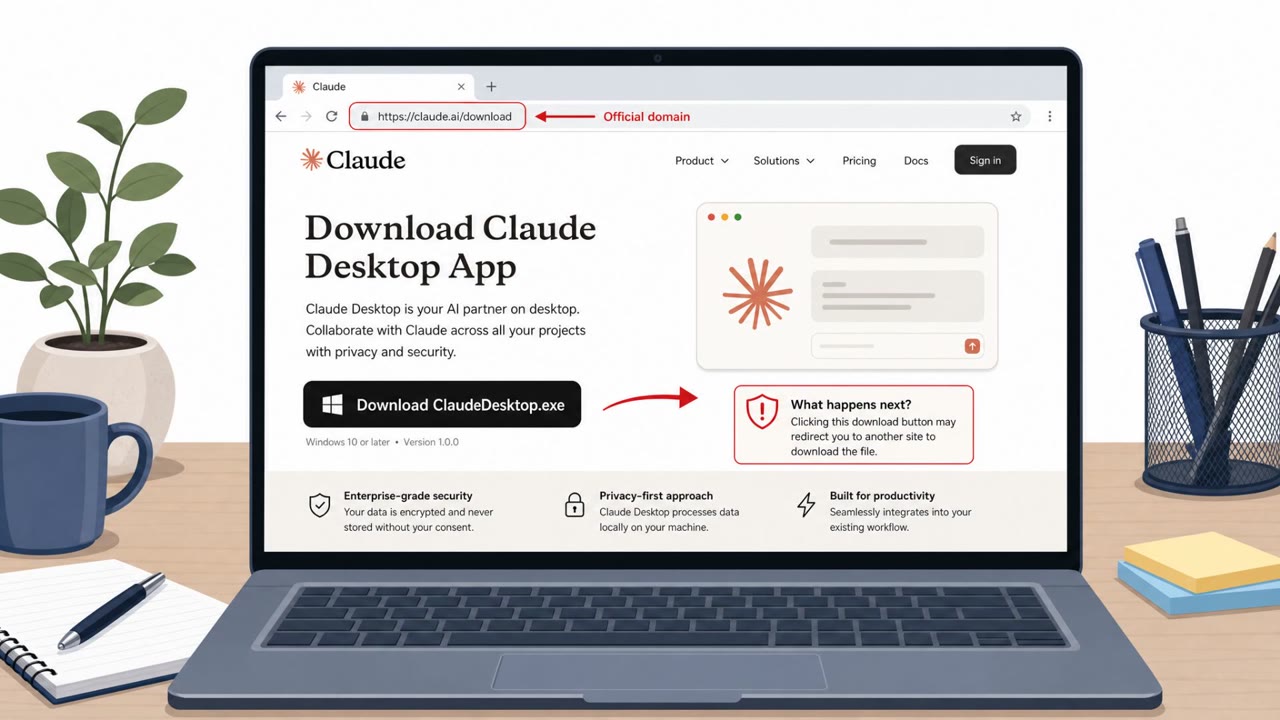
This roundup describes multiple real-world campaigns where attackers trick people into installing malicious software that looks legitimate (a fake Claude desktop app, a fake emergency alert app, and banking-malware phishing). The common pattern is “looks normal, feels urgent,” leading users to…

July 23, 2026
Zimbra Email View Triggers Russian Data Theft

Zimbra Email View Triggers Russian Data Theft

Government agencies say a Russian-linked group sent specially crafted HTML emails that exploit a Zimbra webmail flaw, so simply viewing the message can trigger data theft, no click required. The campaign has targeted multiple Western sectors since July 2025 and focuses on stealing email content and…

July 23, 2026
Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Zero-Click Zimbra Webmail Phish Hits NATO Sectors

Researchers at Unit 42 reported a real espionage campaign targeting organizations using Zimbra webmail, including government, defense, transportation and financial sectors. The attackers sent “zero-click” phishing emails disguised as news headlines, where opening/viewing the message could trigger a…

July 23, 2026
Fake Claude Download Used in JadeProx Attacks

Fake Claude Download Used in JadeProx Attacks

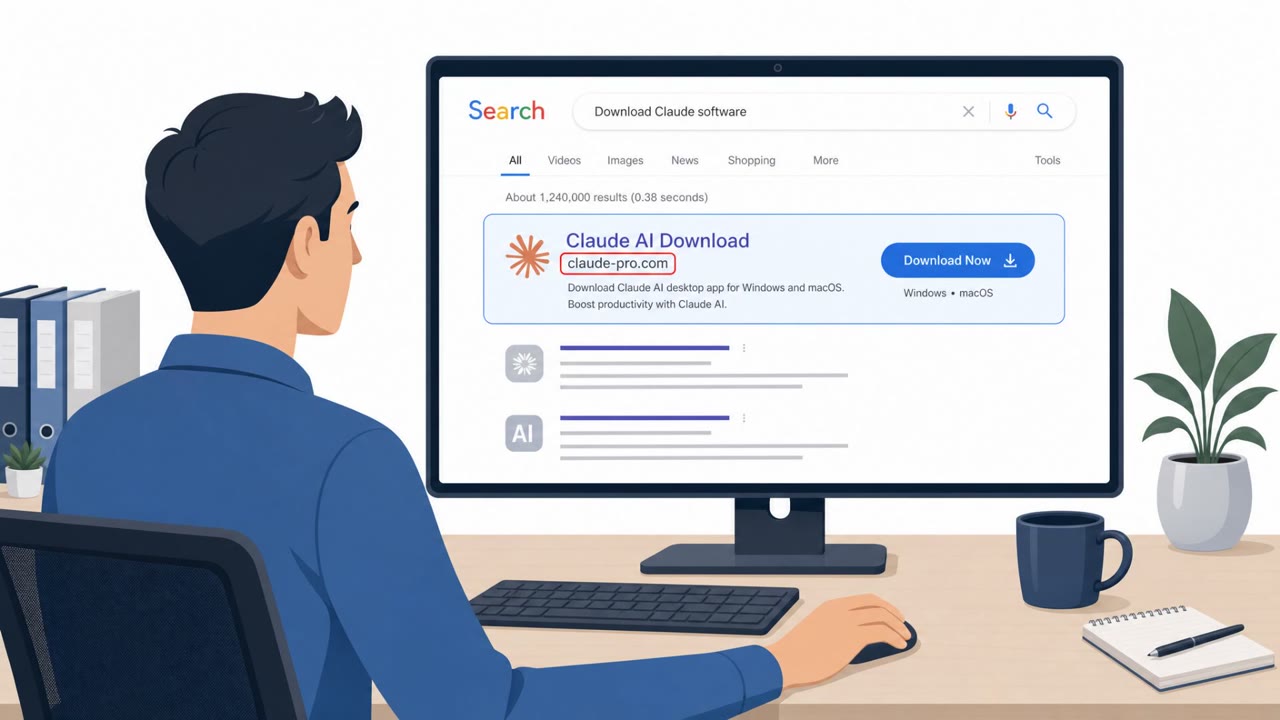
Investigators found evidence of a China-linked operation (tracked as JadeProx) targeting government, healthcare, and education organizations, including spear-phishing and a fake software download site. One campaign impersonated Anthropic’s Claude using a lookalike domain to deliver a malicious…

July 23, 2026
Phishing Link Plants a Rogue ChatGPT “Insider”

Phishing Link Plants a Rogue ChatGPT “Insider”

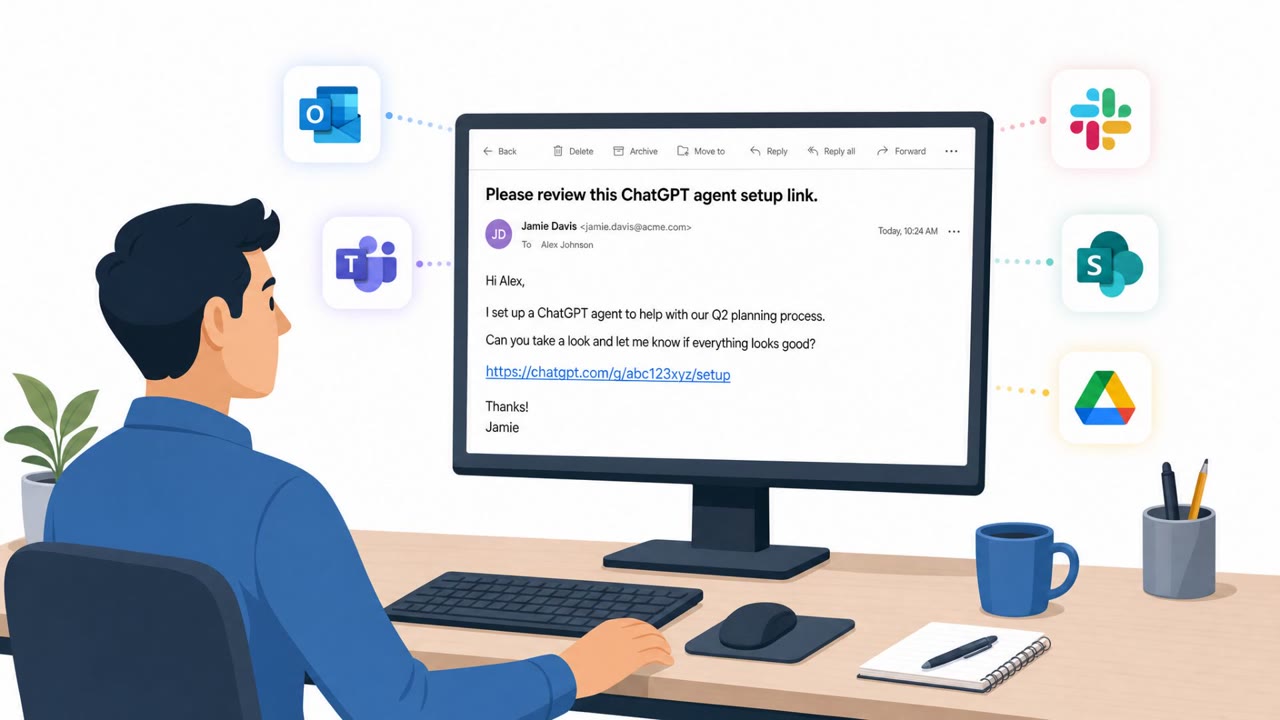
Researchers say a one-click phishing link could trick ChatGPT into creating a malicious AI “agent” inside a company’s ChatGPT workspace. The agent could act using the employee’s existing access (Outlook, Teams, Slack, Google Drive, etc.), run on a schedule, and take instructions from attacker…

July 23, 2026
Kimsuky Poses as Diplomats in LNK Phishing

Kimsuky Poses as Diplomats in LNK Phishing

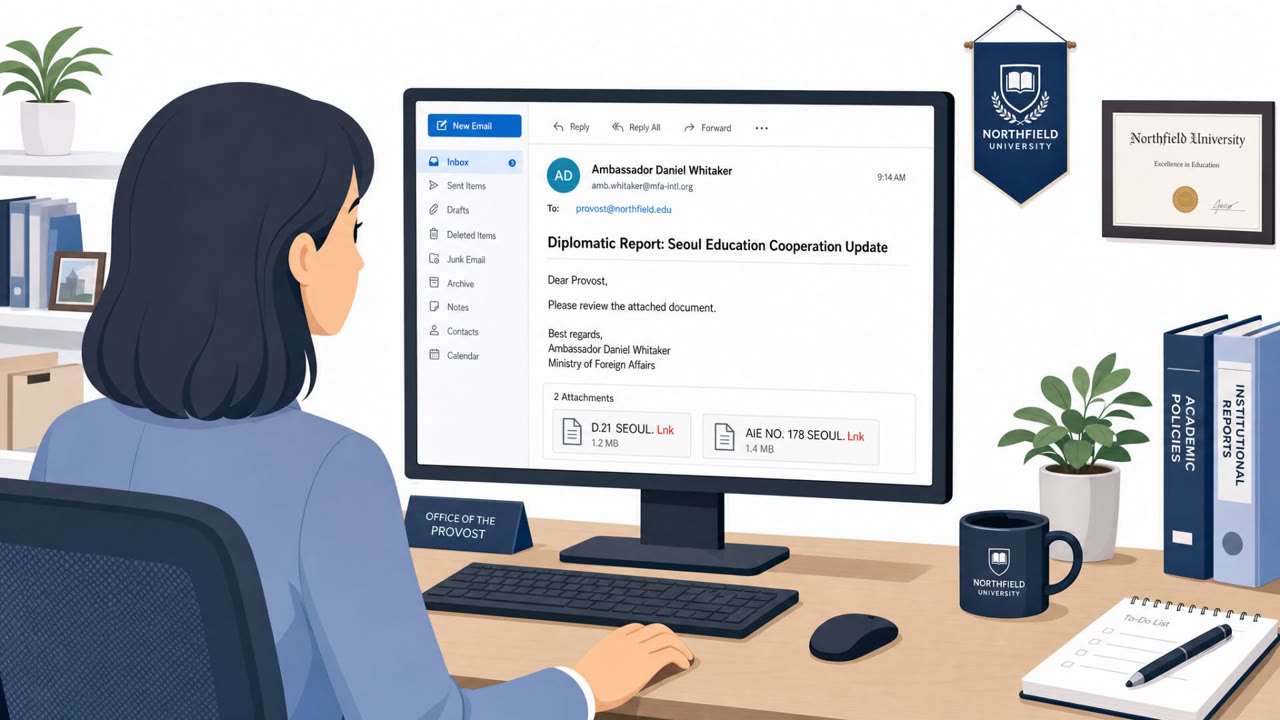
AhnLab reports real-world spear-phishing attacks by the Kimsuky group that impersonate diplomatic personnel and trick targets into opening disguised LNK “document” attachments. Opening the fake document launches scripts that install tools like the PebbleDash backdoor and PrxClient proxy, enabling…

July 23, 2026
Fake Defense Summit Invites Hit Dutch Police

Fake Defense Summit Invites Hit Dutch Police

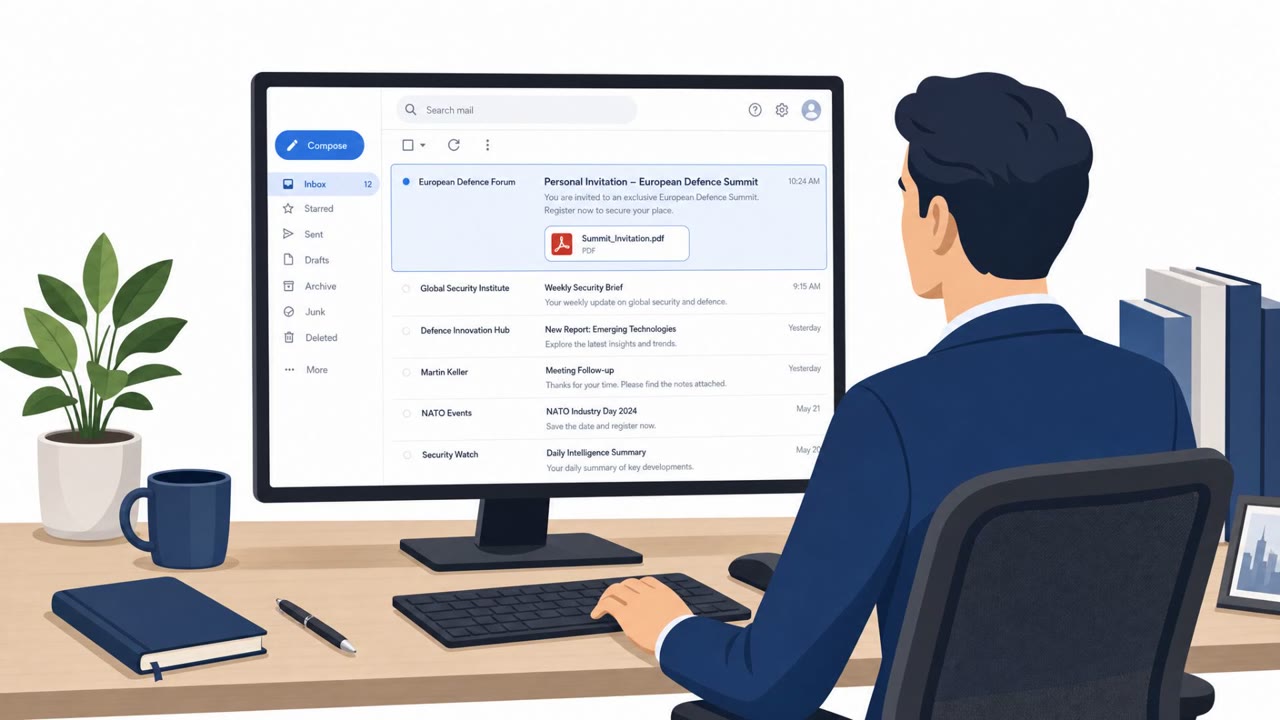
A Russian-linked group allegedly stole sensitive contact data from the Netherlands National Police after getting access to an employee’s email account. The podcast describes a realistic spearphishing lure: an email invitation to a “European Defence Summit” that includes a link or a QR code in a PDF…

July 23, 2026
Govt-Themed Phishing Spreads Cruciferra Malware

Govt-Themed Phishing Spreads Cruciferra Malware

Proofpoint observed real phishing campaigns using government-themed lures to trick people into downloading ZIP files that install malware. The campaigns used a “crypter” service called Cruciferra to help common remote-access and data-stealing malware evade detection. Financial services, healthcare,…

July 21, 2026
Deepfake FBI Videos Push Victims to Fake IC3 Sites

Deepfake FBI Videos Push Victims to Fake IC3 Sites

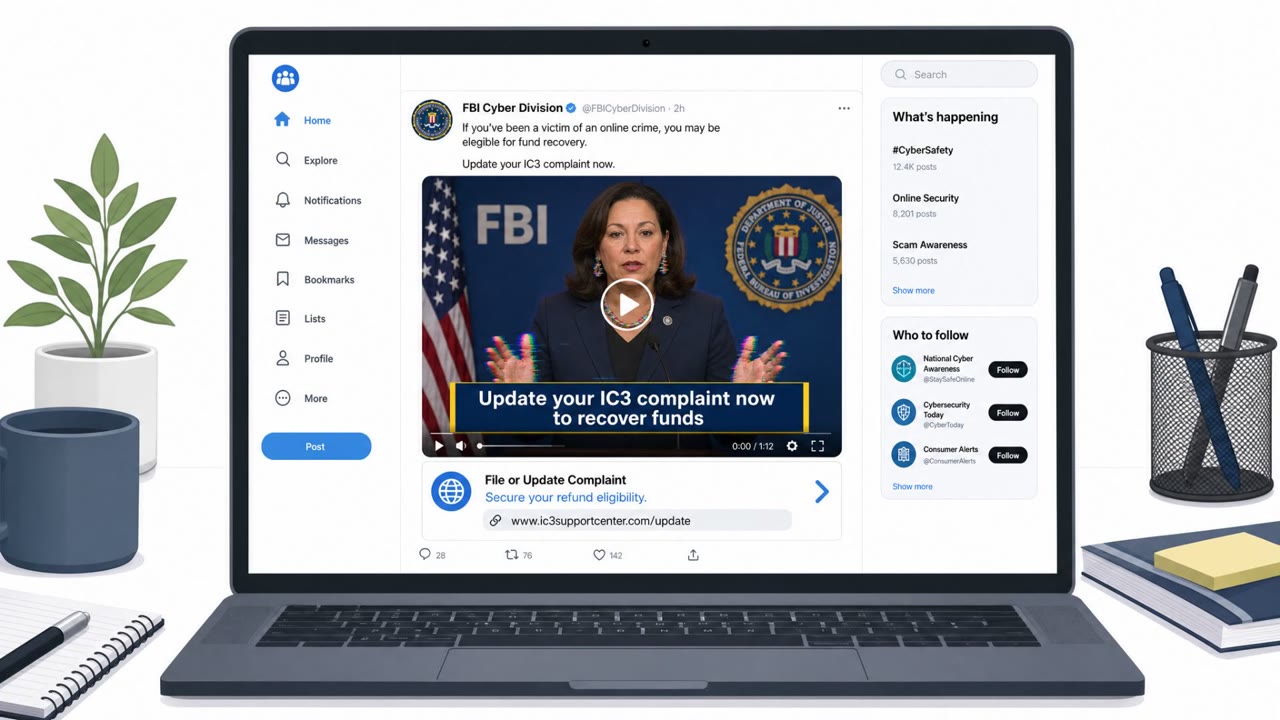
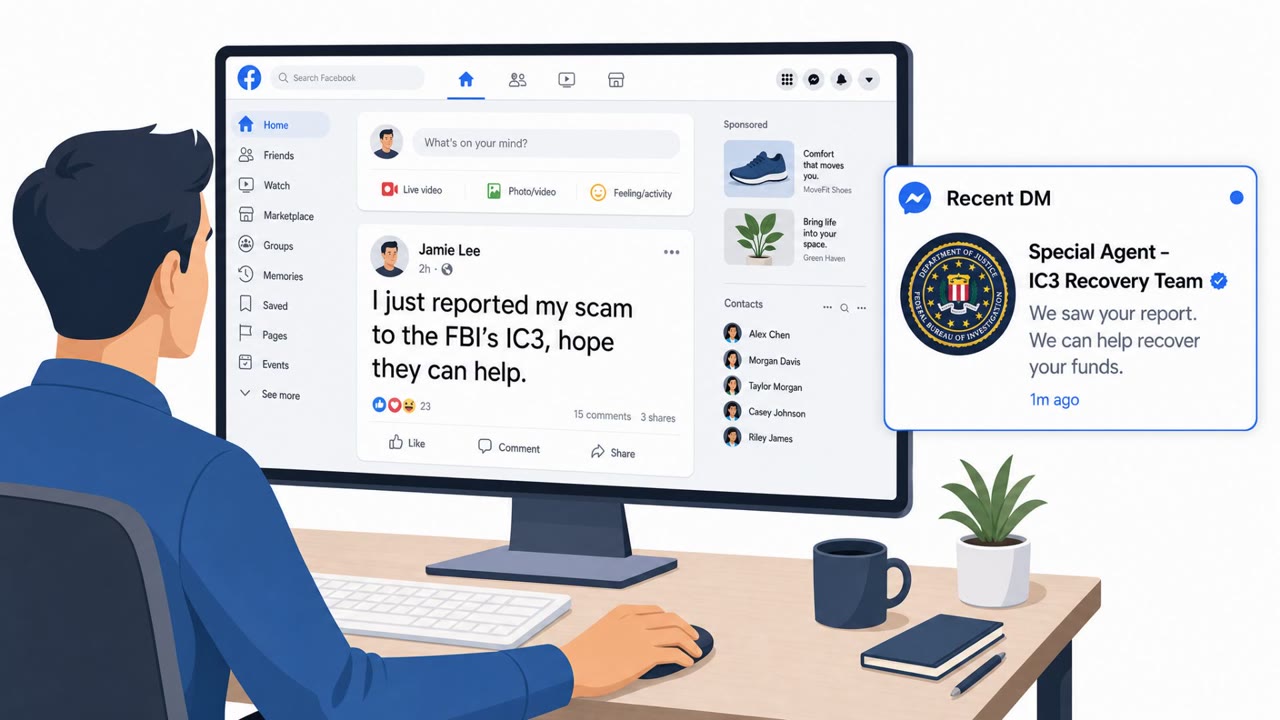
The FBI warned that scammers are impersonating IC3 leadership using AI-generated (deepfake) videos and spoofed IC3 websites to trick prior fraud victims into sharing more personal and financial information. In one example, victims are contacted on Facebook Messenger by someone posing as an FBI…

July 21, 2026
Fake “FBI Agents” Target Scam Victims in DMs

Fake “FBI Agents” Target Scam Victims in DMs

The FBI’s IC3 warns that scammers are impersonating FBI/IC3 staff on social media and messaging apps, especially targeting people who have already been scammed. The criminals use convincing branding (logos, fake reviews) and may even use AI-generated deepfake videos to pressure victims into…

July 21, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo